Gatekeeper puts constraints, mutation, audit and external data into Kubernetes CRDs
🐊 Policy Controller for Kubernetes
At a glance
- What is it?
- Gatekeeper is the Open Policy Agent policy controller for Kubernetes, and what separates it from running OPA with the kube-mgmt sidecar is a set of CRDs: a parameterised policy library, constraints that instantiate it, templates that extend it, mutation, audit and external data. The build is three container images from one Makefile with the whole test toolchain pinned.
- Who is it for?
- Gatekeeper fits a Kubernetes platform team that wants policy expressed as custom resources rather than as a sidecar configuration, with audit and mutation in the same controller, and Kubernetes validating admission policy generated alongside it. It does not fit a cluster with no CRDs to spare or a team that wants the policy logic separated from the cluster entirely.
- Can I use it commercially?
- Yes. Apache-2.0 is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 1 day ago.
- What is it written in?
- Mainly Go, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
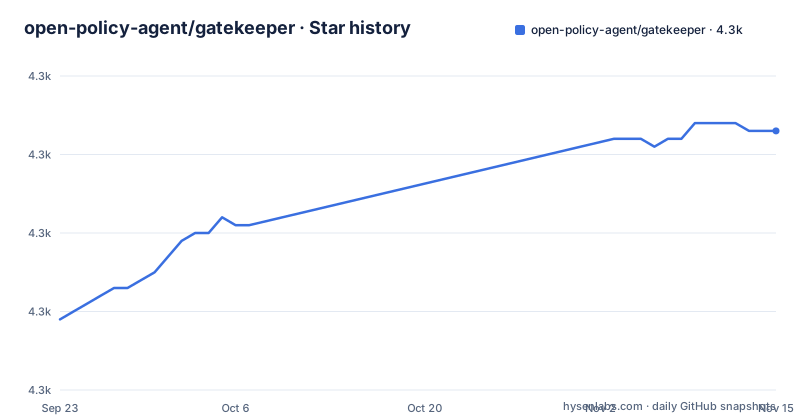
Star history
- open-policy-agent/gatekeeper4,303 ★ · +24
| Repository | 2026-09-23 | 2026-11-15 |
|---|---|---|
| open-policy-agent/gatekeeper | 4.3k | 4.3k |
24 Stars in the last 53 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The whole difference from OPA is six additions
The project states its own delta rather than waiting to be asked. Set against OPA used with its kube-mgmt sidecar, described in the same sentence as Gatekeeper v1.0, the current version adds an extensible and parameterised policy library, native Kubernetes CRDs for instantiating that library, native Kubernetes CRDs for extending it, native Kubernetes CRDs for mutation support, audit functionality, and external data support.
Constraints instantiate the library, templates extend it
Two of the six additions are the halves of the same mechanism and are easier to understand as a pair. A constraint template is the CRD that extends the policy library: it is where new logic enters, and the templates are what the separately published policy library is made of. A constraint is the CRD that instantiates the library, which is where a cluster administrator sets parameters for an existing template. The library page is described as a collection of constraint templates and sample constraints, so the intended reading order is template first, constraint second. A constraint is a resource you can apply, diff and revoke like any other object in the cluster.
The container runs as UID 65532 out of distroless
The image build is a two stage Dockerfile and every input is pinned. The builder stage starts from a golang image referenced by platform and by digest, with build arguments for the target platform, operating system, architecture and variant, and linker flags passed in. Module downloads and the build cache are mounted as cache mounts so a rebuild does not refetch the dependency tree, and the binary is produced with the module mode flag on and cgo disabled, which is what lets one build produce images for several architectures. The runtime stage is a distroless static Debian image pinned by digest, the binary is copied to the root of the filesystem, and the last two instructions in the file are the ones that define the runtime contract:
USER 65532:65532
ENTRYPOINT ["/manager"]
The image runs as an unprivileged numeric user rather than root.
go.mod asks for Go 1.26, the builder image carries 1.27
The two toolchain signals do not match exactly, which is the kind of detail worth knowing before a build fails on a machine with the wrong Go. The module file declares go 1.26.0, while the Dockerfile builder stage uses golang:1.27. The dependency list is wide and tells you what the controller actually does: OPA itself at 1.17.1, the Kubernetes client libraries and apiserver packages all at 0.36.5, cobra for the command line, the Prometheus client, the OpenTelemetry SDK with an OTLP metrics exporter and a Prometheus exporter, resource detectors for AWS EC2 and for Google Cloud, the Dapr SDK, zap for logging and the usual test trio of gomega, go-cmp and testify. The cloud detectors and the Dapr SDK are the two that tell you the project follows the workload rather than sitting beside it.
The Makefile pins the test toolchain and says why
The Makefile is where the development environment is declared, and it carries a comment for the pin that would otherwise look like neglect. KIND_VERSION is 0.33.0 and KUBERNETES_VERSION is 1.33.0, with the note that the Kubernetes version is pinned because KIND image availability lags Kubernetes releases. The rest follows the same pattern: Kustomize at 5.8.1, Bats at 1.14.0 with the test files test/bats/test.bats and test/bats/vap_scope.bats, ORAS at 1.3.4, Helm at 4.2.3, Node at a 24 bullseye slim image and YQ at 4.53.3, with a Helm timeout of five minutes. Three image repositories are declared rather than one, for the manager, the CRDs and gator, each with a GHCR counterpart, and pushing to GHCR is off by default with a development tag that CI replaces with a short Git SHA on a pre-release stage.
The generator flags decide what a build produces
Most of the Makefile is booleans that switch artefacts on, and reading them tells you what the project generates besides the controller itself. GENERATE_VAP and GENERATE_VAPBINDING default to true and SYNC_VAP_ENFORCEMENT_SCOPE defaults to true, so Kubernetes validating admission policy output is part of a default build and its binding is kept in step with the enforcement scope. ENABLE_GENERATOR_EXPANSION, ENABLE_EXPORT and ENABLE_ADMISSION_EXPORT default to false, so the expanded generator and the two export paths are opt in. Two audit annotation flags, EMIT_ADMISSION_AUDIT_ANNOTATIONS and ADMISSION_AUDIT_ANNOTATIONS_INCLUDE_SUCCESS, default to false, which means the audit trail on admitted objects is something you opt into rather than inherit. AUDIT_CONNECTION and AUDIT_CHANNEL both default to audit, the log level defaults to INFO, and the Helm export arguments include a Dapr block that turns on audit pod annotations.
Five demos, a deprecated directory, and a beta ahead of the tags
The repository is large enough that the directory names carry meaning. demos exist for a basic install, an agilebank scenario, mutation, scoped enforcement actions, and Kubernetes validating admission policy, which is the same feature the generator flags produce. There is a deprecated directory kept in the tree rather than deleted, a manifest_staging directory beside deploy, and a library directory that sits inside this repository as well as being published separately. Development scaffolding is equally visible: a Tiltfile, a helm_migrate.sh, a cliff.toml for the changelog, AGENTS.md, a typos configuration, a custom linter configuration, a trivy ignore list and a security audit PDF at the root. Releases run v3.23.0 in July 2026, a v3.24.0 beta in the same month and v3.23.1 in August, while the Makefile still carries the beta version as its build version, and the last push landed on 2026-10-06.
Editorial conclusion
Gatekeeper fits a Kubernetes platform team that wants policy expressed as custom resources rather than as a sidecar configuration, with audit and mutation in the same controller, and Kubernetes validating admission policy generated alongside it. It does not fit a cluster with no CRDs to spare or a team that wants the policy logic separated from the cluster entirely. Before adopting it, read the difference list to see which of the six additions you actually need, check the generator flags your build would set, and confirm the pinned KIND and Kubernetes versions match the cluster you intend to test on.
Frequently asked questions
how to install opa gatekeeper
The getting started section points at the installation instructions on the Gatekeeper website, which cover deploying the Gatekeeper components to your Kubernetes cluster. Separately, the Makefile declares three images: the controller, the CRDs and gator.
How is Gatekeeper different from running OPA directly?
Compared with OPA and its kube-mgmt sidecar, described as Gatekeeper v1.0, the current version adds a parameterised policy library, CRDs for constraints and for constraint templates, CRDs for mutation, audit functionality and external data support.
What is the difference between a constraint and a constraint template?
A constraint template is the CRD that extends the policy library, and it is where new policy logic lives. A constraint is the CRD that instantiates the library, where a cluster administrator sets the parameters for an existing template. The published policy library is a collection of templates and sample constraints.
What is gator in the Gatekeeper repository?
It is a separate binary with its own image, declared in the Makefile as the gator repository with a GHCR counterpart, and it has its own crd.Dockerfile and gator.Dockerfile at the repository root. The Makefile also declares separate images for the controller itself and for the CRDs, so a release pushes three artifacts.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/open-policy-agent-gatekeeper)Star history chart for your README
[](https://hysenlabs.com/projects/open-policy-agent-gatekeeper)Was this useful?