wanderer: a self-hosted trail database that ships its own secrets file
wanderer is a self-hosted trail database. Save your adventures!
At a glance
- What is it?
- A GPS track catalogue in three containers, where the compose file checked into the repository carries a literal master key and a proxy secret that only the documentation expects you to replace.
- Who is it for?
- wanderer fits a person who wants to keep their own recorded tracks and metadata on hardware they control, and does not fit anyone who treats a compose file from a public repository as ready to run unmodified. Before starting, generate fresh secrets, because the file in the repository has a working Meilisearch master key, a fixed PocketBase encryption key, and a proxy secret whose value is the instruction to change it.
- Can I use it commercially?
- Yes, with strict conditions. AGPL-3.0 is a network copyleft licence: if people use a modified version over a network, for example as a hosted service, you must offer them its source code under the same licence.
- Is it still maintained?
- Yes. The repository last received commits 1 day ago.
- What is it written in?
- Mainly Go, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
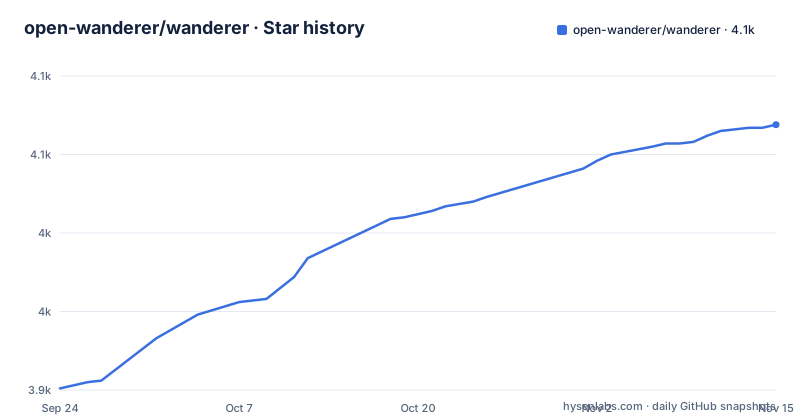
- open-wanderer/wanderer4,069 ★ · +168
| Repository | 2026-09-24 | 2026-11-15 |
|---|---|---|
| open-wanderer/wanderer | 3.9k | 4.1k |
168 Stars in the last 52 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The compose file in the repository contains working credentials
The recommended install path is a setup script that downloads the compose file and fills in fresh secrets, which is the correct way to use it:
# create docker-compose.yml with fresh secrets
/bin/bash -c "$(curl -fsSL https://wanderer.to/setup.sh)"

# launch via docker compose
docker compose up -d
The alternative is to take the docker-compose.yml from the repository, and that file declares a Meilisearch master key as a literal string of 32 characters, a PocketBase encryption key as a 32 character hex string, and a proxy secret whose value is dev-proxy-secret-change-me. The document does warn about this, naming MEILI_MASTER_KEY, POCKETBASE_ENCRYPTION_KEY, and POCKETBASE_PROXY_SECRET as the three values to replace before starting. What the file itself communicates is different: the values are present, well formed, and formatted as if they were meant to work. A reader who skips the note runs a search index and an authentication proxy on the keys published in a public tree. The proxy secret in particular is identical in the db and web services, which means it is a shared secret between two containers rather than a per service one, so anyone who reads it can present themselves to the proxy from anywhere that can reach it.
Two ports are published to the host, not just to the internal network
The compose file puts all three services on a single network called wanderer, which is the right shape for internal traffic. Two of them also publish ports to the host. The search service maps 7700:7700 and the database maps 8090:8090, while the web service has no published port in the visible portion of the file. That means the Meilisearch API and the PocketBase API are both reachable from outside the container network on a default install, each with its own credentials in play: the master key for search, the proxy secret for the database. The internal wiring uses service names rather than hostnames, with MEILI_URL pointing at http://search:7700 and PUBLIC_POCKETBASE_URL at http://db:8090, so nothing inside the compose network depends on the published ports at all. Publishing them is therefore a choice about the host's network rather than a requirement of the application, and the compose file does not say which. Binding those two ports to a loopback address, or dropping the ports block entirely and reaching the services through an explicit tunnel, are both smaller changes than rotating the keys after the fact.
Startup order is enforced by health checks, not by depends_on alone
Both the database and the web service declare depends_on the search service with condition service_healthy, so the ordering here is a gate rather than a start hint. The search container's healthcheck is a single curl against http://localhost:7700/health, retried every 15 seconds, ten times, after a 20 second start period, with a 10 second timeout. The database's check is the same shape in exec form, using CMD with curl against http://localhost:8090/health. The web service waits on both, so a database that cannot answer its health endpoint keeps the frontend down even though its container is running. That is the mechanism behind the stated first startup time of up to 90 seconds: 20 seconds of grace plus retries at 15 second intervals is enough to exceed a minute if the first few probes fail, and the frontend at localhost:3000 is only reached after both gates pass. The search service also sets MEILI_NO_ANALYTICS to true, which is a small privacy decision made at the environment level rather than in application code.
ORIGIN is set to localhost in the file, so any other host breaks CORS
Both the db and web services carry ORIGIN as http://localhost:3000, matching the frontend address the documentation points you at. The note above the install commands says what happens when that value is wrong: if you are not hosting wanderer at http://localhost:3000, change ORIGIN, otherwise you will run into CORS errors. That is the single most likely first failure for anyone deploying this on a real hostname, and it is a mismatch between two variables rather than a bug in either. The database also sets PUBLIC_DISABLE_SIGNUP to the string false, so account creation is open on a fresh install with no flag flipped to close it, and UPLOAD_USER and UPLOAD_PASSWORD are present as keys with no values after them. An empty credential pair is easy to read as intentional and easy to miss, so whether the install leaves file uploads open depends on values that are not filled in here.
Two volume paths assume a data directory the compose file never creates
Persistence is declared through bind mounts rather than named volumes. The search service mounts ./data/data.ms to /meili_data/data.ms and the database mounts ./data/pb_data to /pb_data along with ./data/plugins to /data/plugins. All three are relative host paths under a single data directory, and nothing in the compose file creates it, so Docker creates the intermediate directories on first run, owned by root, which is the usual reason a self hosted instance ends up with permission problems on the data directory afterwards. The plugins mount is the interesting one, because it lines up with the build side: the Makefile's local install target creates data/plugins, clears out the hammerhead, komoot, and strava plugin directories, and copies the built binaries into them. The tree contains a plugins/ directory with an sdk alongside those three, so the mount point is where compiled plugin binaries are expected to appear, and a fresh clone that skips the build step gives you an empty plugin directory with no error.
Plugins are separate Go binaries built with TinyGo, not part of the container images
The plugin set is visible in the build file rather than in the documentation. The test target walks four directories in order: plugins/sdk, plugins/hammerhead, plugins/komoot, and plugins/strava, each running go test. The build target skips the sdk and builds the other three with make, passing a cache location through XDG_CACHE_HOME that defaults to /tmp/wanderer-tinygo-cache, which is what identifies the toolchain. Packaging then tars each plugin's dist directory into plugin_dist under names like wanderer-plugin-hammerhead.tar.gz, meaning the three plugins ship as three separate archives rather than one bundle. Note that plugins-test and plugins-build disagree on scope: sdk is tested but not built, since it is a library. The db and web images are built separately as flomp/wanderer-db:latest and flomp/wanderer-web:latest, and the compose file pins neither to a version, so a local rebuild silently replaces what a running deployment uses.
Two release trains run on the same repository
The release history shows two naming schemes in the same window. v0.21.0 and v0.20.0 carry plain semantic versions with a v prefix, while app-v0.1.0-beta.16 is named for a separate app train and is still at beta 16. Both of the September entries land on the same day, v0.21.0 at 12:12 and the app beta at 10:18, which suggests a coordinated release rather than an accident of ordering. The default branch is dev rather than main, so the branch you see on the repository is not the branch releases are cut from by name. The last commit is dated 2026-10-04, and the repository is not archived, so the project is being worked on as of that date. For anyone pinning a deployment, the practical question is which of the two trains a given install actually needs, since the compose file references images by name without a tag and the two version lines do not describe the same artifact.
Editorial conclusion
wanderer fits a person who wants to keep their own recorded tracks and metadata on hardware they control, and does not fit anyone who treats a compose file from a public repository as ready to run unmodified. Before starting, generate fresh secrets, because the file in the repository has a working Meilisearch master key, a fixed PocketBase encryption key, and a proxy secret whose value is the instruction to change it. Set ORIGIN to wherever you actually host the frontend or you will meet CORS errors, and expect the first boot to take up to 90 seconds while the search and database containers pass their health checks.
Frequently asked questions
How do I install wanderer?
The documented path runs the setup script that downloads the docker-compose.yml and fills in freshly generated secrets, then launches the stack with docker compose up -d. The first startup can take up to 90 seconds before the frontend is reachable at localhost:3000, and a bare metal route is documented separately at wanderer.to.
Why does wanderer give me CORS errors after installing?
Both the db and web services set ORIGIN to http://localhost:3000, which only matches a frontend hosted at that address. If you host wanderer anywhere else, change ORIGIN, since the mismatch between the declared origin and the one you are browsing is what produces the CORS failure.
What secrets do I have to change before starting wanderer?
Three values are named for replacement if you download the docker-compose.yml yourself: MEILI_MASTER_KEY, POCKETBASE_ENCRYPTION_KEY, and POCKETBASE_PROXY_SECRET. In the repository's own file the master key and encryption key are literal values, and the proxy secret reads dev-proxy-secret-change-me in both the db and web services.
Which plugins does wanderer ship and how are they built?
The build file covers plugins/sdk, plugins/hammerhead, plugins/komoot, and plugins/strava, testing all four and building the last three with make using a cache under /tmp/wanderer-tinygo-cache. Each is packaged as its own tar.gz under plugin_dist, and the local install target copies the built binaries into data/plugins, which is the directory the database container mounts at /data/plugins.
What license is wanderer released under?
AGPLv3. The README states the project is licensed under the AGPLv3 License and points at the LICENSE file in the repository root for the full text. The repository also carries SECURITY.md, CONTRIBUTING.md, CHANGELOG.md, and crowdin.yml for translations.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/open-wanderer-wanderer)Star history chart for your README
[](https://hysenlabs.com/projects/open-wanderer-wanderer)Was this useful?