OpenCTI ships a platform and a worker, and the two editions share one license path
Open Cyber Threat Intelligence Platform
At a glance
- What is it?
- OpenCTI is a threat intelligence platform that structures reports, observables, and attribution on a STIX2 schema behind a GraphQL API. What this page actually documents is thin: four installation routes that all resolve to the documentation site, a rolling package built from master, a settings toggle for the Enterprise edition, and anonymous usage telemetry described in a separate document.
- Who is it for?
- OpenCTI fits an organization that already collects reports and observables and wants them on a STIX2 schema with a GraphQL API, a relational model built around confidence and first and last seen dates, and connectors to MISP, TheHive, and MITRE ATT&CK.
- Can I use it commercially?
- Check first. The repository uses a licence we do not classify automatically, so read its LICENSE file before any commercial use.
- Is it still maintained?
- Yes. The repository last received commits 2 days ago.
- What is it written in?
- Mainly TypeScript, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 19, 2026, and from our analysis. They are not legal advice.
Star history
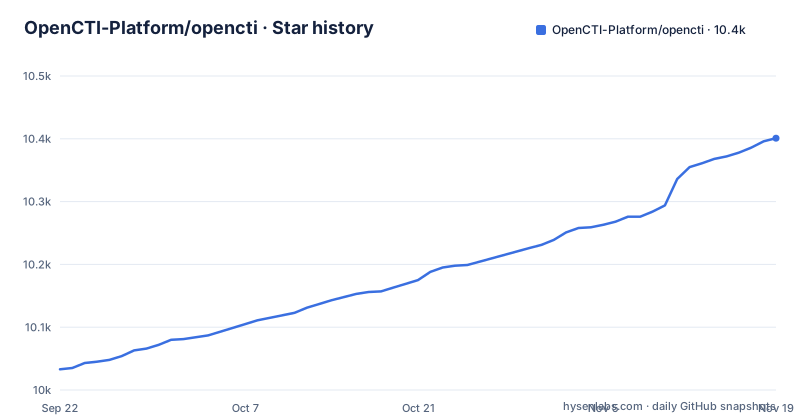
- OpenCTI-Platform/opencti10,401 ★ · +368
| Repository | 2026-09-22 | 2026-11-19 |
|---|---|---|
| OpenCTI-Platform/opencti | 10k | 10.4k |
368 Stars in the last 58 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Four install routes, none of them a command you can paste
The installation section is a list of four links and no commands. You can use Docker, install manually, or use the community Terraform or the community Helm charts, and every one of those entries points into the documentation site rather than into a file in this repository. There is no compose file, no Dockerfile, and no chart at the top level of the tree, which holds `opencti-platform/`, `opencti-worker/`, `client-python/`, `docs/`, `scripts/`, and `nx.json` alongside the usual community files.
Getting the software is a separate matter from building it, and there are two channels. Releases sit on the GitHub releases page, and there is also a rolling release package generated from the master branch, which the default branch is. Recent tags show how fast that channel moves: 7.261030.1 on 2026-10-30, 7.261030.0 on 2026-10-30, and 7.261026.0 on 2026-10-26, against a last push of 2026-11-02. The consequence for an operator is that the rolling package gives you master rather than a version you tested, so pin a tag if your process depends on reproducing last week's behavior.
Both editions point at the same LICENSE path from the same README
OpenCTI has two editions and the difference is stated in terms of investment rather than features. The Community Edition is licensed under the Apache 2, Version 2.0 license, the Enterprise Edition is licensed under the Enterprise Edition license, and both bullets in that list link to the same file named LICENSE at the root of the repository. The Enterprise Edition is described as providing additional features that require specific investments in research and development, and the detail page lives on the vendor's own offering site rather than in this repository. The repository metadata, meanwhile, records the license as NOASSERTION rather than resolving the question.
What this does not give you is a way to audit the boundary from the README. What it does give you is a shortcut worth knowing: the Enterprise Edition can be enabled directly in the settings of the platform, which the README presents as a way to try that edition. For a reader in a procurement conversation, the consequence is that feature availability and license entitlement are the same toggle in the interface, so the answer to whether you may use a capability has to come from the LICENSE file and your agreement, not from the settings screen.
The runtime is a platform and a worker, driven by Nx fan-out targets
The root manifest shows what working on this looks like. It is a private, ES module package that pins yarn as its package manager, requires Node 22.18.0 or newer, keeps Nx at 24.0.0 as its only dev dependency, and pins axios to 1.21.0 through resolutions. Most scripts are an Nx fan-out across the workspace rather than a single build, and a second family of scripts wraps the same commands in a Python virtual environment:
  "engines": {
    "node": ">= 22.18.0"
  },
  "scripts": {
    "deps": "nx run-many --tuiAutoExit --target install",
    "dev": "nx run-many --target dev",
    "dev:watch": "nx run-many --target dev:watch",
    "dev:watch-with-graphql": "nx run-many --tuiAutoExit --target dev:watch-with-graphql",
    "build": "nx run-many --tuiAutoExit --target build",
    "test": "nx run-many --tuiAutoExit --target test,e2e",
    "lint": "nx run-many --tuiAutoExit --target lint",
    "graphql": "nx run-many --tuiAutoExit --target graphql",
    "with-python-venv": "node scripts/with_python_virtual_env.mjs",
    "deps:venv": "yarn with-python-venv yarn deps",
    "build:venv": "yarn with-python-venv yarn build",
    "dev:venv": "yarn with-python-venv yarn dev",
    "dev:watch:venv": "yarn with-python-venv yarn dev:watch",
    "dev:watch-with-graphql:venv": "yarn with-python-venv yarn dev:watch-with-graphql",
    "test:venv": "yarn with-python-venv yarn test",
    "build:ubi9": "nx run-many --tuiAutoExit --target build-ubi9",
    "push:ubi9": "nx run-many --tuiAutoExit --target push-ubi9",
    "renovate:dry-run": "LOG_LEVEL=debug yarn dlx renovate --dry-run --platform=local"
Note that `test` runs two targets at once, `test` and `e2e`, and that a separate ubi9 build and push pair exists. Nothing in this manifest documents how the platform and the worker are wired to each other at runtime; the README points to a dedicated development environment page instead.
Confidence, dates, and a primary source link are what the data model adds
The stated objective is to capitalize both technical material such as TTPs and observables and non-technical material such as suggested attribution and victimology, while linking every piece of information to its primary source, which it names as a report or a MISP event. The named features around that idea are the links between pieces of information, first and last seen dates, and levels of confidence. MITRE ATT&CK is used through a dedicated connector in a separate connectors repository, and the alternative is stated too: a user can implement their own datasets rather than adopting the ATT&CK framework.
There is a demonstration instance at demo.opencti.io that is open to everyone, and what it does not give you is durability. It is reset every night and it runs on reference data maintained by the developers, so anything you model there is a scratch pad. The consequence is a two-speed evaluation: use it to click through the data model, but treat it as incapable of holding a single real report you care about keeping, and do not point an integration at it.
Inferred relations sit on top of the relations you imported
Once analysts have capitalized and processed data, the platform infers new relations from the existing ones so the knowledge can be understood and represented better. Imports and exports are supported under different formats, with CSV and STIX2 bundles named, and connectors are developed to accelerate interactions between the tool and other platforms.
Because relations can be inferred, a reader whose work depends on provenance should check in the documentation how derived links are distinguished from ones an analyst asserted or an imported bundle supplied.
Anonymous usage telemetry is collected and the opt-out is not described here
Under the data collection heading the platform states that, to improve its features and its performances, it collects anonymous statistical data related to its usage and health. The details of what is collected and how it is used are said to be in the usage telemetry documentation, and the project is designed and developed by a named vendor company rather than by an informal group.
The README points to the usage telemetry documentation for the details, so check there whether collection can be disabled. This matters more for OpenCTI than it would for a small tool, because what sits in this platform is incident material and attribution judgements about real actors. The consequence for a reader with a data handling policy is that the answer must be fetched from that documentation page and written into your own runbook, instead of being assumed from the fact that the collection is described as anonymous.
CircleCI configuration in the tree, a Drone badge above it
The build and dependency machinery is visible if you look at the root. Continuous integration is configured through a `.circleci/` directory and coverage through `.codecov.yml`, dependency updates are managed by `renovate.json5`, and formatting hooks live in `.pre-commit-config.yaml`. The README header, by contrast, carries a badge pointing at a Drone project on the vendor's own domain, next to badges for the documentation, the Slack community, Codecov, Renovate, DeepScan, and Docker Hub pulls. So the public readme advertises one CI system while the repository carries configuration for another.
Releases use date-stamped versions such as 7.261030.1, 7.261030.0 and 7.261026.0. The project describes itself as under heavy development, and with a last push on 2026-11-02 that is consistent with the cadence rather than a gap, so the practical move is to choose a channel deliberately and read the release notes you depend on.
Editorial conclusion
OpenCTI fits an organization that already collects reports and observables and wants them on a STIX2 schema with a GraphQL API, a relational model built around confidence and first and last seen dates, and connectors to MISP, TheHive, and MITRE ATT&CK. It is the wrong tool if you need a deployment you can assemble from a single page, if you want the Enterprise feature set on a license you have already settled, or if a usage telemetry clause is not something you can accept in writing. Before you commit, read the installation page for the route you intend, decide whether the date-stamped tags or the rolling package from master match how you release, confirm which edition you are entitled to run by reading the LICENSE file rather than the badge, and read the usage telemetry documentation before an auditor asks you about it.
Frequently asked questions
What does OpenCTI do?
It lets an organization manage cyber threat intelligence knowledge and observables, structuring, storing, organizing, and visualizing technical and non-technical information about cyber threats. The data is structured on a STIX2 knowledge schema and exposed through a GraphQL API with a UX oriented frontend.
Is OpenCTI free to use?
The Community Edition is licensed under the Apache 2, Version 2.0 license. A separate Enterprise Edition exists under the Enterprise Edition license with additional features, and the README says you can enable that edition directly in the settings of the platform to try it.
What are the key differences between OpenCTI and MISP?
The README does not set out a comparison. It names MISP as something OpenCTI integrates with, alongside TheHive and MITRE ATT&CK, and describes linking each piece of information to its primary source such as a report or a MISP event.
how to install opencti
The README lists four routes, all documented on the official documentation site: use Docker, install manually, use Terraform in the community edition, or use Helm charts in the community edition. Built releases are on the GitHub releases page, and a rolling package generated from the master branch is published separately.
what is opencti used for
For capitalizing technical information such as TTPs and observables and non-technical information such as suggested attribution and victimology, with links between each piece of information, first and last seen dates, and levels of confidence. It also imports and exports data in formats such as CSV and STIX2 bundles, and infers new relations from existing ones.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/opencti-platform-opencti)Star history chart for your README
[](https://hysenlabs.com/projects/opencti-platform-opencti)Was this useful?