openfga: what the example compose file gives away
A high performance and flexible authorization/permission engine built for developers and inspired by Google Zanzibar
At a glance
- What is it?
- A Go authorization engine inspired by Google Zanzibar, whose shipped example configuration publishes a Postgres port, authenticates with the password `password` and disables TLS, while the documentation tells you to fetch that file from a website rather than from the repository that contains it.
- Who is it for?
- OpenFGA suits teams that want fine-grained authorization modelled as data rather than as code in an application, and it is a poor fit for anyone who needs the playground or the example configuration to be safe as shipped. Before deploying, read the production guide the quickstart points at, because the in-memory engine is ephemeral and the example Postgres credentials are placeholders.
- Can I use it commercially?
- Yes. Apache-2.0 is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 2 days ago.
- What is it written in?
- Mainly Go, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
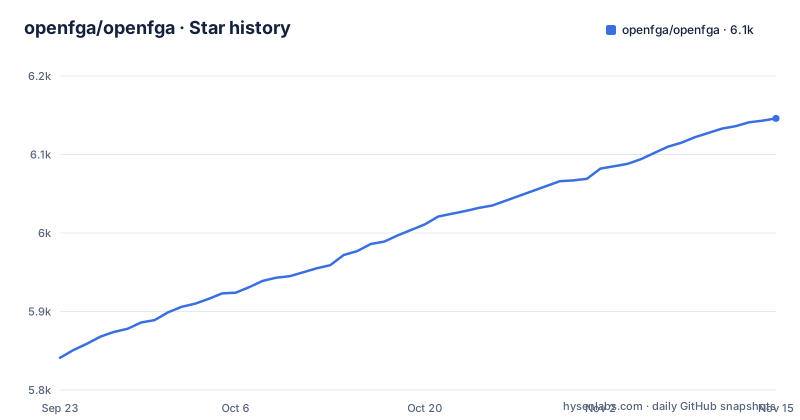
- openfga/openfga6,146 ★ · +305
| Repository | 2026-09-23 | 2026-11-15 |
|---|---|---|
| openfga/openfga | 5.8k | 6.1k |
305 Stars in the last 53 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The example database authenticates with the password password
The compose file in the repository root is a complete Postgres-backed deployment, and it hands you everything needed to run it, including the parts you would want to change.
curl -LO https://openfga.dev/docker-compose.yaml
docker compose up
Inside it, Postgres runs as `postgres:17` with a command that sets its connection ceiling, `postgres -c 'max_connections=100'`. Its credentials are `POSTGRES_USER=postgres` and `POSTGRES_PASSWORD=password`, and its port 5432 is published to the host. The datastore URI appears twice, once in a migration service and once in the server, and both read `postgres://postgres:password@postgres:5432/postgres?sslmode=disable`. Disabling TLS is the third default in a row, and it is written into the connection string rather than left to the reader.
The connection ceiling is echoed on the other side, where the server sets `OPENFGA_DATASTORE_MAX_OPEN_CONNS=100` with a comment pointing back at the database container. That is the one value in the file that is genuinely tuned rather than defaulted.
The repository ships two compose files and the instructions mention neither
The tree at the root of this repository contains `docker-compose.yaml` and `docker-compose.override.yaml`. The installation section tells you to download the first of them from `openfga.dev` and then run `docker compose up`. The override file is not mentioned in the installation instructions, although the README links the local `docker-compose.yaml`.
The download writes into whatever directory you are standing in. So the documented path to a local Postgres deployment involves fetching a file over the network that you could have read in the repository you just cloned, and the override that would apply on top of it is silently out of the picture. A developer who already has a `docker-compose.override.yaml` in the working directory gets compose's automatic merge of the two, which is a behaviour most people learn the hard way.
The README does say the file is an example of how to launch OpenFGA with Postgres, and it points twice at a Running in Production guide for real deployments.
The Playground is local only, and the escape hatch is a wildcard address
The Playground is the modelling UI, and the page is clear about its scope: it is intended for local development only, and it can currently only be configured to connect to an OpenFGA server running on `localhost`. Turning it off and moving its port are both one flag:
./openfga run --playground-enabled=false./openfga run --playground-enabled --playground-port 3001The documented way to point it at a server somewhere else is the `OPENFGA_HTTP_ADDR` environment variable, which the page says configures the address at which the Playground expects the OpenFGA server to be. The example it gives sets that address to `0.0.0.0:4000` and publishes 4000 alongside 3000. A wildcard address is a bind address rather than a destination, so the example shows the server listening on all interfaces and the Playground being told to expect it there, which is not the same thing as the Playground connecting to a remote host.
The default URL is `http://localhost:3000/playground`, plain HTTP on loopback.
The sample response from the verification step is dated 2022
The verify step posts to the stores endpoint and shows what comes back:
curl -X POST 'localhost:8080/stores' \
  --header 'Content-Type: application/json' \
  --data-raw '{"name": "openfga-demo"}'
The response body in the documentation carries an id of `01G3EMTKQRKJ93PFVDA1SJHWD2` and timestamps of `2022-05-19T17:11:12.888680Z` for both created and updated. The id is a lexicographically sortable identifier of the kind the module pulls in as a dependency, which is consistent with how a store key would be built. The date is not: it is four years older than the newest release, which is v1.22.1 from 2026-10-28.
The same three line curl appears twice on the page, once in the quickstart as the way to create a store and again under verify installation. Nothing has drifted between the two copies, so the duplication is harmless, but it does mean the quickstart's only example of talking to the server is repeated rather than extended.
Four ports in compose, three in the image
The quickstart publishes two ports:
docker run -p 8080:8080 -p 3000:3000 openfga/openfga runThe compose file publishes four: 8080 for HTTP, 8081 for gRPC, 3000 for the Playground, and 2112 for Prometheus metrics, each with a comment naming its purpose. The container image's `EXPOSE` lines list 8081, 8080 and 3000, and 2112 is not among them. So a metrics endpoint is reachable in the reference deployment while being absent from the image's declared surface, and the only place its port appears is a comment in a compose file.
Two operational notes come with the image. The HTTP server tries to reach the gRPC server over a unix domain socket first and falls back to a TCP socket when it cannot, which means running the container with `--read-only` also requires `--tmpfs`, with `--tmpfs /tmp` given as the example, because the socket needs somewhere to live.
The image also carries a health check that runs a gRPC health probe against port 8081 every five seconds, copied in from a separate pinned image, with a comment in the Dockerfile asking that the sibling goreleaser Dockerfile be updated by hand whenever that probe version changes.
An authorization engine that depends on the Docker client
The module file lists at least forty direct dependencies, and two of them are unexpected in a permission engine: the Docker API package and the Docker client, along with a containerd error package.
The rest of the list maps cleanly onto what the project claims to do. A Common Expression Language implementation sits alongside the DSL library for authorization models, the API proto pinned to a pseudo-version from a commit dated 2026-03-19 and the language package at the tagged release v0.3.2. A migration library is there, which is why the compose file runs a separate service whose command is `migrate` before the server starts. Caching, hashing, JSON path extraction, JWT verification, a SQL builder, Postgres and MySQL drivers, Prometheus metrics and OpenTelemetry instrumentation for both gRPC and HTTP fill out the rest.
The version directives are worth noting. The module declares `go 1.26.0` and then pins a `toolchain` of `go1.27.3`, and the container build image is the matching Go 1.27.3, so the language floor and the build toolchain are one minor version apart.
Two build paths, and the Makefile vendors what the image does not
The Makefile starts with `.DEFAULT_GOAL := help`, so a bare `make` prints help instead of building anything. The help target is a pipeline rather than a list of echoes: it greps the makefile for target lines carrying a double hash comment, sorts them, and prints them through awk with a colour escape. Adding a target means adding a comment in the right shape, which is why the file is full of `##` annotations.
The dependency target runs `go mod tidy` followed by `go mod vendor`, and the package list is computed by filtering `go list ./...` through a grep that drops anything containing vendor. No `vendor/` directory appears in the repository's root listing, so vendoring is something you produce locally rather than something you inherit. The container image takes the other path: it mounts `go.mod` and `go.sum`, runs `go mod download`, and builds from the module cache with caching enabled and CGO switched off. Two supported routes, two different dependency layouts.
A data store variable defaults to in-memory at the top of the file, quoted inside the assignment, so anything that interpolates it carries those quote characters along. It is a small thing that only matters if you pass the variable on to something that parses it.
Agent instruction files, a telemetry package and no mention of either
The root of this repository contains `AGENTS.md` and `CLAUDE.md`, two instruction files aimed at coding assistants, alongside `plans/`, `scripts/` and a `telemetry/` package. A configuration schema, `.config-schema.json`, sits in the same root.
The rest of the root is a security and release pipeline made visible. Snyk, a Semgrep ignore file, a Fossa configuration, a golangci lint config and a codecov config sit next to each other, and the badge row at the top of the page links out to a security scorecard view, to SLSA, and to a core infrastructure best practices entry. Two goreleaser files, one of them for nightly builds, sit beside a `RELEASES.md`, and a second Dockerfile exists solely for the release pipeline, which is the file the Dockerfile comment asks you to update by hand when the health probe moves.
The last three releases are v1.21.0, v1.22.0 and v1.22.1, and the most recent push to the default branch is dated 2026-11-02.
Editorial conclusion
OpenFGA suits teams that want fine-grained authorization modelled as data rather than as code in an application, and it is a poor fit for anyone who needs the playground or the example configuration to be safe as shipped. Before deploying, read the production guide the quickstart points at, because the in-memory engine is ephemeral and the example Postgres credentials are placeholders. Decide which build path you are on, since the Makefile vendors dependencies into a directory the repository does not carry while the container image builds from the module cache. And treat the metrics port as undocumented, because the compose file publishes it and the image does not expose it.
Frequently asked questions
how to use openfga
The quickstart runs the server with `docker run -p 8080:8080 -p 3000:3000 openfga/openfga run`, then creates a store with a POST to `localhost:8080/stores`. That default in-memory engine is ephemeral, discards everything when the service stops, and is marked on the page as not for production.
openfga vs zanzibar
OpenFGA is described as inspired by Google Zanzibar, and the README links the Zanzibar research paper rather than shipping Zanzibar as a component. Zanzibar appears as the design inspiration; the engine itself is written in Go, with storage backends in memory, PostgreSQL, MySQL and a SQLite beta.
Is OpenFGA production ready?
The README's table of contents lists a Production Readiness section, and the quickstart separately warns that the default in-memory engine is ephemeral and not for production. For storage configuration, tuning and secure deployment, the page points at a Running in Production guide on the documentation site.
Who owns OpenFGA?
The repository lives under the `openfga` GitHub organization and the homepage is openfga.dev. The adopters list on the README leads with Auth0, linked to fga.dev, followed by Grafana Labs, Canonical, Docker, Agicap and Read.AI.
Is OpenFGA a ReBAC system?
The page calls it an authorization and permission engine inspired by Google Zanzibar, for modelling and enforcing fine-grained access control. What it does state is the interface: HTTP and gRPC APIs, a Playground for modelling, a CLI for testing authorization models, five official SDKs and the option of embedding it as a Go library.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/openfga-openfga)Star history chart for your README
[](https://hysenlabs.com/projects/openfga-openfga)Was this useful?