AppAuth-Android: the one thing it refuses to do is embed a WebView
Android client SDK for communicating with OAuth 2.0 and OpenID Connect providers.
At a glance
- What is it?
- A Java client SDK for OAuth 2.0 and OpenID Connect providers that maps the specifications directly rather than wrapping them, insists on a browser's custom tabs for authorization, and will not render a login page inside your own app. Its install line leaves the version as a placeholder, its state object is a JSON string you persist yourself, and the last commit on the default branch is dated 2026-03-22.
- Who is it for?
- This is the right SDK when you want protocol compliance rather than convenience, because every request and response type maps onto the specification and the browser stays the browser, which is also why your users see their own passwords typed into their own browser rather than into your UI. Three things to plan for.
- Can I use it commercially?
- Yes. Apache-2.0 is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Activity is slowing. The repository last received commits 7 months ago.
- What is it written in?
- Mainly Java, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
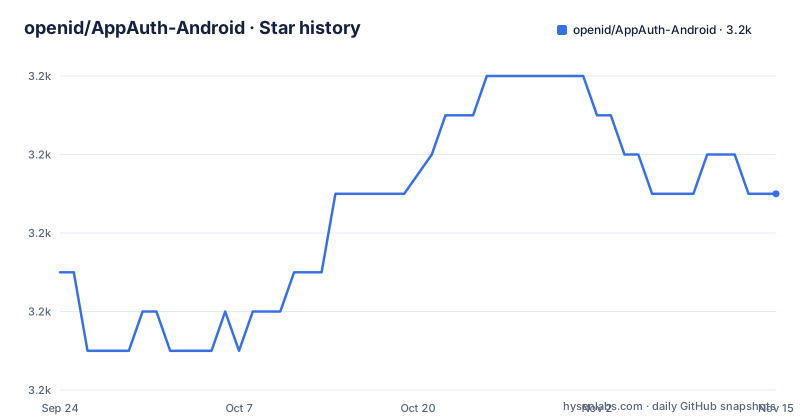
Star history
- openid/AppAuth-Android3,243 ★ · +2
| Repository | 2026-09-24 | 2026-11-15 |
|---|---|---|
| openid/AppAuth-Android | 3.2k | 3.2k |
2 Stars in the last 52 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The one thing it refuses to do is render a login page itself
Most Android OAuth libraries can either use the browser or draw a login page inside your app. This one will not do the second, and the reason is stated in one sentence in the README: WebView is explicitly not supported due to usability and security reasons. It follows the best practice document for native apps, which means authorization happens in the user's browser through a custom tabs implementation rather than in an embedded view. The practical consequence for an integrator is that your app never sees a password, which is the security argument, and that a browser has to be present, which is the usability one. The library prefers a browser with custom tabs but does not require one, so the older route is still available to devices that lack it.
The install line has a placeholder where the version goes
The download section is four lines long and three of them are a link to a package repository search. The fourth is the dependency itself:
implementation 'net.openid:appauth:<version>'The version is written as the word version inside angle brackets, which is how a placeholder is meant to be copied, but it means the README never tells you which version to use. There are also no GitHub releases for this repository, so there is no tag to match a build against either. The only place a number lives is the package repository itself, which makes the choice of version an explicit decision for the integrator and means that a project pinning dependencies has to record that number somewhere the README does not. Two badges at the top of the file cover coverage and the build workflow, so the state of the code is visible even though its version history is not.
The state object is a JSON string and your app decides where it lives
The conceptual overview starts from one class. The authorization state of the user is encapsulated in a state object, and that object is designed to be easily persistable as a JSON string using the storage mechanism of your choice. Three are named: shared preferences, a database, or a file. That is a deliberate boundary for an SDK, since it leaves the persistence policy to the application rather than choosing a storage abstraction and forcing it on every integrator. The same object also carries the convenience layer, with an update method for feeding a response back in so changes are tracked and persisted, and a method that automatically refreshes access tokens as necessary before an action that needs them. Everything else in the library is a direct mapping of the specification onto a data class.
Four stages, and the browser step only happens once
The recommended flow for a native app is the authorization code flow with a public client, and the stated advantage for native clients is that the browser part of the flow only needs to be performed once. The flow is then written out as four stages. Discover or specify the endpoints to talk to the provider. Get an authorization code by sending the user to a browser. Exchange that code for a refresh token, an identity token, or both. Then use access tokens derived from the refresh token against a resource server. At each stage the state object can optionally be updated with the result, so the four stages are independent operations that happen to be usable in order. The identity token in stage three is the reason the library is named for two specifications rather than one.
Redirects come in two flavours with different version floors
Where the authorization response comes back to your app depends on which redirect mechanism you choose, and the two have different requirements. Custom URI schemes work on every supported version of Android. App Links require a later release, named as Android M or API 23 and above. The library supports both, and it says so as a requirement rather than leaving it implicit. The floor for the library as a whole is stated separately and is much lower than either of those numbers: API 16, named by its platform version, which is the oldest supported release. So the compatibility story is a wide range at the bottom, a preferred mechanism that only exists on newer devices, and a fallback that works everywhere. The library also adds the proof key extension, which exists specifically to secure authorization codes in public clients when a custom URI scheme is the redirect method.
Providers that keep a client secret confidential may not work
There is one compatibility warning in the requirements section and it is more useful than the rest of the paragraph around it. In general the library can work with any authorization server that supports native apps as the practice document describes, through custom URI scheme redirects or App Links. But servers that assume all clients are web based, or that require clients to maintain the confidentiality of their client secrets, may not work well. That is the honest consequence of being a public client: a native app cannot keep a secret, so any server that requires one is out of scope by construction. A developer picking this SDK against an existing identity provider should check that point first, because no amount of configuration on the app side will fix it.
Every response comes back to an activity, and every request goes out through one class
The request and response types are described in parallel pairs, and the delivery mechanisms differ between them. An authorization request is dispatched through a method on the authorization service class, and the response object is then dispatched to whichever activity you choose, expressed through an intent. A token request is dispatched through a different method on the same class, and its response comes back through a callback instead. So one class is the single point through which every protocol exchange passes, which is what makes it possible to mock or wrap, and the return path differs by operation: an intent for the browser flow, a callback for the token exchange. The data classes themselves are described as modelling the specification as closely as possible, which is what buys flexibility across servers.
The demo app is in the same repository, and the last commit is from March 2026
The repository is laid out as a Gradle project with the wrapper for both platforms, the library in one directory and a demo application in another, and the demo's own instructions in a readme inside it. There is also a configuration directory for the build's static analysis, and three files about people rather than code: an authors file, a contributors file and a contributing guide, which is more credit bookkeeping than most projects of this size keep. The last commit on the default branch is dated 2026-03-22, and the project publishes no releases, so the release record that exists is whatever the package repository holds. That combination, a mature library with a long-lived compatibility floor and a wide commit history, sits against a default branch whose last commit is this past spring.
Editorial conclusion
This is the right SDK when you want protocol compliance rather than convenience, because every request and response type maps onto the specification and the browser stays the browser, which is also why your users see their own passwords typed into their own browser rather than into your UI. Three things to plan for. The install line gives you a placeholder where the version goes, so you have to pick a version from the package repository yourself, and the repository publishes no releases to match against. Authorization state is a JSON string you persist, so choosing and testing that storage is your first piece of work. And the server side has a compatibility limit: a provider that insists on client secret confidentiality will not work with a public native client.
Frequently asked questions
What is AppAuth for Android?
A client SDK for communicating with OAuth 2.0 and OpenID Connect providers. It maps the requests and responses of those specifications directly and follows the idiomatic style of Java, with convenience methods for common tasks such as performing an action with fresh tokens.
Why does AppAuth not support WebView?
Because it follows the best practice document for native applications, which uses a browser's custom tabs for authorization requests. The README states that WebView is explicitly not supported, for usability and security reasons.
How do I add AppAuth-Android to a project?
With one Gradle dependency line, and the README's own line leaves the version as a placeholder rather than naming one. The library is distributed through the central package repository, and this repository publishes no releases of its own.
How is authorization state stored with AppAuth?
The state object is designed to be persistable as a JSON string, so the storage mechanism is your choice, with preferences, a database or a file all named. Responses are fed back through the object's update methods, and it can refresh access tokens automatically before an action that needs them.
Which Android versions does AppAuth support?
API 16 and above. Both custom URI schemes and App Links can be used for redirects, with App Links requiring Android M or API 23 and above, and custom URI schemes working on every supported version.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/openid-appauth-android)Star history chart for your README
[](https://hysenlabs.com/projects/openid-appauth-android)Was this useful?