OpenKruise: five workload controllers that extend the Kubernetes core ones
Automated management of large-scale applications on Kubernetes (incubating project under CNCF)
At a glance
- What is it?
- A CNCF incubating project whose controllers sit alongside the Kubernetes core controllers: five advanced workloads, three sidecar mechanisms, five pod level operations and two protection objects, installed from chart pages the repository does not carry.
- Who is it for?
- OpenKruise fits platform teams that already run controllers across large clusters and need in-place updates, sidecar lifecycle control or a disruption budget that the built-in objects do not offer. It does not fit a small deployment: you are adding CRDs, webhooks and a second workload vocabulary to a cluster the core controllers already handle.
- Can I use it commercially?
- Check first. The repository uses a licence we do not classify automatically, so read its LICENSE file before any commercial use.
- Is it still maintained?
- Yes. The repository last received commits 10 days ago.
- What is it written in?
- Mainly Go, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
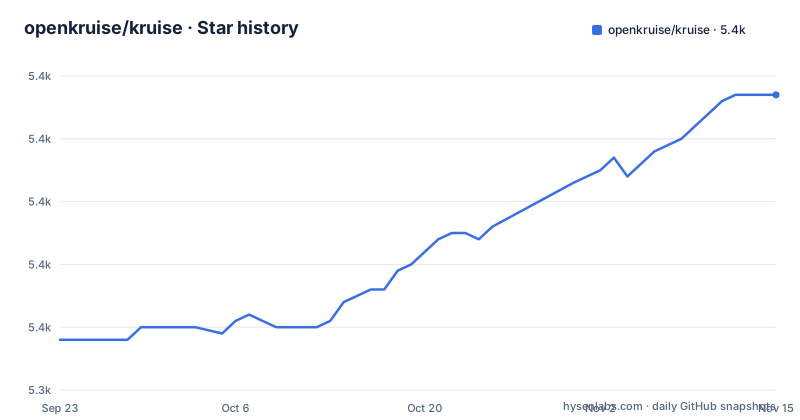
- openkruise/kruise5,387 ★ · +39
| Repository | 2026-09-23 | 2026-11-15 |
|---|---|---|
| openkruise/kruise | 5.3k | 5.4k |
39 Stars in the last 53 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Five workload kinds where Deployments and StatefulSets already live
Kruise is a group of controllers that extend and complement the Kubernetes core controllers, and the workload half of that is five custom resources. CloneSet covers stateless applications, Advanced StatefulSet covers stateful ones, Advanced DaemonSet covers daemon applications, BroadcastJob deploys jobs over specific nodes, and AdvancedCronJob creates a Job or a BroadcastJob periodically. Each keeps the basic behavior of its Kubernetes counterpart and adds in-place update, configurable scale and upgrade strategies, and parallel operations. The price for a platform team is a second vocabulary: five new resource kinds to learn, update rules that can surprise you, and templates you now have to review as carefully as the controllers that read them.
Sidecar lifecycle is split across three controllers
Sidecar handling is not one object but three. SidecarSet is for defining and upgrading your own sidecars, Container Launch Priority controls container startup order, and Sidecar Job Terminator ends sidecar containers in job type Pods once the main containers have completed. That third one exists because a Job Pod whose sidecar never exits is a Pod that never finishes, so something other than the main container has to bring the sidecar down. The cost is that sidecar behavior stops living in one spec you can read at a glance: injection, startup order and termination each need their own configuration, and upgrading a sidecar means changing a SidecarSet rather than editing an image tag in a manifest you own.
WorkloadSpread attaches to workloads, UnitedDeployment replaces them
Multi domain management targets clusters whose nodes differ along several axes at once: node pools, availability zones, architectures (x86 and arm), and node types (kubelet and virtual kubelet). Two mechanisms cover that, and they are not interchangeable. WorkloadSpread works by bypassing how an existing workload distributes its pods, so you keep the workload you already have. UnitedDeployment is a new workload of its own that manages multiple sub-workloads, which is the better fit when one logical application is spread across domains on purpose, and the worse fit when you would rather not restructure existing manifests. The repo does not put a limit on how many domains or sub-workloads either one accepts.
Five controllers act on running Pods instead of defining them
A second group does not create workloads at all. ContainerRecreateRequest lets a user restart or recreate containers inside a running pod. ImagePullJob pre-downloads images on specific nodes. ResourceDistribution spreads Secret and ConfigMap resources across namespaces. PersistentPodState keeps Pod state such as IP Retention. PodProbeMarker lets you customize the probe and return the result to the Pod. Each is a separate object to create, watch and clean up, and the README does not say how they compose. If you enable two on the same Pod, the ordering between a recreate request and a retained IP is not defined in the README, and that is exactly the case where a debugging session gets long.
Protection objects are enforced by generated webhooks and CRDs
Application protection has two parts: guarding Kubernetes resources and applications against cascading deletion, and PodUnavailableBudget, which targets application disruption or SLA degradation. The enforcement path is generated rather than hand maintained. In the Makefile, the manifests target runs controller-gen with CRD_OPTIONS set to "crd:crdVersions=v1" over ./apis/... and ./pkg/..., producing WebhookConfiguration, ClusterRole and CustomResourceDefinition objects written into config/crd/bases.
CRD_OPTIONS ?= "crd:crdVersions=v1"
ENVTEST_K8S_VERSION ?= 1.32.0
Install lives on the website, and the demo form still names chart 1.8.0
There is no install command in the README. Two paths are offered on the project site, one for the stable version and one for the latest version including alpha, beta and release candidate builds. The demo link points somewhere else entirely, at an Alibaba Cloud quick deploy form that installs Kruise on a Serverless Kubernetes cluster in three minutes, with the chart path pinned to versions/kruise/1.8.0 on the master branch. Recent releases are v1.9.1 from 2026-07-04, v1.8.5 from 2026-08-10 and v1.9.2 from 2026-10-19, so following the demo lands you on a chart behind the newest tags. Elsewhere the English bi-weekly community meeting line still reads TODO, while the APAC slot carries a day and time (Thursday 19:30 GMT+8) and a DingTalk group ID.
The image builds two binaries, then empties /bin and /usr/bin
The Dockerfile builds manager from main.go and daemon from cmd/daemon/main.go inside a Go 1.23.9 Alpine builder pinned by digest, both with CGO_ENABLED=0.
ARG BASE_IMAGE=alpine
ARG BASE_IMAGE_VERSION=3.21@sha256:56fa17d2a7e7f168a043a2712e63aed1f8543aeafdcee47c58dcffe38ed51099
FROM golang:1.23.9-alpine3.21@sha256:fb7ea5cd19bc4eea3eb0d1972919ec0f6229b138985ce4b35ce5846c6bc02973 AS builder
RUN CGO_ENABLED=0 GO111MODULE=on go build -a -o manager main.go \
  && CGO_ENABLED=0 GO111MODULE=on go build -a -o daemon ./cmd/daemon/main.go
ENTRYPOINT ["/manager"]
The runtime stage copies the two files to /manager and /kruise-daemon, then empties /usr/local/sbin, /usr/local/bin, /usr/sbin, /usr/bin, /sbin and /bin, and rewrites /etc/passwd to leave only root and nobody. An operator inspecting a stuck pod has logs rather than a shell to work with, and the daemon binary runs only where something references /kruise-daemon. Other targets have their own files: Dockerfile_windows, Dockerfile_multiarch and Dockerfile_helm_hook.
go.mod holds every Kubernetes library on v0.32.10
The module is github.com/openkruise/kruise with a go directive of 1.23.0, and the Kubernetes libraries move as one block.
module github.com/openkruise/kruise

go 1.23.0

require (
	k8s.io/api v0.32.10
	k8s.io/apimachinery v0.32.10
	k8s.io/client-go v0.32.10
	k8s.io/kubernetes v1.32.10
	sigs.k8s.io/controller-runtime v0.20.2
)
Alongside them sit robfig/cron/v3 v3.0.1, docker/distribution v2.8.2+incompatible, three separate jsonpatch modules, AdaLogics go-fuzz-headers, prometheus client_golang v1.19.1, spf13/cobra v1.8.1, and both ginkgo v1.16.5 and ginkgo/v2 v2.27.5. The build side matches: ENVTEST_K8S_VERSION defaults to 1.32.0, and a go_check target calls scripts/check_go_version with 1.23 before the format targets run. Licensing is stated as Apache License 2.0 with the text in LICENSE.md, while the license field shown for the repository reads NOASSERTION.
Editorial conclusion
OpenKruise fits platform teams that already run controllers across large clusters and need in-place updates, sidecar lifecycle control or a disruption budget that the built-in objects do not offer. It does not fit a small deployment: you are adding CRDs, webhooks and a second workload vocabulary to a cluster the core controllers already handle. Before installing, check which chart track the site is serving, since the quick deploy form still names chart 1.8.0 while v1.9.2 is out, and confirm your cluster lines up with the Kubernetes libraries at v0.32.10.
Frequently asked questions
What is OpenKruise used for?
It is a CNCF incubating project made of controllers that extend and complement the Kubernetes core controllers for workload and application management, among them CloneSet for stateless applications, Advanced StatefulSet, SidecarSet for sidecars, and PodUnavailableBudget for disruption control.
How do I install OpenKruise?
The README carries no install command. It points at two pages on the project site, one for the stable version and one for the latest version including alpha, beta and rc, plus an Alibaba Cloud quick deploy form that installs it on a Serverless Kubernetes cluster in three minutes using chart 1.8.0.
Which Kubernetes version does OpenKruise target?
go.mod requires Go 1.23.0 and pins the Kubernetes libraries to v0.32.10, with k8s.io/kubernetes at v1.32.10 and controller-runtime at v0.20.2. The Makefile sets ENVTEST_K8S_VERSION to 1.32.0, and a go_check target runs scripts/check_go_version with 1.23.
What does OpenKruise add to a Deployment?
Its workloads add in-place update, configurable scale and upgrade strategies, and parallel operations on top of the basic behavior of the Kubernetes originals. Five workload kinds are offered: CloneSet, Advanced StatefulSet, Advanced DaemonSet, BroadcastJob and AdvancedCronJob.
How active is the OpenKruise project?
The repository is not archived and the last push is dated 2026-10-20. Recent releases include v1.9.2 on 2026-10-19, v1.8.5 on 2026-08-10 and v1.9.1 on 2026-07-04, and CONTRIBUTING.md holds the contribution guide.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/openkruise-kruise)Star history chart for your README
[](https://hysenlabs.com/projects/openkruise-kruise)Was this useful?