CMake 3.14 builds it, CMake 4 breaks it, and the Docker images are from 2021
A library for doing homomorphic encryption operations on tensors
At a glance
- What is it?
- TenSEAL is a tensor layer over Microsoft SEAL exposed through a Python API, with BFV for integers and CKKS for real numbers. Its own documentation is unusually candid about the paths that do not work: the published container images are four years stale, the Bazel build is broken, and the C++ microbenchmarks cannot run.
- Who is it for?
- Judgment: TenSEAL is the practical choice for homomorphic encryption experiments in Python, and the strongest signal of that is that the difficult parameter choices are delegated back to SEAL rather than re-explained. Anyone using it should treat the noise budget as the real constraint, since a CKKS context is a finite budget and the README says so plainly, and should pick parameters from SEAL's own examples rather than from a tutorial snippet.
- Can I use it commercially?
- Yes. Apache-2.0 is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 23 days ago.
- What is it written in?
- Mainly C++, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
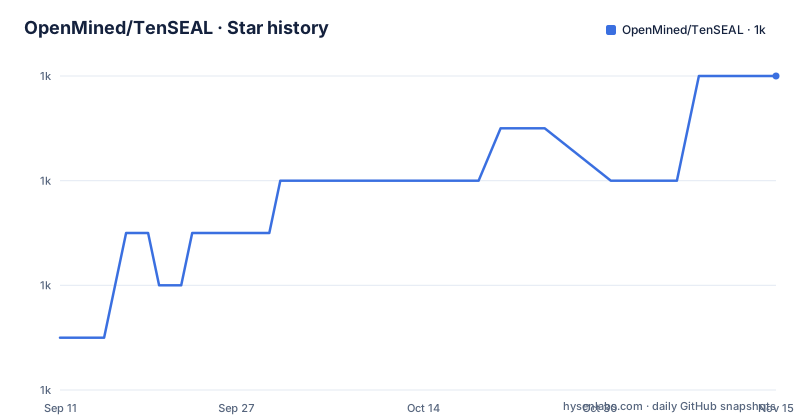
- OpenMined/TenSEAL1,042 ★ · +5
| Repository | 2026-09-11 | 2026-11-15 |
|---|---|---|
| OpenMined/TenSEAL | 1k | 1k |
5 Stars in the last 65 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The encryption parameters belong to SEAL, not to TenSEAL
TenSEAL is a binding over Microsoft SEAL with a tensor layer added on top, and it is careful not to rename the cryptography. The three parameters in every example, `poly_modulus_degree`, `coeff_mod_bit_sizes` and `global_scale`, carry exactly their SEAL meaning, and the documentation says so rather than inventing TenSEAL-specific variants. The consequence is stated in one sentence: choosing them determines both the security level and how many operations you can chain before the noise budget is exhausted. That is the single most important thing to internalise before writing any code, because a CKKS context is a finite budget and every addition, multiplication and dot product spends some of it. The worked example uses the CKKS scheme with a polynomial modulus degree of 8192, coefficient modulus bit sizes of 60, 40, 40 and 60, Galois keys generated once, and a global scale of two to the fortieth, then adds two encrypted vectors and takes a dot product, both of which decrypt to approximately the plaintext result.
Two schemes, and an escape hatch to the whole SEAL API
The feature list splits cleanly by what you are encrypting. BFV handles vectors of integers, CKKS handles vectors of real numbers, and both go through the same encrypt and decrypt calls. The arithmetic is the familiar set: element-wise addition, subtraction and multiplication, for encrypted-encrypted pairs and for encrypted-plain pairs, plus a dot product and vector-matrix multiplication. Above that sits the tensor layer, with CKKSTensor and BFVTensor as n-dimensional encrypted types supporting reshape, broadcast and transpose, so a model-shaped operation does not have to be flattened by hand. Contexts, keys and encrypted tensors can all be serialised, which is what makes a session survive a process boundary. The last feature is the interesting one for anyone who outgrows the wrapper: the complete SEAL API is reachable under `tenseal.sealapi`, so nothing in the underlying library is actually hidden. You can drop down a level without leaving the package.
Five wheel targets, and no Intel Mac among them
Prebuilt wheels are published for every supported Python version on five targets: Linux glibc on x86-64 as `manylinux_2_28_x86_64`, Linux musl on x86-64 as `musllinux_1_2_x86_64`, Linux glibc on aarch64 as `manylinux_2_28_aarch64`, macOS on Apple Silicon as `macosx_14_0_arm64`, and Windows x64 as `win_amd64`. The Linux pair exists because glibc and musl need different builds, and the musl wheel is what makes the Alpine-based container images work, with pip choosing automatically. The gap in the table is macOS on Intel, which has no wheel at all. Since a source distribution is also published, `pip install tenseal` still works there, it just compiles the C++ extension locally, which puts you straight into the build caveats. TenSEAL requires Python 3.11 or newer, and depends on NumPy. The whole install is one line:
pip install tensealChecking it is two more:
import tenseal as ts
print(ts.__version__)
The build has a floor at 3.14 and breaks at 4.0
Building from source needs a C++17 toolchain and CMake 3.14 or newer: GCC 7 or Clang 5 on Linux, Xcode 15.x command line tools on macOS, Visual Studio 2017 or newer on Windows. Every third-party dependency, Microsoft SEAL and Protocol Buffers included, is fetched and built by CMake, so there is nothing to install by hand and no submodules to initialise. Then the two warnings, which together define the real supported range. With CMake 4.0 or newer the build fails with a compatibility error, because some vendored dependencies still declare a pre-3.5 minimum, and the workaround is to set `CMAKE_POLICY_VERSION_MINIMUM=3.5` in the environment. On macOS, AppleClang 17 and newer, which is Xcode 16 and up, currently fails to compile the vendored xtensor, so the instruction is to use Xcode 15.x or install the published wheel instead. The documentation frames the CMake issue as a note rather than as a ceiling, but it functions as one.
The container images and the Bazel build are both marked as broken
Two sections carry an explicit TODO, and they are the most useful things in the installation guide. The Docker images are described as unmaintained: the newest was published in 2021 for v0.3.4, both the plain tag and the dev tag are far behind the current release, and the `docker-images/` directory targets Python 3.6 to 3.9, all of which are end of life and below the supported minimum. The instruction is not to rely on them, and refreshing or retiring them is tracked as future work. The Bazel build is worse: currently broken, with a workflow that runs on demand only, dependency pins that have drifted from the CMake build, and no migration to bzlmod. The tree still carries BUILD.bazel and a WORKSPACE file, which is the pre-bzlmod layout, consistent with that note. A side effect worth knowing: the C++ microbenchmarks under the tests directory are only wired up through Bazel, so they cannot currently be run at all, even though the Python benchmark suite publishes results for every merge to main.
The build hook switches Intel HEXL off
The extension is built through a small custom setuptools command, and reading it tells you what the build does not do. The package metadata lives in pyproject.toml and only the pieces that cannot be expressed declaratively remain in setup.py, namely the extension declaration and the command classes. The build command first shells out to `cmake --version` and, if that fails, raises a RuntimeError naming every extension it was trying to build, so a missing CMake produces a clear message rather than a traceback. The CMake arguments it passes are short: SEAL's Intel HEXL support is explicitly set to off, the library output directory is redirected to the extension directory setuptools expects, and the Python executable is pinned to the interpreter running the build. On Windows it adds the per-configuration output directory, passes the x64 architecture flag when the interpreter is 32-bit on a 64-bit machine, and adds MSBuild switches for parallelism and file tracking.
NumPy became a dependency because of an import at module scope
There is a comment in the manifest explaining why NumPy is now a declared dependency, and it is a small history of a packaging bug. `tenseal.tensors.plaintensor` imports NumPy at module scope, so importing the package fails without it; the dependency was previously undeclared, which meant a bare `pip install tenseal` produced an unimportable package. The same file solves a related problem with the version. The version is dynamic, read from `tenseal.version.__version__`, but setuptools reads that attribute statically, so building does not require importing the package or its C extension, which would otherwise mean compiling the extension in order to find out what version you are building. Classifiers cover Python 3.11 through 3.14 and the topic is marked as cryptography. The development group installs with uv or pip, and a comment there records that black and flake8 are gone, replaced by ruff through pre-commit.
Three releases in six weeks, with the version living in one Python file
The release cadence is steady rather than fast: v0.3.16 on 3 August 2026, v0.3.17 on 4 August, and v0.3.18 on 12 September, which is also the date of the last push to the repository. Versions are still on the 0.3 line and have been for a while, so anything that depends on the 0.3 series API should be comfortable, and the changelog is at the root for anyone who needs the detail. The dependency story is equally old-fashioned in a useful way: there is a pyproject.toml, a setup.py for the build hooks, a MANIFEST.in, a pytest.ini, a CMakeLists.txt, a cmake/ directory, a third_party/ directory, a CHANGELOG.md, a RELEASING.md and a SECURITY.md. Installation is by pip, there is no conda-forge channel, and the documentation points at uv as the way to get a specific interpreter without touching the system Python, including a one-off command that fetches the interpreter and the package and discards the environment afterwards.
Editorial conclusion
Judgment: TenSEAL is the practical choice for homomorphic encryption experiments in Python, and the strongest signal of that is that the difficult parameter choices are delegated back to SEAL rather than re-explained. Anyone using it should treat the noise budget as the real constraint, since a CKKS context is a finite budget and the README says so plainly, and should pick parameters from SEAL's own examples rather than from a tutorial snippet. Three practical notes before you plan an environment. The Intel HEXL acceleration is switched off in the build hook, so a source build will not use it. The source build has both a floor and a ceiling, CMake 3.14 and an undocumented practical maximum below 4.0 unless you set a policy variable. And the container images and the Bazel build are marked as not to be relied on, so budget for a native build rather than a container.
Frequently asked questions
how to install tenseal
Install with pip, which pulls a prebuilt wheel for Linux glibc, Linux musl, Linux aarch64, macOS on Apple Silicon or Windows x64. TenSEAL needs Python 3.11 or newer and depends on NumPy. If no wheel exists for your platform, pip falls back to the source distribution, which needs a C++17 toolchain and CMake 3.14 or newer.
What is TenSEAL and what is underneath it?
A library for homomorphic encryption operations on tensors, built on Microsoft SEAL. It exposes a Python API while implementing most operations in C++, and the encryption parameters it takes, poly_modulus_degree, coeff_mod_bit_sizes and global_scale, carry exactly their SEAL meaning.
Which encryption schemes does TenSEAL support?
BFV for vectors of integers and CKKS for vectors of real numbers. On top of both it provides n-dimensional CKKSTensor and BFVTensor types with reshape, broadcast and transpose, plus element-wise arithmetic, dot products, vector-matrix multiplication and serialisation of contexts, keys and tensors.
Why does building TenSEAL from source fail with CMake 4?
Because some vendored dependencies still declare a pre-3.5 minimum, and CMake 4 removed compatibility with it. The documented workaround is to set CMAKE_POLICY_VERSION_MINIMUM=3.5 in the environment. On macOS, AppleClang 17 and newer also fails to compile the vendored xtensor, so Xcode 15.x or a published wheel is needed.
Can I use the TenSEAL Docker images?
The documentation says not to rely on them. The images on Docker Hub are unmaintained, the newest was published in 2021 for v0.3.4, and the docker-images/ directory targets Python 3.6 to 3.9, which are end of life and below the supported minimum of 3.11.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/openmined-tenseal)Star history chart for your README
[](https://hysenlabs.com/projects/openmined-tenseal)Was this useful?