OpenOSINT: the tool count changes depending on which paragraph you read
AI-powered OSINT agent with interactive REPL, MCP server, and CLI. 19 tools. Works with Claude, GPT-4, or local models. For authorized security research only.
At a glance
- What is it?
- OpenOSINT is a Python OSINT agent that presents the same twenty-odd lookup tools through four interfaces: a REPL, a CLI, an MCP server and a browser web UI. The engineering worth reading is in the deployment posture and the dependency shape, and the number to distrust is the one in the headline.
- Who is it for?
- This is a tool for someone who already has an authorization question answered, because it makes no attempt to ask one and it cannot: the tools query breach records, search engines and third-party APIs on identifiers the operator supplies. Two things make it more careful than the marketing suggests.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository received new commits within the last day.
- What is it written in?
- Mainly Python, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
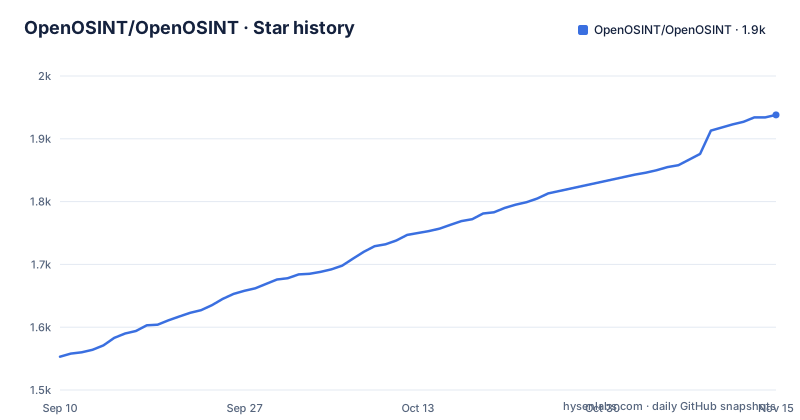
- OpenOSINT/OpenOSINT1,938 ★ · +385
| Repository | 2026-09-10 | 2026-11-15 |
|---|---|---|
| OpenOSINT/OpenOSINT | 1.6k | 1.9k |
385 Stars in the last 66 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Nineteen tools in the table, twenty everywhere else
The counts do not agree. The repository description says 19 tools. The introduction says 20 investigation tools behind a natural-language interface. The MCP row says all 20 tools are exposed to any MCP-compatible client. And the list under the 20 modular tools heading names nineteen entries: email, username, breach, WHOIS, IP, subdomain, dorks, paste, phone, Shodan, VirusTotal, Censys, IP2Location, AbuseIPDB, GitHub, DNS, live dork search, URL scraping and SERP footprint. A reader who counts the table lands on nineteen, and every number except that one says twenty. The pyproject description repeats the claim a third time, calling the package an interactive REPL plus 20 tools.
What is not in dispute is the interface shape, and the three shortest ways in are on the page itself:
# Interactive AI REPL (default)
openosint

# Web interface
openosint web

# Direct tool (no AI)
openosint email [email protected]
That last line matters for the rest of this article, because it is the same agent reached with the model removed. A live demo is offered at demo.openosint.tech where you bring your own Anthropic, OpenRouter or Ollama key and there is no signup. For a tool whose central idea is that an agent selects the right query for a target, a count that varies by paragraph is minor, and it is still the number most likely to be copied into a procurement note.
The web interface publishes on loopback, with a host allowlist
The compose file that runs the web interface gets a deliberately narrow default. The published port mapping is `${OPENOSINT_BIND:-127.0.0.1}:8080:8080`, so the service is reachable from the host only, and a comment beside it explains how to widen that on purpose by setting OPENOSINT_BIND to 0.0.0.0. Two more values travel with it. OPENOSINT_PUBLISHED_BIND declares what the port is published on, with a comment noting that the container itself binds 0.0.0.0 and only an exact loopback value lifts the restriction. OPENOSINT_ALLOWED_HOSTS defaults to localhost,127.0.0.1 and is labelled a host-header check for DNS rebinding protection, with instructions to add any other names you reach it by.
Two smaller decisions carry as much weight. The `.env` file is declared optional, with required set to false and a comment saying the web UI starts with no keys configured, so a first run is never blocked on having an API key. And storage is split: the reports directory is bind-mounted from the working tree, while a named volume, openosint-data, holds everything else, which is what keeps a graph database and session history across container re-creation. The application layer matches: POST /api/setup stays localhost-only unless OPENOSINT_SETUP_TOKEN is set, and when it is set, remote callers have to send the value as an X-Setup-Token header.
The image installs the package editable so saved keys resolve
The Dockerfile explains its own choices, which is rarer than it should be. It starts from python:3.11-slim and installs git, build-essential, pkg-config and libicu-dev, with a comment saying that a compiler is needed once to build PyICU, which the graph view's followthemoney dependency requires, and that the compiler is purged afterwards.
The package itself is installed with `pip install --no-cache-dir -e ".[graph]"`, and the comment above it gives the reason: the install is editable on purpose because the setup endpoint saves keys to the .env at the package root, which has to resolve to /app/.env. Three optional OSINT binaries are installed alongside, named holehe, sherlock-project and sublist3r. Then OPENOSINT_HOME is set to /data, /data is declared a volume, 8080 is exposed, and the command symlinks /data/.env to /app/.env before execing `openosint web --host 0.0.0.0 --port 8080 --no-browser --allow-remote`. The comment on that flag cites GHSA-cqr4-hcfp-m6m4 and says the reason it is safe here is that only the container network boundary is exposed, and the port should be published to trusted networks only.
The only walkthrough is a transcript, and a paid link follows it
There is no written procedure anywhere in the page. The usage section is a single recorded session: a target described in plain language, the agent running a dork generator and an email search, an account list coming back, a breach lookup returning two dated breaches, then a username search on an identifier taken from the email findings and marked in the transcript as a pivot. It ends with a report written to a timestamped Markdown file under `reports/`, named for the moment it was produced.
That transcript is worth reading as design rather than as documentation, because it shows the intended loop: one lookup produces the input for the next, and the agent chooses. The parallel option is described in the feature table as `--parallel` running complementary tools concurrently through `asyncio.gather()`, which is the escape hatch for the case where two lookups do not depend on each other.
What follows the transcript is not documentation either. The line immediately after it offers the full investigation workflow behind it as a paid kit, priced at $55 through a Gumroad link with tracking parameters attached.
The demo says its entities are seeded, not gathered
The globe visualisation comes with an unusually direct disclaimer: it is a deterministic, synthetic-data demo in which every entity shown is fictional, it can be regenerated with `demo/web_demo.py`, and the entities are seeded at the statement layer rather than produced by the current mappers, with `demo/README.md` holding the detail. That last clause is the important one. Seeded at the statement layer means the demo inserts the relationships it wants to display rather than running lookups and showing what came back, so the shape on screen is a design mockup of an investigation and not a record of one.
The supporting files match that description. The demo directory holds two scripts, `seed_demo.py` and `web_demo.py`, a README, a VHS tape called `graph_demo.tape`, and four recorded variants of the same visualisation as gif and webm. Two more artefacts sit at the repository root, `web-demo-edit.gif` and `openosint.tape`, and the README links an MP4 under `assets/demo`. A separate newsletter is advertised in the same block, one AI-OSINT workflow a week plus a roundup.
An MIT core with three paid layers beside it
The license is MIT and the install line is `pip install openosint`, but the page routes every other path toward something you pay for. The first layer is a hosted version sold as pay-per-use Apify Actors: email recon at from $0.015 per run for linked accounts across more than a hundred services, username recon at $0.04 per username, and domain recon at $0.02 per domain returning an A to F email-security grade, RDAP data and dork URLs. The same three are offered as MCP tools at `mcp.apify.com` with no server to run. The page states plainly that cloud usage funds ongoing development of the self-hosted project.
The second layer is the paid kit linked after the transcript. The third is sponsorship, and here the integrations reach inside the tool list: IP2Location is documented as powering `search_ip2location`, with a guide under `docs/integrations/`, while RapidProxy and TestMu AI are listed alongside. SPONSORSHIP.md is described as open to breach and compromised-credential data providers and to email and identity lookup providers, which is a statement about what the project is looking for. The root also carries COMMERCIAL.md, COMMERCIAL-LICENSE.md, CLOUD.md, a `legal/` directory and a `_leadmagnet/` directory. Two different homepages are recorded as well, openosint.tech in the project metadata and openosint.github.io in the package URLs.
Nineteen dependencies, three Python versions, one stable classifier
The dependency list is where the shape of the program shows. The MCP client library and the Anthropic SDK sit at the top with a capped range on the first, then requests and httpx for blocking and async HTTP, aiohttp alongside them, dnspython for name resolution and python-whois for registration records. FastAPI, uvicorn and sse-starlette are the web layer, asyncpg is a PostgreSQL driver, authlib and itsdangerous are session and signing machinery, cryptography and pyyaml are general utilities, and reportlab accounts for PDF output. rich and prompt_toolkit are the terminal interface, and python-dotenv handles the environment file every entry point reads. Nineteen in total, none of them pinned to an exact version, with `uv.lock` at the root even though the install instructions use pip.
The Python story has three answers. requires-python is >=3.10, the classifiers name 3.10, 3.11 and 3.12, and the container builds on 3.11. The project also declares itself as Development Status 5, Production/Stable, at version 2.30.0, with three releases inside two weeks: v2.29.0 on 2026-09-17, then v2.29.1 and v2.30.0 on the same day, 2026-10-01, hours apart. One configuration note is explicit about deprecation: OPENOSINT_MODEL still works as an alias for ANTHROPIC_MODEL but logs a one-time warning.
Every query leaves your machine and reaches a third party
This is a reconnaissance toolset and the boundaries are worth stating plainly, because the software draws them itself and no further. Both the project description and the pyproject description limit use to authorized security research, and the root carries a DISCLAIMER.md, a SECURITY.md and a `legal/` directory. Beyond that the tooling imposes nothing: nothing asks whether a target consented, and nothing distinguishes an engagement you were hired to run from a person you decided to look up.
What the tool list implies about traffic is concrete. Breach lookup, username enumeration, WHOIS, subdomain enumeration through sublist3r, paste search, phone and IP lookups, dork generation, live dork search, URL scraping and SERP footprint all send an identifier you supply to a service you do not control, and Shodan, VirusTotal, Censys, AbuseIPDB and IP2Location each need your own API key in the .env file. Generated dork URLs are aimed at search engines on someone else's infrastructure. The image installs holehe and sherlock-project alongside, both of which query many third-party sites in a single run.
The practical consequence is that third-party rate limits and terms apply to whoever runs it, and that image is a signature of the operator's intent. Scope, consent and the record of what was collected stay entirely outside the tool.
Editorial conclusion
This is a tool for someone who already has an authorization question answered, because it makes no attempt to ask one and it cannot: the tools query breach records, search engines and third-party APIs on identifiers the operator supplies. Two things make it more careful than the marketing suggests. The web surface defaults to loopback with a host allowlist and a setup token, and the container configuration is commented closely enough that you can see why each decision was taken. Against that, the tool count disagrees across the page, the demo data is seeded rather than gathered, and a commercial layer sits beside the MIT core selling the same tools per run. Before using it on anything real, confirm the authorization in writing, keep the port on loopback, count the nineteen named tools yourself rather than the twenty in the headline, and read the sponsor integration list, since two of those features call out third-party data services by name.
Frequently asked questions
what is openosint
OpenOSINT is a Python OSINT agent for security researchers and analysts, installed with `pip install openosint` and used as a REPL, a CLI, an MCP server or a browser web UI. Its own descriptions limit it to authorized security research use only.
How many tools does OpenOSINT actually have?
The counts disagree. The repository description says 19 tools, the introduction says 20 investigation tools, the MCP row says all 20 tools, and the list under the 20 modular tools heading names nineteen entries, from email and username through to SERP footprint.
Which AI backends can OpenOSINT use?
Anthropic Claude by default, local Ollama, or any OpenAI-compatible endpoint such as LiteLLM, vLLM or LM Studio. A self-hosted OpenAI-compatible gateway takes precedence over Ollama when no ANTHROPIC_API_KEY is set, and that server has to support tool calling.
Is OpenOSINT free to run?
Self-hosting is MIT and free with your own keys. A hosted option sells the same tools as pay-per-use Apify Actors at from $0.015 per email run, $0.04 per username and $0.02 per domain, and the page says cloud usage funds the self-hosted project.
How is the OpenOSINT web interface secured by default?
The compose file publishes 8080 on loopback only and sets a host-header allowlist defaulting to localhost and 127.0.0.1. POST /api/setup stays localhost-only unless OPENOSINT_SETUP_TOKEN is set, in which case remote callers must send the value as an X-Setup-Token header.
Which Python versions does OpenOSINT support?
requires-python is >=3.10 and the classifiers name 3.10, 3.11 and 3.12. The container image builds on python:3.11-slim, and the root carries a uv.lock alongside pip install instructions.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/openosint-openosint)Star history chart for your README
[](https://hysenlabs.com/projects/openosint-openosint)Was this useful?