OpenSign self-hosting: a Parse backend, floating image tags and a .env.prod you write yourself
🔥 The free & Open Source DocuSign alternative
At a glance
- What is it?
- OpenSign is an open source e-signing application that pitches itself against DocuSign. Its signing features are broad, but the Docker stack in the repository pulls unpinned images, publishes MongoDB on the host and loads an env file the repository does not ship.
- Who is it for?
- OpenSign suits teams that want guest OTP verification, signing order, expiring documents and an audit certificate on infrastructure they control, and who are comfortable editing a compose file.
- Can I use it commercially?
- Check first. The repository uses a licence we do not classify automatically, so read its LICENSE file before any commercial use.
- Is it still maintained?
- Yes. The repository last received commits 2 days ago.
- What is it written in?
- Mainly JavaScript, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
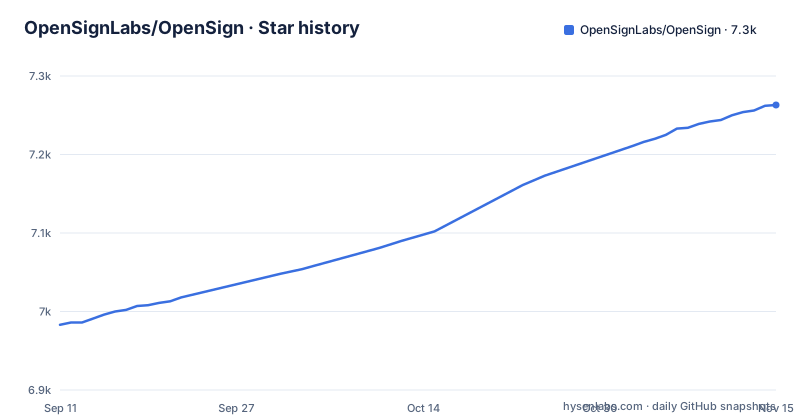
- OpenSignLabs/OpenSign7,263 ★ · +280
| Repository | 2026-09-11 | 2026-11-15 |
|---|---|---|
| OpenSignLabs/OpenSign | 7k | 7.3k |
280 Stars in the last 65 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Parse Server under an Express backend, React in front
OpenSign is a document e-signing application from OpenSignLabs, written mainly in JavaScript and positioned as a free replacement for DocuSign, PandaDoc, SignNow, Adobe Sign, Smartwaiver, SignRequest, HelloSign and Zoho Sign. The .env.example file splits configuration into a "Frontend config" block for a React app and a "Backend ExpressJS config" block, and the backend variables reveal what sits underneath. PARSE_MOUNT=/app is the path where the APIs are mounted, and MASTER_KEY is described as the secret that Parse dashboard uses to view all data in the database. Storage is MongoDB, reached through MONGODB_URI.
The two halves are tied together by one identifier. REACT_APP_APPID on the frontend must equal APP_ID on the backend, and both are described as a 12 character random string, although the example sets both to opensign, which is eight characters. PARSE_MOUNT carries its own warning: do not change it, because the variable is slated for removal and the value will be hardcoded in coming versions. The frontend finds the API through REACT_APP_SERVERURL, which for local development should be localhost:3000/api/app with your own port number substituted.
Example values that point at the vendor and expose a master key
Copying .env.example without edits produces a deployment that is not really yours. PUBLIC_URL is set to https://app.opensignlabs.com/ and REACT_APP_SERVERURL to https://app.opensignlabs.com/api/app, the hosted service, so an untouched frontend talks to the vendor's API rather than your backend. REACT_APP_GTM=GTM-123N7LD configures a Google Tag Manager container on all pages of the app; leave it in place and every page you serve loads a container ID you did not create.
The more serious one is MASTER_KEY=XnAadwKxxByMr. The comment states that this key allows access to all the data, and it is printed in a public repository. Any install that keeps it hands full database access to whoever reads the file. appName, set to open_sign_server, is visible in the verification emails sent to users, so it is worth changing for branding alone. GENERATE_SOURCEMAP=false is the one setting that is safe to keep; flip it to true only when you need sourcemaps for debugging the frontend.
Four containers pulled by tags that keep moving
docker-compose.yml defines four services. server runs opensign/opensignserver:main on port 8080, mounts the opensign-files volume at /usr/src/app/files and depends on mongo. mongo runs mongo:latest with data-volume at /data/db. client runs opensign/opensign:main on port 3000 and depends on server. caddy runs caddy:latest on 3001, 80, 443 and 443/udp, mounting ./Caddyfile into /etc/caddy/Caddyfile. All four share the app-network bridge.
The server receives NODE_ENV=production plus SERVER_URL=${HOST_URL:-https://localhost:3001}/api/app and PUBLIC_URL=${HOST_URL:-https://localhost:3001}. Caddy receives HOST_URL=${HOST_URL:-localhost:3001}, with no scheme in its default, so one HOST_URL value feeds two services that expect different shapes.
None of the image tags is pinned. The project publishes tagged releases (v3.0.0 on 2026-10-21, v3.0.1 on 2026-10-26, v3.1.0 on 2026-10-30), yet the compose file references none of them; it pulls main and latest. The consequence is that two installs made a week apart can run different server code and a different MongoDB build without any change on your side. To hold a version, edit the image lines yourself before the first pull.
The compose file loads .env.prod, which the repository does not contain
Both server and client declare env_file: .env.prod. The top level of the repository holds .env.example and .env.local_dev, but no .env.prod. The Makefile does not create it either: both of its targets copy .env.local_dev to .env, a different file name. Running the run target on a fresh clone therefore does not produce the file the two application containers read their settings from.
The practical result is that self-hosting starts with writing .env.prod by hand, using .env.example as the template and replacing the values covered above: your own PUBLIC_URL and REACT_APP_SERVERURL, a fresh MASTER_KEY, matching APP_ID and REACT_APP_APPID, and a MONGODB_URI that reaches the mongo container. The repository also carries INSTALLATION.md and USAGE.md next to the README; INSTALLATION.md is the file to read before trusting the Makefile, because the Makefile alone does not take a clean checkout to a running stack.
make build compiles a frontend the containers never run
The build target echoes the HOST_URL it was given, then runs these lines:
cp .env.local_dev .env
cd apps/OpenSign && cp ../../.env.local_dev .env && npm install && npm run build
HOST_URL=${HOST_URL} docker compose up --build --force-recreate
The run target is shorter and starts the stack detached:
cp .env.local_dev .env
docker compose up -d
The gap is in the middle line of build. It installs dependencies and builds the frontend inside apps/OpenSign, but none of the four services in docker-compose.yml has a build key; every one of them pulls a published image. The --build flag has nothing to build, and the client container keeps serving opensign/opensign:main regardless of what npm run build produced. If you change code in apps/OpenSign, this pipeline will not put your change in front of users. You need your own image or a compose file with a build context before local edits reach the running app.
MongoDB, the server and the client are all published on the host
The mongo service maps 27018:27017. The server already reaches mongo over the app-network bridge, so the host mapping exists for access from outside the compose network, and on a machine with a public address and no firewall that means the database port is open to anyone who can reach the host. The mongo service also has no environment block, so the compose file sets no root credentials, while the example MONGODB_URI assumes a username:password pair. Those two have to be reconciled by you.
The same pattern applies to the application ports. server publishes 8080 and client publishes 3000 directly, alongside Caddy on 3001, 80 and 443. Traffic can therefore reach the backend and frontend without passing through the Caddyfile at all. For a production host, remove the ports entries for mongo, server and client, or block them at the firewall, and let Caddy be the only public entry point.
Guest OTP, signing order and the completion certificate
On the signing side the feature set is wide. Guest signers can only sign after entering a unique code sent to their email address. A sender can invite multiple signers, share signing links and enforce a signing sequence. Documents can be set to expire after a number of days, after which nobody can sign, and signers can reject a document with a reason that is passed back to the sender. The signing pad accepts hand drawn, uploaded image, typed and saved signatures. Templates store PDFs for repeated use, OpenSign Drive acts as a document vault, and the invitation, completion and reminder emails use templates you can customise.
Every completed document gets a completion certificate containing its logs, and the audit trail records timestamps, IP addresses, email IDs and phone numbers. On a self-hosted install that personal data lands in your MongoDB volume, which is one more reason to close port 27018. The feature list makes security claims, encryption, OTP and audit logs, but it names no certification such as HIPAA, so legal validity and compliance in your jurisdiction are questions for your own counsel.
API keys, Zapier, and a package.json that reads 1.0.6
API access works through a key generated from inside the app, with reference documentation at docs.opensignlabs.com under API-docs v1.1. A Zapier integration covers tools that have no direct connector, and the project lists cloud storage, CRM and enterprise platform integrations without naming them in its feature list.
Do not read the project's version from the root package.json. It is named opensign at version 1.0.6, its devDependencies are only husky, lint-staged and prettier, and its test script prints "Error: no test specified" and exits 1. It is repository tooling; the application lives under apps/. The real version line is the release tags, which reached v3.1.0 on 2026-10-30, with the last push on 2026-11-02 to the default branch, staging.
Licensing needs the same care. GitHub reports the license as NOASSERTION, while package.json declares AGPL-3.0. Scanners that read GitHub metadata will flag the project as unknown, so check the LICENSE file at the repository root before building OpenSign into a product.
Editorial conclusion
OpenSign suits teams that want guest OTP verification, signing order, expiring documents and an audit certificate on infrastructure they control, and who are comfortable editing a compose file. It is a poor fit for anyone expecting a pinned, turnkey install: before deploying, pin the image tags to a release, write your own .env.prod with a new MASTER_KEY and your own URLs, remove the 27018 MongoDB mapping, and read the LICENSE file, since GitHub reports NOASSERTION while package.json declares AGPL-3.0.
Frequently asked questions
Is OpenSign free?
OpenSign is open source, and its feature list says unlimited documents can be signed on the cloud hosted free version at opensignlabs.com. The root package.json declares AGPL-3.0, while GitHub reports the license as NOASSERTION.
Can OpenSign be self-hosted?
Yes. The repository ships a docker-compose.yml that runs opensign/opensignserver:main, opensign/opensign:main, mongo:latest and caddy:latest, with the two OpenSign containers reading settings from a .env.prod file that you create yourself.
Is OpenSign secure?
Guest signers must enter a unique code sent to their email before signing, and the audit trail records timestamps, IP addresses, email IDs and phone numbers. On a self-hosted OpenSign install you also need to replace the example MASTER_KEY and stop publishing MongoDB on host port 27018.
What is OpenSign?
OpenSign is an open source document e-signing application from OpenSignLabs, written mainly in JavaScript, positioned as an alternative to DocuSign, PandaDoc, SignNow, Adobe Sign and Zoho Sign.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/opensignlabs-opensign)Star history chart for your README
[](https://hysenlabs.com/projects/opensignlabs-opensign)Was this useful?