easy-rsa: a shell PKI utility that says master may be broken
easy-rsa - Simple shell based CA utility
At a glance
- What is it?
- easy-rsa is a command line utility for building and managing a certificate authority, from a root CA through intermediate CAs and certificate revocation lists. Its README spends most of its length on branch policy, including the warning that master may be broken and the list of releases that do not work with OpenSSL 3.
- Who is it for?
- Use easy-rsa when you want to run a certificate authority from a shell in a POSIX environment, and when you can accept a released version rather than the trunk. Do not pick an older line for a new deployment, because the README states that v3.0.4 through v3.0.6 and `release/3.0` are not compatible with OpenSSL 3.
- Can I use it commercially?
- Check first. The repository uses a licence we do not classify automatically, so read its LICENSE file before any commercial use.
- Is it still maintained?
- Yes. The repository last received commits 27 days ago.
- What is it written in?
- Mainly Shell, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 13, 2026, and from our analysis. They are not legal advice.
Star history
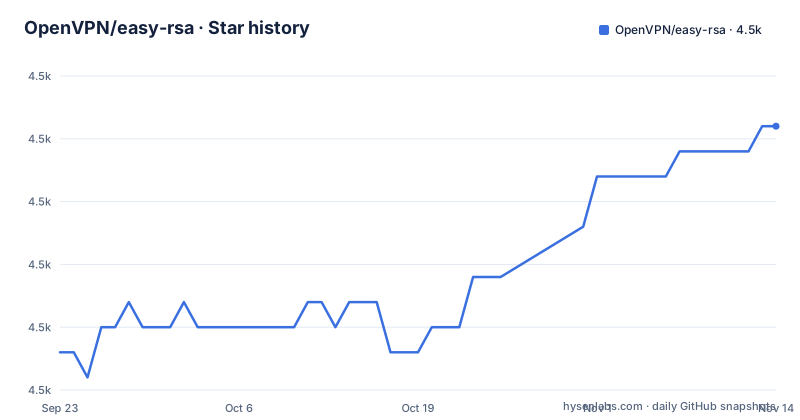
- OpenVPN/easy-rsa4,488 ★ · +9
| Repository | 2026-09-23 | 2026-11-13 |
|---|---|---|
| OpenVPN/easy-rsa | 4.5k | 4.5k |
9 Stars in the last 51 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The first thing the README tells you is that master may be broken
Branch policy takes up more of this README than usage does, and the opening line of that section is unusual.
The master branch is currently tracking development for the 3.x release cycle, and the README says plainly that at any given time master may be broken. You are welcome to file issues against master, but you are asked for patience when using it.
The recommendation is to use a release instead, with the reason given as priority: bugs identified in the most recent release get attention first.
The branch layout is then spelled out as a block:
    master             <- Active: v3.2.x - Rolling.
    v3.<N>.<N>-<LABEL>    Active: Development branches.
    testing               Sandbox: Subject to change without notice.
    v3.1.8                Sunset: Bugfix only for v3.1.7
Four categories in four lines. A rolling trunk, named development branches, a sandbox that changes without notice, and a sunset branch that only receives fixes for one specific older patch.
For a utility that signs certificates, that framing is the correct one. A broken master is a nuisance in a build tool and a different problem entirely in the thing that issues your credentials.
Everything before 3.1 is incompatible with OpenSSL 3
The compatibility cut is the most operationally important line in the README, and it is introduced with a line of its own: the following are not compatible with OpenSSL version 3.
The list that follows is entirely old branches.
    v3.0.6                Inactive: Archived.
    v3.0.5                Inactive: Archived.
    v3.0.4                Inactive: Archived.
    release/3.0           Inactive: Archived.
    release/2.x           Inactive: Archived.
    release/1.x           Inactive: Unmaintained.
So the README marks v3.0.6, v3.0.5, v3.0.4, release/3.0, release/2.x and release/1.x as not compatible with OpenSSL 3. Five branches are archived, and `release/1.x` carries the different label of unmaintained rather than archived.
The prior 2.x and 1.x versions are described as still available as release branches, for tracking and possible back-porting of relevant fixes.
For someone arriving from an older install, that is the whole migration question in one paragraph: the branch you may have been running is archived, the branch you can run may not work with your OpenSSL, and the fix is a version upgrade rather than an OpenSSL downgrade.
The README is an index, and the commands are in two other files
easy-rsa is described in one sentence: a CLI utility to build and manage a PKI CA. In plain terms, that means creating a root certificate authority, and requesting and signing certificates, including intermediate CAs and certificate revocation lists.
Everything else in the README points rather than explains. For 3.x documentation and usage it points to `README.quickstart.md` and to the more detailed documents under `doc/`, and it notes that those files are Markdown, so they can be converted to HTML as desired for release packages or read as-is in plaintext.
That last detail is more than a packaging note. It means the documentation you install alongside the tool is the same Markdown that is in the repository, and it means a distribution that wants HTML documentation generates it rather than maintaining a second copy.
There is also a `CONTRIBUTING.md` equivalent under `doc/`, named `doc/EasyRSA-Contributing.md`, and a `KNOWN_ISSUES` file in the root.
What the README does not contain is any command. There is no `easyrsa` invocation, no example configuration and no walkthrough, which is why anyone searching for how to run it lands on the quickstart file rather than here.
The implementation sits in easyrsa3/ and the tests in shell and batch
The repository root shows where the code and the checking live.
`easyrsa3/` is the implementation directory, and the name carries the major version. `build/` and `distro/` sit beside it, which is the conventional split between building the package and packaging it for a distribution.
The test harnesses are three files with telling names: `op-test.sh`, `wop-test.sh` and `wop-test.bat`. Two are shell scripts and one is a Windows batch file.
There is a `release-keys/` directory, which is where the keys used to sign release artefacts belong, and a `Licensing/` directory alongside `COPYING.md`, which is where the README says licensing information for 3.x lives.
A `ChangeLog` in the root and `doc/` for the documentation complete the layout, with `.github/` holding the workflow whose badge sits at the top of the README.
POSIX is the stated target, and OpenVPN is a neighbour, not a parent
Two pieces of context sit oddly close together in this project, and the README separates them.
The code style section says the project is attempting to adhere to the POSIX standard, linking the published standard. That is a deliberate constraint for a shell utility: no bashisms, no GNU-only behaviour.
The other piece is governance. The README states that Easy-RSA development co-exists with OpenVPN even though they are separate projects. The repository lives under the OpenVPN organisation, and the help section sends usage questions to the openvpn-users mailing list.
Co-exists rather than belongs is the phrase to hold on to. Anyone expecting OpenVPN release cadence, OpenVPN versioning or an OpenVPN support commitment will be disappointed, and anyone filing an issue expecting it to be triaged as an OpenVPN bug should read that sentence first.
The help section also hedges its own advice with the phrase as of this writing, which is a reminder that these pointers change.
Three releases in nine months, all on the 3.2 line
Release activity is regular and recent. v3.2.7 was published on 2026-09-19, v3.2.6 on 2026-03-13 and v3.2.5 on 2025-12-13.
All three sit on the 3.2 patch line, which is consistent with the branch layout that describes master as active for v3.2.x on a rolling basis. So the rolling trunk is the current patch series, and named tags are how you get a fixed point.
The downloads section says release downloads are on the GitHub releases section, and that releases are also available as source checkouts using named tags. Two routes to the same artefact, which matters for environments where a package manager is not an option.
The last push to the repository was on 2026-10-18, about a month after the newest release, so the trunk is being worked on while 3.2.7 is the newest thing you can pin.
The project declares no licence in the repository metadata that a reader can rely on, which is why the README points at `COPYING.md` for licensing information on 3.x instead.
Editorial conclusion
Use easy-rsa when you want to run a certificate authority from a shell in a POSIX environment, and when you can accept a released version rather than the trunk. Do not pick an older line for a new deployment, because the README states that v3.0.4 through v3.0.6 and `release/3.0` are not compatible with OpenSSL 3. Before you script against it, check three things: which release you are installing, since master may be broken at any moment and bugs in the most recent release get priority; whether the version you need supports your OpenSSL, since the README lists the older branches that do not work with OpenSSL 3; and where the commands live, because the README itself is an index pointing to `README.quickstart.md` and the `doc/` directory rather than a tutorial.
Frequently asked questions
what is easy rsa
A command line utility to build and manage a PKI certificate authority. In the README's own terms, it creates a root certificate authority and requests and signs certificates, including intermediate CAs and certificate revocation lists. It is written as a shell utility and aims to adhere to the POSIX standard.
how to install easy rsa
The README does not contain an install command. It points to the GitHub releases section for downloads, noting that releases are also available as source checkouts using named tags, and it directs 3.x documentation and usage to `README.quickstart.md` and the `doc/` directory. The repository root also carries `distro/` for distribution packaging.
how to use easy rsa
Follow `README.quickstart.md` for 3.x usage, with the `doc/` directory holding the more detailed documentation in Markdown. The README itself only describes the scope, which is creating a root CA and signing certificates, intermediate CAs and CRLs. For questions the documentation does not answer, the openvpn-users mailing list is the recommended place to post.
easy rsa vs openssl
The README makes no comparison. What it does state is that v3.0.4, v3.0.5, v3.0.6, `release/3.0`, `release/2.x` and `release/1.x` are not compatible with OpenSSL version 3. easy-rsa also requires OpenSSL in the sense that its certificates come from it, but the utility's own scope is the certificate authority workflow rather than the cryptographic primitives.
easy rsa 2 vs 3
Version 3 is the active line: master tracks the 3.2.x cycle and releases such as v3.2.7 are on that series. Version 2 exists only as the archived `release/2.x` branch, which the README lists as inactive, along with `release/1.x` as inactive and unmaintained. Licensing information for 3.x is in `COPYING.md`.
easy rsa subject alternative name
The README does not cover subject alternative names, and neither the overview nor the branch policy mentions them. The overview lists creating a root CA and signing certificates, intermediate CAs and CRLs, and the detailed documentation is delegated to `README.quickstart.md` and `doc/`, which is where to look for how a particular certificate request is formed.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/openvpn-easy-rsa)Star history chart for your README
[](https://hysenlabs.com/projects/openvpn-easy-rsa)Was this useful?