John the Ripper jumbo: a Unix password auditor that admits its code is rough
John the Ripper jumbo - advanced offline password cracker, which supports hundreds of hash and cipher types, and runs on many operating systems, CPUs, GPUs, and even some FPGAs
At a glance
- What is it?
- The community fork of John the Ripper autodetects several crypt(3) families, cracks more than hashes through bundled *2john tools, and says outright that its quality bar is low. That combination suits a defender auditing their own accounts, and suits almost nobody who needs a result they can certify.
- Who is it for?
- Adopt jumbo if you own the systems and want a fast read on which of your own accounts fall to a wordlist. Do not adopt it as evidence in an audit you have to defend, because the hash implementations are contributed code the project itself describes as not necessarily mature.
- Can I use it commercially?
- Check first. The repository uses a licence we do not classify automatically, so read its LICENSE file before any commercial use.
- Is it still maintained?
- Yes. The repository last received commits 10 days ago.
- What is it written in?
- Mainly C, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 14, 2026, and from our analysis. They are not legal advice.
Star history
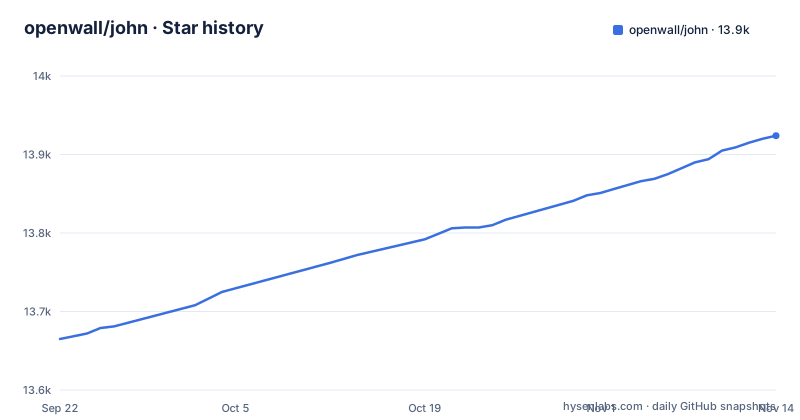
- openwall/john13,924 ★ · +259
| Repository | 2026-09-22 | 2026-11-14 |
|---|---|---|
| openwall/john | 13.7k | 13.9k |
259 Stars in the last 53 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The crypt(3) families it finds before you pass a single option
John the Ripper's stated purpose is narrow: detect weak Unix passwords. Its out-of-the-box value is format detection rather than wordlist quality, because the core build recognises traditional DES-based crypt(3) hashes, bigcrypt, BSDI extended DES-based, the FreeBSD MD5-based scheme also used on Linux and in Cisco IOS, and the OpenBSD Blowfish-based scheme now carried by some Linux distributions and supported by recent Solaris. Kerberos/AFS hashes, Windows LM (DES-based) hashes and DES-based tripcodes ship alongside them. For a system administrator who has just collected shadow file copies from several hosts, that list is the whole first triage: you get the account names to rotate without writing a filter for each Unix flavour. Windows administrators feed the same binary an LM hash dump.
john.pot lives in the home directory, and the home directory depends on your install
Handing the binary a password file is the entire first command, and John walks its cracking modes in the default order until something breaks:
john passwdEvery recovered password goes to the terminal and is appended to $JOHN/john.pot. That path is relative to John's home directory, and which directory it really is depends on how you installed John, so two machines set up by different methods do not share a pot file even when the same binary name sits in $PATH. John reads the pot file on the next run and skips hashes already listed in it, which is what stops a resumed audit from redoing finished work. To pull the stored values back out rather than watch a live session:
john --show passwdExpect the pot file to keep entries from earlier jobs. It maps recovered hashes to passwords and is not scoped to the file you just cracked, so it grows across a whole audit cycle and is worth archiving as a finding rather than deleting between runs.
Wordlist mode, mangling rules, and a compiler that runs your own code
Restricting the run to wordlist mode drops the automatic formats, but the rules option stays available, so you control how candidates get mangled:
john --wordlist=password.lst --rules passwdJohn also carries a built-in compiler supporting a subset of C, which the core documentation presents as the way to define a custom cracking mode when the built-in ones do not fit a target. That is a real capability and also a liability: a mode you write in that compiler is your code executing inside the cracker, so it deserves the same review as anything else you put on an audit host. The official GUI, Johnny, drives the same core, and because it is a separate program you need John installed before it does anything.
A second Ctrl-C discards the session instead of saving it
Interruption handling is where a long run quietly loses time. Pressing any key during a session prints status. q or Ctrl-C ends the run after saving state to $JOHN/john.rec. The edge case is documented: if you press Ctrl-C a second time before John has had a chance to complete handling of the first, it aborts immediately without saving anything. On a slow format, a keypress meant for status followed by an impatient second interrupt throws away everything since the last save. The same file is written every 10 minutes by default so a crash can be recovered from, and continuing an interrupted session takes:
john --restoreOpenMP stays off until you edit the Makefile, and GPUs go unmentioned
CPU parallelism is not on by default. On Linux distributions with glibc 2.7+, John 1.7.6+ autodetects SHA-crypt hashes (the ones recent Fedora and Ubuntu use) and offers optional OpenMP, but enabling it needs GCC 4.2+ and an edit before you compile: you uncomment the proper OMPFLAGS line near the beginning of the Makefile. On recent Solaris, John 1.7.6+ autodetects SHA-crypt and SunMD5 the same way, needing GCC 4.2+ or recent Sun Studio, the same uncommented line, plus the OMP_NUM_THREADS environment variable set at runtime to the thread count you want. Note that OMP_NUM_THREADS appears only in the Solaris passage, so the Linux threading story is thinner than the Solaris one. Pre-compiled distributions may ship alternate executables instead of a single john, with john-omp named as the example for multiple CPUs or cores, so the package you install may not expose threading at all. The larger gap is graphics hardware: the repository description claims runs on many operating systems, CPUs, GPUs and even some FPGAs, yet the core documentation section of the README covers only the OpenMP route, so check the separate documentation files before planning GPU throughput.
A bundled *2john has to flatten the file before John ever sees it
Jumbo stretches past password hashes into files, and the conversion step is where that gets awkward. The added non-hash targets include SSH private keys, S/Key skeykeys files, Kerberos TGTs, macOS .dmg files and sparse bundles, ZIP in both classic PKZIP and WinZip/AES flavours, RAR, 7z, PDF and Microsoft Office documents. For the larger of these you run the corresponding bundled *2john program first and feed its output into JtR-jumbo. John therefore never opens the container itself: something else has to pull the key material or the encrypted payload out first. The consequence for an auditor is that a bad conversion surfaces as a hash set John has nothing to work on, so OPTIONS, which covers command line options and additional utilities, and each tool's own help are where you look. One boundary worth stating plainly: every target listed here is a file you already hold.
The project's own words: quality requirements are low, bugs are expected
Jumbo sets expectations bluntly. It is easy for new code to be added, the quality requirements are low, and only lately have contributions been put through quite some automated testing. The consequence stated in the same paragraph is that you get a lot of functionality that is not necessarily mature, which in turn means bugs in the code are to be expected. That is an unusual concession for a security tool to print in its own README, and it changes how you deploy the thing. The repository does carry test infrastructure, with .ci/, .circleci/, .travis.yml and .pre-commit.sh at the top level, and that is what the automated testing claim rests on. What the wording does not claim is per-format validation. The last push on this repository was on 2026-11-02, so the code moves quickly; whether any one format is correct stays your verification burden, and the honest way to discharge it is to cross-check a recovered hash against a second implementation.
A bleeding branch with no releases here, and a licence field left unasserted
Versioning gives you a branch rather than a release. The default branch is bleeding-jumbo, the repository has no GitHub releases, and the release badge in the README points at a separate repository, openwall/john-packages/releases, which is where pre-compiled distributions come from. An upgrade is therefore either a rebuild from a moving branch or a binary pulled from a sibling repository, and pinning a known-good copy matters more than usual given the quality note above. Some distributions also ship alternate executables instead of just john, john-omp being the named example, so a wrapper script that assumes one binary name can break on upgrade. Contributions go through pull requests on GitHub, and discussion belongs on the john-users mailing list rather than in an issue thread. On licensing, the repository's licence field reads NOASSERTION while both a LICENSE file and doc/LICENSE sit in the tree. Read those two files yourself before redistributing anything you build here; this article gives no legal reading of them.
Editorial conclusion
Adopt jumbo if you own the systems and want a fast read on which of your own accounts fall to a wordlist. Do not adopt it as evidence in an audit you have to defend, because the hash implementations are contributed code the project itself describes as not necessarily mature. Before anything else, read doc/INSTALL for your platform and compile the format you plan to rely on, then cross-check one recovered hash against a second tool.
Frequently asked questions
What are the different modes of John the Ripper?
John combines several cracking modes in one program and tries them in the default order when you give it only a password file, as in john passwd. You can restrict it to wordlist mode while keeping word mangling rules with john --wordlist=password.lst --rules passwd, and you can define a custom mode using the built-in compiler that supports a subset of C. The MODES document in doc/ is where they are described individually.
How do I download John the Ripper on Ubuntu?
The README names many flavors of Unix, macOS, Windows, DOS, BeOS and OpenVMS as supported platforms and then points you at doc/INSTALL for the actual steps. The install document is the thing to read before you build or download anything.
Does John the Ripper use the GPU?
The repository description says it runs on many operating systems, CPUs, GPUs and even some FPGAs. The README's own parallelism section covers only optional CPU OpenMP, enabled at compile time by uncommenting the proper OMPFLAGS line near the beginning of the Makefile, and names no GPU flag or device selection, so check elsewhere before planning around graphics hardware.
Where does John the Ripper store cracked passwords?
Cracked passwords are printed to the terminal and saved in $JOHN/john.pot, where $JOHN is John's home directory and which directory that really is depends on how you installed John. That pot file is also read on the next run so hashes already cracked are not loaded again, and john --show passwd retrieves the stored values.
Can John the Ripper jumbo crack things that are not password hashes?
Yes, jumbo handles non-hash targets such as SSH private keys, S/Key skeykeys files, Kerberos TGTs, macOS .dmg files and sparse bundles, ZIP, RAR and 7z archives, and PDF or Microsoft Office documents. For the larger files a corresponding bundled *2john program runs first and its output is fed into JtR-jumbo.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/openwall-john)Star history chart for your README
[](https://hysenlabs.com/projects/openwall-john)Was this useful?