OpenZiti puts the policy decision on the identity, not the listening port
The parent project for OpenZiti. Here you will find the executables for a fully zero-trust, programmable network @OpenZiti
At a glance
- What is it?
- OpenZiti is a Go overlay network that can make services reachable through identity-based policy without exposing their ports publicly. It suits operators who already run their own infrastructure, and it costs you a controller to keep.
- Who is it for?
- Adopt OpenZiti when you run the infrastructure and need services that are unreachable until an identity is presented, and accept that you now own certificate issuance, policy and controller availability. Do not adopt it as a drop-in VPN replacement for a team that has no capacity to run a control plane, A hosting tunneler can also run as a gateway on another machine if it can reach the destination; secure the network path and configure policy accordingly.
- Can I use it commercially?
- Yes. Apache-2.0 is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 1 day ago.
- What is it written in?
- Mainly Go, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
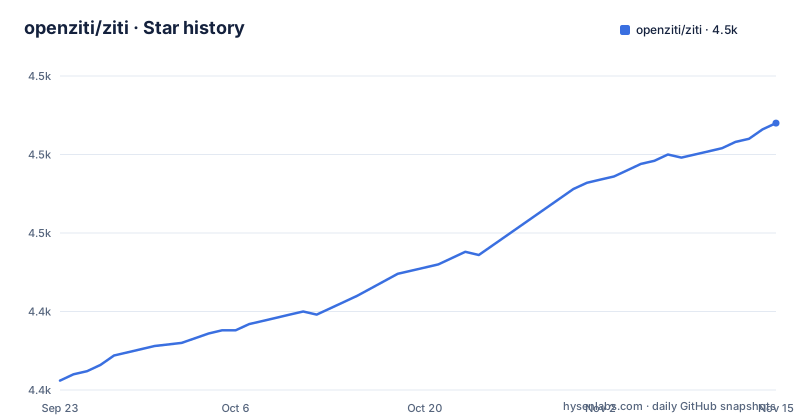
Star history
- openziti/ziti4,485 ★ · +82
| Repository | 2026-09-23 | 2026-11-15 |
|---|---|---|
| openziti/ziti | 4.4k | 4.5k |
82 Stars in the last 53 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The controller decides reachability, not the firewall
OpenZiti takes the listening port out of the exposure calculation. OpenZiti can expose a service through identity-based policy without a publicly reachable application port. Whether the underlying application port is still reachable depends on its bind address, network topology and firewall rules; the overlay alone does not hide an independently exposed port.
That reframes who installs it. The operators who benefit already own their infrastructure and want internal applications to stop being reachable from everywhere. The home lab case is spelled out in the README: Nextcloud, Home Assistant, media servers and development environments reachable from anywhere without opening a router port, without dynamic DNS and without a third-party tunnel service. The same mechanism is sold for the opposite reason in a data centre, where an internal API has to disappear from the internet.
Machines hold identities the same way users do, so sensor to gateway traffic goes through the same policy path. Whether that earns its keep depends on your certificate and policy operations, which is where the real work sits.
A connection starts at the router, not at the service
Traffic never begins at the service. A client tunneler intercepts the connection attempt, an edge router carries it across the overlay fabric, and a second tunneler on the service host opens the connection to localhost. The service keeps its ordinary socket and nothing else can reach it.
Both ends hold keys. Data is encrypted from source to destination using libsodium, with mTLS for authentication and no trust placed in the network path between them. Identity is cryptographic, not a network location, and a policy decides whether a given identity may reach a given service.
The router is the load bearing component: a mesh fabric with path selection for performance and reliability. This repository is the parent project that carries the executables, split across directories you can see at the root, controller/ for the control plane, router/ for the fabric, tunnel/ for the intercepting clients and setup-cli/ for the setup tooling.
Network, host or application access moves the trust boundary
The three deployment models differ in one thing only: where the trust boundary stops.
Network access places an OpenZiti edge router in a trusted zone. Clients are authenticated as they enter, and the router exits into the private network where services live. Nothing runs on the service host and no code changes, which makes it the cheapest model and the one most like a gateway.
Host access runs a tunneler beside the service. The tunneler handles identity, authentication and encryption, and the service is told to accept connections from localhost only. Still no code changes, but the trust boundary drops from the network to the host operating system.
Application access embeds an SDK so the application itself holds the identity and encrypts in process. No listening ports exist at all, not even on localhost, and the README calls this the strongest model since identity sits at the application layer rather than the host. It is also the only model that needs code changes, and the only one where a language without an SDK rules the service out entirely.
The module path and the pinned logger are the build facts
The repository is Go, and go.mod states the toolchain and one deliberate override:
module github.com/openziti/ziti/v2

go 1.27.1

// pinned
replace github.com/michaelquigley/pfxlog => github.com/michaelquigley/pfxlog v0.6.10
The module path carries the /v2 suffix, which is what a Go import path does past a second major version. The replace directive pins the logging library regardless of what a consumer would resolve, so a build from this tree logs in the format the project expects.
For a first run, the starting point in the repository is the quickstart/ directory, which holds local/, docker/, kubernetes/ and test/ subdirectories plus aws.md for the cloud case. Read quickstart/README.md for the sequence, and remember the README's host access setup is to install a tunneler and enroll an identity.
Revocation closes a live connection rather than waiting it out
Most access control changes take effect on the next login. OpenZiti's policy model does not wait. Access is described as fine grained and identity based, and revocation happens in real time by closing active connections, not by letting them run until a timeout.
Operations shift with it. Networks are managed through identities and policies instead of IP addresses and firewall rules, and the project ships a full management REST API plus a web admin console, which is where automation belongs if you have more than a handful of services. Be aware what you give up: address based thinking is gone, so any existing tooling that reasons about IP ranges has to be rewritten against identities.
go.mod declares /v2 while two v1 lines move alongside it
Releases v2.0.7, v2.0.8 and v1.6.22 were published on 2026-09-25, 2026-10-08 and 2026-10-19, and the last push to this repository was on 2026-11-02. A v1 line and a v2 line were moving within weeks of each other.
The repository root carries RELEASE_POLICY.md and lts-versions.json, which is where that answer lives, but a reader who takes the newest tag by default will land on v2 while an LTS installation stays behind.
Licensing is Apache 2.0, and the project was created and sponsored by NetFoundry, so redistribution inside a product carries the usual attribution obligations and nothing more.
Revocation stops working when the controller is out of reach
The real time revocation claim has an unstated dependency: a policy decision needs the control plane that evaluates it. Check the project documentation for controller availability and for what happens to an existing session when the controller becomes unreachable.
The dark service model has a second cost in the same place. When something fails, you have no listening port to curl, no banner to identify and often no obvious host level symptom, because the service is listening normally and the tunnel in front of it is the thing that is broken. Teams migrating from a VPN usually need new runbooks, not adjusted ones.
There is a third case where this is the wrong tool. The strongest model, application access, requires an SDK in the application itself, and a service with no SDK for its language has no route through it. A hosting tunneler can instead run on a gateway that has network access to the service, though that leaves the gateway-to-service path to secure.
Where OpenZiti and NetBird part company
NetBird builds the same user goal, internal reachability without exposing ports, on a different foundation. It coordinates a WireGuard mesh from a management server that hands peers keys and addresses, and the security property rests on the tunnel and the peer configuration rather than on the application being unreachable by design.
The difference shows up at the service. In a WireGuard mesh the service host has an interface and an address, so it is reachable by anything that gets onto that interface. In OpenZiti the service has no port at all in application access, and in host access only a tunneler stands between it and the network, so identity is enforced at the service boundary rather than at the network boundary.
That also changes the cost curve. A mesh is easier to explain to a network team and fits existing WireGuard knowledge. OpenZiti costs more to run, because identities, enrollment and policy are yours to operate, and buys you a service that scanners cannot see at all. A team whose requirement is remote user access to a handful of networks pays for OpenZiti and gets a control plane it does not need. A team whose requirement is that an internal API does not exist on the wire gets the same from OpenZiti alone.
Editorial conclusion
Adopt OpenZiti when you run the infrastructure and need services that are unreachable until an identity is presented, and accept that you now own certificate issuance, policy and controller availability. Do not adopt it as a drop-in VPN replacement for a team that has no capacity to run a control plane, A hosting tunneler can also run as a gateway on another machine if it can reach the destination; secure the network path and configure policy accordingly. Before anything else, read RELEASE_POLICY.md and lts-versions.json at the repository root and confirm which of the concurrently released v1.6 and v2.0 lines your build actually tracks.
Frequently asked questions
How does OpenZiti work?
A client tunneler intercepts the connection, an edge router carries it across the overlay, and a tunneler on the service host opens the connection to localhost. Data is encrypted from source to destination using libsodium, and mTLS authenticates both ends against a policy the controller evaluates.
Does OpenZiti require an open port on my server?
No. Services published on an OpenZiti network have zero listening ports, and tunnelers dial out to the overlay rather than accepting inbound connections. With application access there are no listening ports at all, not even on localhost.
What are the three OpenZiti deployment models?
Network access, where an edge router sits at the trust boundary with nothing on the service host; host access, where a tunneler runs beside the service and the service accepts localhost only; and application access, where an SDK is embedded so the application holds the identity and encrypts in process.
Which OpenZiti release line should I pin to?
The repository's recent releases are v2.0.7, v2.0.8 and v1.6.22, so the newest tag is not the only choice. The root of the repository carries RELEASE_POLICY.md and lts-versions.json.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/openziti-ziti)Star history chart for your README
[](https://hysenlabs.com/projects/openziti-ziti)Was this useful?