Hurl makes the .hurl file the test, and ships a formatter for it
Hurl, run and test HTTP requests with plain text.
At a glance
- What is it?
- Hurl is a Rust command line tool that runs and tests HTTP requests written in a plain text format, with a libcurl engine underneath, XPath and JSONPath predicates, request chaining with captured values, and JUnit, TAP, HTML or text reports for CI. The project documents prebuilt packages, package managers and source builds for multiple platforms.
- Who is it for?
- Hurl fits a team that wants HTTP checks living in version control as readable text, that needs a multi-step session with a captured token in one artefact, and that has to hand a machine-readable result to a CI system, since JUnit, TAP, HTML and text reports are all built in. It does not fit a payload shape the text grammar cannot express without dropping to raw curl options.
- Can I use it commercially?
- Yes. Apache-2.0 is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository received new commits within the last day.
- What is it written in?
- Mainly Rust, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
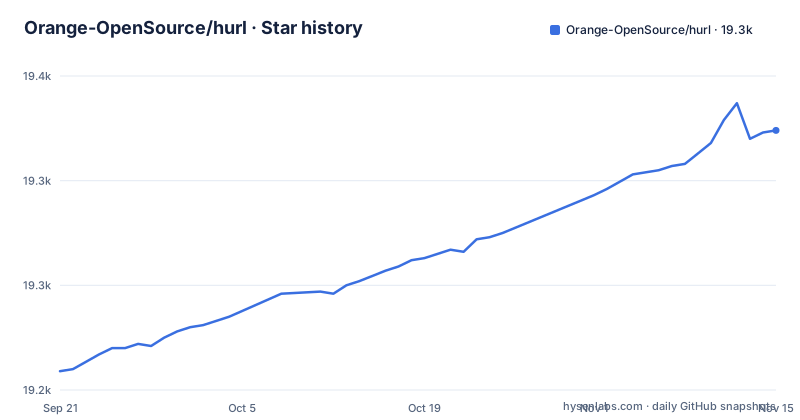
- Orange-OpenSource/hurl19,324 ★ · +115
| Repository | 2026-09-21 | 2026-11-15 |
|---|---|---|
| Orange-OpenSource/hurl | 19.2k | 19.3k |
115 Stars in the last 55 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
A file is a request, a status, and then optional sections
The grammar is small enough to read in one screen. A request line with its method and URL, then the expected HTTP status, then any number of sections. The login example is the shortest complete one:
# Go home and capture token
GET https://example.org
HTTP 200
[Captures]
csrf_token: xpath "string(//meta[@name='_csrf_token']/@content)"

# Do login!
POST https://example.org/login
[Form]
user: toto
password: 1234
token: {{csrf_token}}
HTTP 302
Three section names do most of the work. `[Form]` sets a urlencoded body from key and value pairs, `[Captures]` names a value extracted from the response, and `[Asserts]` holds the predicates. A body can be written inline as JSON or XML, or wrapped in a fenced block of its own language, which is how the GraphQL example embeds a graphql block inside a hurl file and the SOAP example embeds an XML envelope.
The consequence of that design is that a test and its fixture are the same file. There is no separate assertion file to keep in step, and adding a request to a file adds a test to the run, which is why the format suits a repository where the API checks live next to the client code.
Captured values become template variables, so a session is one file
The `[Captures]` entry above is the mechanism that makes multi-step flows work. The name on the left, `csrf_token`, and the query on the right, an XPath expression reading a meta tag's content attribute, define a value. Later, `{{csrf_token}}` substitutes it, and in that example it goes into the form body of the next request.
Chaining without values is just consecutive request lines, and the README shows it as a health check followed by three numbered steps. With values, the file becomes a session: fetch a token, authenticate, then use the authenticated result.
The samples list names the other things you can do inside a request, and they cluster around moving data: passing data between requests, posting a JSON body, templating a JSON body, templating an XML body, using dynamic values, and capturing and using a CSRF token as its own entry. That is the vocabulary for a file that has to reproduce a real login rather than a single call, and it is the reason Hurl is used for both fetching data and testing sessions rather than only for the second.
The predicate set is XPath, JSONPath, headers, duration and hashes
Assertions are written as query plus operator plus expected value, and the JSON example packs four of them under one response:
[Asserts]
header "X-Frame-Options" == "SAMEORIGIN"
jsonpath "$.status" == "RUNNING"    # Check the status code
jsonpath "$.tests" count == 25      # Check the number of items
jsonpath "$.id" matches /\d{4}/     # Check the format of the id
Note the operators differ in kind, not just in name. `==` is an exact comparison, `count ==` asserts on cardinality, and `matches` takes a regular expression, so a format check does not need a value to compare against. For HTML the query language is XPath instead, with `xpath "normalize-space(//head/title)" == "Hello world!"`, where the normalisation is what makes a whitespace-padded title comparable.
Two predicates reach outside the body. A performance check is a duration assertion, `duration < 1000` in milliseconds, so latency becomes part of the test rather than a separate benchmark. A content check is a digest, `sha256 == hex,039058c6f2c0cb492c533b0a4d14ef77cc0f78abccced5287d84a1a2011cfb81;`, which pins a downloaded artefact exactly. The status line itself is the other assertion, which is why every example ends with `HTTP 200` or `HTTP 302`.
Four report formats, and the samples list covers what a request can do
The integration story is one sentence in the README: Hurl is easy to integrate in CI/CD, with text, JUnit, TAP and HTML reports. The samples index adds a JSON report and a JSON output entry, so there is a machine-readable stream as well as a per-test report.
That set is chosen for whoever consumes it. JUnit is what most Java and PHP CI dashboards ingest, TAP is line oriented for shell pipelines, HTML is for a human reviewing a build, and the JSON report is for something you post-process yourself. Choosing a report is the integration decision; the test file does not change.
The samples index is also the honest coverage list, and it is long: HTTP version, IP address, polling and retry, delaying requests, skipping requests, testing the endpoint performance, using SOAP APIs, capturing and using a CSRF token, redacting secrets, checking a byte order mark in a response body, AWS Signature Version 4 requests, and using curl options. Two of those deserve a second look. Redacting secrets is a documented feature because these files hold credentials by design, and using curl options is the escape hatch for anything the text grammar does not cover.
The workspace publishes a runner, a formatter and a library
The Cargo manifest is a workspace with three members:
[workspace]
members = [
    "packages/hurl",
    "packages/hurlfmt",
    "packages/hurl_core",
]
resolver = "2"
So the distribution is not a single program. `packages/hurl` is the command line tool, `packages/hurlfmt` is a formatter for the `.hurl` format itself, and `packages/hurl_core` is the engine as a library crate. The formatter is the one that changes how a team works, because a format that a tool can rewrite is a format you can enforce in a pre-commit hook or a CI job.
The top level backs this up with `completions/` for shell completion and `bin/` alongside it, and the crate is published to crates.io as `hurl`.
One entry in the root listing does not fit the picture. Alongside `rustfmt.toml` there is `ruff.toml`, a Python linter's configuration file, in a repository whose workspace members are all Rust. Source does not say what `ruff.toml` is used for.
The release profile strips symbols and aborts on panic
The release profile is tuned, and the four settings each have a cost:
[profile.release]
lto = true          # Enable Link Time Optimization
codegen-units = 1   # Reduce number of codegen units to increase optimizations.
panic = "abort"     # Abort on panic
strip = true        # Automatically strip symbols from the binary.
Link time optimisation and a single codegen unit make for a smaller and faster binary at the cost of a slow build. `strip = true` strips symbols, which can make crash backtraces harder to interpret on platforms that rely on them. A debug build or separate symbols may be needed for diagnosis.
`panic = "abort"` is the setting with consequences beyond the binary. Code built with an aborting panic strategy cannot be caught with `catch_unwind`, so a panic in the released binary ends the process. The lint configuration is strict by comparison: rust warnings are denied workspace wide, and four clippy lints are denied, including wildcard imports.
Semver checking is patched to treat a new enum variant as allowed
There is a comment in the manifest, `# Patch cargo-semver`, and then a metadata block that relaxes three semver checks, two of which are:
[workspace.metadata.cargo-semver-checks.lints]
enum_variant_added = { level = "allow" }
enum_no_repr_variant_discriminant_changed = { level = "allow" }
These checks would otherwise flag a breaking change. Adding a variant to a public enum is a breaking change for any downstream crate that matches on it exhaustively, and the usual advice is to treat an enum as a closed set. This workspace has decided that none of them is a break worth failing a release over.
For a maintainer that is a reasonable trade, because it means a new option can be added to a library without a major version bump. For a consumer of `hurl_core` it is worth knowing, because your match expression has to tolerate variants that did not exist when you wrote it, and the library's own policy is not going to warn you when one appears.
The engine is libcurl, and export curl commands is the way out
The architecture is stated plainly: Hurl is a lightweight binary written in Rust, and under the hood the Hurl HTTP engine is powered by libcurl. With its text file format, Hurl adds syntactic sugar to run and test HTTP requests over that engine, and the README keeps the emphasis on curl being fast, efficient and ready for IPv6 and HTTP/3.
Two things follow. The protocol capabilities you get are the ones your libcurl build has, so HTTP/3 and any TLS feature depend on how the library underneath was compiled, not on a flag in the Hurl manifest. And the layering is the difference from a general purpose client: Hurl does not replace curl so much as add assertions, chaining and captures to it, keeping curl's behaviour underneath.
The samples index makes the boundary explicit with a section on using curl options, and a debug section whose most useful entry is exporting curl commands. That is the migration path in both directions. When a check is easier in shell, export the curl command line and work there; when a shell script has grown request dependencies, express it as a `.hurl` file and let the captures and asserts carry the logic.
Editorial conclusion
Hurl fits a team that wants HTTP checks living in version control as readable text, that needs a multi-step session with a captured token in one artefact, and that has to hand a machine-readable result to a CI system, since JUnit, TAP, HTML and text reports are all built in. It does not fit a payload shape the text grammar cannot express without dropping to raw curl options. Stripped symbols can make crash backtraces harder to interpret; a debug build or separate symbols may be needed. Before adopting, check two things: the `enum_variant_added = allow` semver patch if you depend on `hurl_core`, and the sample list for redacting secrets, because these files hold tokens and the redaction feature exists for exactly that reason.
Frequently asked questions
What is Hurl, and what does it replace?
Hurl is a command line tool written in Rust that runs and tests HTTP requests defined in a simple plain text format, so a request sequence, its expected status and its assertions live in one file. The HTTP engine underneath is libcurl, and Hurl is published on crates.io as the hurl crate.
How do I install Hurl?
On macOS, run `brew install hurl`; Rust users can run `cargo install --locked hurl`. The installation guide lists additional packages and binaries for Linux, Windows and other platforms. Windows requires the Visual C++ Redistributable.
Does Hurl have a formatter for its own file format?
Yes. The Cargo workspace has three members, packages/hurl, packages/hurlfmt and packages/hurl_core, so a formatter for .hurl files and a reusable core library are published alongside the command line tool. The repository root also carries rustfmt.toml for the Rust sources.
Can Hurl replace curl or a GUI API client in CI?
Hurl is built on libcurl and describes itself as syntactic sugar over it, and its samples include an Export curl Commands debug tip and a Using curl Options section. For CI it produces text, JUnit, TAP and HTML reports plus a JSON report, which is the part that differs from a GUI client.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/orange-opensource-hurl)Star history chart for your README
[](https://hysenlabs.com/projects/orange-opensource-hurl)Was this useful?