binsider reads one ELF binary five ways inside a single TUI
Analyze ELF binaries like a boss 😼🕵️♂️
At a glance
- What is it?
- binsider folds general file information, ELF layout, string extraction, syscall tracing and a hexdump into one Rust terminal interface. A close reading of the manifest shows what the quickstart leaves out: the tracer is a default feature, the published crate ships a slice of the tree, and the container image runs the analyzer as an unprivileged user.
- Who is it for?
- binsider is a good fit when an unfamiliar Linux ELF file needs a layout read, a string sweep and a syscall trace in one sitting, and a poor fit the moment the target is not ELF, since the manifest pulls elf 0.8.0 and names no other format.
- Can I use it commercially?
- Yes. Apache-2.0 is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 7 days ago.
- What is it written in?
- Mainly Rust, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 21, 2026, and from our analysis. They are not legal advice.
Star history
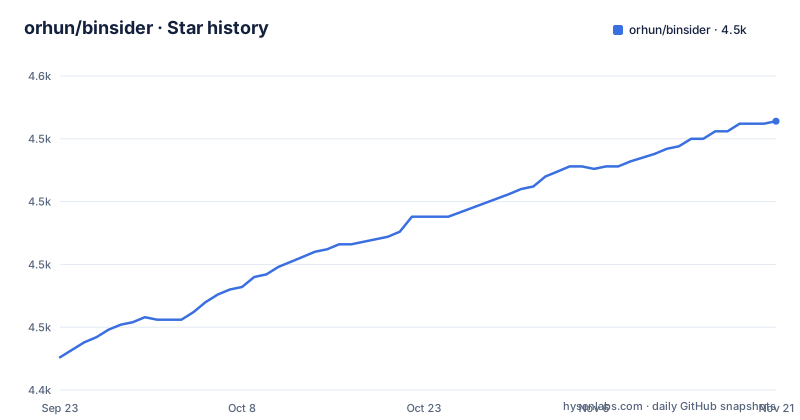
- orhun/binsider4,532 ★ · +94
| Repository | 2026-09-23 | 2026-11-21 |
|---|---|---|
| orhun/binsider | 4.4k | 4.5k |
94 Stars in the last 59 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Five analysis views behind one terminal interface
Binsider takes a bare positional argument and hands the file to five views. General analysis reports file size, ownership, permissions, date and linked shared libraries, which the project sets against `stat(1)` and `ldd(1)`. Static analysis walks the ELF layout, its sections, segments, symbols and relocations. Dynamic analysis executes the binary and traces system calls, signals and the program's execution flow, set against `strace(1)` and `ltrace(1)`. String extraction pulls printable text out of the file the way `strings(1)` does, aimed at URLs, passwords and other sensitive information, and a hexdump view puts raw bytes beside a dashboard. All of it lives in one terminal interface, so moving from a symbol table to a byte offset costs no second process. Each of the five views has its own page on the project site, at /usage/general-analysis, /usage/static-analysis, /usage/dynamic-analysis, /usage/strings and /usage/hexdump, which is where the detail behind this short list lives.
binsider <binary>That last point carries a habit cost. The README does not document a non-interactive mode, and the single invocation it shows is the interactive one.
The default build wires in the tracer
Installing means one command, `cargo install binsider`, and that command takes the crate's default feature set with it. The feature table in Cargo.toml is short. `dynamic-analysis` is listed as default and wires to one optional dependency, `lurk-cli`, pinned at 0.3.14.
[features]
default = ["dynamic-analysis"]
dynamic-analysis = ["lurk-cli"]
No other feature key exists in that file, so a stock install compiles the tracing path whether or not you ever open that view. A lighter build means asking for the absence of default features at build time, and the README does not document that switch. Its installation note points only to a page listing other installation methods. Because the tool is compiled rather than downloaded, the toolchain sitting on your machine also decides which build of the analyzer you end up running against a sample.
System call tracing rests on ptrace and signal handling
The `dynamic-analysis` feature pulls in lurk-cli 0.3.14, and the dependency list also enables the `ptrace` and `signal` features of nix 0.30.1. Other entries appear to map to visible jobs: elf 0.8.0 parses the static layout, rust-strings 0.6.0 extracts strings, lddtree 0.4.0 builds the shared library listing, sysinfo 0.38.0 arrives with only its user feature for ownership and permissions, bytesize 2.3.0 formats file size, chrono 0.4.43 stamps the date, and which 8.0.0 resolves programs on disk. Ratatui 0.30.0 and tui-input 0.15.0 draw the interface, while tui-popup 0.7.2, ansi-to-tui 8.0.1 and tui-big-text 0.8.1 handle overlays, colour and headings. Two entries do not map to a named feature, webbrowser 1.0.6 and termbg 0.6.2, and nothing in the README says which view reaches for them.
The published crate carries a fraction of the tree
A crate install is assembled from a fixed path list rather than from the whole repository. The `include` field in Cargo.toml names five patterns, beginning with `src/**/*` and `Cargo.*`, and the published package stops there:
include = [
  "src/**/*",
  "Cargo.*",
  "LICENSE*",
  "README.md",
  "CHANGELOG.md",
]
The tree itself is wider, and these top-level entries never reach the registry:
ARCHITECTURE.md
SECURITY.md
deny.toml
committed.toml
flake.nix
Dockerfile
examples/demo.rs
Contributor tooling sits in the same layer: rustfmt.toml, typos.toml, codecov.yml, cliff.toml, committed.toml, a tests directory backed by the dev-dependency pretty_assertions 1.4.1, and flake.nix beside flake.lock for a Nix-based build.
So a reader who wants the design rationale or the vulnerability contact has to reach the repository rather than the cargo cache. The last push to the main branch landed on 2026-11-01.
The container image drops to an unprivileged user
Docker packaging exists, and the Dockerfile shows its shape. The build stage starts from rust:1.88-slim-bullseye, which matches the `rust-version` of 1.88.0 declared in Cargo.toml. It warms the dependency cache with a stub source file, deletes the stub artifact, copies the tree, then repeats the build locked to Cargo.lock:
FROM rust:1.88-slim-bullseye AS builder
COPY Cargo.toml Cargo.toml
RUN cargo build --release
RUN rm -f target/release/deps/binsider*
RUN cargo build --locked --release
The runtime stage is a slim Debian image holding one file:
FROM debian:bullseye-slim AS runner
WORKDIR /app
COPY --from=builder /src/build-out/binsider .
USER 1000:1000
ENTRYPOINT ["./binsider"]
Nothing in that file adds capabilities or mounts the host filesystem, so the traced program runs inside as an ordinary user. That is the part to think about before pointing this image at a file you would not otherwise execute: the dynamic view runs the sample on purpose, and `USER 1000:1000` is the only boundary the image sets.
One profile strips symbols while another aborts on panic
Cargo.toml splits development and distribution across four profiles. The dev profile sets `opt-level = 0`, keeps `debug = true` and sets `panic = "abort"`, while test stays unoptimised with debug information on and bench uses opt-level 3 without debug information. The shipped profile pushes optimisation to 3, drops debug information, restores unwinding panics, and adds shrink work:
[profile.release]
opt-level = 3
debug = false
panic = "unwind"
lto = true
codegen-units = 1
strip = true
Two things follow for anyone running the tool on a stranger's executable. A distributed build of binsider itself carries no symbols, so a crash inside the analyzer offers less to work with than a local build does. And because panic mode differs between profiles, a failure that aborts in development unwinds in the copy you install. better-panic 0.3.0 sits in the dependency list, and the README does not describe how that output is rendered.
Apache-2.0 on GitHub, a dual choice in the manifest
Three places state reuse terms, and they do not agree. The licence field on GitHub reads Apache-2.0, while Cargo.toml declares `MIT OR Apache-2.0` and the README closes with Apache License Version 2.0 or The MIT License at your option, so the manifest and the README match each other and the repository field does not. Code that vendors the crate can pick either, and a reader who checks the sidebar alone misses the second option.
Other metadata in the same file describes an application rather than a library. Categories list command-line-utilities, the keywords are analyze, binary, tui and elf, and the only invocation the quickstart shows takes a file path. The README presents it as an application: you install the binary, point it at a file, and read the result in a terminal pane, though it also links a docs.rs page and the repository has examples/demo.rs.
Editorial conclusion
binsider is a good fit when an unfamiliar Linux ELF file needs a layout read, a string sweep and a syscall trace in one sitting, and a poor fit the moment the target is not ELF, since the manifest pulls elf 0.8.0 and names no other format. Read ARCHITECTURE.md before trusting the trace view, and keep in mind that dynamic analysis executes the very file you are inspecting, that the tracer ships as a default feature, and that the published crate leaves the architecture notes behind. Five views in one pane is the whole scope of the tool.
Frequently asked questions
What does binsider do that stat, ldd and strings do not separately?
It puts five views in one terminal interface: general file information, ELF layout, syscall tracing, string extraction and a hexdump. Its dynamic analysis executes the binary and traces system calls, signals and execution flow the way strace(1) and ltrace(1) do.
Why does installing binsider with cargo also build a tracer?
Cargo.toml sets dynamic-analysis as a default feature and wires it to the optional lurk-cli dependency at 0.3.14. An install that does not opt out of default features therefore compiles the tracing code path.
Does binsider read Windows PE or macOS Mach-O binaries?
The manifest depends on elf 0.8.0 for the layout view, and the README describes ELF binaries throughout. Neither the README nor the top-level tree names PE or Mach-O support.
Which licence covers binsider?
Cargo.toml declares MIT OR Apache-2.0 and the README offers either licence at your option, while the repository licence field on GitHub shows Apache-2.0 alone. The manifest and the README agree with each other.
What does building binsider require?
Cargo.toml sets rust-version to 1.88.0 with edition 2021. The Dockerfile builds on rust:1.88-slim-bullseye and ships a debian:bullseye-slim runtime image that runs the binary as USER 1000:1000.
Can I use binsider as a Rust library?
Cargo.toml classifies the package under command-line-utilities, although the README links a docs.rs page and the repository has an examples/demo.rs file. The quickstart shows cargo install binsider followed by a file argument, which is an application workflow rather than an import.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/orhun-binsider)Star history chart for your README
[](https://hysenlabs.com/projects/orhun-binsider)Was this useful?