Ory Hydra ships no user management, and its tests want three databases
Internet-scale OpenID Certified™ OpenID Connect and OAuth2.1 provider that integrates with your user management through headless APIs. Solve OIDC/OAuth2 user cases over night. Consume as a service on Ory Network or self-host. Trusted by OpenAI and many others for scale and security. Written in Go.
At a glance
- What is it?
- Ory Hydra is a Go implementation of the OAuth 2.0 authorization framework and OpenID Connect Core 1.0 that is deliberately incomplete on purpose: it has no user management, and it reaches your existing identity provider through a login and consent application that you build and host yourself. The implementation details that decide whether you can adopt it are the certified profile list obtained against version 1.0.0, a test target that needs MySQL, Postgres and CockroachDB in Docker, and a build whose toolchain is downloaded by piping remote scripts into a shell.
- Who is it for?
- Ory Hydra fits teams that already have an identity provider and want protocol work, token lifecycle and client management handled by a dedicated Go service while keeping the login and consent interface entirely their own. It does not fit a team hoping to get user accounts, registration or password handling from the same box, because that is explicitly out of scope and you supply the login and consent app it redirects to.
- Can I use it commercially?
- Yes. Apache-2.0 is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 108 days ago.
- What is it written in?
- Mainly Go, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 12, 2026, and from our analysis. They are not legal advice.
Star history
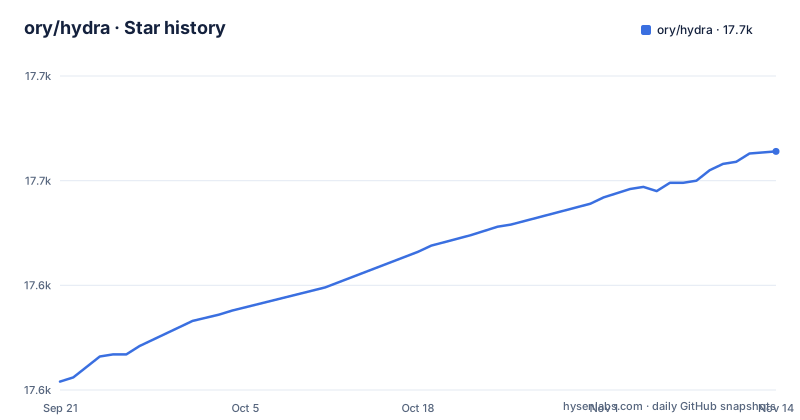
- ory/hydra17,663 ★ · +109
| Repository | 2026-09-21 | 2026-11-12 |
|---|---|---|
| ory/hydra | 17.6k | 17.7k |
109 Stars in the last 52 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
There is no user management, and the login and consent app is yours to build
This is the decision that shapes everything else about the project. Ory Hydra is described as a standalone OAuth 2.0 and OpenID Connect server without user management, and the reason it works that way is that it connects to an existing identity provider through a login and consent app, which is what gives you absolute control over the user interface and the experience flows. The authentication endpoint is explicitly pluggable: it works with Ory Kratos, with authboss, with User Frosting, or with your proprietary system. So the component list to budget for is a login and consent app you host, plus the Hydra service that orchestrates it. Adopting it means accepting that the user facing part of the flow is your code, your templates and your accessibility work, with the OAuth 2.0 and OpenID Connect mechanics handed to you.
The OpenID certificate was obtained against v1.0.0, not a current tag
The certification section is specific about what is certified, and the profiles are worth reading as a flow checklist. Certified are the Basic OpenID Provider with the code response type, the Implicit provider with id_token and id_token+token, the Hybrid provider with code+id_token, code+id_token+token and code+token, publishing configuration information for discovery, and the Dynamic OpenID Provider for dynamic client registration. The sentence that follows is the one that matters for a version decision: to obtain certification, the reference user login and consent app was deployed unmodified, together with Ory Hydra v1.0.0. The recent tags are v26.2.0 from 2026-03-20, v25.4.0 from 2025-11-07 and v2.3.0 from 2025-01-17, and the branch was last pushed on 2026-07-29. So the certified artifact is a much older release than the current line, and what the certificate actually tells you is which response types and which registration modes were verified, not that the version you deploy carries the same verification.
The standards list covers the token lifecycle, and stops there
The protocol coverage is presented as a list of the documents the implementation follows, and the list is the specification of what you can rely on. On the IETF side that is the core authorization framework, the threat model and security considerations, token revocation, token introspection, the native apps draft, dynamic client registration and its management protocol, proof key for code exchange for public clients, and the JWT profile for client authentication and authorization grants. On the OpenID Foundation side it is Core 1.0, Discovery 1.0, Dynamic Client Registration 1.0, and both logout profiles, front channel and back channel. Revocation, introspection and PKCE being named explicitly means the operations that usually get bolted on later are in the design.
The Go test target spins up three database engines in Docker
Reading the test target tells you what running the suite actually costs. It first resets the databases, then runs the Go tests, then removes the containers it created.
source scripts/test-env.sh && go test -failfast -timeout=20m ./...The reset step launches three engines by hand, MySQL and Postgres are both pinned to a host port and started detached, and a third is created for CockroachDB.
docker run --rm --name hydra_test_database_mysql  -p 3444:3306 -e MYSQL_ROOT_PASSWORD=secret -d mysql:8.0
docker run --rm --name hydra_test_database_postgres -p 3445:5432 -e POSTGRES_PASSWORD=secret -e POSTGRES_DB=postgres -d postgres:16
Two consequences follow. You need a working Docker daemon to run the suite at all, and the -failfast flag means the first failure ends the run, so a single environment problem hides every test after it. The end to end side is a Node project pinned in the root manifest, with the test script running Cypress in headless mode, a watch mode that opens the runner, and the OpenAPI generator CLI as its one runtime dependency.
The build puts curl piped into a shell in front of lint and docs
The Makefile prepends a local .bin directory to the path and then fetches its tools into it, so a first build reaches the network for its own tooling. The linter is not installed by a package manager, it is produced by piping the golangci-lint install script from GitHub into sh with a version argument of 2.10.1, and the lint target is that binary run over everything. The Ory CLI is fetched the same way from the ory/meta install script at version 0.2.2, and a licenses helper is pulled from the ory/ci repository with retries on both the connection and the request. The command documentation is generated locally, with clidoc compiled from the cmd directory and then run to write into the docs directory. Node dependencies come from npm ci keyed on the lockfile. The consequence is that make lint, the CLI and the generated command docs all depend on remote scripts executing successfully, so an air gapped or partially mirrored build environment has to pre-seed .bin.
Two dependencies are replaced by directories inside the tree, and Go 1.26 is the floor
The module declaration tells you two things about the source layout. The import path is versioned as github.com/ory/hydra/v2 while the release tags are calendar shaped, which is why a checkout can report a v2 module path and a 26 series tag at the same time. More usefully, there are two replace directives: the generated Hydra client is redirected to the internal/httpclient directory, and github.com/ory/x is redirected to a local oryx directory, with that dependency required at a zero pseudo version that only the local copy can satisfy. The consequence is that a build from a checkout uses the in-tree copies rather than registry versions, and the generated HTTP client is not a separate module you can pin or upgrade on its own. The go directive reads 1.26, so anyone building from source needs a current toolchain rather than whatever their distribution ships.
Persistence, keys and hardware modules sit beside the release and security plumbing
The top level layout shows how much of the operational surface is in this repository rather than in a wrapper. Persistence and configuration live under persistence and driver, encrypted storage under aead, key handling under jwk, and there is a dedicated hsm directory, matched by PKCS 11 libraries in the module requirements from two different providers. Alongside them sit consent and flow packages, an oauth2 directory, a client package, health checks, a fosite directory with a fositex sibling, and an internal directory that holds the generated client. The surrounding files are the release and safety plumbing: a goreleaser configuration, a schema directory, a grype configuration, nancy and reference ignore files, an openapi generator manifest, and a security policy with an upgrade document, a change log and a development guide. The consequence for an adopter is that operational concerns, from migrations to key rotation to HSM attachment, are things you configure in this service rather than delegate to a platform, unless you take the managed offering on the Ory Network instead.
Editorial conclusion
Ory Hydra fits teams that already have an identity provider and want protocol work, token lifecycle and client management handled by a dedicated Go service while keeping the login and consent interface entirely their own. It does not fit a team hoping to get user accounts, registration or password handling from the same box, because that is explicitly out of scope and you supply the login and consent app it redirects to. Before committing, confirm your flow type appears in the certified profile list, remember that the certificate was obtained against version 1.0.0 rather than a current tag, budget for running a login and consent app in production, and if you plan to contribute, expect Go 1.26, a Docker based test suite across three database engines, and a linter that is fetched with curl the first time you run it.
Frequently asked questions
What is Ory Hydra?
It is a hardened OAuth 2.0 server and OpenID Connect provider written in Go and licensed under Apache-2.0. It handles the OAuth and OpenID flows, token issuance and validation, client management, consent and login flow orchestration, and JWKS management.
Does Ory Hydra manage user accounts?
No. It is a standalone OAuth 2.0 and OpenID Connect server without user management, and it connects to an existing identity provider through a login and consent app that you build. Any authentication endpoint works, including Ory Kratos, authboss, User Frosting or a proprietary system.
How can I run Ory Hydra in production?
Either as a managed service on the Ory Network, where the hosted OAuth2 and OpenID Connect product is powered by the open source Hydra server and is API compatible, or self hosted under your own control, with or without the Ory Enterprise License.
Which OpenID Connect profiles is Ory Hydra certified for?
The certified profiles are Basic, Implicit, Hybrid, OpenID Provider Publishing Configuration Information, and Dynamic OpenID Provider. Certification was obtained by deploying the unmodified reference user login and consent app together with Ory Hydra v1.0.0.
What do I need to build Ory Hydra from source?
The module requires Go 1.26 and declares the import path github.com/ory/hydra/v2, with the generated client and the ory/x dependency replaced by in-tree directories. The test target additionally needs Docker, because it starts MySQL, Postgres and CockroachDB containers before running go test.
Official sources
Where developers are discussing it
Posts on Hacker News, dev.to and Lobsters that link to this repository, found by our scan of those communities. 1 in the last 30 days; newest first.
- Go auth libraries: pick by the side of the wire you are ondev.to · Oct 31, 2026 · 4 points · 0 comments
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/ory-hydra)Star history chart for your README
[](https://hysenlabs.com/projects/ory-hydra)Was this useful?