RedELK pulls teamserver and redirector logs into one Elastic stack
Red Team's SIEM - tool for Red Teams used for tracking and alarming about Blue Team activities as well as better usability in long term operations.
At a glance
- What is it?
- A red team SIEM that centralises operational logs from multiple teamservers and traffic logs from redirectors, then queries them to notice defenders investigating the same infrastructure. The documentation is thin: the conceptual overview is a single sentence and the newest tag is from 2022.
- Who is it for?
- RedELK fits engagements where one person has to hold a picture of several teamservers at once, and the redirector traffic angle is the part that answers a question red teams keep asking. Check the wiki and the third-party playbooks before planning a deployment, because the repository ships no commands of its own and its conceptual overview never appears in text.
- Can I use it commercially?
- Yes. BSD-3-Clause is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 2 days ago.
- What is it written in?
- Mainly Python, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
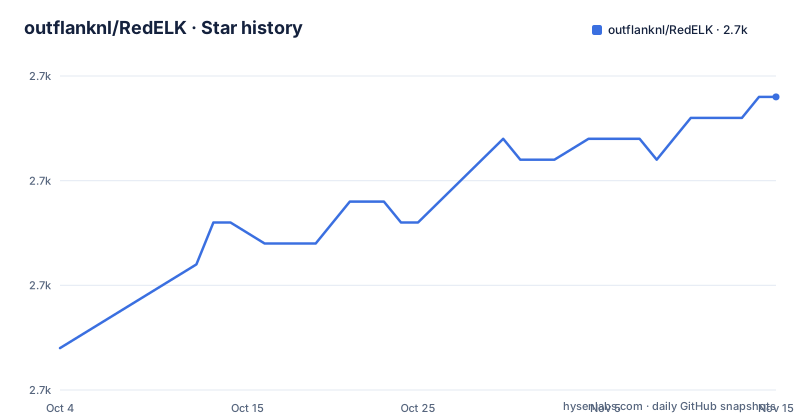
- outflanknl/RedELK2,689 ★ · +12
| Repository | 2026-10-04 | 2026-11-15 |
|---|---|---|
| outflanknl/RedELK | 2.7k | 2.7k |
12 Stars in the last 42 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The build badges name the whole stack: base, Elasticsearch, Jupyter, Kibana, Logstash
Five GitHub Actions badges sit above the project title, one for each development image: docker-build-dev-base.yml, docker-build-dev-elasticsearch.yml, docker-build-dev-jupyter.yml, docker-build-dev-kibana.yml and docker-build-dev-logstash.yml. That row is the closest thing to an architecture statement the README offers, and it settles the composition question immediately. A base image plus the Elasticsearch, Logstash and Kibana trio behind the ELK in the name, and a separate Jupyter image.
The Jupyter entry is the one worth noting. It is not part of the ELK trio, so the project builds an analysis surface as a first-class component rather than asking operators to query the store by hand. What that image is meant to contain is not stated anywhere in the README, and neither is how it receives the enriched events the other components hold.
Two log sources flow inward: teamservers and redirectors
The collection split runs along two axes, and the root tree names both: c2servers/ and redirs/. Operational logs from teamservers carry the operator-facing material, screenshots, indicators of compromise and keystroke output, gathered into one place so a historic search can span an operation rather than one box. Traffic logs from redirectors carry the network side, and those are what get queried to notice a blue team working through the same infrastructure.
The intended users are named as multiple: engagements described as multi-scenario, multi-teamserver, multi-member and multi-month. The stated benefit is that whoever holds the overview gets a read-only view of the operation, with the white team given as the example of someone outside it who needs one.
The last push is 2026, the newest tag is 2022
The repository is not archived and its last push was on 2026-09-23. The newest published release is v2.0.0-beta.6, published 2022-02-20, preceded by v2.0.0-beta.5 in January 2022 and v2.0.0-beta.4 in May 2021. So work has continued on master for roughly four and a half years past the last tagged build, and the version everyone can download is still a beta.
The tree carries both a VERSION file and a releasenotes.txt at the root, which means the project keeps release state as tracked text, yet the README states no version and no branch policy. Nothing in it says whether master is expected to be deployable, so the tag list and the working branch disagree about what current means, and the README leaves that question open.
The conceptual overview is one sentence and nothing else
A heading called Conceptual overview introduces the architecture, and its entire contents is the sentence announcing that a conceptual overview of how RedELK works follows. No description, no diagram in text, no data flow. Anyone trying to understand the pipeline before installing has to reassemble it from the directory names: elkserver/, c2servers/, redirs/, certs/, helper-scripts/, example-data-and-configs/, initial-setup.sh and images/.
Those names do sketch the shape, a server, the client side and the redirectors, and the directory called helper-scripts suggests glue that the README never explains. The installation section has the same shape of gap: it sends readers to the project wiki for the manual installation rather than describing one.
Installation is delegated to a wiki and to playbooks maintained elsewhere
No commands appear anywhere in the README. Deployment guidance is a pointer to the wiki plus three Ansible playbooks: a RedELK Server playbook and a RedELK Client playbook, both maintained by fastlorenzo, who is listed among RedELK's own developers, and ansible-redelk, maintained by curi0usJack of TrustedSec. The server and client split in those names is the only statement in the documentation about deployment topology.
The root directory complicates that reading. Alongside c2servers/ and redirs/ there is a separate elkserver/ and an initial-setup.sh, so the roles implied by the tree are more numerous than the two in the playbook names. The setup script is present in the tree and absent from the README, which never says when it should run or what it expects to find.
certs/ sits in the tree with no explanation anywhere
A certs/ directory is a top-level entry, next to elkserver/ and initial-setup.sh, and the README does not mention certificates, TLS, or key handling at any point. It is not said what generates the contents, which components consume them, or whether they are shipped as placeholders that an operator has to replace before anything is exposed.
That is worth flagging because the same tree holds example-data-and-configs/, which is at least named for what it holds. Certificates are load-bearing for a distributed stack that receives logs from teamservers and redirectors over a network, and a directory with that name appearing undocumented is a question for the maintainers rather than something an operator should guess at.
Keystrokes and screenshots are collected, with no stated limits
The README is explicit that the operational view covers screenshots, indicators of compromise and keystroke output, alongside the enriched log stream. That is the strongest content claim in the project, and it is also the one with the least surrounding detail. Nothing says how long collected material is kept, who can read it, how the teamservers authenticate to the store, or whether anything is redacted before it lands.
Enrichment is named twice, once for operational logs and once for traffic logs, and is never defined. For a tool whose purpose includes giving a read-only window to a white team, the access model is the part an operator needs most and gets least.
Every dated guide in the README stops in 2020
The background section points at a wiki, three blog posts on outflank.nl dated 2019-02-14, 2020-02-28 and 2020-04-07, and four conference appearances: BruCon 2018, x33fcon 2019, Hack in Paris 2019 and SANS Hackfest 2020. Every dated artefact there falls between 2018 and 2020, which lines up with the 2022 tag rather than with a 2026 push.
The authors section names four maintainers, Marc Smeets, Mark Bergman, Lorenzo Bernardi and Geert Smelt, and asks for contributions in code and in ideas for alarms and usability work. So the project still solicits input after the docs went quiet, which means the wiki rather than the README is where anyone actually deploying should start reading.
Editorial conclusion
RedELK fits engagements where one person has to hold a picture of several teamservers at once, and the redirector traffic angle is the part that answers a question red teams keep asking. Check the wiki and the third-party playbooks before planning a deployment, because the repository ships no commands of its own and its conceptual overview never appears in text. Confirm which version you are deploying: the last push was on 2026-09-23 while the newest published tag, v2.0.0-beta.6, dates from 2022-02-20, and no document here reconciles the two.
Frequently asked questions
what is RedELK
RedELK collects operational logs from red team teamservers and traffic logs from redirectors into one searchable store. The root tree splits it into elkserver/, c2servers/ and redirs/, and the build badges name separate images for Elasticsearch, Logstash, Kibana and Jupyter.
Which components does RedELK run on?
The badges above the project title name five development image builds: a base image plus Elasticsearch, Jupyter, Kibana and Logstash. Jupyter sits outside the Elastic trio, so analysis is a built component rather than something operators wire up themselves.
How do I install RedELK?
The README carries no commands. It points to the project wiki for the manual installation and lists three Ansible playbooks: a RedELK Server playbook and a RedELK Client playbook by fastlorenzo, and ansible-redelk by curi0usJack of TrustedSec.
How does RedELK detect blue team activity?
Traffic logs from redirectors are collected and enriched alongside the operational logs, and running specific queries over them is what surfaces a blue team investigating your infrastructure. The queries themselves are not written down in the README.
Which RedELK version should I deploy?
Nothing in the README settles it. The repository root holds a VERSION file and a releasenotes.txt next to a master branch last pushed on 2026-09-23, while the newest published tag is v2.0.0-beta.6 from 2022-02-20, and no document reconciles the two.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/outflanknl-redelk)Star history chart for your README
[](https://hysenlabs.com/projects/outflanknl-redelk)Was this useful?