One folder per Samsung preinstalled-app vulnerability, 176 of them
176 vulnerabilities in Samsung preinstalled Android apps
At a glance
- What is it?
- A responsible disclosure report laid out as 176 numbered directories, where the titles cluster into a few recurring classes of preinstalled-app bug and the per-report bounties range from two hundred dollars to five figures.
- Who is it for?
- Use this repository as a taxonomy of preinstalled-app vulnerability classes, not as a scanner and not as a patch checklist, since every finding in it is described as already fixed and the index titles name no firmware builds. It is most useful to a security reviewer who wants to know which components Samsung ships and which of them handle intents, content providers or shared UIDs.
- Can I use it commercially?
- Yes. BSD-2-Clause is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 123 days ago.
- What is it written in?
- Mainly Java, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
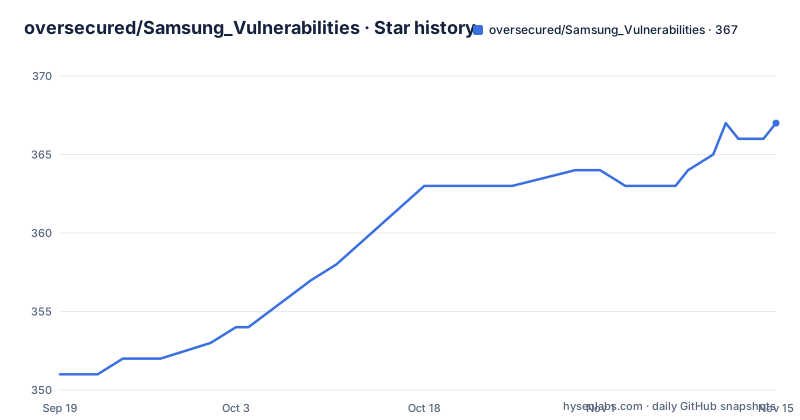
- oversecured/Samsung_Vulnerabilities367 ★ · +16
| Repository | 2026-09-19 | 2026-11-15 |
|---|---|---|
| oversecured/Samsung_Vulnerabilities | 351 | 367 |
16 Stars in the last 57 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The report is the directory listing
oversecured/Samsung_Vulnerabilities is a disclosure report rather than a tool. There is no build, no dependency file and nothing to install; the primary language is recorded as Java because that is what the affected applications are written in, not because there is Java source here to compile.
The structure is one top-level directory per finding, numbered and titled with the affected app and the bug class. Entry 001 is Settings and intent redirection with system privilege, 002 is FactoryCamera and corruption of arbitrary files with system privilege, 003 and 004 are both Galaxy Themes Service, and the sequence continues through the 020s. The README index and the directory names carry the same information in two places, so the tree alone is browsable without opening anything.
The scope is stated precisely: 176 vulnerabilities discovered between 2022 and 2025, with detailed descriptions of 140. The remaining 36 are listed without a write-up, which is normal for coordinated disclosure where a full explanation would help someone else find the same bug before the fix ships everywhere.
Intent redirection, file writes and provider access are the recurring three
Read the titles as a set and the findings collapse into a small number of families.
Intent redirection appears more than once: Settings in 001, Galaxy Store together with AppLinker in 005, where the redirect rides on an `install_complete` broadcast, and Samsung Galaxy Friends in 017. Arbitrary file write and corruption form the second family, in 002 for FactoryCamera, 006 for Galaxy Store, 009 for Contacts Storage through `CallLogProvider`, and 012 for CallBGProvider running as the phone UID.
The third family is access to arbitrary content providers, which shows up as 013 for CallBGProvider, 024 for Video Trimmer through MultiGridActivity, and 027 for DeX for PC with system privilege.
That clustering is the most reusable thing in the report. Preinstalled apps that hold shared UIDs, register broadcast receivers or expose content providers are the three places where a vendor-specific bug tends to live, and 176 findings spread across roughly thirty applications confirm the pattern rather than a single isolated mistake.
Shared UIDs are the root cause the titles keep pointing at
Several entries name the mechanism outright, which makes them more useful as a reference than the ones that only name a symptom.
Entry 012 is overwriting arbitrary files as UID android.uid.phone, and 013 is gaining access to arbitrary content providers as the same UID. Two findings in the same application, with the same UID named, is a signal about how that application was integrated rather than about two separate bugs.
Privilege shows up in the same way. Entry 004 is directory listing with system privilege in Galaxy Themes Service, 001 is intent redirection with system privilege in Settings, and 027 is content provider access with system privilege in DeX for PC. Where the word privilege appears in a title, the finding is about a vendor app operating with more authority than an ordinary application should hold.
One detail worth flagging for anyone parsing these names: three titles write arbitrary with an asterisk after it, as in arbitrary* content providers. The report does not explain the asterisk in the visible index, so a script keying on those strings should match on the surrounding words rather than assuming the asterisk is significant.
The information leaks are identifiers, not just content
A second cluster is disclosure rather than execution, and it is the cluster that matters most to a person carrying the phone rather than an attacker with the phone.
Entry 021 discloses phone-related information including IMSI and MSISDN through Group Sharing, and 011 leaks contact details through Phone. Those two are identifiers that follow a SIM card and a person across apps.
The rest are network and proximity data. Entry 014 discloses Wi-Fi connection info through CSC, 018 leaks connected devices and shared files from Nearby Service, and 023 leaks connection data about streamed devices from Smart View. Entry 010 leaks a token from Galaxy Themes.
Worth separating clearly: a leaked token or Wi-Fi detail is a privacy problem for the user, while the arbitrary-file and provider-access entries are code execution or data access problems for anyone who can reach them. The titles in this repository cover both, and a reader assessing risk for one device should not average them together.
Billing is the sharpest cluster: universal XSS and SQL injection
Two entries against Samsung Billing sit adjacent in the numbering and are the most serious pair by class.
Entry 025 is universal XSS, and 026 is SQL injection in IAPService. In-app purchase code is a target worth naming because it runs with the account and payment context attached, and SQL injection in a service component suggests an injectable query surface behind an exported or reachable interface.
Alongside them, entry 019 allows locking the device through the Link to Windows Service, which is a denial-of-service against the handset rather than data theft, and entry 020 lets an actor interact with MobileServiceSocialService and perform arbitrary actions on the user's behalf, which is an authorisation failure rather than a data leak.
None of these four are described in detail in the visible index, so the mechanism has to be read in the individual folders. The titles are enough to tell you which applications to audit in your own review, and that is close to the limit of what an index can carry.
What a coordinated disclosure leaves behind
The context around the list matters as much as the list.
Samsung runs a vulnerability disclosure programme and regular security audits, and the research team reported to that programme's team, describing the response as quick and efficient. All vulnerabilities in the list are stated to be already fixed with the researcher's help, and when the article was published Samsung had rewarded the team a total written as $163.475 and ranked them first in its security research ranking. The per-report values in the visible rows run from $200 for opening arbitrary URLs in EsimClient to $10,310 for corruption of arbitrary files in FactoryCamera.
Earlier context is in the same repository's history rather than in the list: a two-week study of Samsung's system app security in 2021 that produced 17 vulnerabilities, reported and fixed before this round began.
Two things are conspicuously absent from the index. No CVE identifiers appear in the visible titles, and no affected firmware or One UI build numbers do either, so a finding cannot be mapped to a specific release from this repository alone. That is the practical limit on using it, and it is why it reads as a taxonomy rather than as a triage tool.
BSD-2-Clause, last push 2026-07-15, no releases
The repository is licensed BSD-2-Clause, which is permissive enough that the write-ups can be quoted with attribution, and it is not archived, with the last push dated 2026-07-15.
There are no GitHub releases and no versioning scheme, which suits a corpus that only grows as findings are published. Nothing in the top level suggests tooling beyond the numbered directories and the README, so a reader who wants to process these findings programmatically would be writing that script themselves, and the directory names are the stable interface available.
One risk to keep in mind when reading any disclosure corpus: the descriptions describe applications as they were during 2022 to 2025. Samsung ships monthly security updates and has patched everything in this list according to the report, so a title like arbitrary file write in Galaxy Store describes a historical state of that app rather than what you will find on a current handset.
Editorial conclusion
Use this repository as a taxonomy of preinstalled-app vulnerability classes, not as a scanner and not as a patch checklist, since every finding in it is described as already fixed and the index titles name no firmware builds. It is most useful to a security reviewer who wants to know which components Samsung ships and which of them handle intents, content providers or shared UIDs. Check the licensing and the folder contents before reusing any write-up, and do not treat the bounty column as a severity scale.
Frequently asked questions
What is inside the Oversecured Samsung vulnerabilities repository?
176 vulnerabilities found in Samsung preinstalled Android apps between 2022 and 2025, with detailed descriptions of 140 of them. Each finding sits in its own numbered top-level directory named after the affected app and the bug class.
Which Samsung apps are named in this vulnerability report?
Settings, FactoryCamera, Galaxy Themes Service, Galaxy Store with AppLinker, EsimClient, call settings, Contacts Storage, Phone, CallBGProvider, CSC, Game Optimizing Service, Samsung Galaxy Friends, Nearby Service, Link to Windows Service, Group Sharing, Smart View, Video Trimmer, Samsung Billing, DeX for PC and PersonaManagerService, among others.
How much reward did these Samsung vulnerabilities earn?
The report states Samsung had rewarded the team a total written as $163.475 and ranked them first in its security research ranking. Individual values in the visible rows range from $200 for EsimClient to $10,310 for FactoryCamera, and the bounties track impact rather than serving as a severity scale.
Can I use this report to check whether my Galaxy is affected?
Not directly. Every vulnerability in the list is described as already fixed with the researcher's help, and the index titles name no CVE identifiers and no affected firmware builds, so a finding cannot be mapped to a specific release from this repository alone.
What did the earlier Samsung research in 2021 find?
A two-week study of Samsung's system app security that resulted in the discovery of 17 vulnerabilities, which were reported to Samsung and fixed before the 2022 to 2025 round covered in this repository began.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/oversecured-samsung-vulnerabilities)Star history chart for your README
[](https://hysenlabs.com/projects/oversecured-samsung-vulnerabilities)Was this useful?