laravel-wechat and the install line that asks for the previous major
WeChat SDK for Laravel, based on overtrue/wechat.
At a glance
- What is it?
- A WeChat integration for Laravel built on the easywechat SDK: a message route, an OAuth middleware, authorization events and open platform verification. Its install command asks for version 7.2 while the newest release is 8.0.0, it names two different upstream projects, and its OAuth instructions target an application skeleton the CSRF section already moved past.
- Who is it for?
- laravel-wechat fits a Laravel application that has to receive WeChat messages and read a signed-in user's profile, and it removes the two pieces of glue that are easy to get wrong, the route that must accept both verbs and the session key the OAuth middleware writes. Four things to check first.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 42 days ago.
- What is it written in?
- Mainly PHP, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 14, 2026, and from our analysis. They are not legal advice.
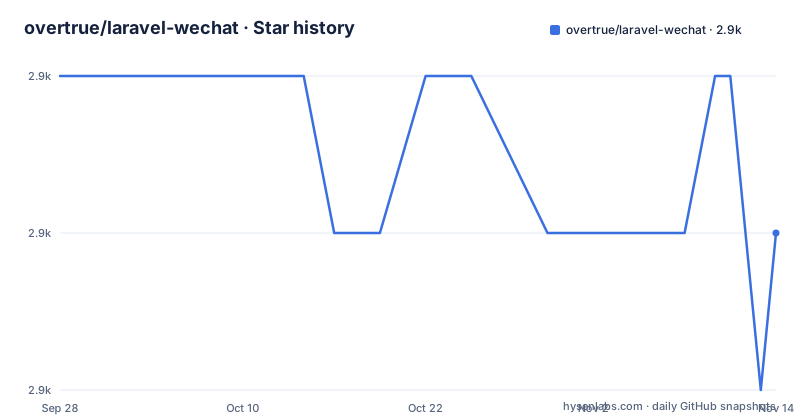
Star history
- overtrue/laravel-wechat2,899 ★ · -1
| Repository | 2026-09-28 | 2026-11-14 |
|---|---|---|
| overtrue/laravel-wechat | 2.9k | 2.9k |
-1 Stars in the last 47 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The install line asks for a major that is no longer current
The install section is one command:
composer require overtrue/laravel-wechat:^7.2The requirement table two sections above it stops at the 7.x line, mapping version 7 of the package to Laravel 8.0 or newer, version 6 to Laravel or Lumen 7.0 or newer, and version 5.1 to Laravel or Lumen 5.1 or newer. The repository's default branch, meanwhile, is 8.x, and the newest release is 8.0.0, published in March 2026. So a reader who copies the command the file gives them installs the previous major of a package whose current major is the branch it is shipping from. The same table also quietly drops Lumen: a line near the top says that from 7.x onwards Lumen is no longer supported by default, which is the one framework-support change the file records.
The summary names one upstream project and the README names another
The repository summary says this package is built on overtrue/wechat. The README says it is built on the easywechat project at w7corp/easywechat and links that repository in its first line. The closing line of the file sends the reader to easywechat.com for the SDK's own documentation. Three references to an upstream dependency across two files, and one of them disagrees with the other two. It matters more than a naming quibble, because what this package contributes is the Laravel-shaped glue: the route, the controller, the middleware, the events and the published configuration. The behaviour of every call those make is defined by the upstream SDK, so which repository you actually read when something returns an unexpected value is the first thing to settle.
CSRF is written for two Laravel generations, the OAuth middleware for one
WeChat cannot post to a route that requires a CSRF token, so the file tells you to exclude its routes from that check, and it tells you twice. The first form is the classic property on the application's CSRF middleware, with the route prefix in an exclusion array. The second is explicitly for the newer generation, a call on the middleware builder inside the application bootstrap file that takes an except argument. The OAuth section then walks back to the older shape: it tells you to add your middleware to the route middleware array inside the HTTP kernel file, a file the newer skeleton does not have. So on the latest Laravel a reader gets the CSRF step from the file's modern example and the OAuth step from its obsolete one, in the same document, with nothing marking the difference.
One route that accepts any verb, and the reason given in full
The message entry point is a single route registered with a call that accepts every HTTP verb, and the file insists on that choice with an explanation rather than leaving it implicit: WeChat's server-side verification arrives as a GET, while user messages arrive as a POST, so a route restricted to one of them breaks half the conversation. The controller that handles it logs the arrival, resolves the official account's server object out of the container by a dotted key, attaches a closure that returns a fixed string, and serves. The account comes from configuration rather than from a constructor argument, which is what makes the next section possible.
One account name, threaded through middleware, session and events
The configuration section says most modules support multiple accounts, with the name default as the default one. That string then reappears in three more places. It is the suffix you can pass to the OAuth middleware to select a configuration. It is the last segment of the session key that holds the authorized user profile. And it is the account property carried on the authorization event, alongside the user object and a flag saying whether the session was newly created. So the identity of the account is a bare string that has to agree across four call sites, and the file gives no warning for the case where it does not. If you run more than one account, that string is the thing to get right before anything else in this package.
A documented way to fabricate the authorized session
There is a section on simulating authorization, for the situation where a developer wants to work locally and only go through the real flow after deployment. It builds a user object of the SDK's social user type, filling in an id, a name, a nickname, an avatar URL, an email, an original array and a provider name, then writes that object straight into the session under the same key the OAuth middleware reads. The file is explicit about ordering: the write has to happen before the middleware runs, and the suggested mechanism is a global middleware that is enabled only in a development environment. It also says which fields matter for which scope, everything for the user-info scope and only the open identifier for the base scope. This is a test double for your own application rather than a way around WeChat's verification, and the single sentence about development environments is the whole of the guard.
Open platform events come back through an invokable controller
Third-party application support is handled by a trait that takes care of server verification, wired to a route that accepts any verb and points at an invokable controller. Its single method takes an application object and returns a PSR response interface, resolving the open platform client from the container and delegating to the trait. Four events are named for the notifications the platform pushes: an authorization granted, an authorization updated, an authorization withdrawn, and a verify ticket refreshed. Each carries the notification payload as its payload property. Once configured, one URL on your domain becomes the event receiving endpoint for the third-party applications registered against it, which makes it the piece of this package with the widest blast radius and the least explanation.
An English README beside the Chinese one, and an agent file
The repository root holds an English README next to the Chinese one this file is, plus an agent instruction file, a configuration directory, the source directory, the composer manifest, the licence and a workflows directory. The README links to neither the English version nor the agent file, and apart from the version matrix and the code samples it is written entirely in Chinese. So there is an English entry point for readers who want one, and the way to find it is to list the repository. The maintainer's identity is visible throughout, through the sponsor link and a note crediting a JetBrains licence for the work, which is also the only statement in the file about how the project is resourced.
Editorial conclusion
laravel-wechat fits a Laravel application that has to receive WeChat messages and read a signed-in user's profile, and it removes the two pieces of glue that are easy to get wrong, the route that must accept both verbs and the session key the OAuth middleware writes. Four things to check first. The install line asks for the previous major, so read the requirement table and the release list before you copy it. The OAuth middleware is still documented through the classic application kernel, which the newest Laravel skeleton does not have, so budget a translation step. The mock authorization feature writes a fabricated user into the session and the only guard the file offers is a sentence about development environments. And the repository names one upstream project in its summary and a different one in its README, so read the README before you assume which SDK you are configuring against.
Frequently asked questions
What is overtrue/laravel-wechat?
A WeChat SDK integration for Laravel, packaged as EasyWeChat for Laravel and built on the easywechat SDK. It provides the server and OAuth pieces: a route and controller for receiving messages, an OAuth middleware with a per-account session, an authorization event, and open platform server verification.
How do I install overtrue/laravel-wechat?
Require it with composer require overtrue/laravel-wechat:^7.2, then publish its configuration file using the vendor:publish command with the package's service provider. Registering an alias for the facade is optional.
Which Laravel versions does overtrue/laravel-wechat support?
The requirement table maps package version 7 to Laravel 8.0 or newer, version 6 to Laravel or Lumen 7.0 or newer, and version 5.1 to Laravel or Lumen 5.1 or newer. Lumen is not supported by default from 7.x onwards. The repository's default branch is 8.x and its newest release is 8.0.0.
How does overtrue/laravel-wechat handle the WeChat callback route?
It is registered as a route that accepts any HTTP verb, and the README insists on that, because WeChat's server verification arrives as a GET while user messages arrive as a POST. The controller resolves the official account server from the container and serves it, with a callback attached for the reply.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/overtrue-laravel-wechat)Star history chart for your README
[](https://hysenlabs.com/projects/overtrue-laravel-wechat)Was this useful?