PatchMon pipes its setup script from the default branch and ships three patch releases in one day
Linux Patch Management & Automation Platform
At a glance
- What is it?
- An AGPL-3.0 Go server that patches Linux, FreeBSD and Windows fleets from outbound-only agents, with dry-run validation, approval audit trails, OpenSCAP compliance scanning and a browser SSH terminal carrying an AI assistant. Three point releases shipped on the same day in August 2026, the quick start curls its installer from the default branch, and the CodeQL job scans JavaScript only.
- Who is it for?
- PatchMon fits an operations team that wants to see what a patch run will do before it does it, because the dry-run validation, the per-host audit trail naming who approved what, and the ability to watch a run stream and stop it mid-flight are the features that separate this from a cron job, and the outbound-only agent design means you can enrol a fleet without opening a port on anything. Three things to weigh.
- Can I use it commercially?
- Yes, with strict conditions. AGPL-3.0 is a network copyleft licence: if people use a modified version over a network, for example as a hosted service, you must offer them its source code under the same licence.
- Is it still maintained?
- Yes. The repository last received commits 4 days ago.
- What is it written in?
- Mainly Go, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
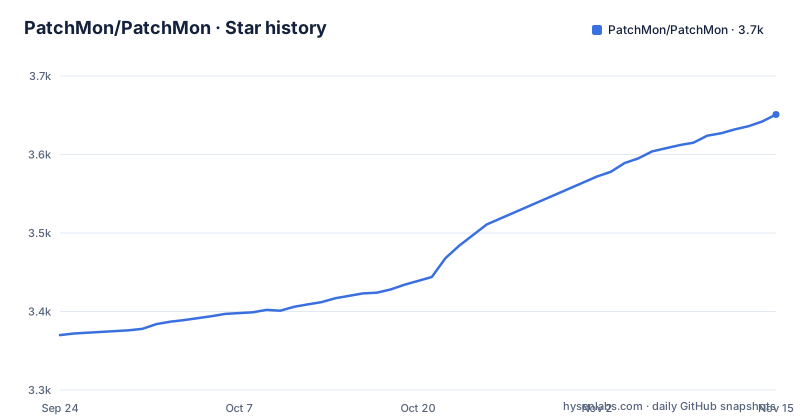
Star history
- PatchMon/PatchMon3,651 ★ · +281
| Repository | 2026-09-24 | 2026-11-15 |
|---|---|---|
| PatchMon/PatchMon | 3.4k | 3.7k |
281 Stars in the last 52 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Three patch releases shipped on one day
The three most recent releases are 2.1.1, 2.1.2 and 2.1.3, and all three were published on 2026-08-15, roughly five and a half hours apart from one another. A burst like that usually means a fix went out, something in it broke, and the next patch corrected it, which is normal but worth reading as three tags rather than one. The default branch is main and was last pushed on 2026-08-26, eleven days after the last release, so the branch is ahead of every published tag. None of that is a mark against the project, which is not archived and is moving, but it does mean the release you install and the code in the repository are two different things unless you pin.
The quick start pipes a shell script out of the default branch
Three commands stand between you and a running instance, and two of them are worth reading closely:
mkdir patchmon && cd patchmon
bash -c "$(curl -fsSL https://raw.githubusercontent.com/PatchMon/PatchMon/refs/heads/main/docker/setup-env.sh)"
docker compose up -d
The middle line fetches a script over HTTPS and executes it in the same command, and the URL points at the main branch of the repository rather than at a tag. The content you run therefore changes whenever the repository's default branch does, with no tag and no checksum to verify against. That is a deliberate convenience for a trial, and it is the wrong pattern for anything you intend to keep. The script is described as downloading a compose file and an example environment file, generating all required secrets, and walking you through the URL and CORS origin configuration interactively. The Proxmox path does the same thing with a community script fetched from that project's own main branch.
A browser SSH terminal with an AI panel attached to four model providers
The access section describes a terminal in the browser that connects to any host from the user interface, and a built-in assistant panel inside that terminal offering command suggestions, error diagnosis and context-aware help. The assistant is described as working with OpenRouter, Anthropic, OpenAI or Google Gemini. That combination deserves a plain reading: this is a shell into your production hosts, rendered in a browser, with a chat panel that can send context about what you are doing to an external model provider. Nothing about that is wrong for a tool that ships a browser terminal in the first place, but the data flow is a decision to make deliberately rather than by accepting a default. Access to it sits behind role-based access control and single sign-on, which are the boundaries that matter if the panel is enabled.
Proxy mode turns the agent into an SSH relay
The terminal has two modes. In direct mode it connects to the host the way SSH normally would. In proxy mode the connection is routed through the agent, and the stated benefit is that no SSH port is exposed. That is a real improvement in exposure, and it also changes the agent's job. The agent that was designed to make one outbound, scheduled, low-volume report now carries interactive shell traffic in both directions for the life of a session. The same outbound-only property still holds, and no inbound port appears anywhere, but the agent becomes a network path rather than a beacon. Worth thinking through against your own threat model, particularly for the hosts where the terminal is enabled at all.
Docker is the only self-hosted path marked officially supported
The deployment section lists four routes and marks exactly one of them. Self-hosted Docker carries the parenthetical that it is the officially supported option, with hardened images named as the reason. Manual Docker setup is documented on the operator guide site. Proxmox LXC is one command through a community helper script, which by its nature is not the same as an officially supported path. The fourth is the managed cloud, offered with a fourteen-day trial, where the vendor handles provisioning, updates, backups and scaling. That structure is worth reading as a statement about where the support burden sits: the Docker image is the product, and the LXC route is a convenience built on somebody else's script.
The root manifest says version 0.0.0 and describes a Linux system
The JavaScript manifest at the repository root is not the package you install; it is a workspace for building the interface. It declares the project private, sets the version to 0.0.0, describes the product as a Linux patch management system when the product now covers three operating systems, and defines a frontend workspace. Its scripts are the interesting part, since they are the project's development surface: a Go server and an agent, each with a watch mode, a frontend dev server, and a combined dev command that runs both concurrently. Formatting and linting go through one tool across the tree, dependency auditing has a high-severity gate for JavaScript and a separate vulnerability check that walks both Go modules, and a secrets scan plus a code analysis job sit behind a single security script.
Secret scanning pulls an unpinned image and CodeQL reads only JavaScript
Two details in that security script are worth knowing before you rely on it. The secrets scan runs a container image by name with the tag latest, which means the tool that guards your repository is whatever that image resolves to on the day you run it, and the image is a third party's rather than a pinned digest. The code analysis job creates a database with the language set to JavaScript and runs a JavaScript security suite over it. Neither Go tree is analysed, so the server and the agent are outside the reach of that job even though the JavaScript vulnerability check does walk both of them with a different tool. The three security jobs are: secrets, JavaScript code analysis, and package and module vulnerability audits.
The readme truncates mid-heading and repeats its quick start
The document has two editorial problems worth naming, because both affect whether you can finish reading it. The section on enrolling hosts begins and then stops partway through the heading, so the instructions for getting an agent onto a machine are the part that is not visible, and that is the step a new user needs most. Separately, the same three-line quick start appears twice, once near the top and again under the Docker deployment section, with no difference in wording, which is a duplication a reader will notice. There is also an AI declaration file linked as a badge in the header, which is the sort of thing you would want to read before enabling the terminal's assistant.
Editorial conclusion
PatchMon fits an operations team that wants to see what a patch run will do before it does it, because the dry-run validation, the per-host audit trail naming who approved what, and the ability to watch a run stream and stop it mid-flight are the features that separate this from a cron job, and the outbound-only agent design means you can enrol a fleet without opening a port on anything. Three things to weigh. The quick start pipes a shell script straight out of the default branch, so pin a release tag if you care about what runs. The SSH terminal has an AI assistant that talks to four external model providers, and whatever you type there can leave your network. And the security tooling has a gap: secret scanning pulls an unpinned container image and the code analysis job covers JavaScript rather than the Go server and agent.
Frequently asked questions
what is patchmon
An AGPL v3 licensed platform for monitoring, patching and securing a Linux, FreeBSD and Windows fleet. One Go binary with the interface embedded talks to outbound-only agents on a schedule, so no inbound ports, SSH exposure or VPN are needed on monitored hosts.
how to install patchmon
Create a directory, run the setup script fetched from the repository's docker directory, then bring the stack up with docker compose up -d. The application listens on http://localhost:3000 by default, where you create an admin user and add a host.
is patchmon free
Self-hosting is free under the AGPL v3 licence. Production hosting is sold separately as a managed cloud offering with a fourteen-day trial, and Docker is the self-hosted path marked as officially supported.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/patchmon-patchmon)Star history chart for your README
[](https://hysenlabs.com/projects/patchmon-patchmon)Was this useful?