vm2's own readme tells you it should not be your only line of defence
Advanced vm/sandbox for Node.js
At a glance
- What is it?
- A sandbox that runs untrusted JavaScript in the same Node process using the built-in VM module, Proxies and an overridden require. What makes this readme unusual is that it spends more space on why in-process sandboxing keeps failing, which alternatives exist, and why Bun support is compatibility rather than a security boundary.
- Who is it for?
- vm2 is for the case its own readme names: untrusted code that is not fully untrusted, meaning internal tools or plugins from authors you have vetted, where you need tight integration with host objects and fast synchronous calls, and where you are layering network isolation, filesystem restrictions and resource limits around it anyway. Three things to take from the documentation before you use it.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 35 days ago.
- What is it written in?
- Mainly JavaScript, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 21, 2026, and from our analysis. They are not legal advice.
Star history
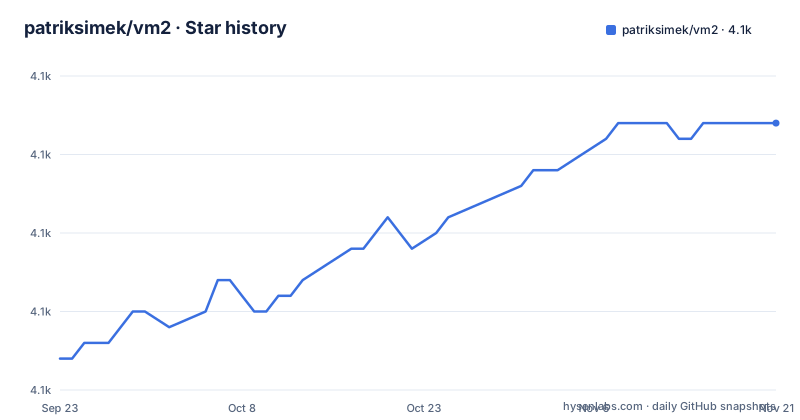
- patriksimek/vm24,117 ★ · +15
| Repository | 2026-09-23 | 2026-11-21 |
|---|---|---|
| patriksimek/vm2 | 4.1k | 4.1k |
15 Stars in the last 59 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The readme leads with how sandboxing keeps failing
The security disclaimer comes before the feature list, and its first line is an instruction to understand how vm2 works and its limitations before using it. The mechanism is described next: vm2 attempts to sandbox untrusted JavaScript within the same Node.js process as your application, through a complex network of Proxies that intercept and mediate every interaction between the sandbox and the host environment. Then comes the reason that mechanism is hard, stated as the fundamental challenge. Objects can be reached through prototype chains, constructors can be reached via error objects, symbols provide protocol hooks, and async execution creates timing windows. The conclusion drawn is that the sheer number of ways to traverse from one object to another makes an airtight in-process sandbox extremely difficult, which is the honest version of why the next section exists.
New bypasses will likely be found, and you must keep updating
Three numbered consequences follow from that difficulty, and they are the operational part of the disclaimer. First, new bypasses will likely be discovered in the future, with a pointer to the repository's security advisories. Second, you must keep vm2 updated to benefit from the latest security fixes, subscribe to security advisories and update promptly. Third, vm2 should not be your only line of defence, because defence in depth is essential when running untrusted code. Underneath the three is a maintenance claim: despite best efforts, researchers and security professionals continuously discover new ways to escape, and the project patches them as they are reported. That pairing, an active patch record next to an admission that the record is incomplete, is what a cat-and-mouse problem looks like from the maintainer's side. The releases back it up in shape, with v3.12.0, v3.12.1 and v3.12.2 all published in the first week of September 2026.
Bun support is compatibility, not a security boundary
The runtimes table has two rows and they are not comparable. Node.js is supported, and the sandbox is a security boundary. Bun is experimental, with partial functional compatibility, and explicitly not a security boundary. The explanation underneath is the most precise paragraph in the readme. vm2's threat model, the attack catalogue in docs/ATTACKS.md and every regression test in test/ghsa/ are derived from V8 internals. Bun uses JavaScriptCore, which has its own equivalents, and none of them have been audited against vm2's bridge. A passing test suite under Bun therefore demonstrates compatibility, not that the sandbox holds there, and the readme's instruction is blunt: do not use vm2 on Bun to isolate untrusted code. Two separate limitations are named for Bun and neither implies the other, which is a careful distinction, because a reader could otherwise conclude that a green run means a safe run.
A 64 MB allocUnsafe takes over 400 seconds under Bun
The partial-compatibility claim is then backed by specifics. A green Bun run covers only the tests that actually execute there, test/bun-skips.js records what is excluded and why, and the known behavioural gaps are named. Buffer.from with an arrayLike argument returns a zero-length buffer. VMScript metadata for filename, lineOffset and columnOffset is not observable, because JavaScriptCore's CallSite objects carry no methods. Object.freeze on a frozen host object with a non-configurable accessor throws a proxy-invariant TypeError where V8 does not. And the performance gap is the one to notice: some Buffer operations across the sandbox boundary are drastically slower, with a 64 MB allocUnsafe taking over 400 seconds against 1.7 on Node, slow enough that the readme says it reads as a hang. So a Bun deployment is a compatibility target for trusted code, not a faster or equivalent runtime.
Four alternatives are named, each with a cost
The alternatives table is the most useful part of the disclaimer for anyone deciding whether to use vm2 at all. isolated-vm gives separate V8 isolates on a different V8 heap, is rated fast, and its trade-offs are that it is in maintenance mode and requires manual V8 updates. A separate process or Worker, using child_process or Worker threads with limited permissions, is rated medium, with higher IPC overhead and the requirement that data be serialized. Containers or virtual machines, naming Docker, gVisor and Firecracker, are rated slow, with startup overhead and a resource-heavy profile. Managed services, naming cloud-based code execution such as AWS Lambda or Cloudflare Workers, are rated variable, with network latency and an external dependency. Each row pays for isolation in a different currency, so the choice is which cost your use case can absorb.
The gap between node:vm and vm2 is one line of traversal
The readme demonstrates the difference rather than asserting it, with two short snippets. Against Node's own module:
import { runInNewContext } from "node:vm";

runInNewContext('this.constructor.constructor("return process")().exit()');
console.log('Never gets executed.');
That reaches the real process object, so the console.log after it never runs. Against vm2:
import { VM } from 'vm2';

new VM().run('this.constructor.constructor("return process")().exit()');
// Throws ReferenceError: process is not defined
One string of prototype traversal is the whole demonstration, which is the point: the built-in context is not a security boundary, and vm2's job is to break exactly that chain by proxying every property access. The features section adds the rest of the surface, console output control, limited access to process methods, requiring built-in and external modules from inside the sandbox, the ability to restrict which built-in modules are reachable, calling methods and exchanging data and callbacks between sandboxes, and transpiler support.
Two runtime dependencies, and both of them are an acorn parser
Installation is one command:
npm install vm2After that the dependency list is short enough to read in full. The package is vm2 at version 3.12.2, published by Patrik Simek under the MIT licence, and it has exactly two runtime dependencies: acorn at ^8.15.0 and acorn-walk at ^8.3.4. Both are JavaScript parsers, which tells you the package parses code rather than only interpreting strings at runtime, and that is what the transpiler support feature rests on. Development dependencies are eslint at ^9.38.0 and mocha at ^12.0.0-beta-9.2. The manifest declares sideEffects as false, exposes a single entry point at index.js with types at index.d.ts, and publishes lib, index.js, index.d.ts, LICENSE.md and README.md. It also declares a bin entry named vm2 pointing at ./bin/vm2, so there is a command line entry point that the visible documentation does not describe.
engines says node 6, the test runner is a 2026 beta
Two details in the manifest sit oddly next to each other. The engines field says node >=6.0, which is a very old floor and is presumably there to say that the package does not restrict the runtime. Meanwhile the development toolchain is current: a 2026 beta of mocha and eslint 9. The scripts explain the shape of the workflow. build:sources runs node scripts/build-sources.js, and the same script is wired into pretest and prepublishOnly, so sources are generated before tests and before publishing rather than committed by hand. The test script is mocha over the test directory, recursive, ignoring test/compilers.js and requiring ./test/bun-setup.js, and there is a separate test:compilers script for the file that main run skips. The repository tree matches that: scripts/, test/, docs/, lib/, bin/, a CHANGELOG.md, a SECURITY.md, a CLAUDE.md and a .claude/ directory.
Editorial conclusion
vm2 is for the case its own readme names: untrusted code that is not fully untrusted, meaning internal tools or plugins from authors you have vetted, where you need tight integration with host objects and fast synchronous calls, and where you are layering network isolation, filesystem restrictions and resource limits around it anyway. Three things to take from the documentation before you use it. The readme states plainly that new bypasses will likely be discovered, that you must keep the package updated to get the fixes, and that it should not be your only line of defence. For code from completely untrusted sources, such as arbitrary user submissions, it recommends a solution with stronger isolation guarantees instead, and it names four with their trade-offs, where isolated-vm is fast but in maintenance mode and needs manual V8 updates. And the runtime story is split: Node.js is supported and the sandbox is a security boundary there, while Bun is experimental, partial, and explicitly not a security boundary, because vm2's threat model and its regression tests are all derived from V8 internals that JavaScriptCore does not share.
Frequently asked questions
What is vm2?
A sandbox that can run untrusted code with whitelisted Node's built-in modules, installed with npm install vm2. It uses the internal VM module to create a secure context, Proxies to prevent escaping, and an overridden require to control access to modules.
Is vm2 safe for untrusted code?
The readme says new bypasses will likely be discovered, that you must keep vm2 updated for security fixes, and that it should not be your only line of defence. For code from completely untrusted sources such as arbitrary user submissions, it recommends a solution with stronger isolation guarantees.
Does vm2 work with Bun?
Bun is listed as experimental with partial functional compatibility, and explicitly not a security boundary. vm2's threat model, the attack catalogue in docs/ATTACKS.md and the regression tests in test/ghsa/ are all derived from V8 internals, and JavaScriptCore has not been audited against vm2's bridge.
What alternatives to vm2 does the readme recommend?
isolated-vm with separate V8 isolates, rated fast but in maintenance mode and needing manual V8 updates; a separate process or Worker thread, rated medium with higher IPC overhead; containers or VMs such as Docker, gVisor and Firecracker, rated slow; and managed services such as AWS Lambda or Cloudflare Workers, rated variable.
What is the difference between node:vm and vm2?
Against Node's own module, runInNewContext with this.constructor.constructor("return process")().exit() reaches the real process. Against vm2, the same expression under new VM().run throws ReferenceError: process is not defined.
When does the readme say vm2 is still the right choice?
When you need tight integration with host objects and fast synchronous communication, when the untrusted code comes from a relatively trusted source such as internal tools or plugins with vetted authors, when you combine it with other security layers, and when you accept the risk and monitor for updates.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/patriksimek-vm2)Star history chart for your README
[](https://hysenlabs.com/projects/patriksimek-vm2)Was this useful?