FastNetMon is a flow sensor that reacts by blackholing, and that is the design
Very fast DDoS sensor with sFlow/Netflow/IPFIX/SPAN support
At a glance
- What is it?
- pavel-odintsov/fastnetmon is the community edition of a denial-of-service detector that reads flow records or captures mirrored packets, matches them against thresholds, and then does something about it: notifying you, running a script, or announcing a route. The readme is a product page as much as a manual, and the capture-backend list is where the engineering detail sits. Nothing in it explains how the flow records are matched to thresholds, so a reader is left with the interface rather than the algorithm.
- Who is it for?
- FastNetMon Community suits a network operator who already has an upstream provider and wants detection plus a response they control, and who can accept the terms of a community edition maintained by a company selling a commercial one. It does not suit someone looking for an application-layer defence.
- Can I use it commercially?
- Yes, with conditions. GPL-2.0 is a copyleft licence: if you distribute software that includes it, you must release that software's source code under the same licence. Running it internally without distributing it does not trigger that obligation.
- Is it still maintained?
- Yes. The repository last received commits 12 days ago.
- What is it written in?
- Mainly C++, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 14, 2026, and from our analysis. They are not legal advice.
Star history
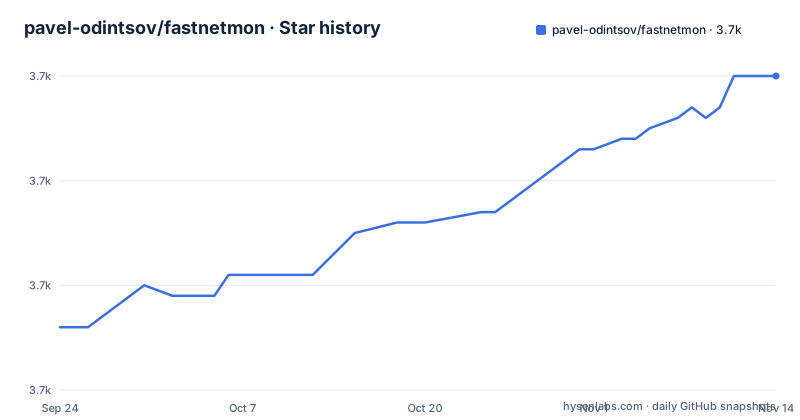
- pavel-odintsov/fastnetmon3,730 ★ · +24
| Repository | 2026-09-24 | 2026-11-14 |
|---|---|---|
| pavel-odintsov/fastnetmon | 3.7k | 3.7k |
24 Stars in the last 51 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Detection ends in an action, not an alert
The what-do-we-do paragraph is two sentences and both matter. It detects hosts in the deployed network that are sending or receiving large volumes of traffic, measured in packets, bytes or flows per second, and then performs a configurable action to handle that event. The configurable actions are listed as three: notifying you, calling a script, or making a border gateway announcements. That third option is the difference between this being a monitoring tool and this being a mitigation tool, and it is why the readme carries integration instructions for specific router vendors further down. A detector that can withdraw a route for an offending address is closer to an automatic firewall than to a dashboard.
Eight capture backends, two of them deprecated with conditions
The backend list is the most technical part of the readme and it is worth reading closely. It starts with three flow protocols: three versions of one flow export format, the internet protocol flow information export, and its own version five. Then packet capture from a file, and three live kernel interfaces, one of which is marked recommended and one of which is the newest, an eBPF-based one. Then two entries that have been deprecated rather than removed, each with the condition attached: a userspace capture interface supported only on one operating system, and a commercial ring-buffer product available only on a distribution release that is long out of support and only in a particular version of this project. So the list encodes not just what works but what the maintainers will accept bug reports about.
Thresholds can be per subnet, and attacks become routes
Two features determine whether the tool is usable in a real network rather than a lab. The first is that thresholds can be configured on a per-subnet basis through a host-group mechanism, which is the difference between a detector that fires on your biggest customer and one that fires on an anomaly. The second is route announcement, and the readme names the two supported implementations, marking one of them recommended. Both are open source routing daemons rather than features of a commercial switch, which means the announcement path is something you run rather than something you license. That is the integration point with the previous section: the sensor's output is a prefix, and the protocol that carries it is the thing to get right. Announcing a blocked address is only as fast as the routing protocol that carries the announcement, which is why the two supported implementations are named explicitly rather than left as an integration detail.
Where the data goes: metrics, flows, fingerprints, databases
The feature list covers output as well as detection, and it is long. Notifications by email about a detected attack. Metrics exposed in the Prometheus text format, covering both system metrics and total traffic counters. Flow and packet export to a message broker in two serialisations. An API. Integration with a document store, a time-series database and a graph database, all three named with links. Then two capture-side features that are easy to miss: VLAN untagging in mirror and flow modes, which matters if your mirror port carries tagged traffic, and the ability to capture attack fingerprints as packet files, which is what turns a detection into something you can hand to someone else. So the design assumes the detection is the start of an investigation rather than the end of it, and the fingerprint output is the hand-off point between the sensor and whoever reads the packet afterwards.
Three router plugins live in the source tree
There is a short section on router integration with separate instructions for one vendor's routing software, and then a claim of complete integration with three vendors, each linked to a plugin directory inside the source rather than to documentation. So unlike the route announcement feature, which is a protocol choice, the device integration is code, and the code is in the tree. That matters for anyone planning to run this: the plugin set is three vendors, and a fourth family of device is handled through the protocol route rather than through a plugin. The readme also separates the two by phrasing, calling one an integration and the other complete, which is a distinction worth preserving when you evaluate a device you already own.
The edition boundary is stated in the readme
Four of the links near the top exist to draw a line. There is an official site, a commercial edition, a free trial of that edition, and a table comparing the advanced and community editions. The legal section then states that installing or using the software constitutes agreeing to the community edition terms and a privacy notice, and that the project is a product of a company registered in the United Kingdom with a registered trademark. So the community edition is not a community fork that happens to be free; it is the free tier of a commercial product, which explains both the feature list stopping where it does and the presence of a privacy notice alongside the terms. It also means the terms are a dependency of the installation, not an optional read. The comparison table being hosted rather than reproduced is the other half of that arrangement: the boundary between the two editions is defined by the vendor and can move, which is worth remembering before building a monitoring workflow around a feature that might move across it.
Seven support channels and a usage-analytics disclosure
The support section lists a mailing list, a chat platform, an IRC channel over TLS with a web client, a messenger app, and a second chat platform, which is a lot of channels for one project and suggests an international user base with different preferences for where to ask questions. Above them there is a sentence that deserves more attention than it gets: the project tracks platform and environment specific metrics to understand how the product is being used and to prioritise development accordingly. That is a usage-analytics disclosure in the middle of a feature list, and it is the one line in the readme that tells you the free edition phones home. Whether that matters to you depends on your environment and your threat model, and the disclosure at least lets you decide.
Editorial conclusion
FastNetMon Community suits a network operator who already has an upstream provider and wants detection plus a response they control, and who can accept the terms of a community edition maintained by a company selling a commercial one. It does not suit someone looking for an application-layer defence. Before deploying, read the edition terms the installation itself is gated on, pick a capture backend from the list rather than the default, and confirm your router speaks one of the two supported route announcement protocols.
Frequently asked questions
is fastnetmon free
The readme is organised around an edition split: there is a community edition, which this repository is, and a commercial edition sold separately with a comparison table and a free one-month trial of it. Installing the community edition means agreeing to its terms and privacy notice, and the project states that it collects platform and environment specific usage metrics to understand how the product is used.
fastnetmon community vs advanced
The repository does not summarise the difference; it links a comparison table hosted by the vendor, alongside links to the commercial edition and its trial. What the community edition's own feature list shows is flow- and packet-based detection with configurable thresholds per subnet, script and notification responses, route announcement for blocked addresses, several metrics and database integrations, and eight packet capture backends of which two are deprecated with conditions attached.
fastnetmon alternative
No alternatives are named. What the readme offers instead is a detailed reference document, a comparison table of capture backends, and separate integration guides for the metrics, time-series and graph databases, the two supported route announcement implementations, and three router vendors.
What are the three main types of DDoS attacks?
The readme does not categorise attacks. What it describes is a detector that finds hosts sending or receiving large volumes measured in packets, bytes or flows per second, and reacts by notifying, calling a script, or announcing a route, with thresholds configurable per subnet.
What are layer 7 DDoS attacks?
That classification is not used here. Everything the project reads arrives as a flow record or as a captured packet, which places it in the volumetric and protocol-level category rather than the application layer, and the mitigation it performs is a routing decision rather than anything that inspects a request.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/pavel-odintsov-fastnetmon)Star history chart for your README
[](https://hysenlabs.com/projects/pavel-odintsov-fastnetmon)Was this useful?