Flame reads its app list off container labels and its secrets off a _FILE suffix
Flame is self-hosted startpage for your server. Easily manage your apps and bookmarks with built-in editors.
At a glance
- What is it?
- Flame is a self-hosted start page built on Node.js, Express, Sequelize and SQLite, which discovers applications from Docker labels or Kubernetes ingress annotations and overrides any environment variable with a _FILE suffix for Docker secrets. Its bookmark importer is marked experimental and tells you to back up db.sqlite first.
- Who is it for?
- Flame suits a home server or small cluster where services are already containers, because the application list comes from labels those containers already need and the UI is edited in the browser rather than in files. Without the Docker socket mounted, automatic discovery has to come from a remote Docker host over TCP or from Kubernetes ingress annotations, or apps are added by hand in the built-in editors.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 146 days ago.
- What is it written in?
- Mainly TypeScript, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 17, 2026, and from our analysis. They are not legal advice.
Star history
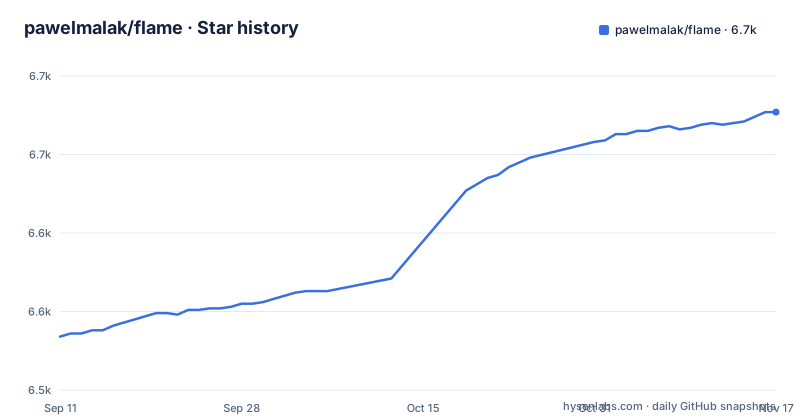
- pawelmalak/flame6,677 ★ · +143
| Repository | 2026-09-11 | 2026-11-17 |
|---|---|---|
| pawelmalak/flame | 6.5k | 6.7k |
143 Stars in the last 67 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Any environment variable can be replaced by a file with a _FILE suffix
Flame's secret handling has one rule and applies it to everything. Append _FILE to a variable name and the value is read from that path instead. PASSWORD is the worked example, and PASSWORD is also the only variable a plain docker run needs:
# run container
docker run -p 5005:5005 -v /path/to/data:/app/data -e PASSWORD=change_me pawelmalak/flame
With Compose the same password arrives as a secret file:
version: '3.6'

services:
  flame:
    image: pawelmalak/flame
    container_name: flame
    volumes:
      - /path/to/host/data:/app/data
      - /var/run/docker.sock:/var/run/docker.sock # optional but required for Docker integration
    ports:
      - 5005:5005
    secrets:
      - password # optional but required for (1)
    environment:
      - PASSWORD=change_me
      - PASSWORD_FILE=/run/secrets/password # optional but required for (1)
    restart: unless-stopped
The precedence rule is stated without hedging: if both PASSWORD and PASSWORD_FILE are set, the docker secret wins. The secret is defined in a top-level secrets block pointing at a file on the host.
docker-secret ^1.2.4 is a declared dependency in package.json. The cost of a blanket rule is that it applies to variables you may not have thought of as secret, and nothing in the repository enumerates which variables the app reads.
Port 5005 and /app/data are the two facts a deploy has to accept
Three images are published and they differ by tag rather than by name. A plain docker pull pawelmalak/flame gets the default architecture. A Raspberry Pi or other ARM board needs the multiarch tag, and pinning a version means appending that version to the image name:
docker pull pawelmalak/flame

# for ARM architecture (e.g. RaspberryPi)
docker pull pawelmalak/flame:multiarch

# installing specific version
docker pull pawelmalak/flame:2.0.0
The mapping is fixed in every example given: 5005 on the host to 5005 in the container, and a host directory mounted over /app/data. No environment variable in any snippet changes either one.
The compose file adds restart: unless-stopped, which the bare docker run does not, and the development route is a third path again: skaffold dev, against a skaffold.yaml that sits in the top-level tree next to server.js and api.js.
Building locally is where the first real constraint appears. The single-architecture build is one command, and the multiarch build is a buildx command over three platforms:
# build image for amd64 only
docker build -t flame -f .docker/Dockerfile .

# build multiarch image for amd64, armv7 and arm64
# building failed multiple times with 2GB memory usage limit so you might want to increase it
docker buildx build \
  --platform linux/arm/v7,linux/arm64,linux/amd64 \
  -f .docker/Dockerfile.multiarch \
  -t flame:multiarch .
That inline comment about failing repeatedly under a 2GB limit is the most honest sentence in the deployment instructions, and it applies to a developer building images, not to someone pulling one.
App discovery reads four labels off each container
The feature that makes Flame more than a bookmark page is metadata on other containers. Anything carrying the right labels appears in the app list without being typed in:
labels:
  - flame.type=application # "app" works too
  - flame.name=My container
  - flame.url=https://example.com
  - flame.icon=icon-name # optional, default is "docker"
# - flame.icon=custom to make changes in app. ie: custom icon upload
Three of the four are yours to choose; only flame.type is meaningful, and app works as well as application. flame.icon is the only one with a default, which is why the comment notes it falls back to the docker icon, and why a second commented line offers the value custom when you want to change an app icon from the interface instead.
Several apps can share one container by separating values with a semicolon, and the fields line up positionally:
labels:
  - flame.type=application
  - flame.name=First App;Second App
  - flame.url=https://example1.com;https://example2.com
  - flame.icon=icon-name1;icon-name2
One condition is not in the labels at all: the Use Docker API option has to be switched on in Settings before any of this is read. That setting is what turns a plain bookmark page into something that inspects your daemon.
The mount is the other half of the deal. The compose example carries /var/run/docker.sock into the container and marks it optional but required for Docker integration, which means the feature needs write access to the daemon socket, and nothing in the repository explains what that access permits.
A remote Docker host means editing the systemd unit to bind 0.0.0.0
Pointing Flame at a Docker daemon on another machine is done by changing how that daemon listens, not by adding a variable to Flame. The instructions say to open /lib/systemd/system/docker.service, find ExecStart and replace its value:
ExecStart=/usr/bin/dockerd -H tcp://0.0.0.0:${PORT} -H unix:///var/run/docker.sockThe daemon keeps the Unix socket and gains a TCP port at the same time, which is why both -H flags are in the line. Then the daemon has to be told to re-read the unit and restart:
sudo systemctl daemon-reload
sudo service docker restart
And the check is the version endpoint:
curl http://${IP}:${PORT}/versionThe documentation supplies its own gloss on the bind address: 0.0.0.0 means the engine accepts connections from all IP addresses. That is the whole security treatment of the procedure, with no host restriction, no port restriction and no credential step. Anyone following these steps on a machine reachable from elsewhere is opening the daemon to whoever can reach it, and the person writing the page chose that address rather than a specific interface.
Kubernetes discovery moves the same four fields to ingress annotations
The cluster integration is the label scheme with a different prefix and a different namespace. The fields become annotations on an ingress instead of labels on a container:
metadata:
  annotations:
  - flame.pawelmalak/type=application # "app" works too
  - flame.pawelmalak/name=My container
  - flame.pawelmalak/url=https://example.com
  - flame.pawelmalak/icon=icon-name # optional, default is "kubernetes"
Type, name, url and icon survive intact, including the app alias for type. Only the default icon changes, from docker to kubernetes, so an app discovered through the cluster does not look like one discovered through the daemon.
Both switches live in the same screen. Use Kubernetes Ingress API sits next to Use Docker API, and the README still files both of them under Settings, Docker.
package.json declares @kubernetes/client-node at ^0.15.1 as a dependency. What is not specified anywhere is whether Flame watches the cluster continuously or reads the ingresses once at start-up, and whether an annotation added after the container is up shows up without a restart.
One search bar, a prefix per engine, and a customQueries.json file
Flame ships 11 web search providers and lets you add more, with one integrated bar on top of local filtering across your own apps and bookmarks. The routing mechanism is a prefix typed before the query, so the engine is chosen by what you type rather than by a dropdown. A query about containers sent with the g prefix goes to that engine, everything else is filtered locally.
The place to extend that list is visible in the dev scripts. Creating the working directories also creates two empty files in public:
npx mkdirp data public && touch public/flame.css public/customQueries.jsoncustomQueries.json is the custom provider list, and flame.css is the custom stylesheet, both empty on a fresh checkout. The custom theme builder and the 15 built-in colour themes work through the same interface, and the styling pages live in the wiki rather than in the repository.
The weather widget is the one feature that needs an account elsewhere. It asks for an API key from the weather provider's pricing page, notes that the free plan allows 1M calls per month, and states that Flame makes fewer than 3K API calls per month. Location comes as latitude and longitude, which the instructions send you to a separate site to convert from an address, then paste in.
The bookmark importer is marked experimental and wants a db.sqlite backup
Importing browser bookmarks is the one part of Flame that reaches outside its own interface, and it is labelled experimental with two warnings attached. It needs python3 and two pip packages, Pillow and beautifulsoup4, and it writes into the same data directory the container mounts:
pip3 install Pillow, beautifulsoup4

cd flame/.dev
python3 bookmarks_importer.py --bookmarks <path to bookmarks.html> --data <path to flame data folder>
The warnings are specific. Back up your db.sqlite before running the script, and generated icons are sometimes incorrect.
The target path matters too. The data folder argument is the same /app/data the container mounts, so the script has to run somewhere that can see the host directory rather than inside the image.
Running outside Docker is a fourth route again: the non-Docker instructions are a single wiki link, with no command in the repository at all. For local work the four documented steps are a clone, npm run dev-init once, and npm run dev.
package.json claims ISC while the repository reports MIT
The licence of a self-hosted app matters more than most, because whoever deploys it ships it. The repository metadata reports MIT and LICENSE.md sits at the top level. Inside package.json the license field reads ISC, the version field reads 0.1.0 while the newest release is v2.4.0, and main points at index.js, a file that is not in the top-level listing where server.js is. The author field is empty.
None of that blocks a deployment. All of it means the packaged metadata does not describe the project you read about, and the two licence statements have not been reconciled.
The release cadence tells the other half of the story. v2.4.0 was published on 2026-04-24, v2.3.1 on 2023-07-23 and v2.3.0 on 2022-03-25, so the gap between 2.3.1 and 2.4.0 is close to three years. The last push to master was on 2026-06-25 and the repository is not archived, so work continued after that release. A gap of that size means a changelog entry and a diff are the only account of what changed, and CHANGELOG.md is in the tree for exactly that.
Editorial conclusion
Flame suits a home server or small cluster where services are already containers, because the application list comes from labels those containers already need and the UI is edited in the browser rather than in files. Without the Docker socket mounted, automatic discovery has to come from a remote Docker host over TCP or from Kubernetes ingress annotations, or apps are added by hand in the built-in editors. Before you rely on it, check four things: which port your reverse proxy expects against the fixed 5005 mapping, whether the build you pull matches the release you read about, what the ISC field in package.json means next to the MIT identifier in the repository metadata, and whether the database in /app/data is on storage you back up, because the bookmark importer tells you to copy db.sqlite by hand.
Frequently asked questions
How do I install Flame on my own server?
Pull the image and run it with the container port mapped to 5005, a host directory mounted over /app/data and a PASSWORD value set. For ARM boards such as a Raspberry Pi, pull the multiarch tag instead, and append a version number to the image name to pin a specific release.
How does Flame find applications without me adding them by hand?
It reads labels from your containers. Add flame.type=application, flame.name, flame.url and an optional flame.icon to a container, enable the Use Docker API option in Settings, and mount /var/run/docker.sock into the Flame container, which the compose example calls required for the Docker integration.
Can Flame keep its password out of the compose file?
Yes. Any environment variable can be overridden by appending _FILE to its name, so PASSWORD_FILE points at a secret mounted under /run/secrets. If both PASSWORD and PASSWORD_FILE are set, the docker secret takes precedence.
How do I add my own search engine to Flame?
The app ships 11 web search providers and creates an empty public/customQueries.json on a fresh checkout. A query typed with a prefix goes to that engine, and everything without a prefix is filtered locally across your apps and bookmarks.
Does Flame work with Kubernetes?
It reads ingress annotations rather than container labels, using the keys flame.pawelmalak/type, flame.pawelmalak/name, flame.pawelmalak/url and an optional flame.pawelmalak/icon. The Use Kubernetes Ingress API option must be enabled in Settings before the annotations are picked up.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/pawelmalak-flame)Star history chart for your README
[](https://hysenlabs.com/projects/pawelmalak-flame)Was this useful?