desloppify: a Production/Stable classifier, zero dependencies, and a lint gate of four rules
Agent harness to make your slop code well-engineered and beautiful.
At a glance
- What is it?
- desloppify is an agent harness that scores a codebase on quality and works through a fix queue. Its package declares no runtime dependencies and puts every language parser behind an extra, its classifier says Production/Stable while its own file says the work is not done, and its lint target installs packages and overwrites your git hooks before checking four rules.
- Who is it for?
- desloppify fits someone who wants an agent held to a numeric quality bar rather than a prose code review, and its anti-gaming design, where skipping an item widens the gap between two scores, is the part worth reading before the number itself. Verify four things first.
- Can I use it commercially?
- Check first. The repository uses a licence we do not classify automatically, so read its LICENSE file before any commercial use.
- Is it still maintained?
- Yes. The repository last received commits 19 days ago.
- What is it written in?
- Mainly Python, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
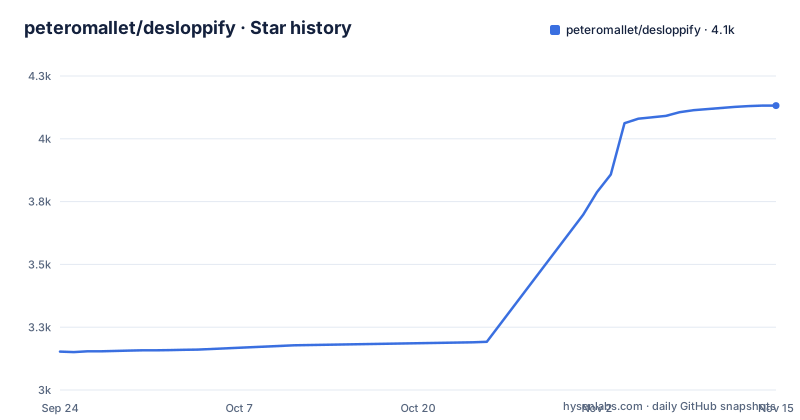
- peteromallet/desloppify4,132 ★ · +979
| Repository | 2026-09-24 | 2026-11-15 |
|---|---|---|
| peteromallet/desloppify | 3.2k | 4.1k |
979 Stars in the last 52 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The package declares zero dependencies and hides every parser behind an extra
The runtime dependency list is empty. That is not an oversight, it is a structure: five optional groups carry the actual work, tree-sitter and its language pack for parsing, a hardened XML parser for the C# path, a Python security scanner, an image library for generating the scorecard badge, and a YAML parser for plan files. A sixth group named full is the union of all five, and it is the one the installation instructions tell you to use. So the base install is a command line shell with nothing to parse, no image output and no security scan. Two details stand out. The language pack is the only dependency anywhere with an upper bound, capped below version 1.8 while every other requirement has a floor and no ceiling. And the C# support described as full plugin depth needs an extra the installation instructions never mention by name, since it arrives only as part of the union.
The classifier says Production/Stable and the file says the work is not done
The package metadata carries the development status classifier for Production/Stable. The README says the opposite in the same project: the effort to define what good looks like as a score is hard, they are not done, and the anti-gaming work matters more to them than anything else. Both statements ship together. Three descriptions of the same thing also coexist. The repository description calls it an agent harness for making code well engineered, the package description calls it a multi-language codebase health scanner and technical debt tracker, and the README heading calls it an agent harness again with a hand gesture emoji. Which of the three a user expects matters, because a scanner is something you run on demand and a harness is something an agent is pointed at with a workflow guide.
The lint target installs packages and overwrites your git hook to check four rules
The lint target depends on the tool-installation target, and that target depends on the hook-installation target. The hook target creates a git hooks directory if needed, copies the repository's pre-commit hook over the one there, and makes it executable. There is no backup and no prompt. So running the linter installs packages into whichever Python is first on your path, in editable mode, and replaces your existing pre-commit hook. What the linter then does is select four rule groups: a syntax-error class and three name and logic classes from the pyflakes set. That is not a style check. It is a minimum bar that catches code which cannot parse and names that do not resolve, which is a reasonable fast gate and a misleading name.
The architecture gate cannot run until you write the contracts it checks
One make target exists to enforce import boundaries, and it refuses to do anything until you have supplied the configuration. It checks for a file under the GitHub directory, and if that file is missing it prints a message telling you to add import contracts before running the gate, then exits with a status of one. So the architecture gate is opt-in in a literal sense: the contract file is not in the repository, and a fresh clone cannot run the target successfully. The tool it invokes is also resolved in an unusual way, by computing the path next to the Python interpreter rather than by searching the path for it, so the command only finds the linter if it was installed into the same environment as the interpreter running make. Both details are defensible and both are invisible until they bite.
Two test targets run the identical pytest command
There is a short test target and a full one, and the command each runs is the same pytest invocation. The only difference is which installation target runs first. The short one goes through the continuous integration tool set, which installs pytest, a type checker, a linter, an import linter, two packaging tools and a YAML library. The full one goes through a different set that installs the package with the full extra group plus pytest and the linter. That means the extra dependencies, including the tree-sitter parsers, the security scanner, the XML parser and the image library, are present for one target and absent for the other. A test run that passes under the short target is therefore not exercising the code paths that need those extras, and the repository does not document which tests belong to which target.
Documentation is copied into the package by a target that deletes first
There is a make target whose whole job is synchronising documentation into the installed package. It creates a directory inside the package tree, deletes every markdown file at the top level of that directory with a find invocation, and then copies the documentation directory's markdown files in. Two things follow. The package ships a duplicate of the documentation, so there are two copies to keep in step, and the only thing keeping them in step is a developer running this target. And the deletion step is unconditional, so a file placed in that directory by hand rather than through the copy is removed without warning. The directory name, global data, suggests the content is meant to be data rather than prose, but what lands there is the documentation. The tree also carries a separate development directory and an assets directory, the latter holding what the scorecard badge is rendered from.
The Java path shells out to PMD, and the threads default to zero
Most languages are handled by tree-sitter or by a generic linter, and the C# path has its own integration target in the build. Java is different again. The README notes that on constrained CI runners the PMD detector defaults to a thread count of zero to avoid fanning out worker threads, and that an environment variable can raise it to a value such as two or to a fraction of available cores. So the Java analysis is an external tool invoked by the harness rather than a parser it owns, it is the one language whose cost profile depends on the machine, and the tuning knob is spelled as a CPU fraction rather than an integer. Three separate execution models for language analysis in one tool is the design consequence of supporting twenty-nine of them.
The shipped CI job collects scores without enforcing any threshold
A complete workflow file is provided, and it is a good illustration of the intended shape:
name: desloppify

on:
  pull_request:
  push:
    branches: [main]

jobs:
  health:
    runs-on: ubuntu-latest
    steps:
      - uses: actions/checkout@v4
      - uses: actions/setup-python@v5
        with:
          python-version: "3.11"
      - run: pip install --upgrade "desloppify[full]"
      - run: desloppify scan --path . --profile ci --no-badge
      - run: desloppify status --json
The profile itself matters as much as the steps: it skips the slow and subjective phases and bypasses the mid-cycle queue gate so a job can collect a fresh mechanical snapshot, which is why the subjective half of the score is missing from continuous integration entirely. Two gaps are visible in the file itself. Only one Python version is exercised even though three are declared as supported. And nothing reads the JSON: the job prints the scores and finishes. The README says to use the status output if you want a script to enforce your own threshold, which means the value of the exercise is that you build the gate, not that the tool does.
Editorial conclusion
desloppify fits someone who wants an agent held to a numeric quality bar rather than a prose code review, and its anti-gaming design, where skipping an item widens the gap between two scores, is the part worth reading before the number itself. Verify four things first. Expect to install an extra set rather than the package, since the base install carries no language parser at all. Check the licence yourself, because the manifest carries a non-standard identifier as free text, the repository's own licence field is empty, and there is a licence file in the tree. Read the Makefile before running any target, because the lint target installs packages into your current environment and copies a hook over the one in your git directory. And treat the score as a signal rather than a gate, since the shipped continuous integration job collects the numbers without enforcing a threshold.
Frequently asked questions
What is peteromallet/desloppify?
A harness that gives an AI coding agent tools to identify and improve codebase quality. It combines mechanical detection of dead code, duplication and complexity with LLM review of naming, abstractions and module boundaries, then works through a prioritised fix loop. State persists in a local directory so progress carries across sessions, and it supports twenty-nine languages.
What do I have to install to run desloppify?
The instructions are to install the package with its full extra group, which pulls in a tree-sitter parser pack, a hardened XML parser, a Python security scanner, an image library and a YAML parser. The base package itself declares no runtime dependencies at all, so without the extras there is nothing to parse code with.
How does desloppify stop its score from being gamed?
Two mechanisms are described. Items marked as wontfix widen the gap between the lenient and the strict score, so dismissing a finding costs you. And re-reviewing a dimension can lower its score if the reviewer finds new issues, so a second look is not automatically a higher number.
Does desloppify support incremental or diff-only scanning?
Not as a supported model yet, and the README says so plainly. The recommended approach is to compare full-codebase results across runs or to enforce a project-level threshold, and for a repository with several programs, to run one job or matrix entry per project path.
What licence is desloppify under?
The package manifest declares the identifier OSNL-0.2 as free text rather than as a recognised expression, the repository's own licence field is empty, and a licence file is present in the tree. Read that file directly to see the terms before using the tool or its output.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/peteromallet-desloppify)Star history chart for your README
[](https://hysenlabs.com/projects/peteromallet-desloppify)Was this useful?