Password Pusher: expiry by views, an unbranded delivery page, and a master key you own
🔐 Securely share sensitive information with automatic expiration & deletion after a set number of views or duration. Track who, what and when with full audit logs.
At a glance
- What is it?
- An Apache licensed web app for handing out one-time links to passwords, notes, files and URLs, where the payload is deleted when it expires. The deployment detail that decides whether your instance is safe is a single encryption key variable in the compose file.
- Who is it for?
- Use Password Pusher to share a secret through a link with configurable expiry and an access audit trail. The trail can show access metadata, but it does not by itself prove which person viewed the secret.
- Can I use it commercially?
- Yes. Apache-2.0 is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 2 days ago.
- What is it written in?
- Mainly Ruby, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
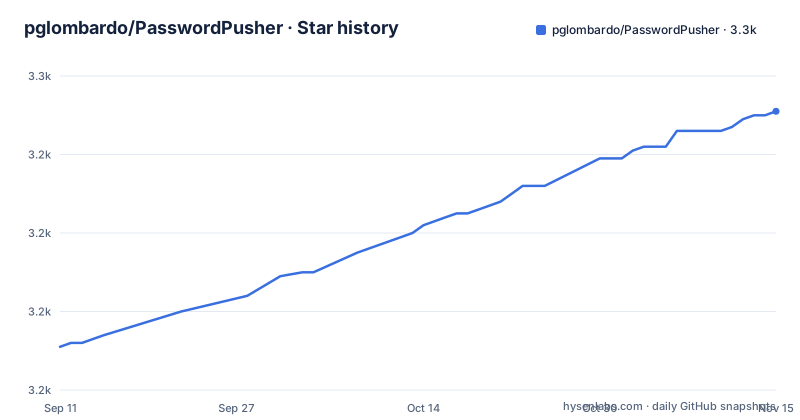
- pglombardo/PasswordPusher3,251 ★ · +60
| Repository | 2026-09-11 | 2026-11-15 |
|---|---|---|
| pglombardo/PasswordPusher | 3.2k | 3.3k |
60 Stars in the last 65 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
One link, one expiry, and then nothing
The mechanism is simple enough to describe in one sentence, which is why the project works.
You push a password, a note, a file or a URL. The recipient gets a link that expires after a configured number of views, a set duration, or both. It is one-time only when configured for one view. The project states that sensitive push data is deleted on expiration; self-hosters should also account for any backups and retention policies they control.
The privacy properties around that are the ones to look at. Storage is encrypted, expiry can be limited by views and by time together, and a link can require a passphrase, which moves the barrier from possession of the URL to knowledge of a second secret.
The delivery page is described as unbranded: no logos, no superfluous text, and no unrelated links. That is a security decision disguised as a design one. The person following your link is being asked to trust a stranger's infrastructure, so the page does nothing to make them trust you or anyone else, and it gives an attacker who ends up on the wrong URL nothing to click.
It also supports an optional preview step, so a recipient can see metadata about what is being shared before revealing the content.
The audit log is the reason to self-host
For logged-in creators, the project provides an audit log for each push. It can record access metadata such as time, IP address and user agent, but those signals do not prove a human viewer’s identity: proxies and automated link scanners can also appear in the log. The optional retrieval step can help protect the view count from scanners; test the behaviour in your deployment.
The interface to that data is an API rather than the web page. A JSON API version two covers the workflows that matter: creating a push, retrieving one, reading the audit trail, listing active pushes and listing expired ones. And the older style routes for pushes, files and retrievals are still there, described as legacy compatibility, so an integration written against the first version of the API keeps working rather than breaking on upgrade.
There is also an official command line client and a browser extension, plus third party integrations, so the tool does not require you to use its own web page.
PWPUSH_MASTER_KEY decides who can read your database
The compose file is the best documentation in the repository, because it explains each setting and says what happens if you skip it.
Two settings are called out in its own comments as the important ones. The TLS domain setting enables automatic provisioning and renewal of HTTPS certificates through Let's Encrypt, and is described as strongly recommended. The master key setting is the encryption key for the database, and if you omit it a default key is used.
That second point is the one to read twice. The default is convenient and it means your payloads are encrypted with a key that is not yours. The comments recommend generating your own and setting it so encrypted pushes use your key.
There is a rotation path as well: old keys go into a comma-separated previous-key variable, which is how you change the key without making existing pushes unreadable.
Two more details are easy to miss. Configuration can come from environment variables or from an external dotenv file, whichever you prefer, and any of them can instead be read from a Docker secret file rather than passed as a value. And mail settings are required for account emails and logins, so an instance without them is an instance without logins.
MFA can be required across the whole instance
Two factor authentication is supported with time-based one-time passwords from authenticator apps, plus backup codes.
The setting that matters for a shared instance is the one that makes it mandatory: an administrator can require MFA instance-wide with a single environment variable rather than leaving it to each user to turn on.
That is the difference between offering the feature and relying on it. An instance where everyone can log in with a password until they feel like adding a second factor is an instance whose audit trail is only as strong as its weakest account. Requiring it centrally removes that choice.
Backup codes are mentioned alongside the authenticator apps, which is the right pairing: the codes are what you use when the second factor stops working, and a deployment that generates them and loses them has locked its administrators out rather than secured them.
The rest of the instance surface is equally practical: an admin dashboard for managing the instance, a database for persistence or a stateless mode with no database at all, and the ability to white label the site with your own theme, logo and site name.
Two editions, and features move from one to the other
The project runs on a two edition model and is explicit about the difference.
The open source edition is this repository. You can self-host it, or you can use a hosted demonstration instance the project publishes for evaluation. The Pro edition is the hosted service, which has extra features, and the project states that Pro features are periodically migrated into the open source edition. There is a feature comparison matrix on the hosted site.
The host side is two commands:
docker compose up -dThat last point is unusual and worth noting in both directions. It means the open source edition is not frozen while the paid one moves ahead; it means improvements arrive, on a delay. For self-hosting, the practical question is not whether you can get a feature today, but whether you would rather wait for it or pay.
Self-hosted Pro is also now offered, with licensing, which closes the gap for people who cannot send their secrets to somebody else's infrastructure.
The release titles are a good proxy for what is actually changing. The most recent three describe passphrases with random passwords and PIN generation, a refined dark theme, and dependency plus security updates. That is a project shipping user-visible changes and maintenance in the same cadence rather than one or the other.
The theme pipeline is Node, the application is Ruby
The repository is a Ruby application with a small JavaScript toolchain attached, and the toolchain exists for styling.
The package manifest is private and its dependencies are the styling stack: a CSS framework, its icon set, a flag icon set, a popper library, autoprefixer, PostCSS with its command line wrapper, and the Sass compiler. Nodemon is there for watching. That is a build-time asset pipeline and not an application framework, which is the honest reading of a Node manifest in a Rails project.
The scripts confirm it. One sets the theme by running a script at the repository root. Two build stylesheets, one for a single theme and one for all of them. And a watch mode that watches two stylesheet directories, deliberately ignores the selected theme partial, and reruns the single-theme build through the package manager.
Theme selection is where the white labelling comes from. Twenty-six themes are available, chosen through environment variables rather than by editing files, and light or dark follows the system preference. There is also a separate document about themes, and a script that sets one.
The toolchain is pinned in two places, which is unusual: the Node engine is declared, and the package manager itself is pinned to a specific version with an integrity hash in the manifest.
Deployment targets are already in the repository
The list of platform configuration files at the top level is longer than most projects of this age carry, and it tells you where the maintainers expect people to run this.
There is a configuration file for a container platform, one for a railway hosting service, and one for a render style host. There is a Heroku style application manifest, and two Procfile variants, one for production and one for development. There is a directory for one more cloud provider, a directory for container platform manifests, and a chart testing configuration for the Helm chart. And there is a devcontainer definition for people working on the code itself.
The linting story has the same character. There are separate configurations for the Ruby linter, for the template linter, a pre-commit configuration, and an overcommit configuration, which is three overlapping systems for the same job. That is not a criticism so much as a record of a project that has grown up with whatever was available.
The documentation files at the root are the ones to read before deploying: a configuration reference, a themes document, an upgrade guide for the second major version with migration notes, a release document, a security policy, and a version file.
Editorial conclusion
Use Password Pusher to share a secret through a link with configurable expiry and an access audit trail. The trail can show access metadata, but it does not by itself prove which person viewed the secret. It suits a small team with a domain and a server, and the compose file is a credible production path rather than a demo. Skip it if your real problem is a password manager, because it is not one, and skip the hosted service if your threat model does not allow a third party holding the payload. Before you deploy, generate your own master key rather than running on the default one, set the TLS domain so certificates are provisioned automatically, and read the configuration document, because those two settings are the difference between an encrypted instance and an encrypted instance you control.
Frequently asked questions
what is password pusher
An open source web app for sharing sensitive information via a link. A push can expire after a configured number of views and/or a set time; it is only one-time if configured for one view. The project states that sensitive data is deleted when a push expires.
Is password pusher safe?
The project describes encrypted storage, configurable expiry, optional passphrases, account MFA and access audit logs. Audit metadata such as IP addresses and user agents does not reliably establish a viewer’s identity, and link scanners can consume views. Assess the deployment, key management and threat model before sharing secrets.
Is password pusher free?
The repository is Apache 2.0 and you can self-host it with Docker Compose, Kubernetes or Helm. There is also a hosted service and a paid Pro edition with extra features, and self-hosted Pro is available under a licence, with Pro features periodically migrated into the open source edition.
how to use password pusher
Point a DNS record at your server, then in the compose file uncomment and set the TLS domain for automatic certificates and optionally your own master key, and run docker compose up -d. If you set no TLS domain you can uncomment port 5100 and reach the application over plain HTTP.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/pglombardo-passwordpusher)Star history chart for your README
[](https://hysenlabs.com/projects/pglombardo-passwordpusher)Was this useful?