PoWFaucet: a faucet whose mining module protects, not mints
Modularized faucet for EVM chains with different protection methods (Captcha, Mining, IP, Mainnet Balance, Gitcoin Passport and more)
At a glance
- What is it?
- A modularized EVM faucet whose protection methods are captcha, proof-of-work, IP, mainnet balance and Gitcoin Passport, deployed as nginx in front of a Node server. The proof-of-work it is known for is a bot tax on requests, not coin generation, and the operator funds the wallet by hand.
- Who is it for?
- PoWFaucet fits a chain team or a community that already has testnet funds to distribute and wants a faucet that bots cannot drain in one sitting. It does not fit anyone expecting it to create tokens.
- Can I use it commercially?
- Yes, with strict conditions. AGPL-3.0 is a network copyleft licence: if people use a modified version over a network, for example as a hosted service, you must offer them its source code under the same licence.
- Is it still maintained?
- Yes. The repository last received commits 1 day ago.
- What is it written in?
- Mainly TypeScript, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
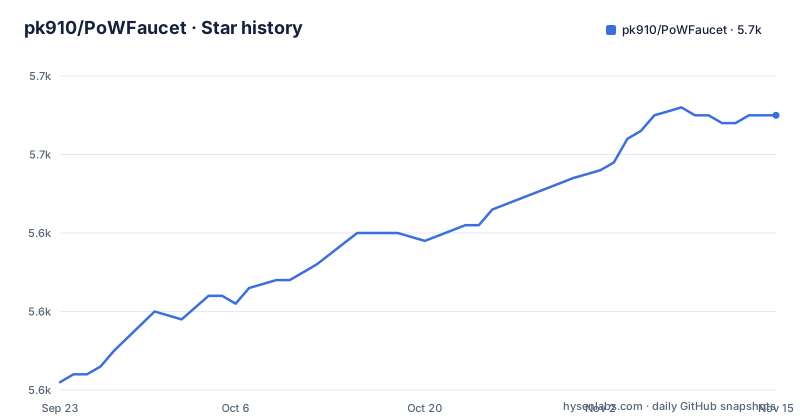
- pk910/PoWFaucet5,655 ★ · +34
| Repository | 2026-09-23 | 2026-11-15 |
|---|---|---|
| pk910/PoWFaucet | 5.6k | 5.7k |
34 Stars in the last 53 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The mining module is a tax on requests, not a mint
The first thing to clear up is the one the project itself clears up. PoWFaucet does not generate new coins with the mining process. The module named Mining is one of the protection methods the faucet uses to prevent anyone from requesting a big amount of funds and draining the faucet wallet, and the word survives in the module list only as a name for that defence. Everything else in the project follows from this. The stated problem is that faucets for ETH testnets are spammed by bots, and the project's aim is to reduce the efficiency of those automated requests by various protection methods. Proof-of-work is the method it is mostly known for, described in the project's own words as currently the best and most reliable way to distribute funds on a network that got low on fund reserves. The cost is paid by the requester in compute time rather than by the chain in newly issued coins.
One wallet address serves all three public instances
The instance table is where the funding model becomes concrete. Three testnets are listed: Sepolia at sepolia-faucet.pk910.de, Hoodi at hoodi-faucet.pk910.de and Ephemery at ephemery-faucet.pk910.de, each with an uptime status link and a block explorer link for the same address, 0x6Cc9397c3B38739daCbfaA68EaD5F5D77Ba5F455. The explorer differs per chain, etherscan.io for the two Ethereum chains and explorer.ephemery.dev for Ephemery, but the address does not. So the three public faucets are one funded wallet reached through three front doors, which is exactly the arrangement that makes draining it attractive, and the reason the protection modules exist. It also means the operator funds it manually: to run your own instance you have to transfer the funds you want to distribute to the faucet wallet yourself. There is no minting, no replenishment and no subscription behind the balance.
The protections are modules you pick between
Modularity is the project's name for its design, and it shows in the module list: Captcha, Mining, IP, Mainnet Balance, Gitcoin Passport, and more. Each entry is a gate that a request has to clear before funds move, and the project says it is known for the proof-of-work one specifically. The cost of that design is that the root page is not the documentation. A detailed description lives in the Project Wiki, the installation and configuration instructions live in a separate Faucet Operator Wiki, and the combinations are shown rather than enumerated: a set of demo instances with different module combinations is linked under docs/demo/README.md.
Five environment variables stand in for the secrets
Configuration is a YAML file, but secrets do not have to live in it. The project states that secrets can be injected at runtime instead of being stored in faucet-config.yaml, and the local examples name five: FAUCET_SECRET, FAUCET_ETH_WALLET_KEY, FAUCET_CAPTCHA_SECRET, FAUCET_GITHUB_APP_SECRET and FAUCET_PASSPORT_SCORER_API_KEY. The names map onto the module list more or less one for one, which is how you can tell what a given deployment is gating on without reading the source: a captcha secret implies the Captcha module, a GitHub App secret implies a GitHub-linked check, and a Passport scorer API key implies the Gitcoin Passport module. The key that moves funds, FAUCET_ETH_WALLET_KEY, is in the same list, so the wallet credential can arrive from the process environment at start rather than from a file on disk. Everything that is not a secret, such as which modules are on, still belongs in the config file, and faucet-config.example.yaml is the template that ships in the package.
The image is nginx with a node binary copied in
The Dockerfile explains the deployment shape without needing any prose. The final stage is nginx-unprivileged 1.30, and the Node runtime is not installed as a package but copied straight out of the official node:24-slim image:
FROM nginxinc/nginx-unprivileged:1.30
USER root
COPY --from=node:24-slim /usr/local/bin/node /usr/local/bin/node
WORKDIR /app
COPY --from=build-server-env /build/bundle ./bundle
COPY --from=build-client-env /build/static ./static
COPY ./faucet-config.example.yaml .
COPY ./docker/nginx.conf /etc/nginx/conf.d/default.conf
COPY --chmod=755 ./docker/entrypoint.sh /entrypoint.sh
USER nginx
WORKDIR /data
EXPOSE 8080
ENTRYPOINT [ "/entrypoint.sh" ]
Two processes live in that image: nginx serves the static files and proxies /api/ and /ws/ to the Node backend, so the WebSocket path and the API path are both handled by the same entrypoint. The working directory at start is /data, created during the build and left world-writable for config, database and other runtime files, which means the container expects to be mounted with somewhere to keep its state. There is also a second copy of the front page, index.seo.html, produced from index.html and left writable.
The package exposes a server, a bundle and an SDK
The manifest is where the modularity shows up in code. The package is @powfaucet/server at version 2.6.0, marked as an ES module, with dist/app.js as its main entry and a powfaucet bin pointing at a webpack bundle:
{
  "name": "@powfaucet/server",
  "version": "2.6.0",
  "main": "dist/app.js",
  "bin": {
    "powfaucet": "bundle/powfaucet.cjs"
  },
  "type": "module",
  "license": "AGPL-3.0"
}
Three subpath exports sit beside the root export: ./sdk, ./sdk/module and ./sdk/testing, each pairing a runtime file under dist with its own type declarations under sdk-dist, and the published file list includes sdk-dist alongside dist, bundle, static, libs and the example config. That arrangement is what lets a protection module be built and tested on its own instead of only inside a running faucet. The build scripts match it: build runs tsc and then copies modules into dist, sdk compiles a separate tsconfig.sdk.json, and bundle runs webpack in production mode before the same copy step.
A Dev Snapshot tag sits next to the 2.5.x releases
The release list mixes conventional versions with a snapshot. v2.5.1 is dated 2026-07-30 and v2.5.2 is dated 2026-10-13, and after them there is a release named snapshot, labelled Dev Snapshot, dated 2026-10-28. The repository is not archived, the default branch is master, and the last push is dated 2026-11-01, four days after that snapshot. For a service that holds a wallet balance, that distinction decides what you deploy: a patch version is a state someone cut deliberately, and a Dev Snapshot is whatever the branch held on a particular afternoon. The licence is AGPL-3.0, SECURITY.md sits at the root, and bugs and features are taken as pull requests. Testing is a separate script that compiles tsconfig.test.json into dist-test, copies libs and static beside it, and runs mocha with --experimental-vm-modules, with .mocharc.json and two coverage configs for the instrumented runs.
Editorial conclusion
PoWFaucet fits a chain team or a community that already has testnet funds to distribute and wants a faucet that bots cannot drain in one sitting. It does not fit anyone expecting it to create tokens. Before you run an instance, read the Operator Wiki, decide which protection modules you will enable and which secrets each one needs, fund the wallet yourself, and pin a tagged version rather than the Dev Snapshot if the balance in that wallet matters to you.
Frequently asked questions
What is PoWFaucet and what is its proof-of-work for?
It is a modularized faucet for EVM chains whose protection methods include Captcha, Mining, IP, Mainnet Balance and Gitcoin Passport. The mining module does not generate coins: it is one of the protections used to stop anyone requesting a large amount of funds and draining the faucet wallet.
Where do I install and configure PoWFaucet myself?
The installation and configuration instructions are in the Faucet Operator Wiki rather than in the repository README, and a set of demo instances with different module combinations is listed in docs/demo/README.md. Secrets can be injected at runtime instead of being stored in faucet-config.yaml.
Which testnet faucets are running on PoWFaucet?
The README lists instances for the Sepolia, Hoodi and Ephemery testnets, at sepolia-faucet.pk910.de, hoodi-faucet.pk910.de and ephemery-faucet.pk910.de. All three point at the same faucet wallet address, 0x6Cc9397c3B38739daCbfaA68EaD5F5D77Ba5F455, with a block explorer link for each chain.
What do I have to put in the wallet before a PoWFaucet instance pays out?
You have to transfer the funds you want to distribute to the faucet wallet yourself, because the faucet does not create coins. The wallet key can arrive from the environment as FAUCET_ETH_WALLET_KEY instead of being stored in faucet-config.yaml.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/pk910-powfaucet)Star history chart for your README
[](https://hysenlabs.com/projects/pk910-powfaucet)Was this useful?