PocketPaw: the package is 0.4.18 and every desktop download is 0.1.3
Your AI agent in 30 seconds. Not 30 hours. Self-hosted, open-source personal AI with desktop installer, multi-agent Command Center(Deep Work), and 7-layer security. Anthropic, OpenAI, or Ollama.
At a glance
- What is it?
- A self-hosted personal AI agent with five install paths, a native desktop app, a Docker image and four chat connectors, wrapping six selectable agent backends. The changelog is a comment on the first line of pyproject.toml and it stopped in April 2026, five months before the last commit.
- Who is it for?
- PocketPaw suits someone who wants an agent they can reach over Discord, Slack, WhatsApp or Telegram, running on their own hardware, and who is comfortable with a container image that ships two third-party agent CLIs and with pinning the images themselves. It does not suit anyone who needs a reproducible deployment out of the box, because all three compose services track `latest` and the resource limits assume an 8 GB machine.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository received new commits within the last day.
- What is it written in?
- Mainly Python, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 21, 2026, and from our analysis. They are not legal advice.
Star history
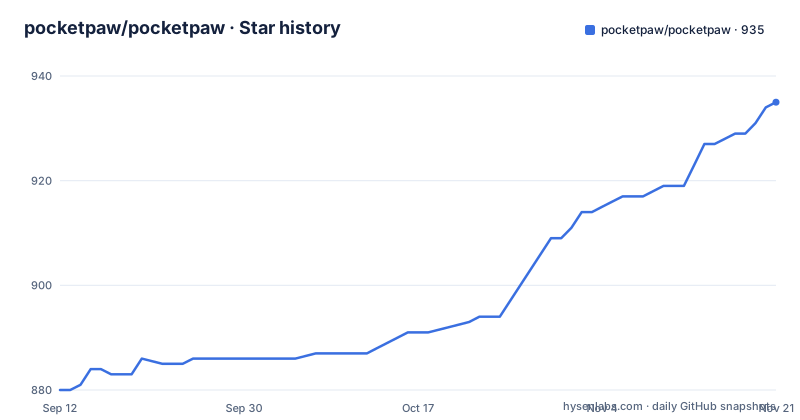
- pocketpaw/pocketpaw935 ★ · +55
| Repository | 2026-09-12 | 2026-11-21 |
|---|---|---|
| pocketpaw/pocketpaw | 880 | 935 |
55 Stars in the last 70 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The package line and the desktop line have unrelated numbers
Every desktop download link points at a tag called `client-v0.1.3` and a filename carrying 0.1.3, across all five platforms: the Windows x64 setup executable, the macOS Apple Silicon dmg, the macOS Intel dmg, the Linux amd64 deb and the Linux amd64 AppImage. The Python package is at a different line entirely. The manifest declares:
name = "pocketpaw"
version = "0.4.18"
requires-python = ">=3.11"
and the three most recent releases are v0.4.18, v0.4.16 and v0.4.15, all on the Python line. So one repository carries two products with two version schemes and one shared releases stream, and the desktop app is three minor versions behind the backend it ships. There is also a gap on the Python line itself: the newest tag is from 2026-04-29 while the default branch was pushed on 2026-10-02, so roughly five months of commits exist on main that no release covers.
The changelog is a comment on line one of pyproject.toml
There is no changelog file in the root listing. The release history lives as the first line of the build manifest, a comment dated 2026-04-29 and headed with the release number:
# Updated: 2026-04-29, Release 0.4.18: dev to main sync (PR #1015)The rest of that same line enumerates what the release contained: a file jail with OCR and speech to text, scope enforcement with a fail-closed `require_scope`, SSRF guard scaffolding, PII tightening, a rate limiter race fix with ReDoS bounds, audit log scrubbing, a dynamic cookie Secure flag, a nonce-based CSP, and two leakage fixes for bus mutation and token usage propagation. That is a substantial list for one release and it is the whole recorded history in the repository. It also stopped at the same moment the releases stopped, so the five months of work since April are documented nowhere in the tree. The security-relevant items on that one line are the reason the file exists at all, since a reader auditing the project's history has to read a source comment.
The container installs Claude Code and Codex as global npm packages
The Dockerfile has three stages, and the first one exists only to vendor two external CLIs. It starts `FROM node:22.14.0-slim`, with a comment explaining that Node is copied from the official image instead of being fetched with curl and bash from NodeSource, and then runs `npm install -g @anthropic-ai/claude-code @openai/codex`. The runtime stage copies `node` and the global `node_modules` directory out of that stage by hand and symlinks `npm` and `npx`. So a container presented as self-hosted, with the claim that your data stays on your machine, ships two third-party agent command line tools as globally installed npm packages. That is a deliberate design, since the agent backend is selectable and includes `codex_cli` among its options, but it means the container's contents depend on two npm packages resolved at build time rather than on anything in this repository. The builder stage is `python:3.12-slim` and installs the `all` extra, then runs `playwright install chromium`.
Three services, all tracking latest, two publishing ports to the host
The compose file defines the agent plus two optional services, and every image is unpinned:
  ollama:
    image: ollama/ollama:latest
    ports:
      - "11434:11434"
  qdrant:
    image: qdrant/qdrant:latest
    ports:
      - "6333:6333"
Two things follow. A `docker compose pull` changes what runs, with no version to record and no way to tell afterwards which build you had, and `restart: unless-stopped` on all three means an unattended host drifts without anyone noticing. And both sidecar ports are published to the host interface rather than left on the compose network, so a local model server on 11434 and a vector database for mem0 semantic memory on 6333 are reachable from anything that can route to the machine. The main service is better behaved on that point, publishing only `${POCKETPAW_PORT:-8888}:8888`. It does declare real resource envelopes, a 2 GB memory and 2 CPU reservation against an 8 GB and 4 CPU limit, and the env file is marked optional rather than required.
Six agent backends and six provider values behind one auto default
The environment sample lists more than the description advertises. The project description names three providers, Anthropic, OpenAI or Ollama, but the provider setting accepts six values: `auto`, `ollama`, `openai`, `anthropic`, `gemini` and `openai_compatible`. Defaults are written into the sample for two of them, `claude-sonnet-4-6` for Anthropic and `gpt-4o` for OpenAI, with `llama3.2` for Ollama. The agent backend is a second, separate axis, and it is where the six-count is more surprising:
POCKETPAW_AGENT_BACKEND=claude_agent_sdkwith the documented alternatives `openai_agents`, `google_adk`, `codex_cli`, `opencode` and `copilot_sdk`. So the runtime choice is which agent framework drives the loop, not which model answers, and those two decisions are configured independently. Every variable in the file carries the `POCKETPAW_` prefix. The Ollama host defaults to the compose service name rather than localhost, with a comment to use the service name in Docker, and the documented override for a host-installed Ollama is `host.docker.internal`, which is why the compose file adds that host mapping.
Slack needs two tokens, Discord needs three allowlists
The allowlist model is different on every connector, which is worth knowing before you expose any of them. Telegram takes a bot token and an allowed user id, the simplest shape. Discord takes a bot token plus three separate allowlists for guilds, users and channels, plus a conversation mode flag that defaults to false and an exclusion list for channels, so six settings in total. Slack takes two tokens, one prefixed `xoxb-` for the bot and one prefixed `xapp-` for Socket Mode, plus an allowed channel list. WhatsApp has two modes rather than one, personal by QR scan or business through the Cloud API, and the two business-only variables are marked as such. The asymmetry is not documented as a design decision, it is simply four integrations written at different times, and it means the security posture of each channel is configured on its own terms.
The recorded homepage is plain HTTP while every script is HTTPS
The repository's homepage field is `http://pocketpaw.xyz/`, with no scheme upgrade, and that is the address a directory listing or a package index will show. Every command that fetches something from the same domain uses HTTPS. The shell installer is `curl -fsSL https://pocketpaw.xyz/install.sh | sh`, and the Windows one is `powershell -NoExit -Command "iwr -useb https://pocketpaw.xyz/install.ps1 | iex"`. So the two entry points that matter most run code fetched over TLS with no checksum and no signature, and neither is mentioned as a caveat. The other install routes are quieter. `pip install pocketpaw && pocketpaw` goes through the package index, `pipx install pocketpaw` is isolated, `uvx pocketpaw` runs without installing at all, and the from-source path is `git clone` followed by `uv run pocketpaw`, with a `uv.lock` committed and a `.python-version` file pinning the development interpreter.
UNHEALTHY on first run is expected, and Windows leans on WSL2
Two expectations are set before anything else works, and both are stated as normal. The first is the health check: after opening the dashboard the system may report UNHEALTHY, and the note says this is expected until at least one model provider is configured, that the app itself is running correctly and that only the AI features are disabled. Fixing it means opening Settings and API Keys and adding one provider, or pointing at Ollama. The second is the platform boundary. Browser automation and shell tools are said to work best under WSL2, with native Windows support covering the web dashboard and all LLM chat features. That is a narrower promise on Windows than on Linux or macOS, and it is the one place where the desktop app's cross-platform framing meets a real limitation. The Windows troubleshooting path is thorough about the other failure, giving the exact error string when the command is not recognised and a way to print the Scripts directory path with `sysconfig`.
Editorial conclusion
PocketPaw suits someone who wants an agent they can reach over Discord, Slack, WhatsApp or Telegram, running on their own hardware, and who is comfortable with a container image that ships two third-party agent CLIs and with pinning the images themselves. It does not suit anyone who needs a reproducible deployment out of the box, because all three compose services track `latest` and the resource limits assume an 8 GB machine. Check four things first. Check that the Ollama and Qdrant ports are acceptable on your host, since both are published to the host interface by default rather than kept inside the compose network. Check your memory, because the service declares a 2 GB reservation and an 8 GB ceiling. Check which agent backend you actually want, since six are selectable and the default is Anthropic's SDK. And check the version you are reading about, since the Python package and the desktop app carry unrelated numbers. The licence is MIT and the classifier marks it beta, with a warning to expect breaking changes between versions. The default branch was pushed on 2026-10-02.
Frequently asked questions
How do I install PocketPaw?
There are several routes. With Python 3.11 or newer, pip install pocketpaw and then run pocketpaw, optionally inside a venv. There is also pipx for an isolated install, uvx to run without installing, git clone with uv run, a curl script piped to sh, a PowerShell one-liner on Windows, docker compose up -d, and native desktop builds for Windows, macOS on Apple Silicon and Intel, and Linux as a deb or an AppImage.
Does PocketPaw need an API key to work?
At least one model provider has to be configured before the dashboard stops reporting UNHEALTHY, and the README says that status on first run means the app is fine and only the AI features are off. You can add a key under Settings and API Keys, or run a local model by starting the ollama compose profile.
Where does PocketPaw store its data?
In a named volume mounted at /home/pocketpaw/.pocketpaw, with agent-created files from the Write and Bash tools landing in ./workspace on the host. The dashboard listens on port 8888 by default and the access token can be read out of /home/pocketpaw/.pocketpaw/access_token inside the container.
Which agent backends does PocketPaw support?
Six, chosen with the agent backend setting: claude_agent_sdk as the default, plus openai_agents, google_adk, codex_cli, opencode and copilot_sdk. The container image installs the Claude Code and Codex command line tools globally with npm to back two of those choices.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/pocketpaw-pocketpaw)Star history chart for your README
[](https://hysenlabs.com/projects/pocketpaw-pocketpaw)Was this useful?