Magic's 60-second install pipes a remote compose file and hands you root on a published port
Instant SECURE Full Stack Apps and AI Agents
At a glance
- What is it?
- A .NET-based platform that generates a database, a secured API and a frontend from plain English on your own hardware, with an MCP plugin that exposes every endpoint as a tool. The one-line install fetches a compose file from the project website and pulls two floating image tags, the first-run credential is written on the page, and the performance and token-saving figures arrive without a method.
- Who is it for?
- This is worth evaluating if you want a self-hosted backend rather than a frontend paired with someone else's service, because the deploy-step argument is the one row in its comparison table you can verify yourself in an afternoon. Three things to check before you run it anywhere real.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository received new commits within the last day.
- What is it written in?
- Mainly C#, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
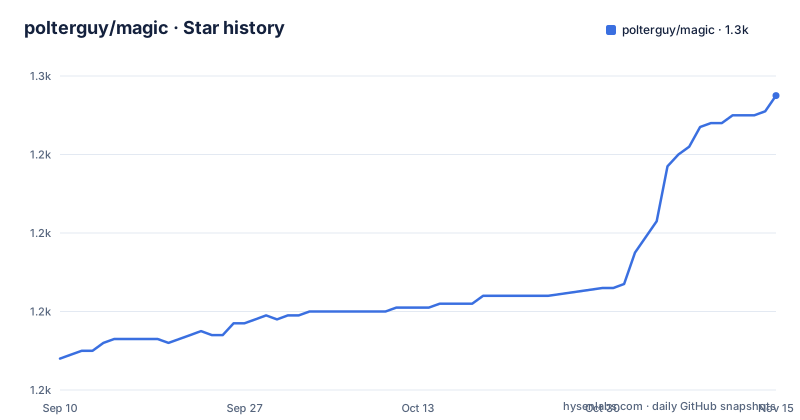
- polterguy/magic1,255 ★ · +67
| Repository | 2026-09-10 | 2026-11-15 |
|---|---|---|
| polterguy/magic | 1.2k | 1.3k |
67 Stars in the last 66 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
One line fetches a compose file from a website and runs it
The whole quickstart is a single command:
curl -fsSL https://hyperlambda.dev/docker-compose.yaml | docker compose -f - upThen the instruction is to open localhost:5555, point it at localhost:4444, and log in with `root` / `root`.
Three things sit in that line. The compose file is fetched from the project website over HTTPS and piped straight into a compose command, so whatever that URL serves is executed as a set of container definitions with no file on disk to inspect first. And the compose file it fetches pulls its images by floating tag:
  backend:
    image: servergardens/magic-backend:latest
  frontend:
    image: servergardens/magic-frontend:latest
Neither tag is pinned by digest, so two runs of the same command a week apart can install different bytes. Together with the fact that the compose file is the project's own hosted artifact rather than one committed to the repository, the shortest documented path to a running stack involves three things you did not choose: a remote file, a mutable tag on each of two images, and a default credential printed on the page.
The repository does contain a compose file of its own, and named volumes for everything the platform stores. So the pinned path exists. It is just not the one the headline points at.
Two of the three newest releases are titled with security language, all on one day
The release history is a compressed burst. v24.0.0 is titled Major security update with two exclamation marks, published 2026-09-28. v24.0.2 is titled Much tighter security on edge cases, published 2026-09-29. v24.0.3 is titled Better default slots, also on 2026-09-29, and carries the same timestamp as the last push to the repository.
So three of the newest tags were cut inside about sixteen hours, and two of them announce a security change. That is a normal pattern for a project that finds a problem and ships a fix, and it is also the clearest signal available about the state of the security model at a given version. Anyone evaluating this should read what changed in those two commits before concluding anything about the claims further down the page.
The version number itself is worth noting. This is v24, not a 0.x or a 1.x, and the last push is 2026-09-29, so the tree and the newest tag are the same moment. There is no lag between what you clone and what is released.
The comparison table names the product Magic Cloud, which is the same thing as the repository, and the release titles are the only place the page uses that name at all. The project homepage is hyperlambda.dev, the bounty links to a different domain entirely, and one of the compose images lives under a Docker Hub organisation called servergardens. So three names circulate for one artefact.
Four performance ratios and an 80% token claim, none with a method
The performance section is a single paragraph of multiples, all prefixed with In our measurements:
> Hyperlambda is roughly 20x faster than FastAPI or Flask, around 50x faster than LangChain, and 100-1,000x faster than graphical workflow tools such as n8n, Zapier and Make.
No hardware, no workload, no language on either side, no version numbers, no test harness. The range that spans two orders of magnitude is against tools that execute workflows by interpreting JSON, XML or YAML, and the page does give the reason for that gap, which is that Hyperlambda runs a compiled runtime. That explanation is fair and testable. The multiples are not.
The same pattern appears in the MCP section, which claims the token saving cuts consumption by roughly 80%, again in their measurements, and then links a savings calculator on the project website. The mechanism is not stated, and it is worth asking about: exposing more endpoints as tools normally increases the schema a model must read, so an 80% reduction implies the saving comes from something the agent stops doing rather than from the tool list being smaller. The page does not say what.
What is verifiable without the numbers is the structural claim in the comparison table, that there is no deploy step before you can test, that you save and run. That is a property of the architecture rather than a measurement, and it is the row worth acting on.
The hallucination guarantee covers function names, and the page admits the rest
The heading claims an LLM that cannot hallucinate functions, and the body is narrower and more careful than the heading.
The stated mechanism is that the model generates an abstract syntax tree rather than text, and the output is analysed and rejected if it contains functions that do not exist. The guarantee is then stated precisely: the generator cannot return hallucinated function invocations, and, the page adds, like any LLM it can still write logically wrong code, but every function it invokes is guaranteed to exist.
That is a checkable claim rather than a statistical one. A validator that rejects a tree referencing an undefined function either rejects it or does not, and that can be tested without any model. And the concession is in the same sentence as the guarantee, which is the right place for it.
What the guarantee does not cover is the larger problem of agents growing their tool space. The page combines the AST check with vocabulary restriction to argue that agents can grow their own tool space on demand without widening their attack surface. The vocabulary restriction is doing most of that work, and it is not explained on this page.
The security model claim next to it is hedged: restricting invocations at the execution level makes Hyperlambda, as far as we know, the only language that currently does this. A uniqueness claim attributed to the author's own knowledge of the field is not something a reader can check, and the hedge is in the text rather than added by a reader.
A standing bounty rests on an endpoint that has taken public input for three months
The security section offers money, in the first person, in the middle of the page:
> I'm so confident in the codebase quality, I'll give you $100 if you can find a severe security-related bug in its backend code, and another $100 if you can exploit the natural language API, which has accepted arbitrary public input for 3 months with nobody succeeding.
The first half is an ordinary bug bounty. The second half is a statement about a live service: a natural-language API that has been accepting arbitrary public input for three months, with the evidence offered being that nobody has succeeded against it.
That is a real fact about the deployment, and it is worth reading as one. The argument from absence of exploitation is not an argument about the design. It says something about three months of exposure, which is genuinely useful information, and it says nothing about the fourth month or about an attacker who has not tried.
The link in that sentence points to ainiro.io, while the project's own homepage is hyperlambda.dev. So the bounty covers a service on a second domain, and the page does not explain the relationship between the two.
Two other parts of the security claim are structural rather than statistical. Hyperlambda runs sandboxed with no file system access outside its sandbox, and individual functions can be whitelisted through the RBAC system, which is what lets a server accept code as input and execute it without knowing where the code came from. Those are design properties a reader can evaluate.
Log rotation caps each service at about 30 MB, which an LLM-backed install will reach
The compose file takes one precaution that is easy to miss, because the comment explains it in a way that makes it sound like a nicety:
    logging:
      driver: json-file
      options:
        max-size: "10m"
        max-file: "3"
The comment says to cap container logs so a chatty install cannot fill the disk. Ten megabytes times three files is thirty megabytes, applied separately to the backend and the frontend.
For a platform whose main activity is generating code and prose through a language model, thirty megabytes of retained output is a small budget. Every prompt, every completion, every generated function and every error goes through the same stream. A user who leaves a generation session running will reach that ceiling, and when the cap is hit the oldest entries are discarded silently.
The same applies to the frontend service, which in this design is an nginx container serving a static UI. Its logs should be quiet, so the cap costs nothing there. Applied to the backend, it is a decision with a real consequence that the comment does not mention.
The rest of the compose file is careful in ways that make this one line stand out. The backend health check polls the Hyperlambda health endpoint on port 4444 every thirty seconds with a five second timeout, five retries and a thirty second start period, and the comment notes that the container goes unhealthy after five misses. The frontend waits on `condition: service_healthy` rather than merely on the backend's container having started.
The compose file is careful about health and silent about credentials
There is no environment block in either service.
That is the observation that sits next to the root credential. The quickstart says to log in with `root` and `root`, the backend publishes 4444 on the host, the frontend publishes 5555 on the host, and the compose file as written offers no way to change that credential other than editing the file and supplying an environment variable whose name the page never gives.
The two default passwords for the storage layer are not in this compose file at all, which is worth noting rather than treating as a fault: the named volumes are the only state, at `/magic/files/etc`, `/magic/files/data`, `/magic/files/config` and `/magic/files/modules`, so everything a cloudlet holds lives in those four paths and nothing else. That is a clean statement about where the state is, and it means a backup is those four volumes.
The frontend health check is the detail worth quoting, because the comment explains a workaround rather than just asserting a command:
> nginx:alpine has no curl, but busybox wget ships with it.
So the frontend image is nginx on Alpine, its check uses wget against the root path, and the person writing it knew the obvious command would fail and said why in the file.
Everything a running instance needs is therefore a small, readable compose file: two named images on floating tags, four volumes, two health checks with a real dependency gate, a log cap, and no credential configuration.
No build step is real for the backend, and the palette description stops mid-sentence
The Web Designer section makes an unusual claim and then explains its own limit, which is the most convincing thing on the page. It opens any HTML page the cloudlet serves and lets you edit it like a document: click to select, double-click to rewrite a run of text, drag a block in from a palette, drag it elsewhere to move it.
The stated mechanism is that there is no project format and no build step, and that the page in the middle is the file on disk. Scripts are disabled inside the canvas, so what the browser has parsed is exactly what gets written back. The page then connects that to a specific consequence: because it works on the parsed tree, selection can reach a bare `#text` node, since every run of text is its own thing in the tree rather than a property of the tag around it.
That is a coherent design, and the no-build-step claim is genuinely true for this path. The platform's own summary repeats the claim on the backend side, that once you save the code you can test it with no deployment or publish step, and the sidebar supports it with a Playground that executes Hyperlambda without saving and an IDE that runs and replays any file on the server.
The one loose end is the palette. The page says the palette carries more than sixty blocks and that each one arrives wearing the classes that page already puts on that kind of element, and then the sentence stops: drop a button into. The clause that would explain what happens when you drop it is not there, which is an odd place for the text to run out given it is the last sentence in the section.
Editorial conclusion
This is worth evaluating if you want a self-hosted backend rather than a frontend paired with someone else's service, because the deploy-step argument is the one row in its comparison table you can verify yourself in an afternoon. Three things to check before you run it anywhere real. Do not use the one-line install on a machine you care about, since it fetches a compose file from a website and runs it immediately; use the pinned form instead. Change the default credential before the ports are reachable, because the compose file exposes no environment block through which to do it. And read the security claims as claims: the bounty, the claim of being the only language with execution-level function restrictions, the four performance ratios and the 80% token saving are all self-measured, self-rewarded or self-hedged on the same page. The generator's function guarantee is the one that is technically checkable, and it is genuinely narrow.
Frequently asked questions
How do I run magic?
The quickstart runs `curl -fsSL https://hyperlambda.dev/docker-compose.yaml | docker compose -f - up`, then opens localhost:5555 pointed at localhost:4444 and logs in with `root` / `root`. The compose file it fetches starts two containers from floating `servergardens/magic-backend:latest` and `servergardens/magic-frontend:latest` images.
What are the default credentials for magic?
The quickstart instructs you to log in with `root` and `root`. Neither service in the compose file has an environment block, so the page gives no environment variable name for changing that credential, and the backend port 4444 is published on the host.
Does the magic generator hallucinate function calls?
The page's claim is narrow. Because it generates an AST rather than text, the output is analysed and rejected if it references functions that do not exist, so it cannot return hallucinated function invocations. The same sentence concedes that it can still write logically wrong code.
How does magic compare to Lovable and Bolt?
The page's table lists Magic Cloud against Lovable and Bolt, and against n8n, Zapier and Make, across licence, self-hosting, whether a backend is included, deploy step, execution model, MCP server and vendor lock-in. The verifiable row is the deploy step, which the page claims is none for magic, save and run, against deploying to third parties first for the others.
What is the security bounty for magic?
The page offers $100 for a severe security-related bug in the backend and another $100 for exploiting the natural language API, which it says has accepted arbitrary public input for three months with nobody succeeding. That second link points to ainiro.io, while the project homepage is hyperlambda.dev.
How much log retention does the magic compose file keep?
Both services are capped with a 10 MB maximum size and three files, so about 30 MB each. The comment says this stops a chatty install from filling the disk, and for a backend generating code through a language model that ceiling is reached sooner than a first-time reader would expect.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/polterguy-magic)Star history chart for your README
[](https://hysenlabs.com/projects/polterguy-magic)Was this useful?