PrimeNG takes security fixes only, and new development moved to PrimeUI
The Most Complete Angular UI Component Library
At a glance
- What is it?
- PrimeNG, the Angular component library from PrimeTek Informatics, is no longer under active development in this repository: issues are read-only, patches continue on the 21.1.x line, and MIT releases already published stay MIT. New releases and bug reports now live at PrimeUI, and the project continues at primeng.dev.
- Who is it for?
- Stay on 21.1.10 if your Angular application already uses PrimeNG and you want patches from the team that still ships them. Do not start new feature work against this repository, because issues are read-only and a missing component or a regression gets you no triage.
- Can I use it commercially?
- Check first. The repository uses a licence we do not classify automatically, so read its LICENSE file before any commercial use.
- Is it still maintained?
- Yes. The repository last received commits 52 days ago.
- What is it written in?
- Mainly TypeScript, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
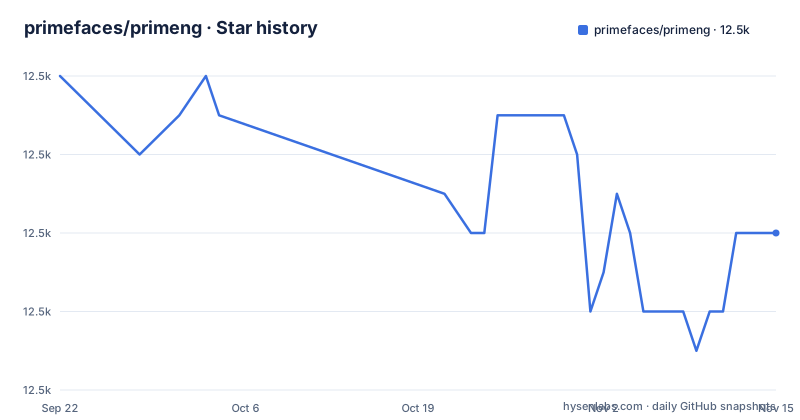
Star history
- primefaces/primeng12,482 ★ · -4
| Repository | 2026-09-22 | 2026-11-15 |
|---|---|---|
| primefaces/primeng | 12.5k | 12.5k |
-4 Stars in the last 54 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The quick start is gone and the README now routes you to primeng.dev
What a reader used to find in this repository is not there any more. The README is a transition notice now: a warning block stating that the repository is no longer under active development and receives security fixes only, a short explanation of what that means, and a set of links. There is no install command, no component list and no usage sample between them.
Two destinations replace it. primeui.dev/nextchapter carries the announcement, and primeng.dev is where the project continues. That split matters for whatever you came here to do. A question about configuring a component has to go to the new home, because this file will not answer it.
The source, meanwhile, is intact. The monorepo at the root declares version 21.1.10 under the name @primeng/monorepo.
Issues here are read-only, so bug reports have another address
Bug reports and feature requests belong at PrimeUI, not in this repository's tracker. The warning says so in one line: issues here are read-only. For a team that has filed issues against primefaces/primeng for years, the consequence is concrete. A crash reproduced today gets no triage here, because the README says the repository receives security fixes only.
Vulnerabilities have their own route, and it is the one channel still open. SECURITY.md is named as the place to report a security problem, and security fixes keep being published for the MIT-licensed releases.
The dates back this up. The last push to the default branch master was on 2026-09-24, and release 21.1.10 was published on 2026-09-09. Something is still moving. It is not features.
MIT releases stay MIT while package.json points at LICENSE.md
The licensing statement is narrow and useful: existing MIT versions remain MIT, forever, and every release published under MIT stays exactly as it is. Existing projects are unaffected.
The metadata reads differently. The licence field in the root package.json is the string SEE LICENSE IN LICENSE.md, and the repository ships a LICENSE.md instead of a bare licence file. That combination is why the project shows up in listings as unasserted rather than MIT. The effect lands on tooling: automated licence scanners and corporate compliance checks that read package metadata will not find MIT spelled out, and someone has to open LICENSE.md by hand to settle it.
The guarantee is also version-scoped. It speaks about releases already published under MIT and says nothing about the terms covering work done at PrimeUI.
The release build runs pnpm audit at high severity before compiling
Nothing compiles until formatting passes and the production dependency audit comes back clean:
"build:check": "pnpm run format:check && pnpm run security:check",
"security:check": "pnpm audit --prod --audit-level high"
Two consequences follow. A high severity advisory in a production dependency stops the build, so a release cannot go out on top of a tree the audit already condemns. And the --prod flag narrows the gate: advisories touching development dependencies do not block anything, which is the right trade for a published artifact and the wrong one if you are worried about a compromised tool in the build chain.
For a consumer this pair is invisible, since you install a built package rather than run the script. For anyone forking the monorepo or trying to reproduce a release locally, it is the first thing that decides whether the build proceeds.
pnpm run setup deletes the lockfile before it installs
The setup script does not do what the word usually means:
"setup": "pnpm run clean && pnpm run init",
"clean": "npx rimraf --glob **/node_modules **/dist **/.angular ./pnpm-lock.yaml",
"init": "pnpm install && husky"
pnpm-lock.yaml is committed at the repository root, and the clean step deletes it along with node_modules, dist and .angular before pnpm install runs again. A new contributor who follows setup resolves dependency versions from scratch and then sees the tracked lockfile show up as a change in git status, which is a poor first impression of a repository that pins its own installs.
The husky call in init is the other half of it. Git hooks configured under .husky/ are installed alongside commitlint.config.ts for commit messages and .prettierrc.json for formatting..
One release build compiles five workspaces, not just the library
pnpm-workspace.yaml with packages and apps directories make this a multi-package repository, and the publish script runs pnpm run build first. That build expands into five steps: build:lib filters primeng, build:themes filters themes, build:mcp filters mcp, and build:docs together with build:showcase both target the documentation workspace.
Themes are therefore a separate artifact from the library. A theme mismatch is a versioning question between two published packages, not a stylesheet tweak inside one.
There is an MCP package in that list, an easy detail to miss when reading a component library's tooling. Local work runs through the same workspace: the dev script starts that documentation app, and start:ssr serves it server-rendered.
21.1.10 is the newest thing this repository publishes
Three tags in under four months show what the remaining cadence looks like: 21.1.8 on 2026-05-18, 21.1.9 on 2026-06-04 and 21.1.10 on 2026-09-09. All three sit on one minor line, so consumers choose between patch levels of a single major version rather than between features.
The publish step pins that down. The release script tags v21-stable, writes its report to pnpm-publish-summary.json at the root, and passes --no-git-checks, meaning a release will not refuse to run against a dirty working tree.
Two changelogs sit at the root, CHANGELOG.md and CHANGELOG_ARCHIVE.md, with a changelog-lts directory beside them. Anyone still on an older line should read those before deciding whether to move..
Editorial conclusion
Stay on 21.1.10 if your Angular application already uses PrimeNG and you want patches from the team that still ships them. Do not start new feature work against this repository, because issues are read-only and a missing component or a regression gets you no triage. Before committing, open LICENSE.md rather than trusting the licence field in package.json, then confirm at primeng.dev which package your Angular version installs from, since the README here no longer carries an install command.
Frequently asked questions
What is PrimeNG used for?
It is an Angular UI component library from PrimeTek Informatics, shipped from a pnpm workspace that builds a primeng package and a separate themes package. This repository now receives security fixes only.
Is PrimeNG free or paid?
Releases already published under MIT stay MIT, according to the announcement in this repository. The licence field in package.json says SEE LICENSE IN LICENSE.md, so check that file for anything outside the MIT line.
Is PrimeNG only for Angular?
Yes. The repository is an Angular component library, and its workspace contains the documentation application with start and start:ssr scripts for running it and serving it server-rendered.
How do I install PrimeNG in an Angular application?
This repository no longer carries an install command. Its README points to primeng.dev for the continuing project and to primeui.dev/nextchapter for the announcement..
How do I use PrimeNG themes?
Themes are their own workspace package. The release build runs pnpm --filter themes build as a step separate from pnpm --filter primeng build, and the built themes are published alongside the library.
How do I use PrimeNG in Angular 21?
The 21 line is what this repository still patches. Releases 21.1.8, 21.1.9 and 21.1.10 all shipped in 2026, and the release script in package.json publishes with the v21-stable tag.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/primefaces-primeng)Star history chart for your README
[](https://hysenlabs.com/projects/primefaces-primeng)Was this useful?