PrimeVue's GitHub repo is now a security-only branch of a library that moved to PrimeUI
Next Generation Vue UI Component Library
At a glance
- What is it?
- PrimeVue is a Vue component library, and its repository has been changed in place rather than deleted: the MIT line stays exactly as it was, the issue tracker is read-only, and new releases live under PrimeUI. The judgment for anyone weighing an upgrade: nothing you already shipped is at risk, and nothing new arrives here either.
- Who is it for?
- Stay on PrimeVue if you have 4.x in production and want that line frozen in place, because the MIT terms on those versions are stated as permanent and security fixes are still arriving here. Move to whatever PrimeUI publishes if you need components, bug fixes, or framework integration work that this repository has stopped doing.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 52 days ago.
- What is it written in?
- Mainly Vue, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
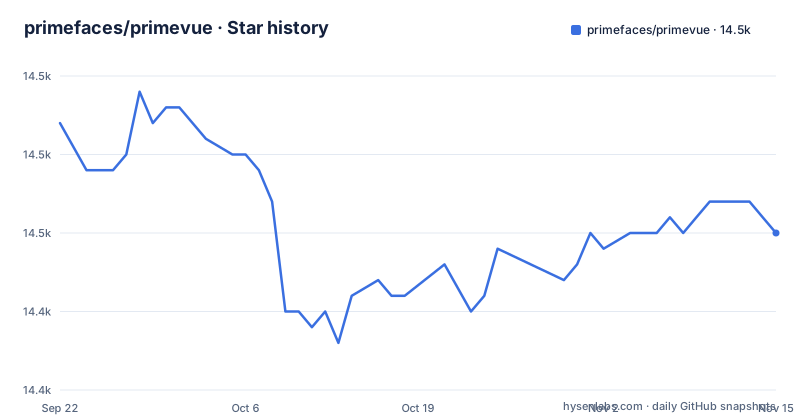
- primefaces/primevue14,450 ★ · -7
| Repository | 2026-09-22 | 2026-11-15 |
|---|---|---|
| primefaces/primevue | 14.5k | 14.5k |
-7 Stars in the last 54 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The repo is a security-only branch of a library that already moved
The line that matters most here is a warning at the top of the README: this repository is no longer under active development and receives security fixes only. PrimeVue continues as part of PrimeUI, a foundation the project points at through primeui.dev/nextchapter, and the issue tracker in this repository is read-only. The dates agree with that status instead of contradicting it. The version in package.json is still 4.5.5, the newest published release was 4.5.5 on 2026-04-08, and the last push landed on 2026-09-24. So the tree is not abandoned: something is still arriving in it, about five and a half months after the last release. What arrives is security work, which is a much narrower stream than the component work most people come here for, and the announcement language is careful to say so.
The MIT guarantee covers the versions you have, not the next one
The reassuring sentence is precise about its scope: existing MIT versions remain MIT, forever, every release published under the MIT license stays exactly as it is, existing projects are unaffected, and nothing is taken away. Read the next sentence and the boundary appears. Active development, new releases, and everything ahead now live under PrimeUI. The license promise is real but closed ended. A team already running 4.x keeps its terms indefinitely, while a team starting fresh today has to find out what the new home publishes before committing to it. PrimeUI is described as a sustainable foundation for the libraries you rely on, which is a funding statement rather than a technical one, and the signoff credits users with hundreds of millions of downloads. For a reader deciding whether to stay or go, the question is not whether the MIT line gets revoked, because the project says it will not, but whether a feature set frozen at 4.5.5 fits a roadmap.
Filing a bug here is a dead end by design
Issues in this repository are read-only. Bug reports and feature requests belong at PrimeUI, and security vulnerabilities have their own route through SECURITY.md, which is kept here. The split is tidy and awkward at once, because it is organised by report type rather than by version. A developer on 4.5.5 with a rendering bug or a missing component has no open channel in the tree where the code lives. The nearest real destinations are primevue.dev, named as where the journey continues, and the two history files kept at the root, CHANGELOG.md and CHANGELOG_ARCHIVE.md. So expect to file upstream rather than here, and keep your own note of which version a problem reproduced on, since a frozen tag means the fix will not land in the copy your app is pinned to.
setup deletes the committed lockfile before installing
The contributor scripts are where this repository still has firm opinions. setup is clean followed by init, and clean is a rimraf glob that removes node_modules, dist and .nuxt across the tree and then deletes the committed pnpm-lock.yaml:
"setup": "pnpm run clean && pnpm run init",
"clean": "npx rimraf --glob **/node_modules **/dist **/.nuxt ./pnpm-lock.yaml",
"init": "pnpm install",
init then runs pnpm install with no lockfile in place, because the file the clone arrived with was the one the previous command removed. What you get is a dependency graph resolved fresh at install time rather than the one the maintainers committed. That is fine for a maintainer doing release work on a machine they control, and awkward for anyone who needs the exact tree behind 4.5.5. It also means the lockfile in git is not the input to a default bootstrap, so a reproducible build starts with restoring that file yourself.
Two lockfiles in the root, and only one of them is honored
The root carries both pnpm-lock.yaml and package-lock.json, plus a .npmrc, while every script in package.json speaks pnpm: init runs pnpm install, link filters through packages with pnpm, and the release scripts use pnpm recursive publish. pnpm-workspace.yaml defines the pnpm workspace. The npm lockfile has no script pointing at it. That leaves two recorded dependency graphs in the tree and one package manager reading them, which invites drift. An npm user who installs from this repository root gets a resolution no script in package.json ever validates, while a pnpm user gets the graph the workspace file and pnpm-lock.yaml describe. The practical instruction that follows is short: treat the pnpm files as the source of truth and leave package-lock.json alone, because nothing in the build or release path will notice or refresh it.
Publishing runs with git checks off and skips apps/ entirely
The release script builds, then publishes every workspace package with git checks disabled:
"release": "pnpm run build && pnpm recursive publish --filter './packages/*' --no-git-checks --report-summary",Two details in that line matter to anyone tracking what shipped. The filter covers packages/* and nothing else, so nothing under apps/ can be published whatever state those apps are in, which is why build:apps still builds a showcase and a volt app on your machine and leaves them there. And --no-git-checks means the publish step does not inspect the working tree, which is exactly the difference between a release run and a review gate. Two sibling scripts, release:beta and release:rc, publish to the beta and rc tags the same way, so the machinery for pre-release channels is still wired up here even though the features those channels would preview are being built somewhere else now.
The build list is an inventory of everything this library ships
build:packages is a chain of ten steps, and reading it tells you what the project counts as its shipped surface:
"build:packages": "pnpm run build:metadata && pnpm run build:resolver && pnpm run build:core && pnpm run build:lib && pnpm run build:module && pnpm run build:themes && pnpm run build:icons && pnpm run build:mcp && pnpm run build:forms && pnpm run build:apps",Each step filters one workspace package by name: metadata, an auto-import-resolver, core, primevue itself, a nuxt-module, themes, icons, an entry called mcp, forms, and finally the apps. For a reader picking a version, this list is a fair description of the surface area. It is not one package of components but a set of separately built pieces, and the resolver and the Nuxt module that framework integrations depend on are separate builds inside the same workspace.
A formatting check sits in front of every release
Release runs build first, and build runs build:check before any package is compiled:
"build": "NODE_ENV=production pnpm run build:check && pnpm run build:packages",
"build:check": "pnpm run format:check && pnpm run security:check",
So a publishing run is gated twice before a file is emitted, once on formatting and once on a security check, with NODE_ENV set to production across the chain. The inputs for those steps sit at the root as eslint.config.mjs, .prettierrc.json and .prettierignore. Read the other way, that gate is a small mercy for anyone waiting on a patch for the MIT line, since a security release cannot quietly ship with a formatting or security-check failure attached. SECURITY.md is where the README says to report a vulnerability.
Editorial conclusion
Stay on PrimeVue if you have 4.x in production and want that line frozen in place, because the MIT terms on those versions are stated as permanent and security fixes are still arriving here. Move to whatever PrimeUI publishes if you need components, bug fixes, or framework integration work that this repository has stopped doing. Before you decide, check which version a problem in your app reproduces on, because that determines whether PrimeUI is even the right place to file it, and read SECURITY.md if you have found a vulnerability rather than a bug, since that path still runs through this repository.
Frequently asked questions
Is PrimeVue free to use?
The versions published under MIT are, and the project states that existing MIT versions remain MIT forever and that every MIT release stays exactly as it is. Security updates keep being published here for those versions. Active development and new releases now live under PrimeUI; the announcement is at primeui.dev/nextchapter.
is primevue free for commercial use
For the MIT line, yes, since LICENSE.md at the root of this repository carries the MIT license and the package author is PrimeTek Informatics. The README is explicit that existing projects are unaffected and nothing is taken away, so a commercial product built on 4.x keeps that footing.
What is PrimeVue used for?
It is a Vue component library, described as the Next Generation Vue UI Component Library, built and published from a pnpm workspace monorepo at version 4.5.5. Its build produces a metadata package, an auto-import resolver, core, the primevue package, a Nuxt module, themes, icons, an mcp entry, forms, and the apps.
how to install primevue
Consumer install steps are not in this repository, whose README now points to primeui.dev/nextchapter and primevue.dev instead. What the repo holds is the contributor side: pnpm-workspace.yaml, the setup, init, build and release scripts in package.json, and the packages/ and apps/ directories that those scripts build.
What companies use PrimeVue?
This repository names no companies. It credits users with hundreds of millions of downloads and signs off as The PrimeTek Team, and the only organisations named are PrimeTek Informatics as the package author and PrimeUI as the foundation development moved to.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/primefaces-primevue)Star history chart for your README
[](https://hysenlabs.com/projects/primefaces-primevue)Was this useful?