Privacy Guides splits its repository into CC BY-SA content and MIT code, and keeps the logos out of both
Protect your data against global mass surveillance programs.
At a glance
- What is it?
- Privacy Guides is a volunteer operated non-profit site that recommends privacy tools and is not affiliated with any of them. The repository is a MkDocs project with a forked theme, two licence files, and a container build that pins Python and Node.
- Who is it for?
- Privacy Guides fits readers who want privacy tool recommendations, written by volunteers with no advertising and no vendor relationship, and who can live with the fact that the wording is community editable. It does not fit a project that needs permissively licensed content with no share-alike obligation, or anyone who wants to reuse the branding.
- Can I use it commercially?
- Yes, with credit. CC-BY-SA-4.0 allows commercial use as long as you credit the authors and indicate what you changed. It is written for creative content, so check how it applies to any code.
- Is it still maintained?
- Yes. The repository last received commits 6 days ago.
- What is it written in?
- Mainly Markdown, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
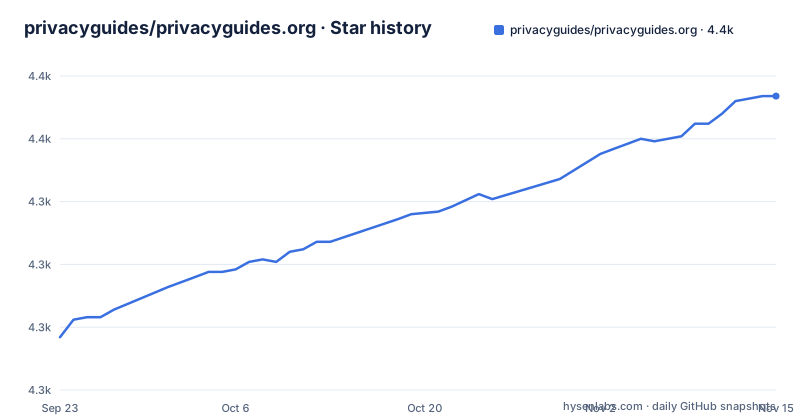
- privacyguides/privacyguides.org4,367 ★ · +96
| Repository | 2026-09-23 | 2026-11-15 |
|---|---|---|
| privacyguides/privacyguides.org | 4.3k | 4.4k |
96 Stars in the last 53 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Content and site code carry two different licences
The repository ships two licence files and draws the line by folder rather than by file type. Content is under the Creative Commons Attribution-ShareAlike 4.0 International Public License, and the folders holding it are named: docs, theme/assets/img and includes. Source code and configuration are under the MIT License and live in the config folder, the theme folder, and the root of the repository. The case of a code snippet written inside a prose file is settled explicitly, with those snippets treated as MIT licensed. A final sentence leaves room for third party work: the licences do not apply to anything where another licence is otherwise noted. So the answer to can I reuse this depends on which directory it came from, and the copyright line, which reads 2019 to 2024, is the only place a date range is stated.
The logos are the part of the project cannot relicense
One folder is explicitly out of bounds. Logos in theme/assets/img may not be original works of Privacy Guides, so the project says it cannot license them, and it states a belief rather than a fact: that these marks came from third party providers and are either in the public domain or used as fair use. The fair use argument quoted is the narrow one, that copyrighted images may be used to identify the subject for purposes of public comment. Trademark law is called out as a separate layer that survives any copyright conclusion. The responsibility is placed on the person doing the copying, who is told to ensure the mark identifies the entity that owns the trademark and that they have the right to use it under the law that applies to their intended use, and who is solely responsible for not infringing copyright or trademark.
No endorsement, and the wordmark needs written approval
Reuse is allowed in any reasonable manner, with one prohibition attached to the manner itself: not in any way that suggests Privacy Guides endorses you or your use. The second prohibition is about the brand rather than the words. The Privacy Guides branding may not be used in your own project without express approval, and the branding is defined as two things, the Privacy Guides wordmark and the shield logo. Contributors grant the project rights at the point of contribution, and the same terms apply to anyone who submits a pull request: contributing means accepting the licences above. For a project that wants to cite the guides in documentation, this is the paragraph that matters, since a citation is fine and a project name with a shield next to it is not.
The site is a MkDocs project with a forked theme and three config files
The build is Python first. Three MkDocs configuration files sit at the root, one for the main site, one for the blog and one labelled insiders, and dependencies are managed with a Pipfile and a Pipfile.lock rather than a requirements file. The theme is not taken from upstream: a directory named modules/mkdocs-material holds a copy that is copied into the image before installation, so theme changes land in this repository rather than in a published package. The container image starts from python:3.12-slim-bookworm, installs pipenv with gcc, libffi-dev and build-essential, and installs the locked dependencies into a project local virtual environment at /.venv with PIPENV_VENV_IN_PROJECT set and pipenv install --deploy. A second stage runs on node:24-bookworm-slim and compiles the all-contributors command line tool with pkg against a node18 target. The last stage adds the runtime pieces a static site with generated images still needs, including GTK and Cairo libraries, image processing tools and Git.
Two web mirrors, five git mirrors, one onion address
Publishing is spread out on purpose. The website itself is reachable through GitHub Pages at privacyguides.github.io and through a BunnyCDN host, each with an /en/ path, so a reader has a second route if the primary one is slow or filtered. The git history is mirrored further out: GitHub, GitLab, Codeberg, a self hosted instance at code.privacyguides.dev, and a server at git.jonaharagon.net. There is also a Tor onion address. That address is introduced with a note rather than a bare link: most hidden service providers are not very extensively used or tested, which is why Tor is strongly recommended, and reaching for any other network can put your anonymity at more risk. The advice given is to make sure you know what you are doing before reaching for an alternative network.
Volunteers only, four ways to help, and no vendor ties
The About section states the structure plainly: a non-profit collective operated entirely by volunteer team members and contributors, free of advertisements, and not affiliated with any of the listed providers. That last clause is the reason the recommendations can be read as advice rather than marketing. Named people are listed on an executive committee page, and everyone else appears in a contributors list kept in the repository, with an invitation to add yourself by opening an issue or by asking the maintainer directly. Four contribution paths are offered: start a discussion on their forum, sponsor the project through GitHub Sponsors, help translate through Crowdin with a Matrix chat for the translation room, or edit the site, where the work list is the open issues, pull requests are expected to correspond to topics already approved in a discussion tag, and a style guide sets the writing rules.
Releases are named after the day, and the newest is 2026.09.17
The visible releases are 2026.08.12, 2026.09.17 and 2026.10.31, so a build is identified by the date it was produced rather than by a version counter. The last push to the repository was on 2026-10-31, the same day as the newest release. Repository automation follows the same pattern as the site: a GitHub Actions workflow publishes the release, a .devcontainer directory backs the Codespaces badge in the contributing section, and a CITATION.cff file lets the project be cited formally. A .allowed_signers file, a .mailmap and an .all-contributorsrc sit alongside the editor and linter configuration files, .markdownlint.yml and .rumdl.toml.
Editorial conclusion
Privacy Guides fits readers who want privacy tool recommendations, written by volunteers with no advertising and no vendor relationship, and who can live with the fact that the wording is community editable. It does not fit a project that needs permissively licensed content with no share-alike obligation, or anyone who wants to reuse the branding. Before copying anything, check whether the file you took sits under the content licence or the code licence, read the trademark paragraph, and remember that the copyright line still reads 2019 to 2024.
Frequently asked questions
Is Privacy Guides run by the companies it recommends?
No. It is described as a non-profit collective operated entirely by volunteer team members and contributors, free of advertisements and not affiliated with any of the listed providers. Team members are named on an executive committee page, and contributors are listed in the repository.
Can I reuse content from Privacy Guides in my own project?
Content is licensed under CC BY-SA 4.0 and site code under MIT, with content in the docs, theme/assets/img and includes folders and code in config, theme and the repository root. Code snippets inside documentation files count as MIT. You may not use the Privacy Guides wordmark or shield logo without express approval, and you may not imply endorsement.
How is the Privacy Guides website built and published?
It is a MkDocs project with three configuration files, a Pipfile and Pipfile.lock, and a copy of mkdocs-material under modules. The container build starts from python:3.12-slim-bookworm, installs locked dependencies with pipenv install --deploy, and adds a Node stage for the contributors tool. Published versions are named after their date.
Where can I reach Privacy Guides if the main site is blocked?
The site is mirrored on GitHub Pages and on a BunnyCDN host, both with an /en/ path, and the git repository is mirrored on GitHub, GitLab, Codeberg, a self hosted instance and a maintainer server. A Tor onion address also exists, with a note that most hidden service providers are not very extensively used or tested, which is why Tor is recommended over other networks.
Official sources
Where developers are discussing it
Posts on Hacker News, dev.to and Lobsters that link to this repository, found by our scan of those communities. 0 in the last 30 days; newest first.
- privacyguides.orgHacker News · Sep 28, 2026 · 2 points · 0 comments
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/privacyguides-privacyguides-org)Star history chart for your README
[](https://hysenlabs.com/projects/privacyguides-privacyguides-org)Was this useful?