nuclei-templates: 11,997 files, two KEV catalogs, and a review path the README does not explain
Community curated list of templates for the nuclei engine to find security vulnerabilities.
At a glance
- What is it?
- This repository holds the checks that the nuclei scanner runs, not the scanner. It is 873 directories of template data, MIT licensed and released every few weeks, and the part worth understanding before you depend on it is where the review rules live, because the README never says what they enforce.
- Who is it for?
- Adopt this repository if you already run the nuclei engine and want current checks, updating from the v10.5.x releases rather than from an old checkout, and read the files under http/ knowing that 1496 templates exist for actively exploited vulnerabilities alone. Do not treat it as a scanner you can install, since the engine lives in the separate projectdiscovery/nuclei repository and nothing here runs on its own.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository received new commits within the last day.
- What is it written in?
- Mainly JavaScript, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 14, 2026, and from our analysis. They are not legal advice.
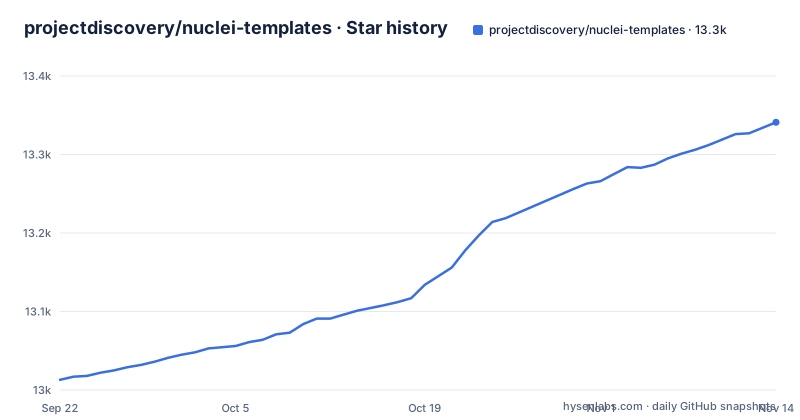
Star history
- projectdiscovery/nuclei-templates13,341 ★ · +328
| Repository | 2026-09-22 | 2026-11-14 |
|---|---|---|
| projectdiscovery/nuclei-templates | 13k | 13.3k |
328 Stars in the last 53 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
This repository ships templates, not the engine that runs them
Everything here is data rather than code you launch: 873 directories and 11997 files of templates, described in the project's own words as the core of the nuclei scanner, which is where the actual scanning engine lives. The link at the top of the page points at that separate projectdiscovery/nuclei repository rather than at anything hosted in this tree. The practical consequence shows up the moment you evaluate the project: a checkout gives you a directory of checks and no way to execute one. If the binary is not already installed, that half of the setup happens elsewhere, and a tag string is the only handle these files offer the person running them.
nuclei -tags kev,vkev selects the 1496 actively exploited templates
Actively exploited vulnerabilities get their own tag pair, and the command is spelled out rather than left to inference. The kev tag covers the CISA Known Exploited Vulnerabilities Catalog with 454 templates, vkev covers VulnCheck KEV with 1449, and 407 templates appear in both catalogs. The overlap is why the stated union of 1496 falls short of the 1903 you get by adding the two rows. Both tags in one pass:
nuclei -tags kev,vkevPick one tag instead of two and the gap is concrete. A vulnerability that VulnCheck lists while CISA does not is not matched by a kev-only run, and the reverse holds for the CISA entries VulnCheck has not picked up.
9281 files sit under http/, while the language label reads JavaScript
Directory counts decide what an untargeted run feels like. http/ holds 9281 files, then a long drop to cloud at 659, file at 436, network at 259, code at 251, dast at 240, workflows at 205, javascript at 92, ssl at 38 and dns at 23. The statistics table also names file at 436 and dns at 26 as types, which are scan types rather than folders, so those two columns are not a second directory listing. GitHub labels this repository JavaScript while the bulk of the tree is HTTP checks, so any tooling that filters by language describes a slice of the corpus rather than its shape.
info is the largest severity bucket and 54 templates carry unknown
Severity travels with the template rather than being decided by the scanner, and the spread is uneven: info 4353, high 2552, medium 2457, critical 1555, low 330 and unknown 54. Critical, the bucket most scans exist for, sits well below the informational and high rows. An unfiltered pass therefore returns roughly three informational results for every critical one, which is what forces a severity decision before the output is readable. The 54 unknown entries are the sharper problem: a severity filter on the named levels will not include them.
vuln tops the tag table at 6468 and the top ten is a truncated view
Tags are the primary handle on this set, and the ten most common are vuln 6468, cve 3587, discovery 3265, vkev 1394, panel 1365, xss 1269, wordpress 1261, exposure 1141, wp-plugin 1103 and osint 848. Only the top ten of each matrix are shown; the expanded table sits in TEMPLATES-STATS.md and a TEMPLATES-STATS.json version exists for integration. That cutoff has teeth for automation. A script that counts coverage from the headline table is reading ten tags and ten authors and will report nothing about everything below the line, including any directory a target-specific scan depends on.
Ten authors account for 7016 files and the review rules are not in the README
Authorship concentrates hard at the top: dhiyaneshdk 1894, daffainfo 905, princechaddha 854, dwisiswant0 805, ritikchaddha 678, pussycat0x 675, pikpikcu 353, pdteam 314, pdresearch 275 and iamnoooob 263. Those ten total 7016 files, so a large share of what a scan runs was produced by people with hundreds of templates each. The root also carries TEMPLATE-REVIEW-GUIDE.md, PULL_REQUEST_TEMPLATE.md, .review-bot and .yamllint, which is where incoming checks meet some form of automated and human scrutiny. What the README never states is what that scrutiny rejects. Whether a given template was reviewed by a person is not something the repository tells you, and that is the fact to check before you act on a finding.
There is no install command here, only a link to the engine's own repository
Nothing in this repository can be installed on its own, and no clone command, package name or version string appears anywhere in the project's instructions. What you get instead is a pointer: https://nuclei.projectdiscovery.io is where to read about building custom templates, and the nuclei repository is where the engine lives. Nor does the README answer where these files sit on disk after a sync, which leaves the question open even though the tree carries templates-checksum.txt and cves.json-checksum.txt, so the set is versioned by checksum as well as by release tag.
Checksums, cves.json and three translated READMEs form the integration surface
The machine-readable surface is plain to inspect: TEMPLATES-STATS.json, TOP-10.md, contributors.json, cves.json, templates-checksum.txt and cves.json-checksum.txt all sit at the root beside the directories. Documentation is duplicated into README_CN.md, README_JA.md and README_KR.md, which means a correction to the main README does not reach readers of the others until someone ports it. Licensing is MIT under LICENSE.md. On cadence, releases are v10.4.9 on 2026-09-16, v10.5.0 on 2026-10-05 and v10.5.1 on 2026-10-23, and the last push was on 2026-11-02, so a checkout falls a release behind within weeks of sitting still.
Editorial conclusion
Adopt this repository if you already run the nuclei engine and want current checks, updating from the v10.5.x releases rather than from an old checkout, and read the files under http/ knowing that 1496 templates exist for actively exploited vulnerabilities alone. Do not treat it as a scanner you can install, since the engine lives in the separate projectdiscovery/nuclei repository and nothing here runs on its own. Verify first whether a specific check on your target has been reviewed by a person: TEMPLATE-REVIEW-GUIDE.md and .review-bot exist in the root, but the README does not describe what either one rejects, and the top ten authors account for 7016 of the 11997 files.
Frequently asked questions
What are the best nuclei templates?
The set is organised by tags and by directory, with vuln, cve, discovery, vkev, panel and xss the most common tags and http the largest directory at 9281 files. For vulnerabilities under active exploitation the project points at the kev and vkev tags, which together cover 1496 unique templates.
How many nuclei templates are there?
The repository reports 873 directories and 11997 files. The figure covers the whole corpus, including community contributions as well as templates provided by the team.
What is Nuclei used for?
Nuclei is the scanner, and templates are its core. This repository stores the checks written by the project team and contributed by the community, which the engine loads when it runs a scan.
Can I use Nuclei in Windows?
The README does not document supported operating systems or platform requirements anywhere. It points to the separate projectdiscovery/nuclei repository for the scanner itself and to nuclei.projectdiscovery.io for building custom templates.
how to use nuclei templates
Templates carry tags, and the one command given in the README uses the kev and vkev tags together to scan for actively exploited vulnerabilities. Custom template authoring is documented at https://nuclei.projectdiscovery.io.
how to install nuclei templates
The README gives no install command for this repository, because it is a set of templates rather than a program. Obtaining the engine to run them means going to the projectdiscovery/nuclei repository the README links to.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/projectdiscovery-nuclei-templates)Star history chart for your README
[](https://hysenlabs.com/projects/projectdiscovery-nuclei-templates)Was this useful?