ProtonVPN's Android release build takes two passwords as command-line properties
Official ProtonVPN Android app
At a glance
- What is it?
- The source for a commercial VPN's Android client, where the release build passes a keystore password and a key password as Gradle properties on the command line, the same repository demonstrates the correct pattern in its own Makefile, and the make target that promotes an image to the latest tag does so from a development branch while another comment in the file says latest is the same as branch-master.
- Who is it for?
- This repository suits a developer who wants to read how a commercial VPN client for Android is put together, and who will treat its published signing fingerprint and its verification script as the two things worth taking from it. Check four things first.
- Can I use it commercially?
- Yes, with conditions. GPL-3.0 is a copyleft licence: if you distribute software that includes it, you must release that software's source code under the same licence. Running it internally without distributing it does not trigger that obligation.
- Is it still maintained?
- Yes. The repository last received commits 24 days ago.
- What is it written in?
- Mainly Kotlin, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
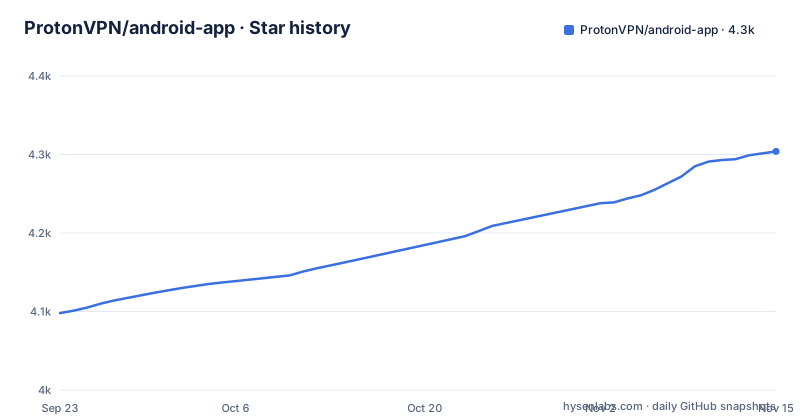
- ProtonVPN/android-app4,304 ★ · +206
| Repository | 2026-09-23 | 2026-11-15 |
|---|---|---|
| ProtonVPN/android-app | 4.1k | 4.3k |
206 Stars in the last 53 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Two passwords on the command line, in a repository that shows the right pattern elsewhere
The release build instruction is a single Gradle invocation with four properties:
./gradlew assembleProductionVanillaOpenSourceRelease -PkeyStoreFilePath=<keystore> -PkeyStoreKeyAlias=<alias> -PkeyStorePassword=<pass> -PkeyStoreKeyPassword=<key-pass>Two of those four are passwords. Passing a secret as a command-line argument puts it in the process table, where other processes on the machine can read it, and in the shell history file. What makes this worth naming rather than filing as a nit is that the same repository demonstrates the correct approach three files away. The Makefile begins by conditionally including an environment file and the comment above it lists exactly the kind of values that belong in one, including a personal access token for the internal forge. So a developer reading the build file learns that secrets go in a dotenv file, and then the release instruction asks for two of them on the command line. There is a third instance of the same habit in the Makefile's registry login, which passes a pipeline token as the password argument rather than on standard input.
The target that promotes to latest pulls a development branch
The Makefile builds a container image per branch, then has a separate target that pulls one branch's image, retags it as latest and pushes it. Which branch it pulls is a variable, and the variable defaults to a development branch. The comment above the tagging logic says the latest tag is the same as the master branch image. Both of those cannot be the default, because the repository's own default branch is master and this file never mentions master except in that comment. So the default behaviour of the promotion target is to take whatever the development branch's image currently is and publish it under the moving latest tag. For a build image that feeds continuous integration rather than a shipped binary that is an odd default but recoverable, because the branch name is a variable. It is still the kind of default that publishes a working state to a stable name without anyone having decided that is what they wanted. There is a second path to the same tag: setting the branch variable to the word latest changes the tag computed during the build, which is not the same code path as the promotion target at all.
The Makefile declares a target it never defines, and tags an image with itself
Two small things in the same file. The list of targets declared as not producing files names seven entries, and six of them have recipes. The seventh is a help target, and there is no rule for it anywhere in the file, so asking make for help prints nothing. That is the mildest kind of build file bug and the easiest to miss, because nothing else in the file refers to it. The second is in the image target, which builds an image with a tag, tags it again with the identical reference, and pushes it. The middle command is a no-op: it applies a tag to an image that already carries exactly that tag. A reader looking for the difference between the build and push paths will spend a moment on it. The file also uses target-specific variables, declaring an image name on a line after the recipe that uses it, which is valid and reads like a second, empty recipe. All of this is ordinary make, and none of it is wrong enough to matter except the missing target.
The fingerprint is published, the verification script ships, and the file never joins them
This repository does something many do not. It publishes the fingerprint of its signing certificate in the readme, states that every build except the F-Droid one is signed with the same key, and ships a shell script whose name says it verifies an application's signature. Three pieces that belong together, and the readme never tells you they are related. The fingerprint is a full colon-separated digest of the certificate, presented in a code block, with the application identifier above it, so the two values you would compare are both right there. The F-Droid exception has an obvious cause, since that store re-signs with its own key, and the file does not say so. The practical consequence of the fixed key is worth spelling out for anyone building this themselves: if you sign the open-source variant with your own key, you cannot install it over an existing Proton install, and vice versa, because the platform treats a different signing identity as a different application and requires the old one to be removed first. The script that would let you check all of this is in the tree, undocumented.
One half of the codebase has committed style rules and the other has the tool's defaults
Style enforcement is split by language and the two halves are configured differently. For Java, the project ships an editor scheme file and tells you to import it into your IDE through a settings menu path. That means the rules exist as an artefact but only apply to a contributor who performs the import; everyone else formats to their own defaults and finds out at review time. For Kotlin, the file says the linter is used with its default rules, and there is no editor configuration file in the tree for it to read. The local checks a contributor can run are four commands:
gradlew checkstyle
gradlew detekt
gradlew test
gradlew androidTest
So the static analysis story is four tools for one project: an editor scheme you import by hand, a linter running on defaults, a Kotlin analyser that ships two project-local modules of its own, one holding custom rules and one formatting its output for an internal forge, and a fourth analyser with an ignore file in the root that the readme does not mention. The two local detekt modules are the most interesting part, because a custom rule set is design intent written as code and the readme says nothing about what the rules are.
A native toolchain, a Python script, and a language field that disagrees with the contributing guide
The build prerequisites are four tools, and three of them exist to compile native code: the platform SDK, the native development kit, CMake, and a binding generator. A binding generator in the list means there is native code in the build producing bindings into the JVM, which is not something the readme mentions anywhere. The tree confirms the shape of a large commercial Android project: two top-level build files with a convention-plugin directory and a legacy build-sources directory, a code-quality rules directory, a shared test library, a UI automation helper, a release test directory, a baseline profile directory, a metadata directory, an observability directory, a Firebase device configuration file, a codeowners file, and a Python script whose name says it converts coverage output. That last one is the only Python file at the top level in a project whose metadata describes a Kotlin project. The metadata records the primary language as Kotlin, while the contributing guide tells you the codebase is mostly Java and that new code should be Kotlin where possible. Those are not contradictory so much as a transition caught mid-flight, with the metadata already reporting the destination.
The documented version scheme is not the scheme the releases use
The versioning section is one line: the version matches a four-part format of major, minor, patch and hotfix. The three newest releases are 5.20.98.0, 5.20.74.0 and 5.20.57.0: major five, minor twenty, a third position that climbs by large steps and a fourth position of zero. The cadence behind it is brisk: fifty-seven to seventy-four to ninety-eight in about three weeks, and the branch was last pushed forty-three seconds before the newest release was published.
The readme documents one build variant and the project ships two
The build instructions name one variant, assembleProductionVanillaOpenSourceDebug, and its release counterpart. The contributor agreement is worth reading as well, and it is not the usual permissive form. The first clause assigns copyright in contributions to the company outright rather than granting a licence, and the third states that a record of the contribution, including personal information submitted with it, is kept indefinitely and may be redistributed with the project. A copyright assignment is compatible with the copyleft licence the project uses, since the holder can relicense, but it is a materially different deal from an inbound-equals-outbound agreement and the readme states it in three sentences with no discussion.
Editorial conclusion
This repository suits a developer who wants to read how a commercial VPN client for Android is put together, and who will treat its published signing fingerprint and its verification script as the two things worth taking from it. Check four things first. The release build takes two passwords as command-line arguments, which is visible to other processes and lands in shell history, while the Makefile in the same repository shows the safer pattern. The target that promotes an image to the latest tag pulls a development branch by default, even though a comment elsewhere in the file equates latest with branch-master. The make file declares a phony target it never defines. The fingerprint and the signature verification script are both present and never connected.
Frequently asked questions
What is the ProtonVPN Android app repository?
The source for ProtonVPN's official Android client, released under GPLv3, written mostly in Java with a transition to Kotlin under way. The readme documents building the open-source variant.
How do I build the ProtonVPN Android app?
Install the platform SDK, the native development kit, CMake and a binding generator, clone the repository, then run the Gradle wrapper for the open-source debug variant or open it in Android Studio. A release build additionally needs a keystore path, an alias and two passwords passed as Gradle properties.
How do I verify a ProtonVPN Android app signature?
The readme publishes the SHA-256 fingerprint of the signing certificate and states that every build except the F-Droid one is signed with the same key, and the repository contains a shell script for verifying a signature. The readme never connects the fingerprint to the script.
What is ProtonVPN's Android version numbering scheme?
The file states four parts, major, minor, patch and hotfix. The three newest releases are 5.20.57.0, 5.20.74.0 and 5.20.98.0, with the third position climbing and the fourth at zero.
What does contributing to the ProtonVPN Android app require?
Matching the existing style and naming, writing new code in Kotlin where possible, conforming to a stated stack of Kotlin with an architectural pattern, data binding and coroutines, and running a Gradle task to update licence attributions after changing dependencies. Contributors assign copyright in their contribution to the company.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/protonvpn-android-app)Star history chart for your README
[](https://hysenlabs.com/projects/protonvpn-android-app)Was this useful?