Craftplan swapped MinIO for SeaweedFS and kept the service name, the variables and the default password
Self-hosted software for managing artisanal D2C micro-businesses
At a glance
- What is it?
- An AGPL Elixir and LiveView ERP for small craft manufacturers, self-hosted with PostgreSQL and object storage, with versioned bills of materials, automatic cost rollups and allergen tracking as first-class features. The interesting part is the deployment layer, where the storage migration was completed at the image and API level but not in the compose vocabulary, the credential variable names or the shipped defaults.
- Who is it for?
- Craftplan suits a small maker who needs costing that survives recipe changes, lot traceability and allergen data in one place, and who would rather host it than rent an ERP per module. It is a poor fit if object storage exposure is not something you want to think about, because the default compose publishes the storage port on plain HTTP with the previous software's default credentials.
- Can I use it commercially?
- Yes, with strict conditions. AGPL-3.0 is a network copyleft licence: if people use a modified version over a network, for example as a hosted service, you must offer them its source code under the same licence.
- Is it still maintained?
- Yes. The repository last received commits 14 days ago.
- What is it written in?
- Mainly Elixir, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
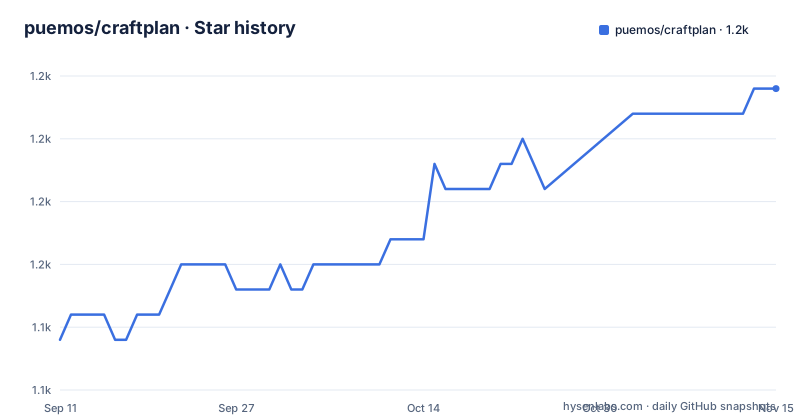
Star history
- puemos/craftplan1,157 ★ · +10
| Repository | 2026-09-11 | 2026-11-15 |
|---|---|---|
| puemos/craftplan | 1.1k | 1.2k |
10 Stars in the last 65 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The storage service is still called minio and still defaults to minioadmin
The compose file describes three services, and the third one tells the whole migration story in its own vocabulary. The service is named `minio`. Its image is not MinIO at all but a project-built storage image. Its environment is expressed entirely in AWS-prefixed variables, because the application talks to it over the S3 API. Its two credential variables fall back to variables named after the old software, and those fall back further to the old software's stock default user and password. Its dependency condition is expressed against the old name, so the application waits for a healthy service called `minio`. And its two volumes are named after both generations at once, one for the new storage engine's data directory and one carrying the old name for a second mount point. Every layer above the image was renamed for the new engine. The compose vocabulary, the credential names and the shipped defaults were not.
The migration cost nothing in application code
You do not clone the repository to run it. Two files are fetched, the second is copied and filled in, and the stack starts:
curl -O https://raw.githubusercontent.com/puemos/craftplan/main/docker-compose.yml
curl -O https://raw.githubusercontent.com/puemos/craftplan/main/.env.example
cp .env.example .env   # Fill in the required secrets (see .env.example)
docker compose up -d
That brings up Craftplan, PostgreSQL and SeaweedFS with migrations running automatically. The migration story then tells you why that is safe. Because the storage engine is reached through the S3 API, the application needed no change: the compose file configures it with a scheme, a host, a port, a public URL, an access key, a secret, a bucket and a region, and the region default is the conventional one for that API. So replacing the implementation was a matter of pointing at a different image and mounting different directories. The upgrade path is documented as automatic: the updated compose file migrates and verifies existing photos before Craftplan starts, later upgrades to the same engine skip migration, and you are told to keep your environment file and volumes. A separate compose file and a second Dockerfile exist for that migration, and the upgrade guide is said to cover disk-space requirements and recovery. The design point worth taking away is that S3 compatibility is what made this a storage swap rather than a rewrite.
Object storage is published on plain HTTP with the old default credentials
Two defaults in the compose file are worth changing before this is reachable from anywhere but your own machine. The first is exposure. The storage port is published to the host, and the public URL the application generates for stored files defaults to a plain HTTP scheme pointing at whatever host you configured, on the storage port rather than the application port. So object storage is on its own published port, not behind the application's port, and it defaults to unencrypted transport. The second is credentials. The access key and secret fall back through a chain that ends at a well-known default pair from the previous storage software, and the example environment file says in a comment to set non-default credentials before exposing storage to the network, and carries a note for existing users of those variables. The application is not the problem here. It is that a migration that preserved compatibility also preserved a default that only made sense when the storage port was never published.
One variable drives both sides of the published port
The application's port mapping is written with the same variable on both sides of the colon, defaulting to 4000. The effect is that you cannot publish the application on a different external port without also changing the port it listens on, because the two are the same value. That is a defensible simplification for a self-hosted tool where you would normally set a reverse proxy in front anyway, and the documentation does point at reverse proxy setup in the self-hosting guide along with single-container mode and a hosted railway deployment. The database service is configured more conventionally, with a healthcheck running the standard readiness probe against the postgres user on a five-second interval with retries, and the application waits for both the database and storage to report healthy before starting. Data directories are set to an explicit subpath rather than the volume root, which avoids a permissions problem that otherwise appears only on a fresh volume.
The version badges lost their opening tags
At the top of the README, where the licence and version badges sit, the version badges are broken. What is left of them is two orphaned attribute fragments containing a version number and a closing quote, with no opening tag in front of them, so the Elixir and Erlang versions the project asks you to expect render as nothing. The real pins are in the Dockerfile, and they are precise: an Elixir version, an Erlang and OTP version, a specific Debian variant with a date in its name, and a Node major. Both the builder and the runtime images are derived from that same Debian variant argument, which is the right way to do it, since a builder and a runner on different library versions is a class of bug you avoid by construction. The project also ships a version file at the repository root and copies it into the image during the build, so the running application knows what it is.
Node exists only in the builder, and the release runs as nobody
The Dockerfile is a two-stage build with a clean division. The builder installs a C toolchain, git and curl, then pipes a NodeSource setup script into the shell to add Node, which exists solely to build assets; the runtime image never sees it. The runtime installs a short library list, generates the en_US locale by uncommenting it in the generator file and running the generator, sets the three locale variables, and chowns the working directory to an unprivileged user before dropping to it with a plain server command as the entrypoint. Two ordering choices are commented and both are deliberate. The application is compiled twice, once before assets and again after the asset deploy step, with a note that the second pass syncs the digested assets into the compiled application. And the runtime configuration file is copied last, with a comment saying it is so earlier layers stay cached, which means a config-only change rebuilds almost nothing.
Four formatters, and a commit type outside the convention
The development workflow is driven entirely by a version manager rather than by hand-installed toolchains: one command installs the Elixir, Erlang and Node versions declared in the project's own file, and the rest are named tasks. Services start the database, the storage engine and a local mail catcher together, so a contributor gets a working environment without touching a compose file directly. Formatting runs four separate tools, covering Elixir source, stylesheets, the utility class ordering and the templates, with a check-only variant and a full CI task that requires the services to be running first. Commits follow a typed and scoped convention with three worked examples, two of which are ordinary and the third of which uses a type that is not part of that convention. A changelog generator or a strict commit linter will either reject it or need it configured, which is a small thing to fix now and an annoying one to inherit.
Mailpit is a development service and the screenshot grid is empty
Two small details tell you what is finished and what is not. The development service set includes a local mail catcher, which the production compose file does not have, and that matches the email feature being configurable from the interface across a local protocol and five hosted providers with keys encrypted at rest. So outbound mail is fully wired in development and delegated to a provider in production, which is the right split. The screenshots section, by contrast, is a table of three rows and two columns with all six cells empty. Alongside it the tree contains a planning directory, an Elixir code-generation configuration, an environment file for a directory-based tool, and a configuration file for a specific hosting provider, none of which the README mentions. The application surface itself is broader than the marketing suggests: both a REST-shaped and a query-style API with key authentication, policy-based authorization across every resource, two roles, a fuzzy command palette over the main record types, and a subscribable calendar feed of deliveries and batch schedules that can be revoked from settings.
Editorial conclusion
Craftplan suits a small maker who needs costing that survives recipe changes, lot traceability and allergen data in one place, and who would rather host it than rent an ERP per module. It is a poor fit if object storage exposure is not something you want to think about, because the default compose publishes the storage port on plain HTTP with the previous software's default credentials. Before you put it on a network, change three things: the storage credentials, the default access key pair that falls through to the old default, and the public URL scheme, since the example environment file says so itself and the compose file shows why.
Frequently asked questions
How do I self-host Craftplan without cloning the repository?
Download the compose file and the example environment file with curl, copy the environment file to `.env`, fill in the required secrets, then run `docker compose up -d`. That starts Craftplan, PostgreSQL and SeaweedFS with database migrations running automatically.
Which object storage does Craftplan use?
SeaweedFS, reached through the S3 API and configured with AWS-prefixed variables and a conventional default region. The compose file still names the service after the software it replaced and still falls back to that software's default credentials unless you set them.
What secrets does Craftplan need before it will start?
Four, all blank in the example file with their generation commands in comments: a Phoenix secret key of at least 64 bytes, a token signing secret for API authentication, a 32-byte AES key for the encryption layer that stores provider credentials, and a PostgreSQL password.
Can Craftplan send transactional email, and to which providers?
Yes, configured from the interface. It supports a local SMTP path plus five hosted providers, and provider API keys are encrypted at rest. Development starts a local mail catcher alongside the other services.
What does the Craftplan API expose?
Both JSON:API and GraphQL endpoints for programmatic access, with API key authentication stored encrypted and CORS configuration available. Authorization is policy-based across all resources, with separate admin and staff roles.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/puemos-craftplan)Star history chart for your README
[](https://hysenlabs.com/projects/puemos-craftplan)Was this useful?