Decepticon: an autonomous red team agent that runs as a Docker stack
Autonomous Hacking Agent for Red Team
At a glance
- What is it?
- An autonomous red team agent with a benchmark table: the model gateway container can mount your coding agent's credential files, per-package versions are stamped from a git tag at image build time, and the repository carries three different organisational names.
- Who is it for?
- Decepticon is an autonomous red team agent that runs as a Docker stack with a terminal CLI, an on-demand web dashboard and on-demand specialist workloads. Three things to settle before a run.
- Can I use it commercially?
- Yes. Apache-2.0 is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository received new commits within the last day.
- What is it written in?
- Mainly Python, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
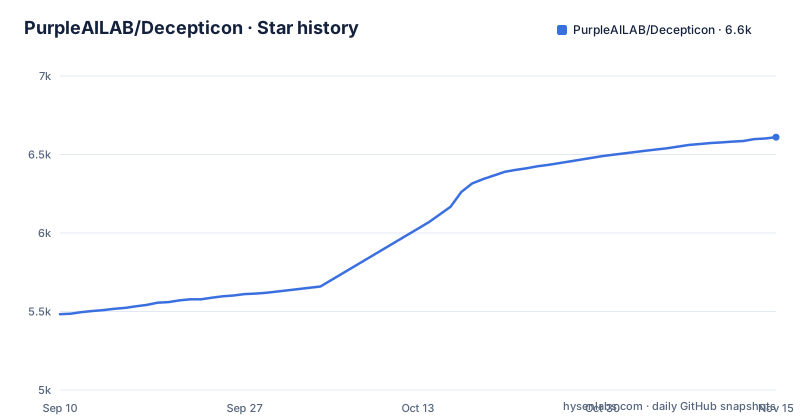
- PurpleAILAB/Decepticon6,610 ★ · +1,127
| Repository | 2026-09-10 | 2026-11-15 |
|---|---|---|
| PurpleAILAB/Decepticon | 5.5k | 6.6k |
1,127 Stars in the last 66 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The agent writes its own rules of engagement before it acts
The README opens by asking whether this is another AI hacker that runs nmap and writes a report.
The specialist workloads named as examples are BloodHound CE, Sliver C2 and REA/Ghidra, and they come up on demand, with the orchestrator spawning them via calls such as `ops_start("ad")`, rather than starting with the core stack.
Nothing in the described design checks that the target is the client's
The README's CLI notes refer to engagements and target authorization: `/new` starts a fresh conversation in the same engagement and mode, and it does not create another engagement or change target authorization.
The installer pipes a remote script to a shell, and the gateway mounts your agent credentials
Two security surfaces in the deployment are worth naming before anything else.
The first is the install path. On macOS, Linux or a WSL2 environment it is a single line that fetches a script from the project's own domain and pipes it into a shell, with no checksum and no signature shown. The Windows path is the PowerShell equivalent. Prerequisites are Docker and Docker Compose v2, and the platform claim is broad: macOS on both Apple Silicon and Intel, Linux on both architectures, and Windows on both, natively through PowerShell or through WSL2.
The second is in the compose file, and it is the one that surprises people. The model gateway service mounts two credential files into the container by host path:
${CLAUDE_CREDENTIALS_VOLUME:-/dev/null}:/root/.claude/.credentials.json
${CODEX_AUTH_VOLUME:-/dev/null}:/root/.codex/auth.json
Both default to `/dev/null`, so an install that does not set them gets an empty mount rather than a failure. If you do set them, the container running the language model proxy can read the stored credentials of your coding agent, and the comment elsewhere in the same file shows that the gateway is the component handling model routing, authentication, usage tracking and billing.
The same service publishes its port on the loopback address only, bound to 127.0.0.1 with a default port of 4000, so it is not reachable from the network. That is the right call and it is worth noticing that the credential mount is the part that is not restricted.
Two networks, a Kali sandbox, and a Docker socket in the path
The rest of the stack is split by lifetime rather than by trust. LiteLLM, PostgreSQL, Neo4j, Skillogy and the graph engine are always on. The web dashboard comes up on a command from inside the terminal interface. The specialist workloads come up only when the orchestrator calls a start function, and the README's own example of that call is written with a two-letter argument that it does not explain.
The published Python version is stamped from the git tag at image build
The Python packaging has an arrangement that is unusual enough to be worth reading twice.
The root project is named `decepticon-workspace` with version `0.0.0`, and a comment states that it is an umbrella that is never published, that per-package versions are stamped from the git tag at Docker build time, and that the root carries only shared tooling configuration so the development workflow runs uniformly.
Under the tool configuration, the umbrella declares that no wheel is built from it, the same comment repeating that real packages live under a packages directory and are built per their own wheel configurations. So the root project exists to be a virtual root for a workspace, not to be installed.
Three real packages are declared as workspace members and dependencies: the core package, a framework package, and an SDK package. The README's pip section installs `decepticon`, which it calls the core SDK, plus an extra for the knowledge graph tools, and it describes what arrives: agent factories, middleware, tools and skills, with model calls and sandbox execution routed over HTTP to services that have to be running.
The consequence of stamping versions at image build is that the version in a wheel and the tag in the container image are produced by the same event, which is good for traceability and bad for pinning. Anything that resolves a version at install time is resolving against whatever the build wrote, not against a manifest in the tree.
The extras are also declared twice, once on the umbrella as a passthrough and once on the real package, and the comment explains why: the tool treats extras as per project, so without the passthrough the extra is invisible from the root.
The enabled plugin set depends on the directory you launch from
One configuration key decides what the agent can load, and where it is read from is unusual.
The project-level plugin activation is read by the plugin loader from the pyproject file in the current working directory. The comment says it is kept at the workspace root so the in-checkout development workflow activates both open source bundles automatically, without every contributor having to remember an environment variable.
The fallback is spelled out too. Installs that do not clone the repository fall back to a hardcoded list containing one entry, and the downstream container images override it through an environment variable holding a comma-separated pair.
So there are three sources for one setting, in ascending order of specificity: a hardcoded default with one bundle, a pyproject file whose location depends on where you are standing, and an environment variable that the images set. Launching the same installation from a different directory can therefore change which plugins are active.
The same comment block is a decent description of the plugin model as a whole: a loader that reads configuration from the project rather than from the package, and a plugin set that differs between a developer checkout, an end user install and a vendor build.
Three organisational names, two package ecosystems, and fourteen lint configurations
The repository carries more identities than a project usually does.
It sits under one organisation. The compose file pulls prebuilt images from a different organisation's package registry. And the sponsor link in the support section points at a third account. All three appear in files a user will read during installation.
There are also two package ecosystems, because there is a Python side and a web side. The web manifest declares workspaces covering two client directories and carries exactly one runtime dependency, an ORM client, with its own tool as a development dependency. Its scripts run the web client under clients/web, including generating and running that ORM's migrations.
The lint configuration is where the project's size shows. Counting the configuration files at the root gives formatting and static analysis for four languages plus one for the shell, a semantic security scanner directory, an audit ignore file for Python packages, a pre-commit configuration, a Python version pin, and separate configuration for the container files, the markdown and the YAML. One of them is a Go linter, in a repository whose visible languages are Python and TypeScript.
Alongside that sit the documents a security-relevant project should have and many do not: a security policy, a release guide, a contributing guide written separately for agents, a code of conduct, a telemetry document, and a third-party licences file.
Editorial conclusion
Decepticon is an autonomous red team agent that runs as a Docker stack with a terminal CLI, an on-demand web dashboard and on-demand specialist workloads. Three things to settle before a run. What the telemetry gateway sends, which the repository documents in TELEMETRY.md. What credentials the model gateway container can read, since it mounts your Claude and Codex credential files when those variables are set. And which plugin set is active, since it depends on the pyproject in the directory you launch from and on DECEPTICON_PLUGINS.
Frequently asked questions
What is Decepticon?
An autonomous red team agent for authorised security testing, published as a Python SDK with a core package and an optional knowledge-graph extra. Its default start brings up a core management plane of LiteLLM, PostgreSQL, Neo4j, Skillogy, LangGraph and a sandbox, with specialist workloads such as BloodHound CE, Sliver C2 and REA/Ghidra spawned on demand.
How do I install Decepticon?
You need Docker and Docker Compose v2. On macOS, Linux or WSL2 the documented step is curl -fsSL https://decepticon.red/install piped into a shell, then decepticon onboard for the setup wizard and decepticon to start the stack. Windows uses a PowerShell equivalent.
Does Decepticon check that a target is one I am authorised to test?
The README's CLI notes refer to target authorization within an engagement: `/new` starts a fresh conversation in the same engagement and does not create another engagement or change target authorization.
What benchmark results does Decepticon publish?
A table against a suite the project calls its validation benchmarks: 45 of 45 on the easy level, 50 of 51 on medium, 7 of 8 on hard, and 102 of 104 overall. The figures are the project's own, and the suite lives in a separate repository.
Does Decepticon send telemetry?
Telemetry is a documented part of the stack: the repository carries a telemetry document at its root and a telemetry gateway service directory alongside the model gateway, the databases and the sandbox. What is collected is described in that document.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/purpleailab-decepticon)Star history chart for your README
[](https://hysenlabs.com/projects/purpleailab-decepticon)Was this useful?