Bandit: an AST security linter for Python that never runs your code
Bandit is a tool designed to find common security issues in Python code.
At a glance
- What is it?
- Bandit reads Python source, builds an AST for every file and runs plugins against the nodes, which makes its findings reproducible and reviewable but keeps it blind to how a value travelled to reach the line it flags. It is a security-only report you can gate a repository on, not a substitute for reading the call paths that matter.
- Who is it for?
- Bandit earns its place in a repository that wants a security-only scan it can run as its own gate, from the signed ghcr.io image or as a pre-commit hook, and a finding that points at a node is evidence you can put in a review. It does not tell you whether an `exec()` call is reachable from untrusted input, so a team whose real risk sits in the call paths needs more than a clean report.
- Can I use it commercially?
- Yes. Apache-2.0 is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 6 days ago.
- What is it written in?
- Mainly Python, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
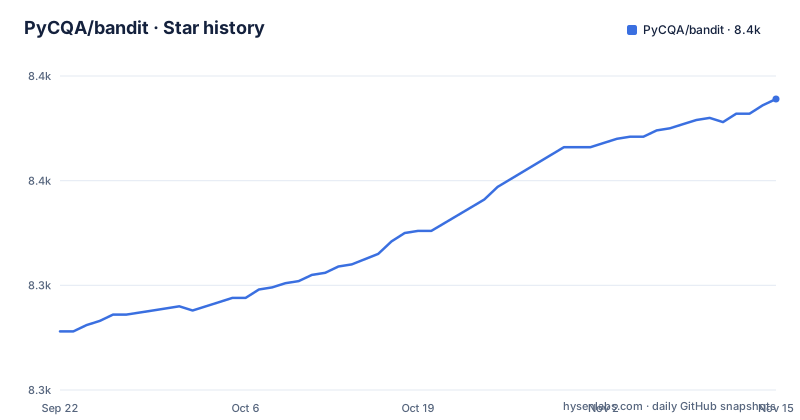
- PyCQA/bandit8,389 ★ · +111
| Repository | 2026-09-22 | 2026-11-15 |
|---|---|---|
| PyCQA/bandit | 8.3k | 8.4k |
111 Stars in the last 54 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Every file becomes an AST, and plugins read the nodes
Bandit does not watch a program run. It reads source. The stated pipeline is short: process each file, build an AST from it, run the appropriate plugins against the AST nodes, and generate a report once every file has been scanned. No runtime instrumentation appears in that description, and nothing in it feeds network state or environment into a rule.
That design is what makes the output arguable. A finding names a node in a file you can open, which is something a runtime detector cannot offer, and the report arrives once at the end of the scan rather than interleaved with execution.
The project began inside the OpenStack Security Project and was later rehomed to PyCQA. It is released under the Apache 2.0 licence, and `setup.py` carries the SPDX identifier in its header. Documentation is published at bandit.readthedocs.io, and bugs and pull requests go to the GitHub repository.
The examples directory is where the rule surface shows through
The `examples/` directory is the closest thing to a rule catalogue the repository offers. Each file is a small program written to trip a rule: `eval.py`, `exec.py`, `assert.py`, `dill.py`, `crypto-md5.py`, `ciphers.py`, `cipher-modes.py`, `hardcoded-passwords.py`, `hardcoded-tmp.py`, `ftplib.py`, `flask_debug.py`, `httpoxy_twisted_script.py`, `django_sql_injection_raw.py` and `huggingface_unsafe_download.py`.
Read as a group, those names describe coverage better than any summary would. The rules reach into Django query construction, Flask debug mode, the httpoxy CGI environment variable, Twisted's directory handling, the insecure hashlib functions, cipher modes, and deserialisation through dill. A Python shop gets checks aimed at the frameworks it already depends on instead of a generic scan of the standard library.
What the README does not do is enumerate plugin identifiers, severity levels or their defaults. That reference lives in the documentation site.
Per-node rules cannot follow a value to where it is used
Here is the boundary, stated in the project's own terms. Plugins run against AST nodes, so a rule sees one node at a time. Nothing in that pipeline carries a value from the place it entered the process to the place it is consumed, which means a rule cannot report that a string arrived from a request object and reached a subprocess call two functions later.
The consequence is work left on the reader. Findings land where the code is written: the hardcoded password where it appears, the Flask debug flag where it is set. Deciding whether an `exec()` call is reachable from untrusted input remains a job for a human reading the call path, and Bandit produces nothing on that path.
Suppression is the second gap. The README documents no baseline file, no per-rule skip and no severity threshold; it covers obtaining the tool and points at the documentation site. The levers it does describe are the code itself and the plugin set that runs over it.
colorama arrives only on Windows, and package order matters
`requirements.txt` is short and annotates each dependency with its licence: PyYAML>=5.3.1 (MIT), stevedore>=1.20.0 (Apache-2.0), rich (MIT), and colorama>=0.3.9 guarded by the marker `platform_system=="Windows"` (BSD 3 clause).
Two things follow from those four lines. A Windows install and a Linux or macOS install do not receive the same set of packages, because the colorama line is behind a platform marker instead of being installed everywhere. And the file opens with a comment saying the order of packages is significant, because pip processes them in order of appearance and changing that order has an impact on the integration process and can wedge the gate.
`setup.py` sets `python_requires=">=3.10"`, so packaging refuses an install on an older interpreter. The same file declares `setup_requires=["pbr>=2.0.0"]` and `pbr=True`, which means the metadata is handed to pbr and no version literal appears in `setup.py` at all.
The documented install is a container image, and it arrives signed
The install path the README spells out is the container image, built inside the repository by GitHub Actions and published on ghcr.io:
docker pull ghcr.io/pycqa/bandit/banditImages are published for amd64, arm64, armv7 and armv8. When a machine needs one specific architecture, the platform goes in the `--platform` option, with `<architecture>` standing in for the one you want:
docker pull --platform=<architecture> ghcr.io/pycqa/bandit/bandit:latestEvery image is signed with sigstore cosign, so its origin can be checked against the workflow that built it. `<version>` is the release version of Bandit:
cosign verify ghcr.io/pycqa/bandit/bandit:latest \
  --certificate-identity https://github.com/pycqa/bandit/.github/workflows/build-publish-image.yml@refs/tags/<version> \
  --certificate-oidc-issuer https://token.actions.githubusercontent.com
Where the README stops is invocation: it gives no command for starting the container, no entry point and no command line for the tool itself. How to point the scan at a path or a set of options comes from bandit.readthedocs.io, and the PyPI project page linked from the README badge is the other distribution route.
The man page installs only when doc/build/man/bandit.1 is already there
`setup.py` carries one detail that decides whether you get a manual page at all. It computes `man_path = "doc/build/man/bandit.1"` and appends that path to `data_files` under `share/man/man1` only when `os.path.isfile(man_path)` returns true.
The man page is therefore conditional on the build tree already containing that file. Build from a source checkout where the documentation has not been built and the file list stays empty; build from an artefact where the file exists and the page installs into the system man path. Nothing in the packaging metadata announces which case you are in, and because `doc/` is a top-level directory rather than a checked-in page, the file is generated during the documentation build.
That is the only conditional logic in the packaging. Everything else is delegated to pbr, which reads metadata from elsewhere in the tree.
Pre-commit, tox and the gap the README leaves on running
Deployment is a choice the layout supports more clearly than the README explains. Two files at the repository root, `.pre-commit-config.yaml` and `.pre-commit-hooks.yaml`, are the shape a pre-commit integration takes, so the same scan can run over changed files before a commit lands. `tox.ini` and `.stestr.conf` sit next to `setup.py` and `test-requirements.txt`, `SECURITY.md` covers reporting a problem in Bandit itself.
The nearest neighbour in approach is Ruff, which folds the Bandit-derived security rules into a much wider linter that also reports style and typing problems. The trade is scope rather than depth: Bandit produces a security-only report, which suits a repository that already has a linter and wants the security scan to be a separate job, while one combined linter saves a second tool at the cost of mixing findings.
Funding is named in the README: Mercedes-Benz, Tidelift and Stacklok, with a `funding.json` in the tree. Releases 1.9.2, 1.9.3 and 1.9.4 shipped in November 2025, January 2026 and February 2026, and the last push was on 2026-11-02.
Editorial conclusion
Bandit earns its place in a repository that wants a security-only scan it can run as its own gate, from the signed ghcr.io image or as a pre-commit hook, and a finding that points at a node is evidence you can put in a review. It does not tell you whether an `exec()` call is reachable from untrusted input, so a team whose real risk sits in the call paths needs more than a clean report. Two things to check before adopting: that your interpreter clears the `>=3.10` floor declared in `setup.py`, and that your platform receives the dependency set `requirements.txt` marks for it.
Frequently asked questions
How do you use bandit for Python code?
Bandit processes each file, builds an AST from it, runs the appropriate plugins against the AST nodes, and generates a report after all files are scanned. The README documents obtaining it as a container image on ghcr.io rather than a command line, so invocation details come from the documentation site.
What does Bandit check in a Python project?
The `examples/` directory names the rule surface: `eval.py`, `exec.py`, `hardcoded-passwords.py`, `flask_debug.py`, `ftplib.py`, `crypto-md5.py`, `httpoxy_twisted_script.py` and `django_sql_injection_raw.py` among them. The README does not enumerate plugin identifiers or severities, so the full inventory is in the documentation at bandit.readthedocs.io.
Which Python versions does Bandit support?
`setup.py` sets `python_requires=">=3.10"`, so packaging refuses an install on anything older. The container image on ghcr.io is the other route, and the README states no Python version for it.
How do I pull the Bandit container image for one CPU architecture?
Images are published for amd64, arm64, armv7 and armv8. Use `docker pull --platform=<architecture> ghcr.io/pycqa/bandit/bandit:latest`, and verify the signature with cosign using the build workflow as the certificate identity.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/pycqa-bandit)Star history chart for your README
[](https://hysenlabs.com/projects/pycqa-bandit)Was this useful?