Pillow's build decides which image formats your install actually supports
Python Imaging Library (fork)
At a glance
- What is it?
- Pillow is the friendly fork of the Python Imaging Library, MIT-CMU licensed, and it is a compiled extension whose feature set depends on a dozen native libraries found at build time. The latest release is 13.0.0, the floor is Python 3.11, and there are no prebuilt Windows wheels for Python 3.16 or newer.
- Who is it for?
- Pillow suits Python work that needs to open, convert and process common image formats without leaving the interpreter, and its typed, mature classifier and active changelog make it a reasonable default.
- Can I use it commercially?
- Check first. The repository uses a licence we do not classify automatically, so read its LICENSE file before any commercial use.
- Is it still maintained?
- Yes. The repository received new commits within the last day.
- What is it written in?
- Mainly Python, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
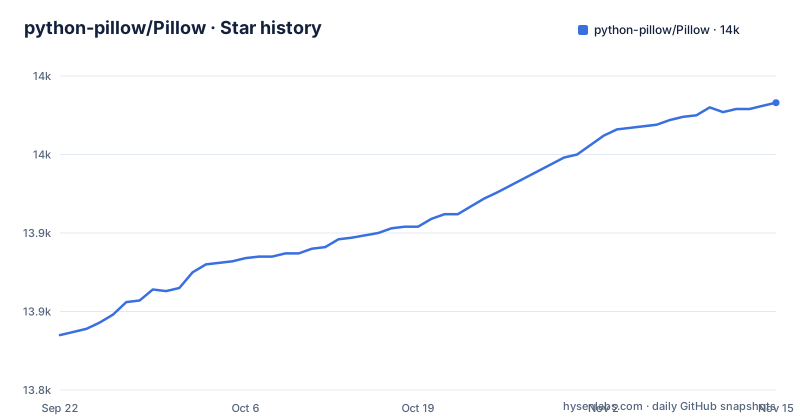
- python-pillow/Pillow13,983 ★ · +148
| Repository | 2026-09-22 | 2026-11-15 |
|---|---|---|
| python-pillow/Pillow | 13.8k | 14k |
148 Stars in the last 54 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
No prebuilt Windows wheel once you move to Python 3.16
The setup script registers an exit handler for one specific combination. On Windows, when the interpreter is 3.16 or newer, it warns that the current Pillow version does not support that Python and does not provide prebuilt Windows wheels. Everything below that threshold is a different story, and the repository runs dedicated workflows for Windows and for MSYS2 builds, plus a wheels workflow and a Docker test workflow. So the answer to whether Pillow installs cleanly is platform and interpreter specific in a way the README never states. For a team with a Windows fleet that upgrades Python, this is the constraint to check before you schedule the upgrade. A source build on that configuration is not blocked, but it turns a pip install into a toolchain problem with a dozen optional native dependencies, and on a locked-down machine that often means a different Python version in your service rather than a patched build.
The build backend is a directory inside the repository, not setuptools
The build-system table does not name setuptools as the backend. It names a backend called backend, and points backend-path at _custom_build, a directory that exists in the repository, with pybind11 and setuptools 77 or newer in the requires list. So installing Pillow from source means pip has to import a Python module that ships inside the source tree, which is a different code path from the usual setuptools backend and a different failure mode when a build happens in a restricted environment. Anything that rebuilds wheels internally, some older build front ends, and offline or airgapped installers that vendor only the declared backend will meet this differently. If you maintain such a pipeline, verify it against a source build rather than assuming the published wheels cover your case, because the wheel path never touches that directory at all.
A dozen native library roots decide your format support
The setup script starts by setting a dozen roots to None and then looks for whatever the system provides: AVIF_ROOT, FREETYPE_ROOT, HARFBUZZ_ROOT, FRIBIDI_ROOT, IMAGEQUANT_ROOT, JPEG2K_ROOT, JPEG_ROOT, LCMS_ROOT, RAQM_ROOT, TIFF_ROOT, WEBP_ROOT and ZLIB_ROOT. That list is the honest answer to the question every Pillow user eventually asks, which is why a given image format opens on your laptop and not in your container. Font rendering pulls in FreeType with HarfBuzz and FriBidi, colour management pulls in LCMS, and the compressed formats pull in their own codecs. None of this appears in the README. The practical consequence is that your acceptance test has to be a format matrix run against the exact artifact you deploy, not a functional test run on your development machine.
The version string is parsed out of a Python file at build time
The project metadata marks version as dynamic, and the setup script fills it in by opening src/PIL/_version.py, reading the text and splitting it on a double quote to take the second field. So the single source of truth for what version you installed is a string literal inside a source file that only the build can see. This matters for the cases where the build is not the project's own. A packaging pipeline that rewrites metadata, or a downstream distribution that wants to record a version without running the build, sees no static version to read. It also means a build that edits _version.py, as release preparation does, changes the identity of the artifact in a way no field in pyproject would reveal. If you pin Pillow in a lockfile, verify the pin against the reported version at runtime rather than trusting what the build system printed during compilation.
The leak tests skip every mobile platform by construction
The test dependencies carry a comment that explains a gap in the safety net. The leak tests only run on Linux and macOS, because psutil, which they rely on, does not support iOS at all and ships no wheels for Android. The rest of the test extra includes coverage, defusedxml, markdown2, olefile and packaging, and the optional extras pull olefile in for the FPX and MIC codec work. The consequence is asymmetric coverage on exactly the platforms where memory pressure matters most. A decoder change that leaks on iOS will not fail any workflow the project runs, and a green build there means the platform was never observed, not that it was verified. If your product ships on mobile, plan to run your own memory checks on those devices rather than inheriting the assumption that CI covered them, and treat mobile regressions as yours to catch.
The repository license metadata says NOASSERTION while pyproject says MIT-CMU
Two places describe the licence and they do not use the same words. The project metadata declares license as MIT-CMU with the LICENSE file listed alongside it, while the licence field reported by the hosting platform for this repository is NOASSERTION, the value used when a licence cannot be classified automatically. Nothing is wrong legally, but scanners and policy gates read the metadata field, and a NOASSERTION value is a common reason a dependency scan stalls or a legal review request appears weeks before a release. If your intake process is automated, capture the licence from the LICENSE file or from the metadata table directly instead of forwarding the platform value. Worth noting alongside it: the classifiers declare Development Status 6 Mature and Typing Typed, and both are the kind of detail that changes what a reviewer asks about, so keep them together in whatever record you keep.
Doc link checking is deliberately made non-blocking
The Makefile defaults to help rather than a build, and prints the target list for contributors. Among the targets is doccheck, which builds the docs and then runs the link checker with the failure deliberately swallowed, prefixed by a comment explaining that the tests should not rely on documentation links being up on every build because the project does not control them. That is a defensible trade, and it has a cost. Links into external services rot quietly, so a contributor can follow a link in the handbook that no longer resolves and never learn it from CI. The same applies to the split between release notes and the changelog, which live in different places, with pre-fork changes kept in a section of CHANGES.rst. If you are onboarding, read the help output rather than guessing target names, and assume documentation freshness is something you verify yourself.
Security reports have two private channels and one prohibition
The vulnerability policy is short and specific. Sensitive findings go to GitHub as a private security advisory, and if GitHub is not an option, the Tidelift security contact is the fallback, with Tidelift coordinating the fix and the disclosure. The text states plainly that sensitive vulnerability information must not be reported in public. The two-channel arrangement has a practical effect on how your team runs disclosure intake. A researcher who cannot use GitHub will reach Tidelift, not your issue tracker, and that path runs on their timeline rather than yours. So if you run a coordinated disclosure programme around Pillow, or you want a fix to be patched rather than merely reported, the advisory route and the Tidelift contact are the two addresses that matter, and the public issue tracker is not one of them. Tidelift has also funded development since 2018, alongside Thanks.dev since 2023 and GitHub Sponsors since 2026.
Editorial conclusion
Pillow suits Python work that needs to open, convert and process common image formats without leaving the interpreter, and its typed, mature classifier and active changelog make it a reasonable default. Check three things first: whether the wheel for your platform bundles the codecs you need, since format support follows the build, not the release note; whether Python 3.16 on Windows is in your fleet, since no prebuilt wheel is provided there; and whether your licence scanner reads MIT-CMU rather than the NOASSERTION metadata.
Frequently asked questions
how to install pillow in python
The README carries no install command. It links the installation page in the documentation at pillow.readthedocs.io, plus a PyPI project page and a best practices entry, and it points to a docs site and a contribution guide rather than a pip invocation.
how to use pillow in python
The package is imported as PIL. Pillow adds image processing to the Python interpreter with extensive file format support, an efficient internal representation, and fast access to data held in a few basic pixel formats, with the handbook linked from the README for task oriented guidance.
Which Python versions does Pillow support?
The project metadata requires Python 3.11 or newer and declares classifiers for 3.11 through 3.15, on both CPython and PyPy. On Windows with Python 3.16 or newer, the setup script warns that Pillow does not support that version and provides no prebuilt Windows wheels.
Why does building Pillow from source need extra libraries?
The setup script resolves a dozen optional native dependencies by looking for their roots on the system: AVIF, FreeType, HarfBuzz, FriBidi, ImageQuant, JPEG 2K, JPEG, LCMS, Raqm, TIFF, WebP and zlib. Which of them are found at build time determines which formats and features the compiled extension actually has.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/python-pillow-pillow)Star history chart for your README
[](https://hysenlabs.com/projects/python-pillow-pillow)Was this useful?