QOR: a Go rewrite split across nine sibling repositories
QOR is a set of libraries written in Go that abstracts common features needed for business applications, CMSs, and E-commerce systems.
At a glance
- What is it?
- QOR packages admin interfaces, staged publishing, state machines, asset management and access control as separate Go modules. The catch is that you assemble them yourself, and the last tag is from 2022.
- Who is it for?
- QOR fits teams that already write Go services and want an admin surface, a publish workflow or a state machine without building one, and it does not fit anyone looking for a finished CMS. Before you commit, read the module list and count how many you actually need, plan for gorm on its v1 line, and pin the exact commit you start from, since the newest tag is v1.3.0 from 2022 while commits continued to 2026-11-02.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 3 days ago.
- What is it written in?
- Mainly Go, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
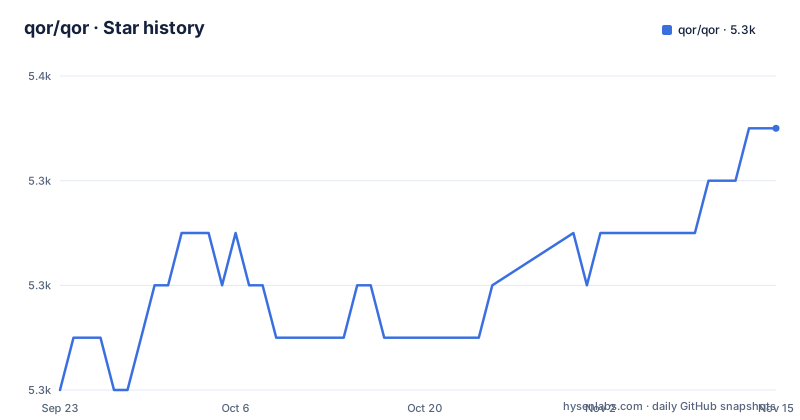
- qor/qor5,349 ★ · +5
| Repository | 2026-09-23 | 2026-11-15 |
|---|---|---|
| qor/qor | 5.3k | 5.3k |
5 Stars in the last 53 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
A Go rewrite of a framework that used to live inside one company
The project's own history explains its shape. QOR began as a proprietary framework written in Ruby on Rails and used internally at The Plant, then got rewritten in Go. Version 1.0 was the first release open sourced, under the MIT license, and that rewrite is what sits in this repository today.
The same history sets expectations. The documentation is blunt that QOR is not a boxed turnkey solution, that you need proper coding skills to use it, and that it is designed to make developers' lives easier when building complex systems rather than handing one over ready to run. Everything else follows from that sentence: you get libraries, and the application around them is yours to write.
Two entry points carry the rest of the detail. Written documentation sits at doc.getqor.com, and a live admin runs at demo.getqor.com/admin with its own source in the qor-example repository, which is the fastest way to see how the pieces are supposed to fit together before you commit to any of them.
The scope is nine sibling repositories and three Go files
The module list is the whole scope, and each entry is a separate repository: admin, which generates an admin interface and a RESTful API over your data; publish, a staging environment where content changes are reviewed before going live; transition, a configurable state machine for states, events and transition constraints; media_library, asset management across several cloud storage backends with CDN publishing; worker, a process scheduler for batch work; exchange, moving data in and out through CSV or Excel; i18n for managing and inline editing translations; l10n for per-locale models with localizable attributes and locale-based querying; and roles, described in one line as access control.
This repository is the glue rather than the payload. At its root sit config.go, context.go, errors.go and utils/, plus resource/, test/, test_all.sh and a script named update_all_qor_repos.sh. The Go module manifest is what ties the siblings together, requiring qor/admin, qor/publish2, qor/roles, qor/sorting and qor/validations directly and pulling in another dozen QOR modules indirectly.
go.mod pins gorm v1.9.16 and a bluemonday release from 2022
The manifest is short and the versions are old in a specific way:
module github.com/qor/qor

go 1.26.10

require (
	github.com/jinzhu/gorm v1.9.16
	github.com/lib/pq v1.8.0
	github.com/microcosm-cc/bluemonday v1.0.27
	github.com/qor/admin v1.2.1-0.20251125093313-4a292fdc9c5d
)
Two things stand out. The data layer is gorm v1.9.16 on the jinzhu/gorm import path, which is the first major line of that library, paired with lib/pq v1.8.0 and go-sql-driver/mysql v1.5.0 for the two supported databases. The HTML sanitizer is microcosm-cc/bluemonday v1.0.27, and the most recent release of this project, v1.3.0, was cut for exactly that reason: its note reads upgrade bluemonday.
Against those sits the go directive, which reads go 1.26.10. A modern toolchain on the first line and older library versions underneath is the combination to plan for, because any Go upgrade you make to QOR will be constrained by what jinzhu/gorm v1 and bluemonday v1 allow.
The newest tag is v1.3.0 from 2022 while commits continue
Release tags and repository activity have drifted apart. The tag history is v1.1 on 2019-04-23, v1.2.0 on 2021-06-30 and v1.3.0 on 2022-11-14, while the last push to the default branch landed on 2026-11-02 and the archive flag is off. So the code is moving and the tags are not.
That gap decides how you consume it. There is no 1.4 to wait for and no release notes describing what changed after 2022, so a version constraint on github.com/qor/qor buys you code from 2022 while the master branch is four years further along. Note how the manifest itself handles this: qor/admin is not pinned to a tag at all but to the pseudo-version v1.2.1-0.20251125093313-4a292fdc9c5d, which encodes a commit from 2025-11-25. Same for publish2, roles, sorting and validations, all pinned by commit rather than release.
If you pin tags you get old code, and if you track master you get a moving target with no changelog. Write down the commit hash you start from, because nothing in the repository will tell you later what you were running.
The docs say npm install while the repository ships a yarn.lock
The frontend section requires Node.js and Gulp, and its setup line is one command:
npm install && npm install -g gulpThen two tasks, one for watching and one for building:
gulp
gulp release
Watch recompiles as SCSS and JavaScript change, and gulp release builds the release files. What the repository actually commits alongside that is a yarn.lock, not a package-lock.json, so the documented npm path and the committed lockfile describe two different resolutions of the same manifest. bower.json is there too, a leftover from an era when frontend assets were pulled by Bower rather than npm.
There is also no Go example anywhere in the README. Every code sample you would want for wiring up admin or transition lives behind doc.getqor.com, which means the repository itself will not tell you how to start the server, which database handle to pass, or what a QOR context looks like. Budget time for the documentation site, because the source alone is not a tutorial.
gulp 5 with exact pins on two plugins and a global install
The asset build is a gulpfile.js driven by a modern gulp and a mixed bag of plugins:
"devDependencies": {
  "gulp": "^5.0.0",
  "gulp-babel": "8.0.0",
  "gulp-sass": "5.1.0",
  "event-stream": "4.0.1"
}
gulp 5 sits next to @babel/core and @babel/preset-env at ^7.24.4, gulp-clean-css, gulp-concat, gulp-plumber, gulp-rename and gulp-uglify. Three packages are pinned to an exact version rather than a caret range, gulp-babel at 8.0.0, gulp-sass at 5.1.0 and event-stream at 4.0.1, which means those three never move on their own when you install.
The setup line also installs gulp globally, even though the manifest keeps gulp in devDependencies and puts gulp-cli in the regular dependencies. Both routes work, but a global install means two gulp binaries can exist on one machine and the version each task picks up depends on your PATH. For CI, run the local binary and let the manifest decide.
Continuous integration is Travis: a .travis.yml at the root and a Travis badge in the README, alongside a .codeclimate.yml for the code quality service. There is no workflow directory, so if your pipeline is not Travis, the build definition is yours to write.
Sessions and cookies only reach the build as indirect dependencies
Read the indirect block in go.mod and the shape of the system appears. gorilla/sessions, gorilla/securecookie and gorilla/context sit there alongside qor/session, qor/middlewares and qor/responder, plus the qor/publish and qor/l10n modules. No QOR module in the README list claims session handling as its job.
Access control is delegated to a single sibling, qor/roles, described in the module list only as access control. The README module list names no authentication module, password handling, multi-tenancy or billing, though it also points to more modules under github.com/qor. Any of those is your code, composed on top of the session and cookie packages the build already carries.
There is a related note on how to report a problem. Security issues are supposed to go to an email address before anything is posted as an issue or raised on a public forum, and the project asks for time to respond first. The README also links two chat rooms at the top, one English and one Chinese.
Editorial conclusion
QOR fits teams that already write Go services and want an admin surface, a publish workflow or a state machine without building one, and it does not fit anyone looking for a finished CMS. Before you commit, read the module list and count how many you actually need, plan for gorm on its v1 line, and pin the exact commit you start from, since the newest tag is v1.3.0 from 2022 while commits continued to 2026-11-02.
Frequently asked questions
What is QOR in business software?
QOR is a set of libraries written in Go that abstracts features common to business applications, CMSs and e-commerce systems, such as admin interfaces, staged publishing, state machines and asset management. The documentation is explicit that it is not a boxed turnkey solution and that you need proper coding skills to use it.
Which repositories make up qor/qor?
Nine siblings named in the module list: admin, publish, transition, media_library, worker, exchange, i18n, l10n and roles. The qor repository itself holds config.go, context.go, errors.go and utils, plus the go.mod that requires admin, publish2, roles, sorting and validations.
How do you build the QOR frontend assets?
Node.js and Gulp are required. The setup line is npm install && npm install -g gulp, then gulp watches SCSS and JavaScript changes while gulp release builds the release files. The repository ships a yarn.lock rather than a package-lock.json.
Which Go version and database layer does qor/qor require?
The go.mod declares module github.com/qor/qor with go 1.26.10, and its data layer is jinzhu/gorm v1.9.16 with lib/pq v1.8.0 and go-sql-driver/mysql v1.5.0. HTML sanitizing comes from microcosm-cc/bluemonday v1.0.27.
How should a QOR security issue be reported?
Email [email protected] and give the maintainers time to respond before posting the issue publicly or raising it on a forum. Ordinary discussion happens in the English and Chinese chat rooms linked from the README.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/qor-qor)Star history chart for your README
[](https://hysenlabs.com/projects/qor-qor)Was this useful?