Qtap: an eBPF agent that reads TLS traffic before encryption, and a container recipe that mounts the Docker socket
Qtap: An eBPF agent that captures pre-encrypted network traffic, providing rich context about egress connections and their originating processes.
At a glance
- What is it?
- A kernel-level network agent that attaches to TLS functions, hands plaintext to plugins with process and container context, and ships a Go package you can embed without starting the agent at all. The documented container run asks for privileged mode, host process ids and the Docker socket, which is the price of the visibility.
- Who is it for?
- Qtap is the right shape for the problem it names: seeing what an application actually sends, without proxies, certificates or code changes, and attributing it to a process and container. Weigh three things before deploying it anywhere shared.
- Can I use it commercially?
- Yes. Apache-2.0 is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 2 days ago.
- What is it written in?
- Mainly C, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
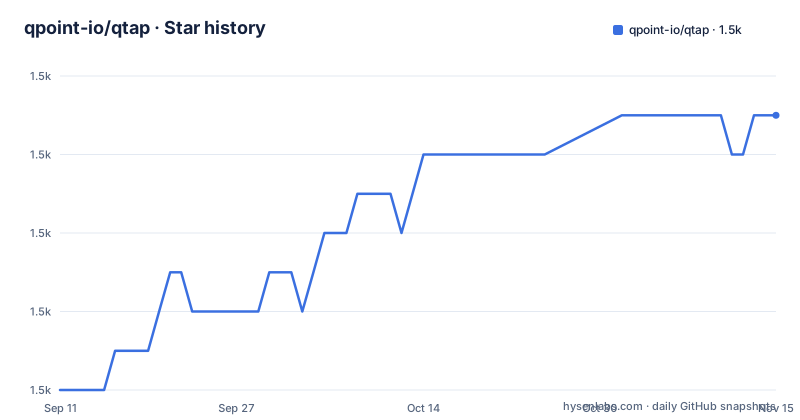
- qpoint-io/qtap1,465 ★ · +7
| Repository | 2026-09-11 | 2026-11-15 |
|---|---|---|
| qpoint-io/qtap | 1.5k | 1.5k |
7 Stars in the last 65 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Intercepting on both sides of the TLS call
The mechanism is stated in one paragraph and it is the whole idea. Qtap is an eBPF agent that captures traffic flowing through the Linux kernel, and it works by attaching to TLS and SSL functions, so data is intercepted before and after encryption and then passed to plugins. The claim is that this shows exactly what is being sent and received in original, unencrypted form, while operating out of band with minimal overhead, without adding latency or disrupting application performance. What the plugins receive is not just bytes but context: process, container, host, user and protocol. That attribution is what separates it from a packet capture, and it is why the file positions Qtap as something you can bolt onto an existing observability pipeline or use as the base of a product, with a list of seven uses running from security auditing to validating that an application change did not alter communication patterns.
Two curl lines, both handed straight to a root shell
The quick start offers a throwaway instance and a real install, and both are one line:
# Run Qtap in demo mode
$ curl -s https://get.qpoint.io/demo | sudo sh# Install the Qtap agent
$ curl -s https://get.qpoint.io/install | sudo sh
# Run with defaults!
$ sudo qtapDemo mode is described as a temporary instance that shows traffic in real time in the terminal, which is the cheapest way to see whether the agent attaches at all on your kernel. The install line downloads and pipes a script into a root shell, and the following line runs the resulting binary with defaults, meaning no configuration file is required to start. If you do want one, the examples directory carries a sample-config.yaml alongside capture samples for MinIO, Fluent Bit configuration, container monitoring and four OpenTelemetry eventstore variants, including a ClickStack object store target and a stdout target.
The container recipe takes privileged mode and the Docker socket
Running inside Docker is documented with a full command, and it is worth reading line by line:
docker run \
    --user 0:0 \
    --privileged \
    --cap-add CAP_BPF \
    --cap-add CAP_SYS_ADMIN \
    --pid=host \
    --network=host \
    -v /sys:/sys \
    -v /var/run/docker.sock:/var/run/docker.sock \
    -e TINI_SUBREAPER=1 \
    --ulimit=memlock=-1 \
    us-docker.pkg.dev/qpoint-edge/public/qtap:v0 \
    --log-level=info
Each flag has a reason. Root user, privileged mode and CAP_SYS_ADMIN get the agent the kernel access eBPF loading needs, CAP_BPF is the capability that governs it directly, host process ids are what let it attribute traffic to a process outside the container, host networking avoids a second hop, and the sys filesystem mount exposes BTF. The memory lock limit is set to unlimited because BPF maps are charged against it. The two entries with no technical explanation are the mounted Docker socket, which grants control of the container host, and the image tag, which is simply v0 with no version in it.
Kernel 5.10 with BTF, verified by looking for one file
The requirements section is short and checkable. Linux with kernel 5.10 or newer, with BPF Type Format enabled, and the file says you can verify it by checking whether /sys/kernel/btf/vmlinux exists on the system. eBPF must be enabled on the host. Then permissions: sudo on the host, or the container flags above. The development prerequisites add more. Go 1.27.1 or newer, make, and clang, with the note that version 14 is required, plus clang-tidy as optional. One line is aimed at a specific audience: macOS developers at Qpoint have used Lima as a quick Linux virtual machine for development, which tells you the agent is not expected to run on Darwin natively and that a VM is the supported path.
A Go package you can embed without starting the agent
Not everything has to run as a service. Go applications can use process.NewMonitor in pkg/process to construct a Linux process monitor, receive the existing lifecycle callbacks, and release its resources without starting the Qtap application. That is a smaller commitment than running the agent, and it is documented separately from the main flow, with a Go module example at examples/process-monitor covering usage, runtime requirements and callback limitations. The limits are called out rather than left implicit, which is the useful part. The tree shows the rest of the surface: bpf/ for the kernel programs, cmd/ and apps/ for entry points, pkg/ for packages including the DevTools app, internal/ for the rest, e2e/ for end-to-end tests, docs/, and scripts/. A jvm/ directory sits beside them, which the Dockerfile explains indirectly by installing a headless OpenJDK 17 in the build image.
Metrics on one port, traces through standard variables
Telemetry is split in two, and neither part requires a configuration file. Traces are enabled by setting OTEL_TRACES_EXPORTER and OTEL_EXPORTER_OTLP_PROTOCOL, with links to the OpenTelemetry documentation for both, so the agent speaks the standard exporter selection rather than a proprietary one. Metrics come from two endpoints on the same port, localhost:10001: /metrics for the activity you would put on a dashboard, and /system/metrics for the health of the agent itself, which is the split you want when the agent and the thing it watches need separate panels. A sample Grafana dashboard is included as a JSON file at examples/dashboards/qtap-http-overview.json, so the panel layout is available rather than described. The OTEL samples in the examples directory cover gRPC and HTTP eventstore targets, a ClickStack object store and a stdout target, which is the shape a custom pipeline usually takes.
The version comes from git describe, the image is tagged v0
Version identity in this repository is soft in three directions at once. The Makefile sets VERSION from an environment variable or from git describe with the tags, always and dirty options, which means a commit hash when no tag is reachable, and there are no GitHub releases to tag from. The published container image is referenced as us-docker.pkg.dev/qpoint-edge/public/qtap:v0, a mutable major-version tag. The build image pins Go 1.27.1 and Node 24 as build arguments, clones bpftool at tag v7.5.0 for building libbpf, and symlinks the generic architecture headers into place for the eBPF compile step. Tooling runs through the module rather than a global install: golangci-lint and govulncheck are both invoked as go tool subcommands, and the tree carries a .govulncheck-allow file, the allowlist that tells the vulnerability scanner which findings to ignore.
Two model SDKs inside a packet agent
The Go module is where the project's real shape shows. It requires cilium/ebpf for the kernel side, containerd and the Docker client for containers, gopacket, prometheus client, cobra for the command line, testcontainers for tests, and the OpenTelemetry exporters. It also requires the Anthropic SDK at version 1.58.0 and the OpenAI Go SDK at version 1.12.0, which is a choice worth noticing in an agent whose stated job is to observe egress traffic. Two proprietary model APIs sit in the dependency list of a tool that claims to be a foundational component for a custom solution. Four examples directories cover adjacent integrations, container monitoring, Fluent Bit, HTTP access logs and the process monitor, and the closing section of the file describes the project as early development, with APIs that may change and documentation that may be incomplete.
Editorial conclusion
Qtap is the right shape for the problem it names: seeing what an application actually sends, without proxies, certificates or code changes, and attributing it to a process and container. Weigh three things before deploying it anywhere shared. The privilege set in the documented Docker run is broad, privileged mode plus host process ids plus a mounted Docker socket, which is close to root on the host and should be scoped to a machine you own. The version identity is soft, since no GitHub releases exist and the Makefile derives its version from git describe with a fallback to a commit hash, while the published image is tagged v0. And the file describes the project as early development with APIs that may change. For local investigation the demo mode is the low-risk way in.
Frequently asked questions
What is Qtap?
An eBPF agent that captures traffic flowing through the Linux kernel. By attaching to TLS and SSL functions it intercepts data before and after encryption and passes it to plugins together with context such as process, container, host, user and protocol, so you can see what an application actually sends without modifying apps, installing proxies or managing certificates.
What does Qtap require before it will run?
Linux with kernel 5.10 or newer and BPF Type Format enabled, which you can check by looking for /sys/kernel/btf/vmlinux, plus eBPF enabled on the host. It needs elevated permissions: sudo on the host, or in Docker the combination of CAP_BPF, host process ids and privileged mode. Building it needs Go 1.27.1 or newer, make and clang version 14.
How do I try or install Qtap?
For a temporary trial, curl -s https://get.qpoint.io/demo piped into sudo sh starts a demo instance that shows traffic in the terminal in real time. To install, curl -s https://get.qpoint.io/install piped into sudo sh, then run sudo qtap to start it with defaults. Sample configuration files live in the examples directory.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/qpoint-io-qtap)Star history chart for your README
[](https://hysenlabs.com/projects/qpoint-io-qtap)Was this useful?