Quinn: one UDP socket, three crates, and a sans-io core
Async-friendly QUIC implementation in Rust
At a glance
- What is it?
- Quinn splits QUIC into a tokio-bound quinn crate, a sans-io quinn-proto state machine, and quinn-udp sockets. That split decides where your buffer tuning, certificate logic and event loop live, and it is also where the rough edges are.
- Who is it for?
- Quinn fits a Rust team that wants QUIC behind a tokio-shaped async API and is willing to own the socket and certificate details: one endpoint is one UDP socket, so the sizes you set for SO_SNDBUF and SO_RCVBUF decide throughput before any quinn code runs, and certificate validation is on unless a rustls override says otherwise.
- Can I use it commercially?
- Yes. Apache-2.0 is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 2 days ago.
- What is it written in?
- Mainly Rust, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 21, 2026, and from our analysis. They are not legal advice.
Star history
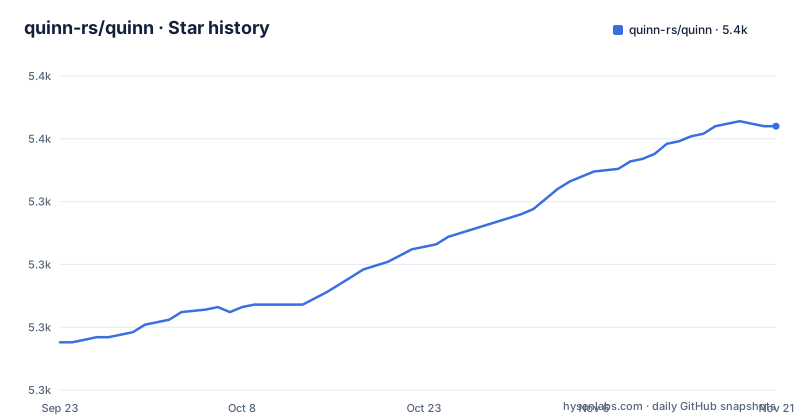
- quinn-rs/quinn5,355 ★ · +86
| Repository | 2026-09-23 | 2026-11-21 |
|---|---|---|
| quinn-rs/quinn | 5.3k | 5.4k |
86 Stars in the last 59 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Where quinn ends and quinn-proto begins
In the workspace overview, quinn is the high-level async API based on tokio, and the crate most developers end up depending on. quinn-proto underneath it is a deterministic state machine that performs no I/O internally, which is what the README ties to custom event loops and to a possible C or C++ API. quinn-udp sits at the bottom as UDP sockets carrying ECN information tuned for the protocol. The same listing names bench, benchmarks without any framework, and fuzz, fuzz tests.
The root Cargo.toml turns that layering into a build decision. Members are quinn, quinn-proto, quinn-udp, bench, perf, fuzz and docs/book, while default-members is quinn, quinn-proto, quinn-udp, bench and perf. A plain build at the root therefore skips the fuzz targets and the guide book under docs/book. If you vendor this workspace for a locked toolchain, default-members is the exact set you get without asking for more, and the members you add yourself are the ones that need a toolchain your CI may not have.
One endpoint is one UDP socket, and the kernel buffer is the ceiling
A Quinn endpoint is a single UDP socket, and it stays a single socket no matter how many connections run over it. That design is why the buffer warnings exist. Aggregate data rates high enough to matter can need a UDP buffer larger than the one most environments configure by default, and the symptom named in the documentation is erratic latency or erratic throughput over an otherwise stable network link.
The adjustment happens before Quinn ever sees the socket: change the SO_SNDBUF and SO_RCVBUF options on the UDP socket, then hand that socket to Quinn. On some platforms, Linux named among them, a process cannot raise those sizes without elevated privileges or modified system configuration. For readers running containers under a dropped capability set, or under a sysctl ceiling set by the host, the limit is not in Rust code at all. The tuning you need lives in the kernel, and skipping it turns a throughput problem into jitter that looks like packet loss.
Validation is on unless you turn it off yourself
Quinn clients check the cryptographic identity of the server they connect to. That stops an active on-path attacker from intercepting messages, and it also means somebody has to be trusted as a certificate authority. The straightforward arrangement is certificates from Let's Encrypt on the server and the default configuration on the client.
Several cases cannot use that arrangement: peer-to-peer, trust-on-first-use, deliberately insecure applications, and servers that are not identified by domain name. Arbitrary validation logic belongs in a customized rustls configuration, and the insecure_connection.rs example in the quinn crate shows how. For self-signed certificates, rcgen generates them on demand, and the workspace pins it at version 0.14. Trust-on-first-use carries one requirement that is easy to miss: a server generating its own certificate has to write it to persistent storage and reuse it on future runs. Skip that step and every restart hands clients a different key, which is how teams end up switching validation off to quiet the errors.
Running the example server and the client that fetches Cargo.toml
There is no install command in the README. The crates are published on crates.io with API docs on docs.rs, and the runnable examples live in the repository, so a clone of the workspace is the starting point. Two example programs are the first thing to start:
$ cargo run --example server ./
$ cargo run --example client https://localhost:4433/Cargo.toml
The first command launches an HTTP 0.9 server on the loopback address serving the current working directory. The second starts a client that fetches ./Cargo.toml over TLS from port 4433. By default the server generates a self-signed certificate and stores it to disk, and the client finds and trusts that file on its own, so no certificate plumbing is needed for a first connection.
Know what this pair proves. HTTP 0.9 has no header block and no status codes, so it shows that QUIC, TLS and your UDP path work together and nothing about application structure. The README lists Linux, macOS and Windows as tested platforms and quotes a minimum supported Rust version of 1.80.0, worth checking against the manifest before you pin a toolchain.
The MSRV is quoted twice and the two numbers disagree
One of the two minimum Rust versions you meet is the one that governs your build:
[workspace.package]
rust-version = "1.88.0"
edition = "2024"
license = "MIT OR Apache-2.0"
repository = "https://github.com/quinn-rs/quinn"
The feature list says the minimum supported Rust version is 1.80.0. The workspace package metadata sets 1.88.0 and pins edition 2024, which needs a toolchain new enough to understand it. Build on 1.80 and the workspace does not compile. The maintainers also state that the minimum supported Rust version for published releases of their crates will always be at least six months old at the time of release, so the floor moves on a schedule the README does not spell out.
Runtime coupling is the other upgrade cost visible in the dependency list. tokio is pinned at 1.28.1 with only the sync feature enabled, socket2 sits in the range >=0.5, <0.7, ring 0.17 is declared as a plain version and aws-lc-rs 1.9 with default features off, next to the rustls 0.23.5 entry the pluggable cryptography claim rests on. Two cryptography backends and a floating socket2 range mean your lockfile, not the README, is the record of what you compiled.
Two quinn-udp version lines shipped on the same day
Three releases landed on 2026-09-30: quinn-udp 0.6.3, quinn-udp 0.5.16 and quinn-proto 0.11.19. Two of them are separate lines of the same crate, published about two minutes apart.
That detail matters more than the numbers themselves. The workspace overview presents quinn as the layer above quinn-proto and quinn-udp, so the version of the socket and the state machine your application ends up running is decided by what the published quinn crate resolves to, not by the line you would have preferred. Pin quinn-udp yourself and you own compatibility across all three crates, and the README does not document which pairings get tested. The 2018 founding by Dirkjan Ochtman and Benjamin Saunders, with more than 30 releases since, says a versioned workspace has moved through several toolchain floors under one crate name.
The repository is not archived and the last push was on 2026-11-02, about a month after those releases. Commercial users are asked to sponsor the project through opencollective, which tells you how the maintenance time is funded.
quinn-proto tests run on simulated IO, and SSLKEYLOGFILE is the only window
The quinn-proto test suite uses simulated IO. The stated reasons are reproducibility and avoiding long sleeps in timing-sensitive tests, which makes the suite fast and deterministic, and also means it never touches a real socket.
Set the SSLKEYLOGFILE environment variable and the tests emit UDP packets for inspection with external protocol analyzers like Wireshark, writing NSS-compatible key logs for the client side of each connection to the path given in that variable. Without the variable there is no packet capture at all. A timing problem that only appears against a real UDP path will not be reproduced by the suite, and a failing timing test hands you nothing to inspect unless you set the variable first.
The top-level entries back this up: fuzz/ for fuzz targets, deny.toml for dependency policy, .codecov.yml for coverage, docs/book for the guide. Only bench and perf sit in default-members alongside the three crates, so the fuzzer stays out of a workspace build unless you request it by name.
Editorial conclusion
Quinn fits a Rust team that wants QUIC behind a tokio-shaped async API and is willing to own the socket and certificate details: one endpoint is one UDP socket, so the sizes you set for SO_SNDBUF and SO_RCVBUF decide throughput before any quinn code runs, and certificate validation is on unless a rustls override says otherwise. Pass on it if you need a stack that does its own I/O on a runtime you do not control, or if your toolchain is pinned to Rust 1.80 by policy, because the workspace manifest sets rust-version 1.88.0 with edition 2024 while the README still advertises 1.80.0. Check three things against your own build first: which quinn-udp line the published quinn crate resolves to, whether the kernel lets your process raise UDP buffer sizes, and whether the guide under docs/book matches the API version you pinned.
Frequently asked questions
Which Rust version does Quinn actually require?
The README quotes a minimum supported Rust version of 1.80.0, while the workspace Cargo.toml sets rust-version to 1.88.0 together with edition 2024. Build against the manifest value, since a 1.80 toolchain will not compile the workspace.
How do I start the Quinn example server and client?
Run cargo run --example server ./ in one terminal, then cargo run --example client https://localhost:4433/Cargo.toml in another. The server serves the current working directory over HTTP 0.9 and stores a generated self-signed certificate on disk that the client trusts automatically.
Can Quinn be used without tokio?
The high-level quinn crate is an async API based on tokio. quinn-proto performs no I/O internally and is presented as suitable for custom event loops, and the workspace dependency list also carries smol and async-io.
What happens when the UDP receive buffer is too small for a Quinn endpoint?
One endpoint is one UDP socket, so high aggregate data rates can overrun the default buffer and show up as erratic latency or throughput. Adjust SO_SNDBUF and SO_RCVBUF on the socket before passing it in, which on Linux may need elevated privileges or modified system configuration.
How do I make Quinn accept a self-signed certificate?
Put your own validation logic into a customized rustls configuration, and see the insecure_connection.rs example in the quinn crate. rcgen generates self-signed certificates on demand, and a trust-on-first-use server should store its generated certificate and reuse it on future runs.
What license is Quinn released under?
The workspace Cargo.toml declares MIT OR Apache-2.0 as the license expression, and the repository root carries both LICENSE-MIT and LICENSE-APACHE.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/quinn-rs-quinn)Star history chart for your README
[](https://hysenlabs.com/projects/quinn-rs-quinn)Was this useful?