sslscan no longer needs a particular OpenSSL to make its checks, and then needs OpenSSL 3.5 to build
sslscan tests SSL/TLS enabled services to discover supported cipher suites
At a glance
- What is it?
- rbsec/sslscan is a TLS scanner in C, forked from the original sslscan, whose version 2 rewrote the backend so most checks no longer depend on the linked crypto library, which is what lets it scan the two legacy SSL protocols and speak TLS 1.3 on any build. The build then requires OpenSSL 3.5 or newer, so the recommended path is a static build against your own copy, and the container image starts from an empty base as a non-root user with the dynamic loader copied in by hand.
- Who is it for?
- Use sslscan when you have authorisation to test a service you own or are engaged to assess, and read its colour output as a starting point rather than a verdict: it flags patterns like weak key sizes, deprecated protocol versions and expired certificates, and those flags encode the tool's own opinion of what matters. Three things to check before you rely on it.
- Can I use it commercially?
- Yes, with conditions. GPL-3.0 is a copyleft licence: if you distribute software that includes it, you must release that software's source code under the same licence. Running it internally without distributing it does not trigger that obligation.
- Is it still maintained?
- Yes. The repository last received commits 1 day ago.
- What is it written in?
- Mainly C, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
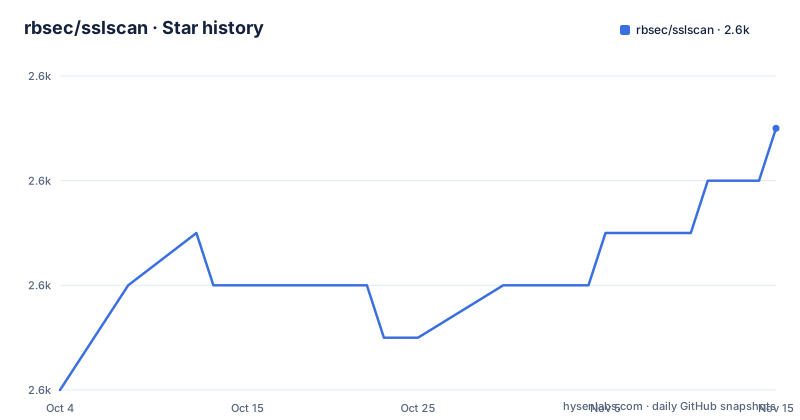
- rbsec/sslscan2,635 ★ · +5
| Repository | 2026-10-04 | 2026-11-15 |
|---|---|---|
| rbsec/sslscan | 2.6k | 2.6k |
5 Stars in the last 42 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The rewrite took the checks off the linked crypto library
Version 2 is described as a major rewrite of the backend scanning code, and the reason given is the most useful sentence on the page: the tool is no longer reliant on the version of OpenSSL for many checks. Before the rewrite, what the scanner could test was bounded by what the crypto library it was compiled against could do. After it, that coupling is gone for most of the checks, which is what makes two things possible at once that used to be mutually exclusive. The scanner can test the two legacy SSL protocol versions, which a modern library no longer supports at all, and it can speak the current version of TLS, which older libraries do not implement. The page credits one contributor with most of that rewrite, which is worth knowing before you file an issue about a specific check.
The two legacy protocols are scanned, but their ciphers are not
There is a deliberate limit inside version 2 that is easy to miss. SSLv2 and SSLv3 are scanned, which means the scanner will tell you whether a service still answers on them at all, and that is the finding most people care about. Individual ciphers are not enumerated for those two versions. So a service that accepts a legacy protocol will be reported as accepting it, without the tool telling you which cipher suites it would let you negotiate there. For an assessor that is a meaningful gap rather than a detail: knowing a protocol is reachable is the headline, and the ciphers behind it are older news, but the tool is not claiming to enumerate them. Everything else in the protocol range, from the middle versions through to the current one, is enumerated in full.
Building requires a crypto library version most distributions do not ship
The build advice is to ignore the system installation of the crypto library and link your own statically, accepting a heavier binary in exchange for being able to run checks that need the newer library. The catch is stated plainly: since version 2.2.0 the minimum required version is 3.5, on the long term support channel, and if your distribution ships anything older the build against it will not work. That is a real constraint in 2026, because the three most common distributions all ship older releases, so the documented path for most people is the static build. The recipe is short:
apt install git zlib1g-dev make gccthen run the static target, which clones the crypto library's own repository and compiles and tests it before compiling the scanner, or pass a compiler name to it for the same build with a different toolchain. You can tell whether you got the static build by looking for a suffix on the version the tool prints.
The XML output moved its certificates and may return more than one
There is a clearly marked breaking change in the XML output, made during the 2.0.0 betas, and the page warns that anyone parsing it may need changes. A new parent element now contains the certificate elements, and each certificate carries a type attribute distinguishing the short form from the full one the display flag produces. The part that will bite hardest is the next sentence: a server that holds several certificates signed with different algorithms can now return more than one of each type, and the page links the issue where that was discussed. So a consumer that assumed one certificate element now has to cope with several, and the label and whitespace inside the signature algorithm element were removed as well. Structured output is where this project's users are most likely to notice the change.
The container is an empty base with the loader copied in by hand
The image is built in two stages and the second one contains nothing but three copied files. The builder runs on the latest Alpine tag, clears the package cache, installs a compiler and the development headers, copies the source into a build directory, runs the static build and strips the symbols. It then prints the dynamic linker output and a file listing, which is a diagnostic decision rather than a mistake: the log tells a maintainer exactly which shared libraries survived into the final image. The final stage starts from an empty base, copies the executable, copies one compression library and copies the platform's dynamic loader by pattern match, sets the user to an unprivileged numeric identifier, and uses the executable as the entry point. Nothing else is in there, including no certificate store beyond what the builder installed.
The build file hardens the binary and drops the flags macOS cannot take
The makefile is where the security posture is actually decided, and it is deliberate about it. Warning flags include the format string checks and the format security switch, with deprecation warnings suppressed. The compile flags add buffer overflow protection, stack protectors and position independent executables, and the link flags add position independent executables with read-only relocations and an immediate global offset table. Those link-time flags are then explicitly withheld on four platforms, with a comment explaining that macOS ships an older compiler, and the SunOS and MinGW paths get their own compiler defaults and socket libraries. C11 mode is forced with a comment about fixing the build on very old compiler versions. The version string comes from the tag description, with a fallback that greps the changelog when git is not installed.
Windows is available and called experimental in two places
Windows support arrived as a contributed patch and can be done two ways: built natively, or cross-compiled from Linux, with the instructions in a separate install document. Pre-built cross-compiled Windows binaries are published on the releases page, which is the fastest route and also the one that tells you the project considers a binary build the normal Windows experience. The caveats are stated twice in the readme in different words: the tool was originally written for Linux, has not been extensively tested on Windows, and the Windows version should be considered experimental. macOS gets the same treatment with a different word: static builds are described as experimental and then as unsupported in the same paragraph. Both platforms have dedicated makefiles, one for MinGW and one for the Visual Studio toolchain.
Pacing is a sleep option, not an authorisation boundary
The tool has two controls that affect how it talks to a target: an option to pause between requests, and an option to set a socket timeout. Those are politeness and reliability settings. What the page does not describe is any kind of scope control, and this is worth stating plainly for a scanner. There is no per-target authorisation check, no dry run mode that reports what it would do without doing it, no record of the engagement, and no built-in limit on how many targets one invocation covers. Everything about who you point it at is decided outside the tool, which is normal for a scanner and is exactly why the authorisation has to live somewhere else. The check list itself is the other half of the picture: it flags legacy protocol support, cipher suites in the vulnerable negotiation mode, deprecated ciphers, compression, a specific historic memory disclosure, weak certificate signatures and keys, and expired certificates.
Editorial conclusion
Use sslscan when you have authorisation to test a service you own or are engaged to assess, and read its colour output as a starting point rather than a verdict: it flags patterns like weak key sizes, deprecated protocol versions and expired certificates, and those flags encode the tool's own opinion of what matters. Three things to check before you rely on it. Decide whether you want the static build, because the documented advice is to ignore the system crypto library, which costs a larger binary and a full compile of that library. If you consume its XML, expect to rewrite the certificate parsing, because the element structure changed during the 2.0 betas. And if you are scanning anything other than your own infrastructure, get the authorisation in writing first, since the tool has no notion of scope.
Frequently asked questions
how to install sslscan on linux
The page recommends ignoring the system crypto library and building statically against your own copy: install git, the zlib headers, make and a compiler, then run the static build target, which clones and compiles that library first. A Docker path is documented too. Since version 2.2.0 the minimum crypto library version is 3.5.
what is sslscan?
A command line tool that tests TLS enabled services and reports which cipher suites, protocol versions, key exchange groups and server signature algorithms they support, flagging deprecated protocols, vulnerable cipher suites, compression, weak certificate keys and expired certificates.
What changed in sslscan version 2?
The backend scanning code was rewritten so most checks no longer depend on the version of the crypto library it was compiled against, which is what allows the two legacy SSL protocols to be scanned and TLS 1.3 to be supported on any build. Version 2 also enumerates key exchange groups and server signature algorithms, drops the broken HTTP option and adds post-quantum group support.
Why did sslscan's XML output break?
During the 2.0.0 betas the certificate elements were moved under a new parent element and gained a type attribute, so a server with several certificates signed differently can return more than one of each type. The label inside the signature algorithm element was also removed, and the page warns consumers may need to change their parser.
Does sslscan work on Windows and macOS?
Windows support came as a patch and can be built natively or cross-compiled from Linux, with pre-built binaries on the releases page, but the page says it has not been extensively tested there and should be considered experimental. macOS static builds are described as experimental and unsupported.
How does sslscan avoid overloading a target?
It has an option to sleep between requests and an option to set a socket timeout. The page describes no authorisation check, no dry run and no target allow list, so those two settings are politeness controls rather than a scope boundary.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/rbsec-sslscan)Star history chart for your README
[](https://hysenlabs.com/projects/rbsec-sslscan)Was this useful?