CodexPro sets the plugin authentication to None and makes the URL the credential
Use ChatGPT Developer Mode as a local coding agent for your repo through MCP.
At a glance
- What is it?
- rebel0789/codexpro is a MIT licensed local MCP server that gives your own ChatGPT account read, edit, and shell tools inside repositories you explicitly allow, reached over an HTTPS tunnel. Its safety design is unusually concrete and its authentication shape is unusual too: the plugin form is told to use no authentication, and the secret is the URL.
- Who is it for?
- CodexPro fits a developer who wants to work on their own repository through a ChatGPT subscription they already pay for, without sending the repository to an indexing service, and who is comfortable running a local HTTP server and exposing it deliberately. Check four things.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 45 days ago.
- What is it written in?
- Mainly JavaScript, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
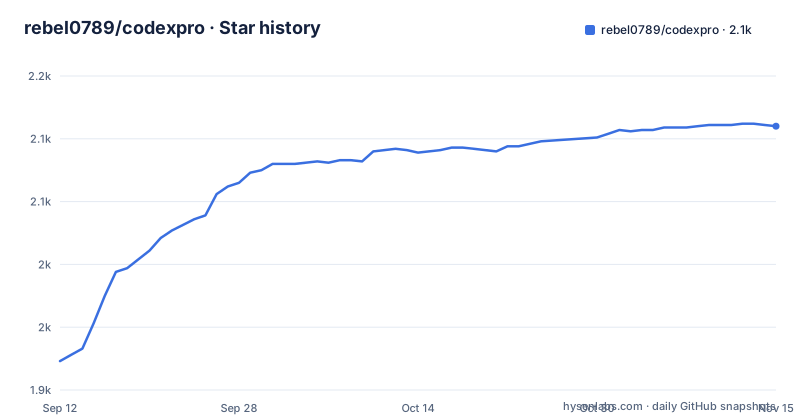
- rebel0789/codexpro2,110 ★ · +187
| Repository | 2026-09-12 | 2026-11-15 |
|---|---|---|
| rebel0789/codexpro | 1.9k | 2.1k |
187 Stars in the last 64 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The plugin is registered with no authentication and the token lives in the URL
The connection walkthrough is five steps and the fourth and fifth are the ones that matter. You paste the server URL that the setup step copied for you, and then you set authentication to No Authentication, None, with a note to change it if the form happens to default to OAuth. The following sentence resolves the confusion that creates: the CodexPro authentication is the token already present in that URL, and the instruction is not to share the URL. So the credential is not a separate field with a separate value, it is a component of the address you paste, and the form you are told to fill in says there is no authentication. That is a workable shape for a loopback or tailnet service where the URL is unguessable, and it is a poor shape for anything reachable from the internet, which is why the tunnel section adds a token requirement and a security document to read first.
A public tunnel needs a token, and the compatibility fallback puts it in the query string
Public exposure has its own gate: public tunnels require a CodexPro HTTP token of at least twenty four bytes. The token is generated with three commands:
mkdir -p ~/.codexpro
openssl rand -hex 32 > ~/.codexpro/http-token
chmod 600 ~/.codexpro/http-token
Thirty two random bytes against a twenty four byte floor, written with restrictive permissions. How the token reaches the server is a separate decision, and the document gives a preference: use `Authorization: Bearer <token>` when the client supports headers, and treat the `?codexpro_token=` query form as a personal compatibility fallback. That ordering is the right one, because a query parameter ends up in server access logs, proxy logs, and browser history, while a header does not. Keeping a stable token is what makes a stable hostname usable, and the tunnel commands show the four options with their character: a cloudflare tunnel that produces a quick demo URL which changes, an ngrok hostname, a stable command that pairs a hostname with a tunnel name, a tailscale hostname on your own tailnet, and a no-tunnel option that stays local.
Writes are hidden rather than gated, and attachment import is limited to approved hosts
The safety defaults are five lines and each one is a specific mechanism rather than a promise. Writes stay hidden unless the write mode is set to workspace, which is a stronger default than prompting: the edit tools exist but are not exposed until you opt in, which is why the tool list is prefaced with the phrase workspace write mode. Safe bash is the default, and the bash tool is described as running allowlisted checks rather than arbitrary commands. Blocked paths cover dotenv files, keys, the git directory, and build caches, so an ordinary read or search cannot walk into your credentials or your object history. Attachment import is restricted to ChatGPT Apps SDK file objects coming from approved HTTPS hosts, which is the control that stops a file reference in a chat from pointing at an address on your own network. And the document closes with a single instruction: read the security file before exposing a tunnel.
The repository intelligence is local, lexical, and honest about its coverage
The claim here is that the server does more than raw file search, and the mechanism is what makes it credible without a model key. Three tools carry the weight. `inspect_workspace` maps languages, project types, entrypoints, areas, symbols, and internal relationships. `search` supports symbol, references, and impact intents alongside ordinary text and regular expression search. `show_changes` identifies affected areas, likely dependents, related tests, risk signals, and relevant verification commands. Declarations are recognised in nine languages: TypeScript and JavaScript, Python, Go, Rust, Swift, Java, C#, C, and C++, and anything else keeps a safe inventory and lexical search. What runs underneath is described as local, bounded, and cached by a workspace fingerprint, needing no model API key, no language server daemon, no embedding service, and no vector database. The sentence that earns trust is the last one: coverage and inference strength are reported rather than presented as certainty.
Two releases forty three minutes apart and the manifest is already ahead of both
The version picture has three numbers in it. The manifest reads 0.30.3. The published releases are v0.30.2 at 15:05:32Z and v0.30.1 at 14:22:25Z, both on 2026-09-20, forty three minutes apart. So the tree has moved one version past the newest tag, and the two most recent tags landed inside the same afternoon. The update path is correspondingly blunt: install the latest from the registry, check the version, and restart the running server, with saved profiles under the dot directory left in place across the upgrade. That last point matters because the profiles are where the token lives and where the tunnel configuration is kept, so an upgrade is not a chance to lose them and also not a chance to rotate them by accident.
The published package ships the documentation website and fourteen markdown files
The files list in the manifest is longer than a server needs to be. Alongside the built output and the scripts directory it ships the documentation site, entry by entry: the English and Chinese pages, a stylesheet, a script, a favicon, an open graph image, a star image, and an images directory. Then fourteen documentation files by name, among them the security file, the domain setup guide, the public launch checklist, both language versions of the readme and the FAQ, two prompt templates written for ChatGPT and for Codex, an example agent configuration file, and an example environment file. Three binaries are registered at once: the main command, plus one for the stdio transport and one for the HTTP transport, so the same server is reachable under three names depending on how you want to launch it.
The repository root keeps a recovery report and a public launch checklist
A few root files describe work rather than instructions, and they are worth knowing about before you read the readme as the whole picture. There is a recovery report, which reads as a postmortem kept in the tree. There is a public launch checklist. There is a design document. There is a domain setup guide specifically for stable hostnames, separate from the tunnel section in the readme. And there is a changelog, a contributors file, and a security file. The readme's own scope statement is short and worth quoting: this is not a hosted SaaS product, a model proxy, a quota bypass, an account pool, or a remote shell service. The last of those five is the claim that matters most for judging the surface, since the tool does grant command execution, and it is bounded by the allowlist and by the workspace mode rather than by the network.
Editorial conclusion
CodexPro fits a developer who wants to work on their own repository through a ChatGPT subscription they already pay for, without sending the repository to an indexing service, and who is comfortable running a local HTTP server and exposing it deliberately. Check four things. How you transport the credential, because a bearer header is supported and a URL query parameter is the documented fallback, and those leak into logs and history in ways headers do not. Whether writes are on, because they stay hidden until the write mode is set to workspace, which is a quieter default than a prompt. What your tunnel actually terminates on, since a demo tunnel URL changes and a stable hostname does not, and the project keeps profiles under a dot directory that survive upgrades. And whether your dependency scanning is happy, because the local analysis is lexical and structural rather than a language server, so coverage and inference strength are reported instead of guaranteed.
Frequently asked questions
What does codexpro actually do?
It is a local MCP server that connects your ChatGPT session to your machine and to repositories you allow. ChatGPT can read, search, edit, review, verify, import attachments, and write handoff plans, and it stays inside the roots you allowed.
How do I authenticate the ChatGPT plugin for codexpro?
Set the plugin's authentication to No Authentication, None, and paste the server URL that setup copied. The authentication is the token already present in that URL, so the document's instruction is not to share the URL.
What are codexpro's safety defaults?
Writes stay hidden unless the write mode is set to workspace, safe bash is the default and runs allowlisted checks, blocked paths cover dotenv files, keys, the git directory and build caches, attachment import accepts only Apps SDK file objects from approved HTTPS hosts, and public tunnels require an HTTP token of at least 24 bytes.
Does codexpro need a model API key or an indexing service?
No. Analysis runs locally, bounded and cached by a workspace fingerprint, with no model API key, no language server daemon, no embedding service and no vector database. Declarations are recognised in nine languages, with lexical search elsewhere, and coverage is reported rather than guaranteed.
How do I keep a stable public URL for codexpro?
Keep a stable token, generated with `openssl rand -hex 32` into a file with mode 600, and use the stable command with a hostname and tunnel name. The cloudflare tunnel option is described as a quick demo URL that changes, and passing `--tunnel none` stays local only.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/rebel0789-codexpro)Star history chart for your README
[](https://hysenlabs.com/projects/rebel0789-codexpro)Was this useful?