drozer: the Agent listens on all interfaces on port 31415, and the cmd example for ANDROID_SDK has spaces around the equals sign
The Leading Security Assessment Framework for Android.
At a glance
- What is it?
- drozer is ReversecLabs's Android security testing framework, a Python project under a 3-clause BSD licence whose newest tagged release is 3.1.0 from August 2024. Its README describes a beta rewrite, names one feature as broken and out of scope, and gives two ways to reach the device agent, whose embedded server listens on every interface by default.
- Who is it for?
- drozer fits an authorised assessment of an Android application you own or are contracted to test, and it fits an assessment that needs the agent identity model rather than instrumentation of the process, because the framework works by assuming the role of an app and talking to IPC endpoints and the OS from there. Three things to settle before you rely on it.
- Can I use it commercially?
- Check first. The repository uses a licence we do not classify automatically, so read its LICENSE file before any commercial use.
- Is it still maintained?
- Activity is slowing. The repository last received commits 7 months ago.
- What is it written in?
- Mainly Python, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
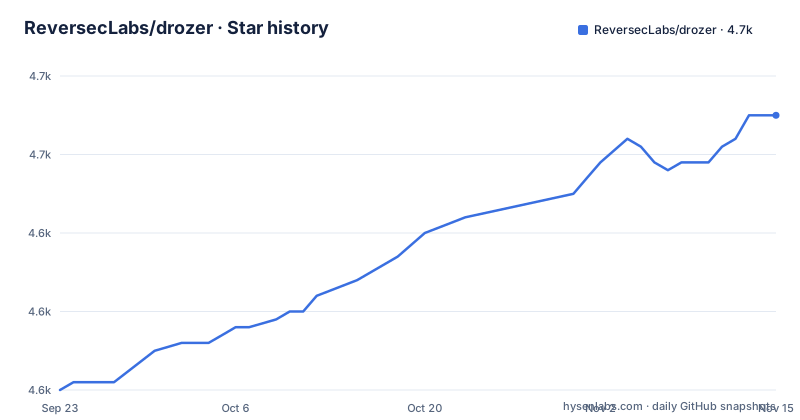
- ReversecLabs/drozer4,655 ★ · +35
| Repository | 2026-09-23 | 2026-11-15 |
|---|---|---|
| ReversecLabs/drozer | 4.6k | 4.7k |
35 Stars in the last 53 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The mechanism is identity assumption, which is why the scope line matters
The README states the design in one sentence, and it is the sentence to read before anything else. drozer allows you to search for security vulnerabilities in apps and devices by assuming the role of an app and interacting with the Android Runtime, other apps' IPC endpoints and the underlying OS. Instead the framework installs an Agent on the device and speaks to it from a console on your machine, and the Agent is the thing that holds the identity. That makes the permission boundary the interesting part of the tool rather than an afterthought: an assessment with this framework is only meaningful against a target you are authorised to test, and the same Agent binary pointed at someone else's device is a different activity entirely. The second capability line, tools to help you use, share and understand public Android exploits, is about reading existing work rather than finding new issues.
One feature is declared broken and out of scope for the beta
The README carries a NOTE section that a reviewer should not skip. It states that this is a beta release of a rewritten drozer version, updated to support python3. Then it lists the known issues present, and there is exactly one: building of custom agents functionality will crash the drozer client, and that functionality is considered out of scope for the beta release of the revived drozer project. So a feature that existed in earlier versions is broken in this one, the failure mode is a client crash rather than an error message, and the project has decided not to fix it in this line. That is honest disclosure, and it is also a planning input: if your assessment method depends on generating a custom agent, this version will not carry it. The release record backs up that this is an in-progress line, with 3.0.2 in April 2024, 3.0.3 in June 2024 and 3.1.0 in August 2024, while the last push to the repository is dated 2026-04-08 with no release after 3.1.0.
pipx is the preferred install and a Docker image covers the rest
Installation is pip based and pipx is named as the preference where available:
pipx install drozerAlternatively you can download an individual release wheel from GitHub and install it the same way, with `pipx install ./drozer-*.whl`. Then one step that catches people out: run `pipx ensurepath` so pipx installed packages appear in your PATH. The alternatives to all of that are a Docker container and a manual build. The container exists to help make sure drozer can be run on all systems, is published as drozerdocker/drozer, and the repository has a docker/ directory with instructions for building your own. The software pre-requisites are six items with floor versions: Python 3.8, Protobuf 4.25.2 or greater, Pyopenssl 22.0.0 or greater, Twisted 18.9.0 or greater, Distro 1.8.0 or greater, and a Java Development Kit at 11 or greater. Note that the numbered list in the README counts two items as 4 and then continues at 5.
The Agent binds every interface by default, and adb forward is the scoped alternative
This is the operational detail worth planning around. The Agent has an embedded server which you enable by launching the Agent, selecting the Embedded Server option and tapping Enable, after which a notification confirms it started. By default it listens for incoming TCP connections on all interfaces on port 31415. There are two connection paths. Over the network you run `drozer console connect --server <phone's IP address>`, with the Docker equivalent using the host network mode. Over USB you set up adb port forwarding with `adb forward tcp:31415 tcp:31415` and then run `drozer console connect` with no target, which reaches the device through localhost. The README frames USB as the answer for scenarios where connecting over the network may not be viable.
The console can open a Linux shell in the Agent's own process context
Read the command reference before planning an assessment, because two of the fourteen commands have consequences beyond enumeration. The `shell` command starts an interactive Linux shell on the device in the context of the Agent process, which means the shell runs with whatever identity and permissions the Agent holds. The `cd` command mounts a particular namespace as the root of the session so you do not have to type the full module name repeatedly. Two more relate to state on the device: `clean` removes temporary files stored by drozer on the Android device, and `set` and `unset` store and remove variables that drozer passes as environment variables to any Linux shells it spawns, which is how you would set up environment for those shells. The rest are navigational: `list` shows modules available in the current session and hides those you lack permission to run, `module` finds and installs additional modules from the Internet, `load` executes a file of commands in sequence, `permissions` shows what the Agent was granted, and `run`, `contributors`, `echo`, `exit` and `help` round it out.
The build compiles Java modules with javac and d8, with bundled fallbacks
The build script is worth reading because it explains what an install actually does. Building from source is three commands: clone the repository, change into the drozer directory, and run pip install. The setup script then walks the modules directory and does three things. It first deletes any existing .class, .apk and .zip files under src/drozer/modules, so a stale artifact never survives a rebuild. It then compiles each .java file with javac using the --release 11 flag and the android.jar as the classpath. Finally it invokes d8 with an output zip and the same jar as the library, producing the packaged module. The two paths it needs can be overridden: ANDROID_SDK points at a specific android.jar, and D8 points at the d8 tool. Both have bundled fallbacks inside src/drozer/lib, with a .bat suffix added on Windows for d8. If javac is not on the path the script raises rather than failing quietly.
The cmd example sets ANDROID_SDK with spaces around the equals sign
The three platform examples for pointing at an SDK differ in one consequential way. On Linux and macOS it is an export statement assigning ANDROID_SDK to the path of an android.jar inside the platforms directory. In PowerShell it uses New-Item against Env:\ANDROID_SDK with a Value parameter. In cmd it is written with spaces on both sides of the equals sign, as `set ANDROID_SDK = "C:\Users\...\android.jar"`. In cmd that syntax does not do what the other two do: set treats everything before the equals sign as the variable name, so this defines a variable whose name is ANDROID_SDK with a trailing space, and the script's environment lookup for ANDROID_SDK will not find it. The build does not fail in that case, because both variables have bundled fallbacks, so the symptom is that your specified SDK is silently ignored and the bundled android.jar is used instead. Worth knowing before you conclude your build picked up the wrong API level for a reason you cannot find.
One package name, three installed packages, three console scripts
The packaging metadata explains the src layout and the entry points. The build system is setuptools at 61.0 or higher with the setuptools.build_meta backend, the project is named drozer, its version is dynamic and read from the drozer.__version__ attribute, and it requires Python 3.8 or higher. The licence is a file reference to LICENSE rather than an SPDX expression, and the classifiers list a BSD licence under OSI approved. Three console scripts are installed from three different modules: drozer itself, drozer-repository, and drozer-complete, which is the autocomplete entry point. Then the part that explains the tree: three separate package directories are mapped into the installation, drozer at src/drozer, reversec at src/reversec, and pysolar at src/pysolar, so the distribution ships three top level packages under one project name rather than one. The runtime dependencies match the pre-requisite list and add service-identity, pyyaml, requests and prompt_toolkit at 3.0.0 or higher.
Editorial conclusion
drozer fits an authorised assessment of an Android application you own or are contracted to test, and it fits an assessment that needs the agent identity model rather than instrumentation of the process, because the framework works by assuming the role of an app and talking to IPC endpoints and the OS from there. Three things to settle before you rely on it. It declares itself a beta of a rewritten version and names one broken feature, custom agent building, which crashes the client and is declared out of scope, so check whether your workflow needs it. The Agent's embedded server listens for TCP connections on all interfaces on port 31415 by default, whichever way you then connect to it. And installation pulls three console scripts and three packages from a src directory, with the Java modules compiled at build time, so the build has more moving parts than a pure Python install. The last push is dated 2026-04-08.
Frequently asked questions
What is drozer?
It is a security testing framework for Android, maintained by ReversecLabs and released under a 3-clause BSD licence. It works by assuming the role of an app and interacting with the Android Runtime, other apps' IPC endpoints and the underlying OS, and it also provides tools to use, share and understand public Android exploits.
How do I install drozer?
With pipx where available: `pipx install drozer`, then `pipx ensurepath` so the command lands on your PATH. You can also install a release wheel from GitHub with `pipx install ./drozer-*.whl`, or build from source with a clone and `pip install .`. A Docker image is published as drozerdocker/drozer, and the pre-requisites are Python 3.8, Protobuf 4.25.2, Pyopenssl 22.0.0, Twisted 18.9.0, Distro 1.8.0 and a JDK at 11 or above.
What is the drozer Agent and how does the console reach the device?
The Agent is an Android application you install with `adb install drozer-agent.apk`. You enable its embedded server in the app, and by default it listens for TCP connections on all interfaces on port 31415. Connect over the network with `drozer console connect --server <phone's IP address>`, or use `adb forward tcp:31415 tcp:31415` and then `drozer console connect` over USB.
Which drozer features are known to be broken?
The README states this is a beta release of a rewritten drozer version updated for python3, and names one known issue: building of custom agents functionality will crash the drozer client. That functionality is considered out of scope for the beta release of the revived project. The newest tagged release is 3.1.0 from 2024-08-01.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/reverseclabs-drozer)Star history chart for your README
[](https://hysenlabs.com/projects/reverseclabs-drozer)Was this useful?