action-golangci-lint: review comments for Go lint findings that will not fail your build
Run golangci-lint with reviewdog
At a glance
- What is it?
- reviewdog/action-golangci-lint runs golangci-lint and turns its output into pull request annotations. By default it reports and never fails, because the failure level input defaults to none, so a team can adopt it as a comment layer first and gate later. Its own go.mod is marked deprecated and exists only to make test fixtures module aware.
- Who is it for?
- This is worth adopting as a first step for a Go repository that has never had lint review comments, because the action is deliberately non blocking by default, so you can see the noise volume in real pull requests for a week before deciding which linters to gate on, and the filtering default of added lines keeps the first run from annotating the whole file.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 1 day ago.
- What is it written in?
- Mainly TypeScript, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
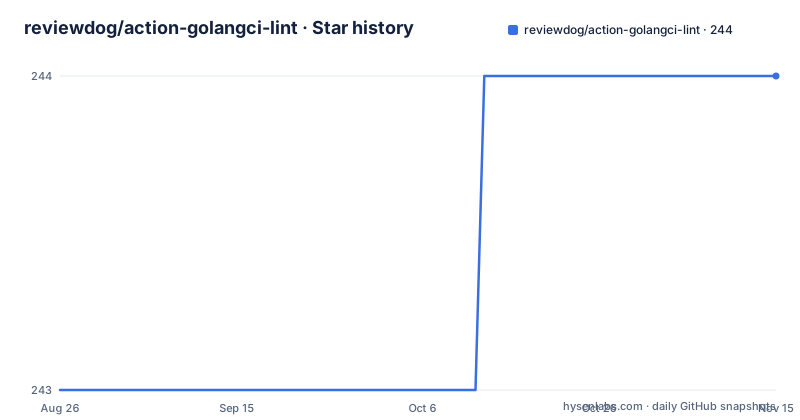
- reviewdog/action-golangci-lint244 ★ · +1
| Repository | 2026-08-26 | 2026-11-15 |
|---|---|---|
| reviewdog/action-golangci-lint | 243 | 244 |
1 Stars in the last 81 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The action comments on your pull request and returns a green build
The default behaviour is the thing to understand first, because it surprises people. The reporter is what the action calls tool when talking to reviewdog, and there are two options: a pull request check or a pull request review. The one that fails the build is a separate input, and its name is the failure level. Set to none, which is the default, the action always uses exit code zero for reviewdog no matter how many issues were found. Set to anything else, reviewdog exits with code one if it finds at least one issue at or above the severity you named, and the permitted values are none, any, info, warning and error. The pairing is sensible. The old boolean input for failing on errors still exists but is marked deprecated in favour of the severity version, and it defaulted to false, so the migration does not change behaviour for anyone who was already using it.
The v2 migration deleted your setup and cache steps
The migration section is unusually practical. In most cases the change is a single character, using the v2 reference instead of v1 in the workflow. The second half is where people actually saved time. The v1 pattern required a step to set up Go and a step to cache, and both are now unnecessary because v2 does both itself. The readme shows exactly what to delete by including those steps commented out in the example, with the cached paths spelled out: a directory for the linter's own cache, the Go build cache, and the module cache. Removing them is the recommendation, not an optimisation, so a workflow carrying a manual setup step after upgrading is doing redundant work. What is left is two steps, and one of them has a setting that matters more than it looks:
name: reviewdog
on: [pull_request]
jobs:
  golangci-lint:
    name: runner / golangci-lint
    runs-on: ubuntu-latest
    steps:
      - name: Check out code into the Go module directory
        uses: actions/checkout@11bd71901bbe5b1630ceea73d27597364c9af683 # v4.2.2
        with:
          fetch-depth: 0

      - name: golangci-lint
        uses: reviewdog/action-golangci-lint@3dfdce20f5ca12d264c214abb993dbb40834da90 # v2.7.2
That fetch depth of zero asks the checkout for the full history rather than a shallow clone, which is what lets the linter compare against a base revision instead of only looking at the working tree. Both steps are pinned to full commit hashes with the human readable version kept in a trailing comment, which is the pattern to copy rather than a tag reference.
Two Go version inputs, and the explicit one wins
Getting the right Go version is a first class concern, because a linter built against a different toolchain than your code produces results you cannot act on. There are two inputs for it and the precedence is documented. The version file input takes a path to a go.mod file or a file containing nothing but a Go version, which lets you read the requirement straight out of the module definition instead of duplicating it in the workflow. The version input takes a version directly. When both are supplied, the direct one is used, so an override always wins over what the file says. With neither supplied, the latest Go 1 release is installed. The same pattern applies to the two tools the action installs: reviewdog and golangci-lint each have a version input, and each defaults to installing the latest release. Pinning all four is the configuration that gives you reproducible comments, and leaving all four unpinned is the configuration that gives you a surprise the next time a linter changes its output.
Default filtering is added lines, so old problems stay invisible
The filtering mode decides which findings become annotations, and the default is the narrowest sensible one: added lines only. The available modes are added, diff context, file and no filtering, and they correspond to progressively larger surfaces. Added lines is what makes the action safe to adopt on an existing codebase, because a repository with a decade of lint debt would otherwise light up every file on the first run and the review would be unreadable. Diff context widens that to the surrounding lines of a change, which catches issues where a new line interacts with an old one, at the cost of surfacing debt near every hunk. File mode annotates whole files that were touched, and no filtering passes everything through. The tool name input exists for the case where several lint actions run on the same pull request with different configurations, since reviewdog needs a distinct tool name per configuration to group its comments properly.
The repository ships a compiled bundle and a go.mod marked do not use
Two things in the tree are easy to misread. The first is the build output directory, which is committed, because this is a JavaScript action that runs on the runner rather than a container action, so the bundle the runner executes has to be in the repository. The build produces it by clearing the output directory and running a bundler with the TypeScript plugin, and the whole chain is exposed as a bundle script that formats before packaging, plus an all script that formats, lints, tests and packages in that order. The second is the Go module file at the top level, which opens with a comment saying it is deprecated and exists only for testing, with the reason spelled out: module aware mode became the default in a much earlier Go release, so the action's test fixtures need a module file present to work at all. Anyone who mistakes that file for a real Go package declaration, or tries to depend on this repository as a module, is reading a test scaffold as if it were an API.
You can run every linter without a config file, and one of them will win
There is a documented way to skip configuration entirely, by passing flags through the linter flags input, and the readme gives the pair that turns everything on, enabling all linters and clearing the exclusion list so the defaults do not filter anything out. That is a useful starting point for measuring what a repository would look like under a maximal rule set, and a bad thing to ship as a permanent setting, since the output volume makes the added lines filter do all the work. The advanced example carries a comment worth reading closely, because it records a limitation of the tool underneath rather than of the action: the linter does not report multiple errors on the same line coming from different linters, it reports one of them. So a line with both an unused variable and a shadowed declaration produces a single annotation, and which one survives is not something this action controls.
Editorial conclusion
This is worth adopting as a first step for a Go repository that has never had lint review comments, because the action is deliberately non blocking by default, so you can see the noise volume in real pull requests for a week before deciding which linters to gate on, and the filtering default of added lines keeps the first run from annotating the whole file. It is the wrong tool if you want a single pass or fail job, since the two reporters it can use are pull request checks and pull request reviews rather than a build gate you can rely on alone, and the wrong tool if your findings are spread across a wide diff, because the default filter will hide issues in surrounding context. Before you adopt it, check three things: which reporter you want, since the two produce visibly different artifacts in the pull request; which filtering mode fits your review culture, because the default only looks at added lines and a wider mode will resurface long standing problems; and which version of the linter you are pinning, because the action installs the latest by default and linter output formats change between releases, so a linter upgrade can silently change what lands in your review comments.
Frequently asked questions
Does reviewdog/action-golangci-lint fail the build when it finds issues?
Not by default. The failure level input defaults to none, which always uses exit code zero. Set it to any, info, warning or error and reviewdog exits with code one if it finds at least one issue at or above that severity.
What do I need to change to migrate from v1 to v2?
Use the v2 reference instead of v1 in your workflow. You can also delete any steps that set up Go and any cache steps, because v2 sets up Go and caches modules automatically, caching the linter cache, the Go build cache and the module cache.
How do I control which Go version the action installs?
Two inputs exist. The version file input takes a path to a go.mod or to a file containing only a Go version, and the version input takes a version directly. If both are given, the direct version input is used, and with neither the latest Go 1 release is installed.
What does filter_mode do in action-golangci-lint?
It decides which findings become review annotations, with four modes available. The default is added, which annotates only new lines, and the others are diff context, file and no filtering.
What are the two reporter options?
A pull request check or a pull request review, chosen with the reporter input, which maps to the same flag on reviewdog. The tool name input exists so several lint actions with different configurations can be told apart in the same pull request.
Why is there a go.mod file in a TypeScript action repository?
Because the test fixtures need one. The file opens by saying it is deprecated and exists only for testing, explaining that module aware mode has been the default since an earlier Go release, so the fixtures require a module file to be present.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/reviewdog-action-golangci-lint)Star history chart for your README
[](https://hysenlabs.com/projects/reviewdog-action-golangci-lint)Was this useful?