kubectl-mcp-server installs two command names and documents a third, and its two manifests count a different number of tools than the page does
Published in CNCF Landscape: A MCP server for Kubernetes.
At a glance
- What is it?
- A Kubernetes server exposing its cluster to an assistant over the model context protocol, shipped as an npm binary, two pip console scripts and two container images. The tool count, the Node floor and the release tag all disagree between the readme and the packaging files.
- Who is it for?
- Use it if you want an assistant to read and change cluster state and you are willing to run the server against a kubeconfig with real write access, because the tool surface includes deployment and resource changes rather than read only inspection. Three things to check first.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 24 days ago.
- What is it written in?
- Mainly Python, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
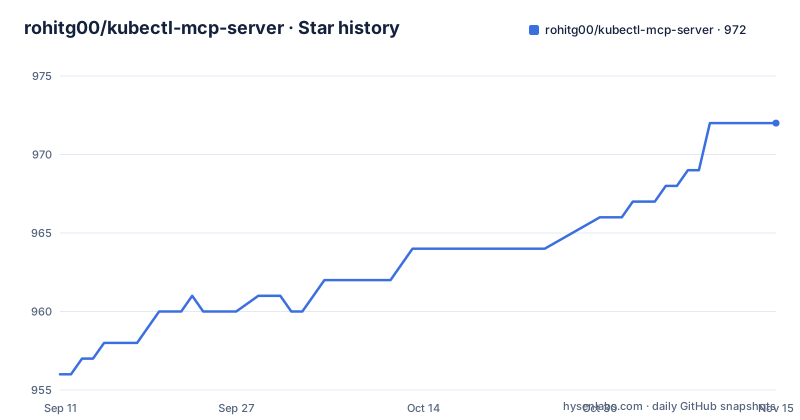
- rohitg00/kubectl-mcp-server972 ★ · +16
| Repository | 2026-09-11 | 2026-11-15 |
|---|---|---|
| rohitg00/kubectl-mcp-server | 956 | 972 |
16 Stars in the last 65 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Pip creates two command names and the guide uses a third
The installation section offers four routes, and they do not produce the same binary name. The npm route registers a single executable called kubectl-mcp-server. The pip route registers two different ones, a short name and a serve name, both pointing into the same Python package.
The verification section then uses the npm name. To test an install, the guide has you list all available tools and then call one by name with a JSON argument:
kubectl-mcp-server info
kubectl-mcp-server tools
kubectl-mcp-server call get_pods '{"namespace": "kube-system"}'
A reader who installed with pip, which is the route the page documents second, gets a package that installs cleanly and then fails on all three of those commands, because the executable it registered has a different name. Nothing warns about this. The npm route is called the recommended one, which explains the choice of command in the examples, but the pip route has no equivalent list of its own.
The manifests say 270 tools and the page says 253
Three places state a tool count and they do not agree. Both packaging files carry the same one: the npm manifest describes the project as a server with 270 or more tools, 8 resources and 8 prompts, and the Python setup file repeats that wording exactly.
The page says 253 powerful tools, with the same 8 workflow prompts and 8 data resources beside it. So the prompts and the resources match across all three, and only the tool count diverges. The page also breaks the surface down further in its own table of contents, with a count for the interactive dashboard tools, a count for the browser automation tools, a count for the enterprise authentication group, and a count for the agent skills.
Version numbers diverge in the same way. Both manifests declare 1.25.0. The newest visible tag is 1.24.0, dated in February and titled for a 3D cluster topology viewer. So the packaging files are ahead of the newest release, which is what happens when a project bumps the version before tagging, and it means installing from the branch gives you a different version string than the newest download.
The Node floor is 16 in the manifest and 14 in the guide
The npm manifest declares an engines field with a single entry: Node 16 or newer. It also restricts the package to three operating systems, macOS, Linux and Windows.
The prerequisite list gives a different number. It asks for Python 3.9 or newer for the pip route and Node.js 14 or newer for the npx route, then adds that a cluster command line tool must be installed and configured and that you need access to a cluster.
The two Python answers agree with each other, since the setup file classifies 3.9. The Node answer does not agree with the manifest, and the manifest is the one that will refuse to install. So on Node 14 the documented route fails at the install step with an engine error rather than at anything to do with the server itself.
The rest of the prerequisite list is the honest part of the setup: a working kubeconfig and cluster access, not just a package. The tool surface includes write operations, so the credential you point it at is the real configuration decision.
kubectl is pinned in the image and Helm is piped from a branch
The container image is careful about one of its two cluster command line tools and not the other. The Kubernetes client is fetched by version, with a build argument defaulting to a specific release, downloaded from the official distribution path for the target architecture, made executable, and then asked to print its own version as a build check. The comment above it says the version is pinned for reliability.
Helm is installed differently. The installer script is fetched from a repository's main branch and piped straight into a shell, with no version argument anywhere in the file. So the image that pins one tool to a fixed release for reliability installs the other from whatever the branch currently holds.
The Python side of the image is more disciplined. The base pins a Python version and the platform comes from a build argument, so multi-architecture builds are intended. The requirements file is copied and installed before the source, specifically to keep that layer cached across source-only changes, and the package is then installed in editable mode. The image exposes one port, declares standard input and output as the default transport, and binds the network transports to all interfaces.
The protocol framework dependency is a beta with the revert path in a comment
The server protocol layer is one dependency, and it is a pre-release. Both the requirements file and the Python setup file pin it to a beta build of the third major version of a framework hosted on its own domain, with a comment naming the domain and explaining what to do if you want to go back.
The revert instruction is the same in both files: change the requirement to the official software development kit package at a stated version. It reads as a deliberate experiment rather than an oversight, since the escape hatch is documented in the two places a maintainer would actually look. It also means the dependency tree is pinned to something that can still move, and that a working install can break under a pull.
The rest of the dependency list is broad for a cluster tool: a web framework, an application server, the template layer, the official Kubernetes client, a YAML parser, two HTTP clients, a websocket client, a schema validator, a cryptography package, a terminal formatting library, and a server-sent events client. Build tooling is also listed among the runtime requirements rather than separated into a development group.
Two container registries under two different owner names
The container section offers the same image from two registries, and the owner names are not the same. One is a Docker Hub path under a personal account whose name does not match the repository owner, and the other is the GitHub container registry under the repository owner's own name. Nothing in the document explains the split, which is the kind of thing that happens when an image was first published somewhere convenient and later mirrored.
Two run modes are given. The standard input and output mode needs no ports and mounts the host's kubeconfig directory into the container read only. The HTTP mode publishes port 8000 and switches the transport with a flag.
The read only mount is the detail worth pausing on. It means the container cannot write to your kubeconfig, which is the right default, but it also means the credential it reads is the full one, so that volume is the whole attack surface for a container that can create and delete cluster resources.
Only one directory is published to npm, and a script runs after install
The npm manifest is short and has two fields that do a lot of work. The files list contains exactly one entry, the binary directory, so everything else in the repository is excluded from the published tarball. And a postinstall script runs a node file from that directory.
So an npm user installs a small package that executes a script on install, and the server they get is not in that tarball. The npm binary is a launcher, and the actual implementation has to come from somewhere else, most likely the Python side, which is why the same project ships a pip package, two container images and a launcher binary and asks you to pick one.
The git route and the release wheel route are also both documented. The wheel route is written as a template with a version placeholder and then a worked example pointing at a version from earlier in the series, so the pattern is copy the URL and swap the two version numbers. The git route installs straight from the repository.
In-cluster deployment lives in two directories, and the release gap is months
The feature list credits the project with being production grade, deployed in-cluster, with 216 passing tests and active maintenance. The test count has matching artefacts, since a pytest configuration file and a tests directory are both at the repository root, along with a separate development requirements file.
The in-cluster claim has matching directories too: a chart directory and a deploy directory, plus a server configuration file at the root and a directory that looks like a packaged application. There is also a skills directory, an evaluations directory, and a registry listing file for the ecosystem directory.
The dates are the part to weigh. The last push to the repository was in April, and the newest visible release tag is from February. That is a gap of several months between the newest release and today, which does not make the claim false, but it does mean the version you get from the branch and the version on the release page are further apart than the tag names suggest.
Editorial conclusion
Use it if you want an assistant to read and change cluster state and you are willing to run the server against a kubeconfig with real write access, because the tool surface includes deployment and resource changes rather than read only inspection. Three things to check first. The documented verification commands use a command name that a pip install does not create, so identify the right binary before concluding the install failed. The protocol framework it depends on is a pre-release third party build with the revert path written into a comment. And the newest tagged release is behind the version both manifests declare, so pin a release rather than tracking the branch.
Frequently asked questions
What command names does kubectl-mcp-server install?
The npm package installs a single kubectl-mcp-server executable, while the pip package registers two console scripts with different names pointing into the same Python package, and the documented verification commands use the npm name.
How many tools does kubectl-mcp-server expose?
The packaging files describe 270 or more tools with 8 resources and 8 prompts, while the page states 253 tools alongside the same 8 prompts and 8 resources, so only the tool count differs between them.
What Node version does kubectl-mcp-server require?
The npm manifest declares Node 16 or newer and will refuse to install below that, while the prerequisite list on the page says Node.js 14 or newer for the npx route.
How do I run kubectl-mcp-server in a container?
Pull the image and mount the host kubeconfig directory into the container read only. The default transport is standard input and output with no ports, and a flag switches to the HTTP transport on port 8000.
Which protocol framework does kubectl-mcp-server depend on?
A pre-release build of the third major version of a third party framework hosted on its own domain, with a comment in both packaging files giving the version of the official SDK to switch back to.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/rohitg00-kubectl-mcp-server)Star history chart for your README
[](https://hysenlabs.com/projects/rohitg00-kubectl-mcp-server)Was this useful?