ByeByeDPI: an Android wrapper that runs ByeDPI on the device
Приложение локально запускает ByeDPI и перенаправляет весь трафик через него
At a glance
- What is it?
- romanvht's ByeByeDPI is a Kotlin app for Android that launches the ByeDPI program locally and points device traffic through it using Android's VPN mode. It is not a VPN service, it encrypts nothing, and it does not hide your IP address.
- Who is it for?
- Adopt ByeByeDPI if you want ByeDPI running on an Android phone or TV box and you accept unencrypted traffic on a visible IP address. Leave it alone if you need encryption or address masking.
- Can I use it commercially?
- Yes, with conditions. GPL-3.0 is a copyleft licence: if you distribute software that includes it, you must release that software's source code under the same licence. Running it internally without distributing it does not trigger that obligation.
- Is it still maintained?
- Yes. The repository last received commits 16 days ago.
- What is it written in?
- Mainly Kotlin, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
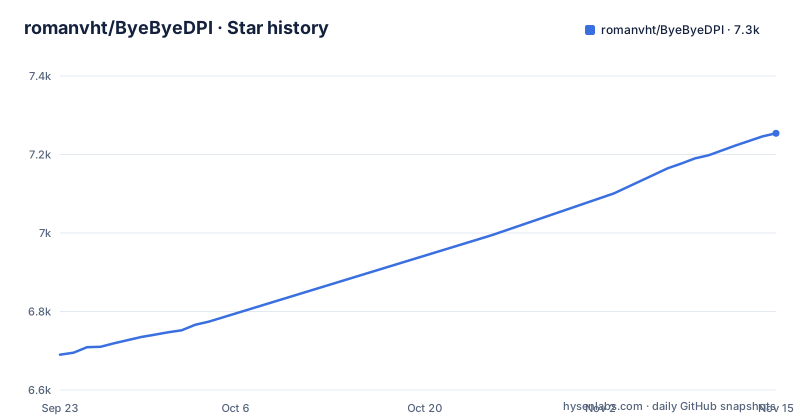
- romanvht/ByeByeDPI7,254 ★ · +564
| Repository | 2026-09-23 | 2026-11-15 |
|---|---|---|
| romanvht/ByeByeDPI | 6.7k | 7.3k |
564 Stars in the last 53 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
A local ByeDPI process behind Android's VPN service
ByeByeDPI is a Kotlin app whose entire job is to host another program. It starts the ByeDPI binary on the device itself and sends all device traffic through it, and the README is explicit that this stays local: nothing is forwarded to a remote server. The redirection mechanism is Android's VPN mode, which any app can request through the system VPN service, so the operating system draws a VPN connection in its status bar while the app runs. That is where the resemblance to a VPN ends. No tunnel leaves the handset, there is no account, and there is no server to operate or pay for. The name expands to deep packet inspection, but the repository never spells the acronym out or explains what ByeDPI does to the packets, which is one reason the upstream documentation matters so much here.
Autostart needs one manual VPN approval before it works
The service can come up on its own when the device boots, and this is the feature that makes the app usable on a phone or a permanently powered TV box. There is a catch. Android shows the VPN permission dialog once, so the order matters: switch on the autostart entry in the settings, connect once by hand to accept the request, and only then will a reboot bring the service back. It returns in whichever mode the settings hold, VPN or Proxy. Until that single approval exists, autostart has nothing to attach to. On a device that boots unattended, a set-top box in a living room, the tunnel stays down until somebody opens the app by hand once.
Saved parameter lists and per-app split tunneling
Two of the listed capabilities do the real work for a daily driver. The first is saved lists of command line parameters. ByeDPI is driven by flags, so rather than retyping them after every restart the app keeps lists of them and reuses them, which matters for anyone who has already worked out a set that holds steady. The second is per-app split tunneling, where redirection can be limited to selected applications instead of covering the whole device. Settings can be exported and imported, so a working configuration survives a reinstall or moves to a second handset. Compatibility with Android TV and BOX devices is called out as improved, which lines up with the boot-time service and the one-time approval flow, both of which suit a box that is never touched after setup.
Building the release APK and the WSL wall on Windows
Building from source is the only command path the project documents, and it needs submodules. Clone with the recursive flag:
git clone --recurse-submodules https://github.com/romanvht/ByeByeDPIThen run the wrapper from the repository root:
./gradlew assembleReleaseThe `gradlew` script and its Windows twin `gradlew.bat` sit at the root beside `build.gradle.kts`, `settings.gradle.kts`, `gradle.properties` and `.gitmodules`, and the finished APK lands in `app/build/outputs/apk/release/`. One warning sits under those steps: hev_socks5_tunnel does not build under Windows, so WSL is required for that part. The limit applies to compiling the project, not to running the result on a phone. Anyone who only wants the app can take a build from the GitHub releases the README links instead of producing one locally.
No encryption, no hidden IP, no parameter list here
Two limits are stated outright, and together they decide whether this project fits your situation. It does not encrypt traffic, and it does not hide your IP address. Whatever ByeDPI does to the packets is documented in hufrea's upstream project, not in this repository, so reading this app's docs tells you nothing about the confidentiality of a connection. Anything that depends on the tunnel to keep data private needs a different tool, and so does anything that depends on the address staying unlisted. The parameter set is absent here too. There is no table of flags, no per-flag explanation and no recommended profile, only saved lists inside the app, so a user who wants to understand a setting has to leave this repository for the upstream one.
Where the tuning knobs live: hufrea's ByeDPI documentation
The README says settings may have to change for stable operation, then sends you to the ByeDPI documentation for what each one does. That division is worth understanding before spending an evening on it, because this repository is the Android shell and the parameter documentation sits upstream. The two named dependencies are ByeDPI itself and hev-socks5-tunnel, the SOCKS5 tunnel that carries the local connection. Credits go to hufrea for ByeDPI and to dovecoteescapee for the original ByeDPIAndroid implementation this grew out of, which is unusual provenance for a small Android tool: recent wrapper work sitting on two named upstreams rather than a fork with a private protocol. The repository is licensed GPL-3.0, and nothing here states what licence the two upstream projects carry, which matters to anyone redistributing a build.
Three releases in five days and a single declared site
Maintenance looks current. The repository is not archived, and the last push landed on 2026-10-14. Three releases came within five days: v.1.8.0 on 2026-09-28, v.1.8.1 on 2026-09-29, and v.1.8.2 on 2026-10-02. That cadence suits a wrapper whose behaviour depends on an upstream tool, since the shell can be rebuilt whenever the parameters move. One official site is declared, byebyedpi.xyz, which also hosts the community manual the README links as the fuller walkthrough. There is no mirror list and no documented way to point the app at a different source, so that site is the only address to trust alongside the GitHub releases. For a tool that runs at boot with access to every app on the device, the SHA-256 signing hash printed in the README is the one control you have before installing.
Editorial conclusion
Adopt ByeByeDPI if you want ByeDPI running on an Android phone or TV box and you accept unencrypted traffic on a visible IP address. Leave it alone if you need encryption or address masking. Before installing anything, compare the APK against the SHA-256 signing hash in the README, and read hufrea's ByeDPI documentation for the parameter list this repository does not carry.
Frequently asked questions
What is ByeByeDPI?
A Kotlin app for Android that starts the ByeDPI program on the device and redirects all traffic through it, using Android's VPN mode for the redirection. It is released under GPL-3.0 and builds to an APK.
Is ByeByeDPI safe to use?
It does not encrypt traffic and it does not hide your IP address. The ByeDPI process runs locally, so nothing is sent to a remote server and there is no VPN provider involved.
How do you use ByeByeDPI on Android?
Enable the autostart entry in the settings, connect once by hand to accept the Android VPN request, and from the next boot the service starts on its own in whichever mode you selected, VPN or Proxy.
How do you set up ByeByeDPI?
Take a build from the project's GitHub releases, then expect to adjust the settings, since the README says stable operation may require changes. What the individual parameters do is documented in the ByeDPI project, not in this repository.
What is the difference between ByeByeDPI and ByeDPI?
ByeDPI is the command line program doing the traffic work, and ByeByeDPI is the Android app that hosts it locally. The app adds autostart on boot, per-app split tunneling, saved parameter lists and settings import and export.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/romanvht-byebyedpi)Star history chart for your README
[](https://hysenlabs.com/projects/romanvht-byebyedpi)Was this useful?