trezor-agent's dependency list names python-daemon twice, and its tags use two schemes
Hardware-based SSH/GPG/age agent
At a glance
- What is it?
- romanz/trezor-agent operates GPG, SSH and age signing keys held on hardware security devices so the key itself never reaches the machine. Four devices and four agent components are supported, one of which lives in another project's repository.
- Who is it for?
- Suitable if you already own one of the four supported devices and want the key to stay on it, since that is the whole design claim and it is stated plainly rather than implied. Before you rely on it, check which protocol you actually need against the documentation index, because one of the five protocol modules in the library has no page there, and note that only three of the four agent components are published from this repository.
- Can I use it commercially?
- Yes, with conditions. LGPL-3.0 is a weak copyleft licence: you can use it inside commercial and closed-source software, but if you distribute changes to its own files, you must publish those changes under the same licence.
- Is it still maintained?
- Yes. The repository last received commits 26 days ago.
- What is it written in?
- Mainly Python, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 13, 2026, and from our analysis. They are not legal advice.
Star history
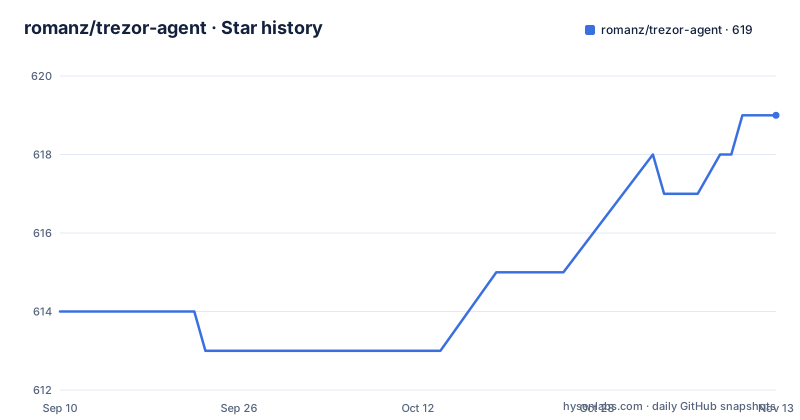
- romanz/trezor-agent619 ★ · +5
| Repository | 2026-09-10 | 2026-11-13 |
|---|---|---|
| romanz/trezor-agent | 614 | 619 |
5 Stars in the last 64 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The key is generated on the device and never reaches the computer
That sentence is the project. Instead of storing a key on the machine and unlocking it with a passphrase when you need it, the key is generated and stored on the hardware device, and the private material never arrives on the host. The design write-up lives in a separate document rather than on the repository front page, which tells you where to look for the details. What the front page does list is the range of uses: signing email, signing commits and software packages, driving password stores through two named tools, and authenticating web tunnels and file transfers. The practical consequence of the design is that each of those operations becomes a device round trip. The agent is doing the cryptography with the device rather than reading a secret, so the cost is a prompt on a small screen per operation rather than a passphrase typed into a terminal.
Four devices, four components, and one component in someone else's repository
Four hardware devices are listed as supported: two Trezor models, a Blockstream device, and an OnlyKey. The repository is described as holding one shared library plus the agents that talk to those devices, and the four components are named separately. Three of them are published as their own installable packages, the shared library and two of the agents on a package index. The fourth, the Jade agent, is linked to the Blockstream repository rather than to anything published from here. So this is a four-part project where three parts are versioned here and one part is not, which matters for anyone tracking updates: a change to the Jade path shows up as a commit in a different project's history, under a different release cycle, with a dependency boundary in between.
Five protocol modules in the library, and one has no documentation page
The shared library is installed as six packages, of which five are protocol or device modules: one for the age encryption scheme, one for device handling, one for GPG, one for SSH, and one for a third signing and verification agent protocol that the front page never mentions in prose. The documentation index has a page for installation, and then one each for SSH, GPG and age, one for configuring the PIN entry program, and one for Windows. Six pages against five protocol modules, and the pairing does not line up: the signing protocol has no page, and the PIN entry and Windows pages have no module of their own. The PIN entry page exists for a mundane reason worth naming, because a device that asks for a numeric code needs a helper program to display the layout and capture the digits in a terminal or on another system.
One dependency appears twice with two different minimum versions
The install list has fifteen entries and one of them is repeated: a daemon library is required at one version floor near the top of the list and again at a lower floor further down. Whichever resolver you use, the effective constraint is the stricter of the two, so it is harmless in practice and wrong in the file. Two other entries are more telling about how the list was assembled. A reStructuredText processor is a runtime requirement, which is a documentation-formatting library, and the wheel build tool is listed alongside it, which is a build-time package. Neither belongs in what a user installs at run time. One entry does carry a platform marker so that it installs only on Windows, and the rest are unconditional, which is consistent with a package that supports both a POSIX and a Windows platform classifier.
The release list mixes two tag schemes and one entry disagrees with itself
The three most recent releases are named inconsistently. The newest is a namespaced tag with a library prefix and a dotted version. The one before it is recorded under the same namespaced scheme while its own title uses the older plain prefix, so the name and the title of the same release disagree. The third uses the plain prefix again. Underneath the naming, the cadence is uneven: the plain-prefixed release before the two newest ones dates from September 2024, and the next release did not appear until February 2026, a gap of about seventeen months. The newest tag was published in March, and the last push to the default branch is dated July, so the working tree is several months ahead of any release. The version declared in the packaging file does match the newest tag, which is one thing that is consistent.
A production stability label next to a setup.py and a version bump file
The packaging metadata classifies the library as production stable, and it is delivered through a setup script rather than a modern build file, with a version-bump configuration file at the repository root and a separate release shell script. Linting is configured through its own file rather than a modern linter's configuration, and there is a tox file for test environments. The declared floor is Python 3.8, while the classifier list mentions only that the package is Python 3 and gives no per-minor versions, so a user cannot tell from the metadata which interpreters are actually exercised. The licence is declared as the LGPL in both the repository and the classifiers, which is the one place where the two surfaces agree completely.
The feature history is documented through vendor firmware announcements
The three blog posts the front page points at are not project write-ups. They are firmware release announcements for three successive versions of the Trezor firmware, covering SSH login, then signing and transaction features, then decryption support. Two are hosted on a blogging platform and one on a forum thread. That choice tells you where the capability boundaries come from: this project cannot add a signature scheme the firmware refuses to perform, so the project's own history is a sequence of firmware versions. The gap is that all three announcements concern SSH and GPG. The age encryption scheme has its own documentation page and its own module in the library, but no announcement among the three describes it, so the newest protocol the project supports is the one with no vendor post behind it.
Editorial conclusion
Suitable if you already own one of the four supported devices and want the key to stay on it, since that is the whole design claim and it is stated plainly rather than implied. Before you rely on it, check which protocol you actually need against the documentation index, because one of the five protocol modules in the library has no page there, and note that only three of the four agent components are published from this repository. Install it as a library rather than from a tag, since the tag naming is inconsistent across releases.
Frequently asked questions
What does trezor-agent actually do?
It uses hardware security devices to operate GPG, SSH and age. The key is generated and stored on the device so it never reaches the computer, and the uses listed include signing email, commits and packages, driving password stores, and authenticating tunnels and file transfers.
Which hardware devices does trezor-agent support?
Trezor One, Trezor Model T, Blockstream Jade and OnlyKey. Each has its own agent component, and the Jade agent is linked to the Blockstream repository rather than published from this one, so three of the four components are versioned here.
Does trezor-agent support age encryption?
Yes. The library is installed with a dedicated age subpackage and the documentation index has its own page for age with common use cases. Age is one of five protocol modules, the others being device handling, GPG, SSH and a signing and verification protocol.
What are the runtime dependencies of the trezor-agent library?
Fifteen entries, and one daemon library appears twice with two different minimum versions. The list also includes a reStructuredText processor and the wheel build tool as runtime requirements, and only one entry carries a platform marker so that it installs on Windows alone.
How is trezor-agent versioned and released?
Two tag schemes appear in the release list, a namespaced library tag for the newest release and plain prefixed tags for the older ones, with one entry whose recorded name and title disagree. The newest tag was published in March and the last push to the default branch is dated July.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/romanz-trezor-agent)Star history chart for your README
[](https://hysenlabs.com/projects/romanz-trezor-agent)Was this useful?