rs/cors: zero dependencies, four ways to answer the origin question, and a sample response from 2014
Go net/http configurable handler to handle CORS requests
At a glance
- What is it?
- A Go handler that implements the cross-origin resource sharing specification and depends on nothing at all, which is the reason it is still the answer in most Go services. What the page shows is also a library that broke one of its own popular behaviours on purpose, four options that each silently override the one before, and a quick start that still describes a workflow the module file has replaced.
- Who is it for?
- Use this when you are writing a Go service and want cross-origin handling that adds nothing to your dependency graph, and treat the defaults as a starting point rather than a configuration. Four of them are permissive by design: every origin is allowed, only the two simple methods are permitted, credentials are off, and the preflight cache lifetime is zero.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 14 days ago.
- What is it written in?
- Mainly Go, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
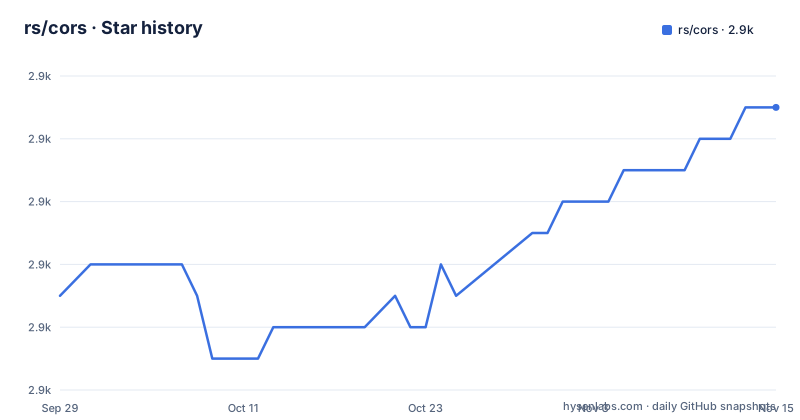
Star history
- rs/cors2,903 ★ · +6
| Repository | 2026-09-29 | 2026-11-15 |
|---|---|---|
| rs/cors | 2.9k | 2.9k |
6 Stars in the last 47 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The quick start describes a workflow the module file has replaced
The getting started section opens by telling you to install Go and set up your GOPATH, which is the pre-modules way of working. It then has you create a file, add the handler to a multiplexer, and serve it:
handler := cors.Default().Handler(mux)
http.ListenAndServe(":8080", handler)
The default configuration, as the comment in that sample says, accepts all origins with the simple methods. Installation is a single command, and the page's own remark about a workspace path being set up first belongs to a workflow that a module file makes unnecessary. The module file in the repository root declares the module path and a language version, and it declares no requirements at all. That last detail is the one that matters: a cross-origin handler is a piece of infrastructure that ends up in the request path of every route, and this one brings no transitive dependencies with it, which is unusual enough in a Go library that it is the first thing to check when you are choosing between candidates.
The sample response does not match the sample request
The page shows a request and the response it produced, which is the kind of thing readers copy without checking. The request sends an origin header of a full URL with a scheme. The response shown underneath returns the allowed-origin header with the scheme missing, and its date header reads 2014. So the block is a twelve-year-old capture, and the header value in it is not what the current code would echo back for that request, since the handler reflects what it was given. Nothing here suggests the library is wrong; the documentation is simply older than the code, and it is the documentation a reader is most likely to trust because it looks like a transcript. If you are using this as your expected-output baseline in a test, regenerate it. The same age shows up elsewhere on the page: the API documentation link points at the retired godoc domain rather than the current package documentation site, and the coverage badge points at a wiki mirror rather than a report the project generates itself.
A popular workaround was removed on purpose, with the code to restore it
One section is worth reading twice, because it documents a behaviour the library used to have and does not. Configuring the allowed origins as everything while also allowing credentials used to make the handler reflect the request's origin header back. That worked around a protection built into the standard, which is that clients are supposed to refuse a response that combines a wildcard origin with credentials, so echoing the origin was a way to make an otherwise rejected configuration appear to succeed. The page says this behaviour was removed, citing two issues by number, and explains why: it was a security problem. It then does the honest thing and tells you how to get it back if you depend on it and understand the implications, by supplying an origin function that always returns true. A library that breaks its own popular behaviour on purpose and documents the way back is unusual, and the removal is the kind of change that belongs in an upgrade checklist rather than in a changelog nobody reads.
Four ways to answer the origin question, each ignoring the ones before it
The origin options are not four independent hooks, they are a precedence chain, and that is the detail most likely to cost you an afternoon. First the origin list, a slice of strings where a wildcard entry allows everything. Then an origin function taking just the origin string, which if set causes the list to be ignored entirely. Then a request-aware version taking the whole request and the origin, which if set causes both earlier options to be ignored, and which the page marks as deprecated in favour of the next one. Then the recommended one, which takes the request and the origin and returns not only a decision but the list of headers that decision depended on, so they can be added to the response's vary header. Setting it ignores all three previous options. So if you configure a list and a callback while debugging, one of them is silently doing nothing, and the recommended option is also the most elaborate, because correct caching in front of a proxy requires that vary header to be honest about what the answer depended on.
The defaults are permissive and the safe configuration is entirely opt-in
Read the defaults as a list and the shape of the library is clear. The allowed origins default to a wildcard, meaning every origin is accepted. The allowed methods default to the simple methods, which the page names as a get and a post, so anything else needs adding. Credentials default to false. The preflight cache lifetime defaults to zero, which the page spells out as no maximum age, meaning browsers re-check every time. There is no stated default for the allowed headers or the exposed headers, and both exist as options. Separately, there is an option for accepting cross-origin requests over a private network, one for letting your own handlers process the preflight method when your application handles it, and one for changing the status code returned on a successful preflight, which defaults to no content. Wildcards inside an origin are allowed and replace zero or more characters, only one per origin, and the page warns that using them carries a small performance penalty.
Ten router examples, several for frameworks that no longer exist
The more examples section lists eleven integrations, and it reads as a history of Go routing rather than a set of current recommendations. Alongside the standard library handler there is a microframework, two middlewares from a framework that has been dormant for years, a router that has since been renamed and rewritten, the gorilla multiplexer, a full-stack framework, two web frameworks that are still widely used, and a lightweight router. Each links to a server file in its own directory, and the tree confirms those directories exist, plus one the page never mentions. The examples also carry their own module manifest and lock file, which means they are a separate module from the library and are not exercised by running the library's own tests. That is a reasonable arrangement for eleven sample servers with a dozen dependencies between them, and it also means a broken example can sit in the tree indefinitely without anyone noticing, which is close to what has happened to the examples for the frameworks that are no longer maintained.
Three source files, and a benchmark block showing what the default costs
The repository is small in a way that matches the dependency claim. The root holds the licence, the readme, three Go files with their tests, a benchmark file, an internal directory and a directory named wrapper, whose purpose the page never explains. There is no configuration, no code generation and no build tooling to speak of, which is what a handler that only reads a header and writes a header should look like. The benchmark block on the page is the most useful number on it and it is also a capture rather than a claim: it was taken on an arm64 Mac with a ten-core machine, where passing a request through with no cross-origin handling at all costs about eight nanoseconds and allocates nothing, and the default configuration costs roughly fifty nanoseconds. That gap, and the allocations that come with it, is the price of the permissive default, and it is the kind of figure you want before pointing this at a hot path rather than a paraphrase of what the library promises.
Editorial conclusion
Use this when you are writing a Go service and want cross-origin handling that adds nothing to your dependency graph, and treat the defaults as a starting point rather than a configuration. Four of them are permissive by design: every origin is allowed, only the two simple methods are permitted, credentials are off, and the preflight cache lifetime is zero. Set the origin list explicitly, decide whether credentials are needed, and pick one of the origin callbacks rather than mixing them, since each one silently ignores the options before it. If you have code in production that relies on reflecting the request origin while allowing credentials, that path was removed deliberately and the page tells you how to get it back. The default branch was last pushed on 2026-06-04 and the repository publishes no releases, so pin a commit if you need reproducibility.
Frequently asked questions
What does CORS stand for?
Cross Origin Resource Sharing. This library is a net/http handler that implements the W3 specification of that name in Go, and the page states the acronym in full. The specification is what makes a browser refuse to hand a response to a script on another origin unless the response says so, and the handler's job is to answer that question on the server.
How can I fix a CORS error?
The library ships three options aimed at exactly that. A debug flag adds server-side output for diagnosing cross-origin problems, with the page's own comment saying to enable it for testing and consider disabling it in production. An option lets your own handlers process the preflight method if your application already handles it. Another sets the status code returned on a successful preflight. There are also lists for the non-simple headers a client may send and the headers that are safe to expose.
Why does rs/cors not reflect the Origin header when credentials are allowed?
Because that behaviour was deliberately removed. Allowing all origins while also allowing credentials used to make the handler echo the request origin, which worked around the protection in the standard that makes clients refuse that combination, and it was treated as a security problem and taken out. The page explains that if you depend on it and accept the implications, you can restore it by supplying an origin function that always returns true.
How do I allow a wildcard subdomain in rs/cors?
An entry in the allowed origins list may contain a wildcard that replaces zero or more characters, so an origin of the form used for a subdomain wildcard works. Only one wildcard is allowed per origin, and the page warns that using wildcards carries a small performance penalty. Leaving the list at its default of everything allows all origins.
What does rs/cors depend on?
Nothing. The module file declares the module path and a language version and has no requirements at all, which is unusual for a Go library that other services pull in. The examples have their own separate module with a manifest and a lock file, so the sample servers do not add dependencies to the library itself either.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/rs-cors)Star history chart for your README
[](https://hysenlabs.com/projects/rs-cors)Was this useful?