Vestige: A Rust MCP Memory Daemon That Walks Causes Backward and Gates Agent Commands With 102 Rules
Vestige enhances agents by deterministic root-cause retrieval that reaches backward through time to find the quiet change, decision, or service that caused today’s failure, not the lookalike.
At a glance
- What is it?
- Vestige is an AGPL-3.0 Rust daemon for AI coding agents that replaces vector search with a signed, append-only ledger queried by exact handles, plus a rule gate that blocks destructive commands. Its README is full of self-described firsts, so the verifiable details matter most.
- Who is it for?
- Vestige is aimed at people running autonomous coding agents who want a command gate and a causal memory that refuses fuzzy queries. Treat its superlatives as marketing and verify the gate yourself with the replay it offers.
- Can I use it commercially?
- Yes, with strict conditions. AGPL-3.0 is a network copyleft licence: if people use a modified version over a network, for example as a hosted service, you must offer them its source code under the same licence.
- Is it still maintained?
- Yes. The repository last received commits 1 day ago.
- What is it written in?
- Mainly Rust, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 14, 2026, and from our analysis. They are not legal advice.
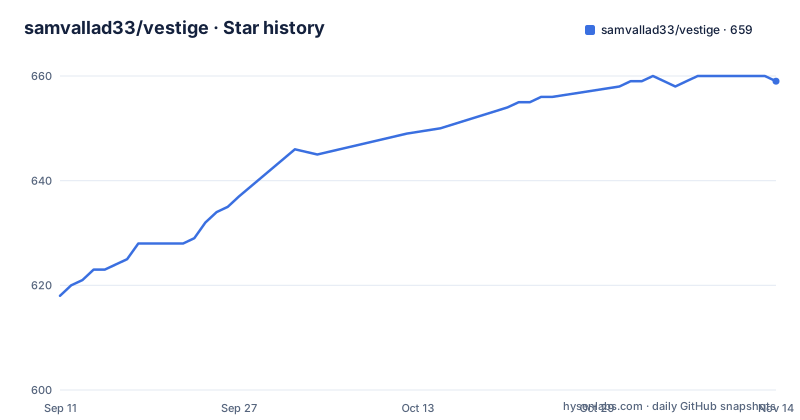
Star history
- samvallad33/vestige659 ★ · +41
| Repository | 2026-09-11 | 2026-11-14 |
|---|---|---|
| samvallad33/vestige | 618 | 659 |
41 Stars in the last 64 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
One npx command wires four hooks into your IDE and replays 30 days of transcripts
The quick start is a single command that does a lot:
npx @vestige/initAccording to its own text, this installs the `vestige-mcp` Rust daemon, wires four autonomic Reflex hooks into your IDE, and replays your last 30 days of agent transcripts against the 114-rule gate. The IDEs named are Claude Code, Cursor, Codex, Windsurf and Gemini CLI. The replay is meant to show every destructive command or failure loop Vestige would have stopped.
Two consequences are worth weighing before you run it. The command changes your agent tooling configuration across several editors in one go, so you should know what it touched. And it reads your past agent transcripts, which may contain secrets or private code, so check where that data goes. The gate itself is described as making no network call. To confirm the store and the six-tool surface afterwards, run:
vestige precedent --query verify_logThe package manifest requires Node 18 or newer for the installer side, while the daemon is a native Rust binary.
The gate counts to 114 but installs 102 stop rules, and deterministic means no model call
The numbers in the Operator description look inconsistent until you do the arithmetic. Running `npx @vestige/init --guard` installs 102 STOP rules numbered OP-000 through OP-114, with OP-086 to OP-097 and OP-100 reserved. That is 115 numbers minus 13 reserved ones, which gives 102 active rules, while the headline figure of 114 refers to the top of the numbering range.
The gate stops force pushes, dropped tables, recursive deletes, production deploys, credential reads and the rest of a closed list before they run, even when the command is disguised. Classification is deterministic, with no model call and no network call. Operator Lite, with rules OP-000 through OP-025, is pinned beside the gate and judges every call too. An existing `~/.operator/gate/operator-gate.py` is left in place.
The limit of any closed list is that anything not on it passes. A destructive action that no rule names will not be stopped, and the README claim that a disguised command is still caught is only as good as the rules written. Run the transcript replay on your own history to see what the gate would have caught.
Memory is queried by exact handles, and free-text guesses are refused
The project's main design claim is that memory retrieval should find a cause, not a similar-looking item. Its text says it removed ONNX, vector embeddings, keyword search and SQLite. In their place, memories are indexed by exact handles: `id`, `tag`, `commit:<sha>`, hunk-level touched-file edges and interned stack-trace symbols.
The tool `causal_walk` traverses those links backward from a failure. Free-text guessing is refused. When that happens, a Handle Discovery step parses your query and returns exact candidate handles found in your words.
This is a trade-off that the marketing frames as a win. The example given is a stack trace for a connection pool failure at 3:00 PM and a config edit of `max_idle_time = 0` at 9:00 AM, which share no semantic similarity yet are causally linked. A vector index would miss that link, and a handle-based walk can follow it. The price is that you cannot ask a vague question like what did we decide about caching and expect a ranked answer. If your memory needs are conversational recall, this design will feel strict, and the claim that vector retrieval fails every time in such cases is the author's statement, not a measured result.
An append-only ledger signs nightly segments, while decay quietly removes noise
Underneath sits a ledger named S.T.R.A.T.A. Every memory write, tool call and gate stop is recorded as a frame carrying the BLAKE3 hash of the frame before it, and nightly segments are sealed with Ed25519 signatures. That makes the history tamper-evident, which suits an audit trail for an agent's actions.
Memory is not kept forever. FSRS-6 decay lets unverified, unreferenced session noise fall out of working memory so context stays small. To avoid losing the cause of a later failure, Retroactive Salience Backfill walks the graph backward when a downstream failure or high-salience constraint is saved, rescues the quiet upstream root-cause memory from decay, boosts its salience and writes a reversible cryptographic receipt.
The consequence is that forgetting is automatic. A fact that nobody referenced and no failure later pointed to can decay, even if you would have wanted it. Pin anything that must survive. The README also describes a prove step, `causal_walk(action="prove")`, that verifies a fix with deterministic git-bisect test witnesses, so claims about causes can be checked against the repository.
Six MCP verbs and a Unix socket carry the whole agent interface
The model-facing surface has six verbs: session, remember, recall, causal_walk, curate and precedent. The README contrasts these with the Reflex hooks, which fire in zero LLM turns through a Unix domain socket at `~/.vestige/reflex.sock`. That socket is described as bridging external shell hooks into the in-memory graph in under 0.2 ms and avoiding `.serve.lock` contention when several IDE windows run at once.
The first reflex, Reflex::SessionStart, runs on boot, resume or context compaction. It queries the local Git index against the graph and injects the top five hot entity handles, with id, tag, last touched file and FSRS-6 retrievability, plus pinned repo rules. The agent therefore starts its first turn already holding the handles it needs.
The timing figures and the claim of zero lock contention come from the project's own text. The repository does contain a benchmarks directory, but no benchmark results appear in the README, so treat the 0.2 ms number as the author's claim until you measure it. The socket also ties the tool to Unix-style systems in its documented path, so Windows users should check support before depending on it.
The prebuilt binary is glibc-only, and the container recipe shows it
The Dockerfile in the repository explains the install mechanics. Its base image is `node:20-slim`, a Debian glibc image, with a comment stating that the base must be glibc, not musl or Alpine. The reason: the npm postinstall downloads the prebuilt x86_64-unknown-linux-gnu Rust binary from the GitHub release, and a gnu binary will not run on musl.
The install line in the container is:
RUN npm install -g vestige-mcp-server@latestIt sets `VESTIGE_DATA_DIR=/data` to keep memory inside the container and starts the server on stdio with the entrypoint `vestige-mcp`. The file says it exists for registries such as Glama that run the standard MCP stdio introspection exchange.
So on Alpine, or on a platform without a matching release asset, the npm route cannot give you a working binary. You would build from source instead. The package script builds with:
cargo build --release --package vestige-mcpThe Cargo workspace uses edition 2024 and a release profile with LTO, a single codegen unit, panic abort, symbol stripping and opt-level z, which is how the README can claim a binary of about 7.8 MB. That size is a claim about the release build, so confirm it on your platform.
Operator companions are sold separately, and the license is AGPL-3.0 with a CLA
The 102-rule gate is in the repository and is what `--guard` installs. But the companion modules board, letter, almost-forgot, onboard and briefing only load when their files sit next to the gate, and those files come from a paid product. The README links a purchase page for Vestige Operator at $149 once, with every later version included and a 30-day refund. So the open repository is the gate and the memory daemon, while those five commands need the purchase.
The code is licensed AGPL-3.0, and the manifest says AGPL-3.0-only. That is a strong copyleft license whose network clause applies if you modify the program and offer it to users as a service. The repository also carries CLA.md and CLA-ENTITY.md files, so contributions come with a contributor license agreement.
The release pace is fast: v5.0.1 on 2026-10-23, v6.0.0 on 2026-10-28 titled around Reflex hooks reaching Vestige, and v6.2.0 on 2026-11-03, with the last push on 2026-11-02. Two major-version steps in a few days mean behaviour and rule numbering can change quickly, so pin a version and read the CHANGELOG before upgrading. The README cites a study of 757 agent memory systems hosted at the same repository address, so it is not independent evidence.
Editorial conclusion
Vestige is aimed at people running autonomous coding agents who want a command gate and a causal memory that refuses fuzzy queries. Treat its superlatives as marketing and verify the gate yourself with the replay it offers. It is a poor fit if you need free-text semantic recall, a permissive license, or a quiet release history: queries need exact handles, the license is AGPL-3.0, and major versions arrived within a week.
Frequently asked questions
What is Vestige for AI agents?
Vestige is a Rust MCP daemon for AI coding agents. It keeps a signed append-only memory ledger queried by exact handles, and installs a deterministic rule gate that blocks destructive commands before they run.
How do I install Vestige?
Run npx @vestige/init. It installs the vestige-mcp daemon, wires four Reflex hooks into IDEs such as Claude Code and Cursor, and replays 30 days of agent transcripts against the gate.
What license does Vestige use?
Vestige is licensed AGPL-3.0, listed as AGPL-3.0-only in its manifest. The repository also includes CLA files for contributors.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/samvallad33-vestige)Star history chart for your README
[](https://hysenlabs.com/projects/samvallad33-vestige)Was this useful?