Sandboxie: one core shared by two editions, and a Plus feature list that keeps growing
Sandboxie Plus & Classic
At a glance
- What is it?
- Sandboxie isolates Windows programs into sandboxes that leave local and mapped drives and the registry untouched, and the fork ships it twice, as a Qt based Plus edition and an old MFC based Classic one. The security core is identical, so the choice you are really making is how much of the configuration you want through a window and how much through Sandboxie.ini.
- Who is it for?
- Adopt Sandboxie Plus if you need the per-sandbox firewall, the trigger system, or the security enhanced restrictions, because those exist in the Qt interface and are awkward to reach from Classic. Do not adopt Classic expecting parity: its MFC interface is no longer developed, and the project says it is not recommended for the latest security options.
- Can I use it commercially?
- Yes, with conditions. GPL-3.0 is a copyleft licence: if you distribute software that includes it, you must release that software's source code under the same licence. Running it internally without distributing it does not trigger that obligation.
- Is it still maintained?
- Yes. The repository last received commits 3 days ago.
- What is it written in?
- Mainly C, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 13, 2026, and from our analysis. They are not legal advice.
Star history
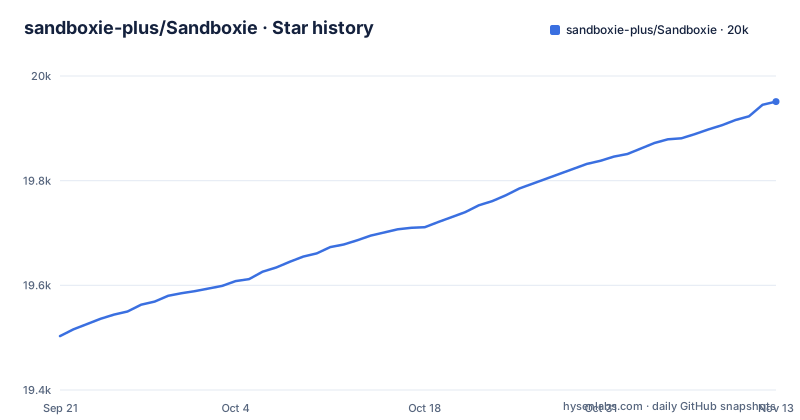
- sandboxie-plus/Sandboxie19,951 ★ · +448
| Repository | 2026-09-21 | 2026-11-13 |
|---|---|---|
| sandboxie-plus/Sandboxie | 19.5k | 20k |
448 Stars in the last 53 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Two editions, identical core, and the interface is the whole difference
The fork publishes Sandboxie twice, and the relationship between the two builds is stated plainly. Plus and Classic share the same core components, which means they have the same level of security and compatibility. What differs is the availability of features in the user interface. Plus is a modern Qt based interface that supports all the features added since the project went open source. Classic is the old MFC based interface, described as no longer developed, so it has no native support for the Plus features. The escape hatch Classic users are given is manual work: some missing features can be configured by hand in `Sandboxie.ini`, or replaced with custom scripts, and the project's own judgement is that Classic is not recommended for users who want to explore the latest security options. That is the alternative worth weighing before you install anything, and it is not a close one. Licences follow the split, with `LICENSE.Plus` and `LICENSE.Classic` sitting at the root, so read the one that matches your download rather than assuming the GPL-3.0 label covers both identically.
The isolation boundary is drives, mapped drives, and the registry
What the software does is narrow and checkable. It is sandbox based isolation software for Windows NT based operating systems, and it creates an environment where applications can be run or installed without permanently modifying local and mapped drives or the Windows registry. The stated purpose is controlled testing of untrusted programs and web surfing. You can create what the README calls virtually unlimited sandboxes, run them alone or simultaneously, and inside a single box run as many programs as you want, with programs isolated from the host and from each other. Two details change how much you should trust that boundary. Protections of sandboxes against the host include the prevention of taking screenshots, and Plus replaces the token creation mechanism of the pre-open-source version, which the project says makes sandboxes more independent in the system. Browsers get their own admission of defeat. A browser compatibility wizard in the Plus edition creates templates for unsupported browsers, which is a way to generate a workaround rather than a promise that a given browser is supported.
The network side is four separate controls, not one on/off switch
Sandboxing a program is not the same as isolating its network, and Plus treats the two separately. There is a network firewall per sandbox which supports the Windows Filtering Platform, and separate DNS control by blocking or redirecting. There is also a way to force programs to automatically use a user provided SOCKS5 proxy, and a set of options for blocking access to Windows components such as the printer spooler and the clipboard. The consequence for anyone configuring this is that you can have a sandbox with disk redirection and full connectivity, or the same sandbox cut off at the firewall, and the DNS setting is independent of both. For untrusted code that resolves names on your behalf, the redirect and block options are the controls that matter, and the SOCKS5 option is the one that changes where your traffic appears to come from. Classic reaches none of these through its interface, so a Classic user who wants them is editing configuration by hand.
Triggers, snapshots, and 7z export cover what a sandbox does over time
Most sandbox documentation is about the moment a program starts. The Plus feature set also covers the states around it. There is a trigger system that performs actions when a sandbox goes through different stages, named as initialization, box start, termination, and file recovery, which means a policy can be attached to a phase rather than to every process inside the box. A Snapshot Manager takes a copy of any box so it can be restored when needed, and sandboxes can be imported and exported to and from 7z files, which is the practical way to move a configured box between machines or keep one per task. An Encrypted Sandbox provides an AES based data storage solution. Global hotkeys can suspend or terminate all boxed processes at once, and the sandbox list itself is searchable with Ctrl+F. Memory is bounded too, per process and in total, and the number of sandboxed processes per box can be capped, which is the control that keeps one runaway program from filling memory.
The custom UAC dialog and the syscall restrictions decide what a privilege prompt means
Windows asks a question when a program tries to gain administrator rights, and Sandboxie has an opinion about the answer. A custom UAC dialog lets you fake a permission, grant it, or cancel the elevation attempt, so a test can proceed past a prompt that would otherwise stop it. Privacy mode sandboxes are described as protecting user data from illegitimate access, and security enhanced sandboxes restrict the availability of syscalls and endpoints, which is a deeper cut than a file redirect. Two smaller controls are worth knowing. One feature prevents sandboxed programs from generating an unnecessary unique identifier in the normal way, which removes a fingerprint signal, and another feature can make a process itself unsandboxed while its child processes stay sandboxed, which is a deliberate hole you can open for a launcher. Privacy mode is also a Plus feature, so a Classic user cannot reach it from the interface at all.
The documentation lags the feature list, and the forum is a partial archive
For a security tool, stale documentation is a cost you should price in. A GitHub copy of the Sandboxie documentation is maintained at `sandboxie-plus.github.io/sandboxie-docs`, and the README says plainly that more volunteers are needed to keep it updated with the new changes. It also recommends checking the issue labels to track current issues, which is an admission that the docs are not the fastest source. The old Sandboxie forum, previously maintained by Invincea, survives as a partial archive, and the project gives you the search syntax to work with it:
site:https://sandboxie-website-archive.github.io/www.sandboxie.com/old-forums/Partial archive is the important word, and the Classic edition leans on that archive for its custom script workarounds. Meanwhile the feature record lives elsewhere: the README suggests finding the sign `=` with Ctrl+F in `CHANGELOG.md` to spot more features. So a new Plus option may exist before any page describes it, and the two places to check are the changelog and the labels. When you need to know what a program did rather than what the docs say, the project points outside itself again, to an add-on called LogApiDll that adds verbose output to the Sandboxie trace log and lists invocations of relevant Windows API functions.
No install command, two version numbers in one tag, and Windows 7 as the floor
Expect no command line from this project. The download section of the README is a single link to the latest release, the stated system requirement is Windows 7 or higher on 64-bit, and that section documents no installer command. Distribution runs through GitHub Releases, and the repository carries GitHub Actions workflows for codespell and for winget. Watch the tag names. The newest three releases are named v1.19.0 with a second number 5.74.0, v1.18.8 with 5.73.8, and v1.18.7 with 5.73.7, so one release carries both a 1.x line for the fork and a 5.7x line inherited from the earlier code, which makes any dependency or script that parses a Sandboxie version ambiguous. The tree around it is Windows native: `Sandboxie/`, `SandboxiePlus/`, `SandboxieTools/`, an `Installer/` directory, the batch scripts `MergeDbg.cmd` and `TestCI.cmd`, and both `AGENTS.md` and `CLAUDE.md` at the root.
Editorial conclusion
Adopt Sandboxie Plus if you need the per-sandbox firewall, the trigger system, or the security enhanced restrictions, because those exist in the Qt interface and are awkward to reach from Classic. Do not adopt Classic expecting parity: its MFC interface is no longer developed, and the project says it is not recommended for the latest security options. Verify first which of LICENSE.Plus or LICENSE.Classic governs the edition you download, since the two live side by side in one repository under GPL-3.0, and read SECURITY.md before you point it at anything you do not control.
Frequently asked questions
Is Sandboxie still free?
The repository publishes the source under GPL-3.0 with two licence files, LICENSE.Plus and LICENSE.Classic, and the README's download section is a single link to the latest release page. The Plus edition adds features over Classic, and both share the same core components.
What is Sandboxie used for?
For controlled testing of untrusted programs and web surfing, and for running or installing applications without permanently modifying local and mapped drives or the Windows registry. Programs inside a sandbox are isolated from the host and from each other, and you can create what the README calls virtually unlimited sandboxes to run alone or at the same time.
Is Sandboxie the same as Windows sandbox?
Sandboxie's README describes its software as sandbox based isolation for Windows NT based systems requiring 64-bit Windows 7 or higher, shipped as two editions, Plus and Classic, and notes that this repository is a community fork that took place after the release of the Sandboxie source code.
how to install sandboxie plus
The README's download section gives no install command. It points to the latest release page, states a requirement of Windows 7 or higher on 64-bit, and notes a Portable mode in the Plus edition where you run the installer and choose to extract all files to a directory instead of a normal install.
how to use sandboxie
You create sandboxes, then run programs in them alone or several at once, with as many programs in one box as you want. In the Plus interface, per-sandbox settings cover a Windows Filtering Platform firewall, DNS blocking or redirecting, a SOCKS5 proxy, memory limits per process and per box, a limit on sandboxed process count, and a Snapshot Manager that copies a box for later restore.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/sandboxie-plus-sandboxie)Star history chart for your README
[](https://hysenlabs.com/projects/sandboxie-plus-sandboxie)Was this useful?