larasend: self-hosted email control plane, and a control mailer that cannot be itself
Self-hosted transactional email platform — send through your own AWS SES account, keep the dashboard, API keys, delivery logs, and webhooks on your own infrastructure.
At a glance
- What is it?
- A transactional email platform for Laravel teams that keeps the dashboard, API keys, delivery logs and webhooks on your own infrastructure while sending through your own SES account or Cloudflare Email Service. Its sharpest design decision is refusing to let the instance be its own account recovery path.
- Who is it for?
- Larasend suits Laravel teams that want their email logs, previews and API keys on infrastructure they control while still sending through a provider account they own, and the two-provider design is genuinely useful when open and click tracking only exists on one of them. Three things to check first.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 9 days ago.
- What is it written in?
- Mainly PHP, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
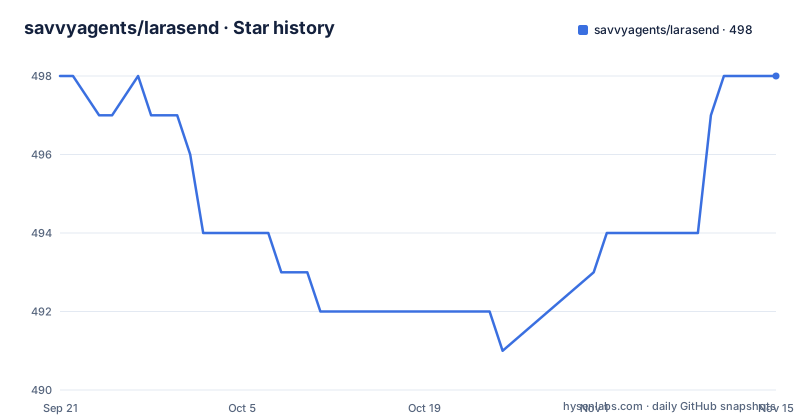
- savvyagents/larasend498 ★ · +0
| Repository | 2026-09-21 | 2026-11-15 |
|---|---|---|
| savvyagents/larasend | 498 | 498 |
0 Stars in the last 55 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Control mailer rejects log, array and larasend on purpose
The account system is wired so the instance can never be its own only recovery path. Authentication email is deliberately separate from the transactional provider.
While control mail is disabled, the first installation owner and any users created in that window stay accessible without verification. Verification, password recovery and new-member invitations only activate once an administrator points `LARASEND_CONTROL_MAILER` at a tested, independently configured mailer. Four are named as acceptable: smtp, ses, postmark and resend.
Three are explicitly refused: `log`, `array` and `larasend`. Those are the two Laravel drivers that write nowhere and the one that would route account mail back through the platform being recovered.
The defaults reflect that: the example environment ships `MAIL_MAILER=log` with an empty control mailer, so a fresh install is reachable but not mailable. The documented configuration sets them apart:
MAIL_MAILER=log
LARASEND_CONTROL_MAILER=smtp
MAIL_HOST=smtp.example.com
MAIL_PORT=587
MAIL_USERNAME=...
MAIL_PASSWORD=...
[email protected]
Leaving the control mailer blank is supported rather than broken. Workspace owners see a dashboard warning, and an invitation that would create an account nobody can reach is blocked before it is sent.
Forced verification exists as a shell command, and it is the emergency exit
Once a real control mailer is configured, the normal path is verification by email. There is also a command for the case where it is not:
php artisan larasend:verify-user [email protected] --forceAn administrator with shell access can verify one exact account explicitly. The address is an argument rather than a pattern, so this is a single-account operation, and the force flag is what distinguishes it from ordinary verification.
That combination is the right shape for a recovery path. It requires shell access to the host, which is the same access level needed to read the environment file, and it cannot be turned into a bulk operation by someone who only has dashboard access. The page frames it as emergency recovery rather than a routine admin tool.
There is a matching health check for the other direction. After a first deployment and after operational changes, a doctor command is meant to be run from an environment that can reach the production services:
php artisan larasend:doctorNote the asymmetry between the two commands. Verification is deliberately narrow and forceful. The doctor is broad and meant to be run often. The documentation distinguishes them by saying when to run each rather than by explaining what either one checks, which is the main thing a reader has to find out from the installed application itself.
Cloudflare has no event webhooks, so delivery state is a send-time record
The two supported sources do not report back the same way, and the page is explicit about the gap.
Amazon SES publishes delivery, bounce, complaint, open, click and suppression events back through the SES webhook, so those states arrive after the fact. Cloudflare Email Service has no event webhooks and no open or click tracking. For those sources, delivery state is recorded at send time, and the suppression list is synced hourly from Cloudflare's account-level list.
That is a real behavioural difference between choosing one source over the other, not a limitation of the platform's implementation. On SES you learn what happened. On Cloudflare you learn what you sent, and you learn about bounces and complaints a batch at a time rather than per message.
Inbound is the other asymmetry. Cloudflare sources can receive mail: one click deploys a Worker and a routing rule, received mail lands in the dashboard and fires `inbound.received` webhooks. The team inbox threads inbound and outbound into conversations with reply, compose, forward, attachments, rich text, drafts, snooze and internal notes.
Choosing between the two sources is therefore choosing between better send telemetry and inbound mail. The requirements section also puts a floor on the Cloudflare path, which needs a Cloudflare account on the Workers Paid plan with a domain onboarded for email sending.
Raw MIME must sit on durable storage, and the docs say so explicitly
Larasend stores the MIME payload of every message, which is what makes previews, headers and email downloads work in the dashboard. Where that content lives is therefore load-bearing, and the deployment guidance is unusually direct about it.
For an S3-compatible disk you set two variables, the general filesystem disk and the MIME disk. The warning that follows is the part worth quoting: do not point the MIME disk at a deployment's ephemeral local filesystem, because queued delivery, inbound attachments and email downloads all depend on that content being available to every web and worker instance.
The bundled single-host stack does not have that problem. Its named storage volume is mounted into the web app, the queue worker and the scheduler at the same path, so all three see the same bytes.
A managed deployment does. On Laravel Cloud the guidance is to configure durable object storage, and the failure mode it warns about is the quiet one, where the web container has the file but a worker spun up elsewhere does not, and delivery fails for reasons that look like provider errors.
The example environment defaults both variables to local, with no comment explaining that this is a single-host default. The comment about the local disk is in the managed-deployment section instead, so a reader who only reads the example file is relying on the compose setup to save them.
Three services share one image and one volume, and only the app migrates
The compose file defines the web app, a queue worker and a scheduler, all from the same image with the same command overridden, and all mounting the same named volume at the application's storage path.
The worker runs `php artisan queue:work --queue=default,webhooks --tries=3 --timeout=150`, so queued email and webhook delivery share one queue worker with three retries and a hundred-and-fifty-second timeout. The scheduler runs `php artisan schedule:work` rather than a cron loop.
The two background services both set a migrations flag to false, and the web app is the only service that runs migrations, automatically on boot. That flag exists to stop three containers racing on the same schema at startup.
Startup ordering is enforced through health conditions rather than plain depends-on. The app waits for PostgreSQL to report healthy and only for Redis to have started. The worker and scheduler both wait for the app to be healthy and for Redis to be healthy, which is stricter on the Redis side than the app is. The app's own health check hits an `/up` endpoint with wget every five seconds, with a fifteen-second start period and up to twenty retries.
That ordering is what makes the single-volume arrangement safe, and it is also why the compose file's first dependency line is a condition rather than a name.
Two of the three build stages exist to produce files the third stage copies
The image is built in three stages and only the last one ships.
A vendor stage starts from the Composer image, copies the two manifest files plus the local packages directory, and installs with no dev dependencies, no scripts and an optimized autoloader. It then copies the application source directories and the artisan file, creates the storage and cache subdirectories that Laravel expects to exist, and dumps the autoloader again.
An assets stage starts from the same Composer image, adds Node and npm on Alpine, copies the vendor stage output, installs from the lock file with npm ci, copies the frontend resources and the Vite and TypeScript configs, and builds.
The build there runs with a placeholder application key and a production environment set inline. That key is a literal string of base64 padding, which is safe because this stage only compiles assets and the output is a static bundle.
The final stage is PHP 8.4 with FPM on Alpine. Extensions are installed for internationalization, opcache, pcntl and PostgreSQL, the Redis extension is compiled and enabled as a separate build step, and the build dependencies are removed afterwards. Then it copies the vendor output, the compiled assets, an nginx configuration, a PHP ini file, and two shell scripts that are marked executable.
So the runtime image contains nginx and PHP-FPM rather than PHP alone, which is why the health check uses wget against a port nginx serves.
The example environment ships debug logging and an empty database password
The example environment file is a Laravel default with a handful of Larasend additions, and two of its defaults deserve a second look.
The log level is debug, and the log channel is the stack writing to a single file. In an environment file that otherwise declares `APP_ENV=production` and `APP_DEBUG=false`, debug-level logging is inconsistent with the posture the rest of the file sets. It is inherited from the framework template rather than chosen.
The database password is empty, while the page's own quick start tells you to edit `.env` and set it. The compose file is stricter about this: its PostgreSQL service uses a required-variable form for the password, so the stack refuses to start rather than falling back to a blank. That asymmetry is a reasonable design, since the compose file is what most people actually run.
The additions are the two MIME disk variables, the queue and cache drivers set to database, the Redis host pointing at the compose service name, and three Larasend-specific switches. One of those switches has a comment explaining the default: the landing page is off, so most self-hosted installs send visitors to sign-in rather than marketing copy, and should only be enabled by an instance intentionally acting as a public site.
Another controls registration, which stays open while the instance has no users so the first visitor can create the owner account, and should then be turned off because new members are normally invited.
One release, and the health check command is cut off mid-line
There is a single release, v0.1.0, published on 2026-07-05. The last push to the default branch is dated 2026-08-15, so the branch is some weeks ahead of anything tagged, and a version one release deep is what a new self-hosted product looks like rather than a sign of trouble.
The installation path itself is short and worth stating in full, because it fetches two files by URL before anything is built:
mkdir larasend
cd larasend
curl -fsSL https://raw.githubusercontent.com/savvyagents/larasend/main/docker-compose.yml -o docker-compose.yml
curl -fsSL https://raw.githubusercontent.com/savvyagents/larasend/main/.env.example -o .env
The URLs point at the main branch rather than at a tag, so the compose file a user gets is whatever is on main that minute. For a security-sensitive database password and a set of environment defaults, tracking a moving branch is the choice most projects avoid, and there is no digest or version pin offered in its place.
After editing the environment, the key is generated by running the image's PHP entrypoint once and printing the result, so the value is pasted back into the file by hand rather than written automatically. Migrations then run on boot when the stack starts.
And the page ends mid-instruction. The final command shown is the health check, and it stops after `docker compose exec app php artisan ` with no subcommand following it, so the command a reader is told to run to confirm a healthy install is not actually written down.
Editorial conclusion
Larasend suits Laravel teams that want their email logs, previews and API keys on infrastructure they control while still sending through a provider account they own, and the two-provider design is genuinely useful when open and click tracking only exists on one of them. Three things to check first. Raw MIME content must live on durable storage, because queued delivery, inbound attachments and downloads all read it from every web and worker instance. Authentication mail is deliberately off until you configure a separate control mailer, so plan that before inviting anyone. And Cloudflare has no event webhooks, which means delivery state there is recorded at send time rather than confirmed afterwards.
Frequently asked questions
What does larasend do with email sends?
It exposes a simple `POST /api/emails` endpoint with API key authentication and a Laravel mail transport, so `MAIL_MAILER=larasend` works as a drop-in. Requests are validated, the MIME payload and metadata are stored, and delivery is queued.
Which email providers does larasend send through?
Amazon SES or Cloudflare Email Service, chosen per source. SES publishes delivery, bounce, complaint, open and click events back through its webhook. Cloudflare has no event webhooks or open and click tracking, so delivery state is recorded at send time and suppressions sync hourly.
Why does larasend refuse log and array as the control mailer?
Authentication mail is deliberately kept separate from the transactional provider, so the instance is never its own only recovery path. Control mail must point at an independently configured mailer such as smtp, ses, postmark or resend before verification, password recovery and invitations are activated.
What does larasend need before it runs?
Docker and Docker Compose for the bundled stack, plus either an Amazon SES account with a verified sending domain or a Cloudflare account on the Workers Paid plan with a domain onboarded. Local development additionally wants PHP 8.4 or newer, Node.js 22 or newer, PostgreSQL 17 or newer and Redis 7 or newer.
Where should larasend store raw email content?
On durable object storage, not on an ephemeral local filesystem. Set the filesystem disk and the MIME disk to s3, or an S3-compatible equivalent. Queued delivery, inbound attachments and email downloads all read that content, and every web and worker instance has to see the same bytes.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/savvyagents-larasend)Star history chart for your README
[](https://hysenlabs.com/projects/savvyagents-larasend)Was this useful?